Malicious scanning activity against Palo Alto Networks GlobalProtect VPN login portals has surged 40 times within 24 hours, indicating a coordinated attack campaign. This escalation is linked to previous campaigns and primarily targets the US, Mexico, and Pakistan. #GlobalProtect #PaloAltoNetworks
Category: Cyber Security News

Cybersecurity experts have identified the Tsundere botnet, actively targeting Windows systems since mid-2025, with sophisticated mechanisms including WebSocket communication on the Ethereum blockchain. The malware spreads through fake MSI installers and PowerShell scripts, leveraging gaming-related lures and maintaining persistence via registry modifications. #TsundereBotnet #EthereumBlockchain…

Oligo Security reports on ShadowRay 2.0, a sophisticated cryptojacking campaign exploiting an unpatched vulnerability in the Ray AI framework to turn clusters into self-replicating botnets. Attackers use exposed Ray dashboards to spread malware, perform DDoS attacks, and hijack computing power for illicit mining. #CVE-2023-48022 #RayAI #cryptojacking #DDoS…

NSO Group is appealing a court order that requires it to cease targeting WhatsApp with its Pegasus spyware, which affected 1,400 users. The company claims the ruling could threaten its existence and hinder law enforcement operations, arguing the judge misinterpreted how Pegasus operates. #NSOGroup #Pegasus #WhatsAppTargeting #CFAA…

The FCC has reversed cybersecurity regulations aimed at protecting telecommunications networks after Chinese hackers breached major U.S. companies during the Salt Typhoon campaign. Critics argue that deregulation weakens national security efforts amid ongoing threats from Chinese state-backed cyber espionage. #SaltTyphoon #ChineseHackers…

Security researchers have identified a new Android banking trojan called Sturnus that can intercept decrypted messages from apps like WhatsApp, Telegram, and Signal. The malware is capable of stealing banking credentials, monitoring user activity in real time, and executing transactions, indicating a potential for broader cyber threats in Europe. #Sturnus #ThreatFabric…
A new Android banking trojan called Sturnus targets secure messaging apps like WhatsApp, Telegram, and Signal to steal sensitive information. It can conduct overlay attacks, log keystrokes, and remotely control infected devices, posing a significant threat to financial institutions and users in Europe. #Sturnus #AndroidTrojan #ThreatFabric #FintechThreats…
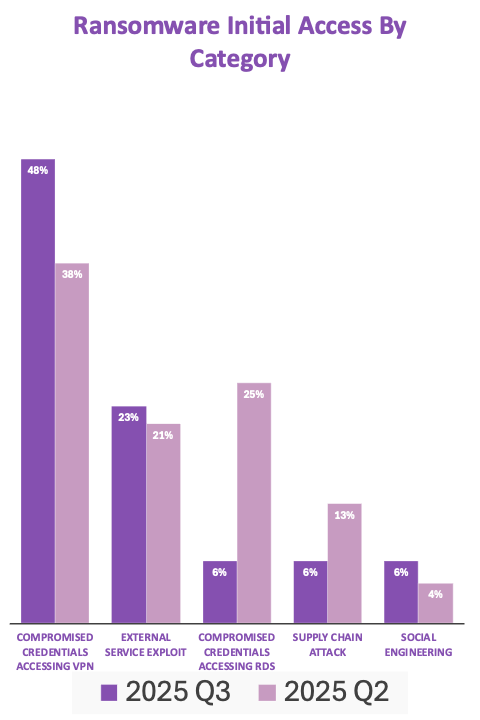
Compromised VPN credentials are the leading initial access point for ransomware attacks, with nearly half of incidents involving VPN abuse. The report highlights the importance of multi-factor authentication (MFA) and dark web monitoring to prevent credential leaks and cyberattacks. #SonicWall #AkiraRansomware…
Photocall, a major TV piracy streaming platform, has shut down after a joint investigation by ACE and DAZN, targeting illegal access to numerous TV channels and sports content. The operation disrupted several illegal streaming sites and transferred domain control to ACE, emphasizing ongoing efforts against digital piracy. #Photocall #DAZN #ACE #Europol #IllegalStreaming

Windows users are reconsidering their OS options as Windows 10 approaches end of support in October 2025, with some sticking to Windows 10 and others migrating to Linux or newer Windows versions. The article highlights the market trends, security concerns, and practical advice for organizations to navigate Windows updates safely. #Windows10 #Windows11 #Linux #CyberThreats
D-Link has announced three remote command execution vulnerabilities affecting all models of its DIR-878 router, which is now end-of-life but still in use. Exploit code has been published, raising concerns about potential abuse by threat actors like botnets #RondoDox #Aisuru.
A recent security advisory from SonicWall highlights a high-severity SSLVPN vulnerability (CVE-2025-40601) that could cause firewalls to crash through a denial-of-service attack. While no active exploitation has been reported, SonicWall recommends urgent patching and mitigation measures. #SonicOS #SSLVPNVulnerability
Salesforce has revoked tokens related to Gainsight applications amid a new wave of data theft targeting customer data, with the investigation ongoing. This incident resembles previous attacks involving stolen OAuth tokens from Salesloft, affecting multiple major organizations. #Salesforce #Gainsight #ShinyHunters #Salesloft #OAuthTokens

Cybersecurity researchers have uncovered a new Android banking trojan named Sturnus that can steal credentials and take full control of devices, bypassing encrypted messaging. This malware targets financial institutions in Europe, uses sophisticated overlay attacks, and maintains strong protection against removal. #Sturnus #AndroidTrojan #FinancialFraud…

A new WhatsApp account-hacking campaign called HackOnChat is rapidly spreading worldwide by using social engineering and impersonation techniques via malicious URLs and portals. The campaign primarily targets users in the Middle East and Asia, exploiting WhatsApp’s web interface to hijack accounts and carry out further scams. #HackOnChat #WhatsAppSecurity…