An educational technology provider, Illuminate Education, has settled allegations with the FTC for poor security practices that led to a 2021 data breach affecting over 10 million students. The company will implement a data security program, improve breach notifications, and delete unnecessary data to address security concerns. #IlluminateEducation #DataBreach #FTC #StudentDataProtection…
Category: Cyber Security News

Law enforcement agencies in Europe shut down Cryptomixer, a cryptocurrency mixing service linked to laundering €1.3 billion worth of Bitcoin. The operation targeted illegal activities including ransomware, fraud, and drug trafficking, seizing servers and data. #Cryptomixer #OperationOlympia…
Facial recognition technology is widely used for public surveillance and access control, but it faces significant trust and security issues. Efforts are underway to improve its security and privacy features, especially for authorized access in private spaces. #Clearview #GDPR…

An Australian man, Michael Clapsis, was sentenced to over seven years in prison for creating ‘evil twin’ WiFi networks to steal women’s private images and credentials. This case underscores the dangers of malicious WiFi networks and highlights the importance of cybersecurity measures like VPNs when using public WiFi. #EvilTwin #WiFiPineapple…

European law enforcement agencies have successfully shut down the cryptocurrency mixing service ‘Cryptomixer,’ which facilitated billions in criminal money laundering. This operation highlights ongoing efforts to combat anonymity tools used by cybercriminals for activities like ransomware and drug trafficking. #Cryptomixer #Europol…
The ShadyPanda operation has infected millions of browser extensions, evolving from legitimate tools into spyware that exfiltrates sensitive user data. Despite removals from Google, the campaign persists on Microsoft’s Edge platform, posing ongoing security risks. #ShadyPanda #BrowserExtensions
Cybercriminals are now impersonating cybersecurity professionals to infiltrate organizations through sophisticated fake profiles and deepfake technology. This rising threat emphasizes the importance of robust verification, advanced technical controls, and continuous security awareness to prevent insider threats. #Deepfake #Impersonation
A major data breach at South Korea’s largest retailer, Coupang, exposed personal information of 33.7 million customers, including names and addresses, but not payment details. The breach is suspected to be caused by a former employee using unrevoked access tokens, raising concerns over insider threats. #Coupang #DataBreach #InsiderThreat
PostHog experienced a significant security breach caused by the Shai-Hulud 2.0 npm worm, which compromised thousands of developer secrets and spread malicious packages. The incident highlights vulnerabilities in CI/CD workflows and dependency management. #ShaiHulud #npmworm…

North Korean threat actors are actively expanding their malicious operations within the npm ecosystem to distribute OtterCookie malware, targeting developers in the crypto and Web3 sectors. The campaign employs fake job offers, typosquatted packages, and a sophisticated infrastructure involving GitHub, Vercel, and C2 servers. #OtterCookie #ContagiousInterview…
British telco Brsk is investigating a data breach involving over 230,000 files, with stolen customer contact information potentially offered for sale on cybercrime forums. The company has assured affected customers that only basic contact details were compromised and is offering fraud protection services. #Brsk #DataBreach…

The emergence of agentic AI browsers represents a significant shift from passive tools to active autonomous agents, raising complex security challenges. Organizations must adopt new strategies to discover, monitor, and protect against these powerful yet vulnerable browser platforms. #OpenAI #ChatGPTAtlas #PromptInjection #AgenticAI #CyberDefense…

The recent data breach at South Korea’s largest online retailer, Coupang, compromised the personal data of 33.7 million customers, highlighting ongoing cybersecurity vulnerabilities in the country. The incident has prompted government action and scrutiny of existing legal protections for personal data. #Coupang #SouthKorea #DataBreach…
CISA has added the CVE-2021-26829 vulnerability in ScadaBR to its KEV catalog after it was exploited by hackers for defacement of an ICS interface. The incident highlights the ongoing threat of exploit only vulnerabilities in industrial control systems by hacktivists and sophisticated actors. #CISA #CVE-2021-26829 #TwoNet #ICSattack #ScadaBR…
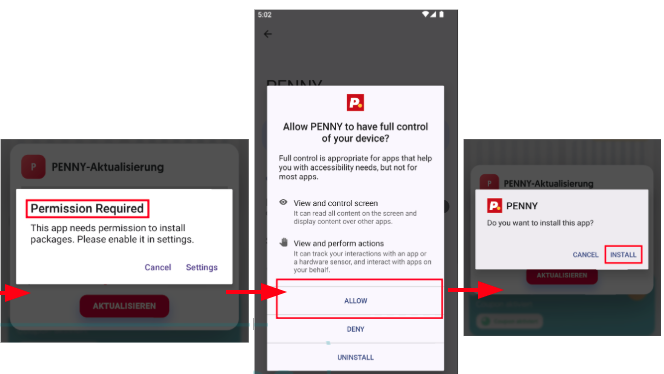
A new Android banking trojan called Albiriox is being marketed on cybercrime forums, with capabilities for real-time device control and overlay attacks. This malware targets over 400 applications globally and is offered as a malware-as-a-service. #Albiriox #RussianThreatActors…