
Daily Recap, Researchers link three hacking groups exploiting two vulnerabilities to campaigns with ties to China, highlighting widespread exploitation paths and potential state involvement. UTA0355 stole Microsoft 365 OAuth tokens via fake security-conference lures and WhatsApp support social engineering, while Android families FvncBot, SeedSnatcher, and an upgraded ClayRat add stronger data-theft features, alongside NFCGate-based banking malware and breaches at Cl0p and Tri-Century Eye Care. #China #UTA0355
Category: Cyber Security News
Google is enhancing Chrome’s security with a new layered architecture for agentic AI browsing powered by Gemini, including the “User Alignment Critic” model to prevent prompt injection risks. This development aims to safeguard user data and ensure safer autonomous web interactions by AI agents. #Gemini #PromptInjection #ChromeSecurity
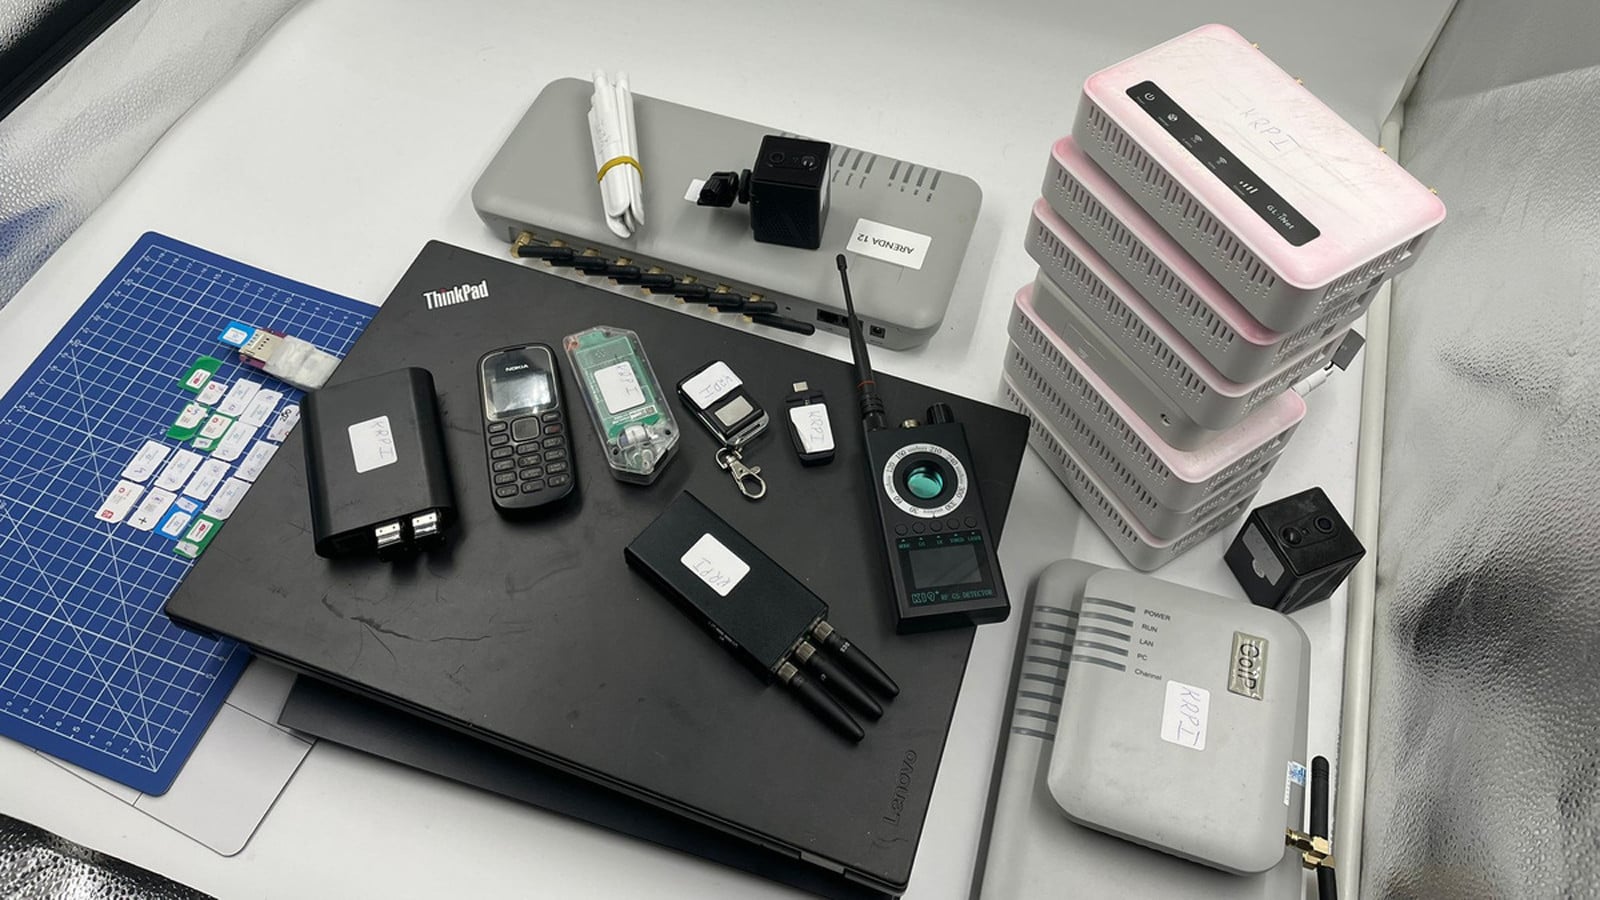
Polish police have arrested three Ukrainian nationals suspected of attempting to damage national IT systems using hacking equipment and collecting critical data related to national defense. The suspects, found with advanced hacking tools including the Flipper Zero device, face charges of fraud and possession of criminal tools, raising concerns about cyber espionage threats. #FlipperZero #CyberEspionage

Cybersecurity researchers have identified the JS#SMUGGLER campaign, which uses compromised websites to deploy the NetSupport RAT via a sophisticated multi-stage web-based attack. The campaign features layered script execution, device-aware targeting, and stealth techniques to evade detection. #NetSupportRAT #JS#SMUGGLER…

Russia has recently blocked major Western online services, including Roblox, WhatsApp, FaceTime, and Snapchat, citing national security and moral concerns. The banning of Roblox has sparked protests among Russian users, especially children and teenagers, while the government pushes for domestic alternatives amidst broader restrictions on foreign digital platforms. #Roblox #Roskomnadzor #Russia…

This article discusses a critical XML External Entity (XXE) injection vulnerability in Apache Tika that can lead to sensitive data exposure. Users are urged to update affected versions to mitigate the risk of exploitation. #ApacheTika #XXEVulnerability…
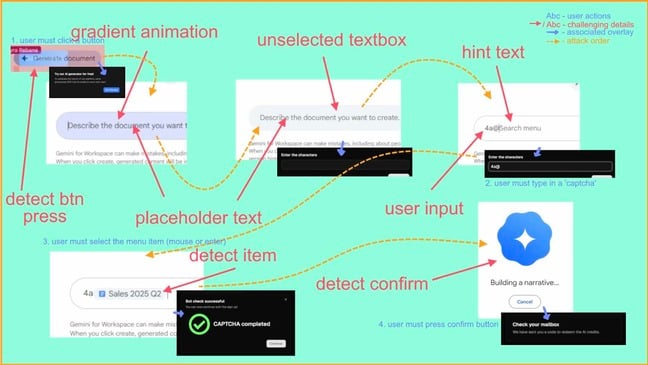
Lyra Rebane uncovered a novel SVG and CSS-based clickjacking attack that can bypass traditional web security measures. This technique manipulates cross-origin data leakage and has been demonstrated to exfiltrate sensitive information, highlighting ongoing vulnerabilities in web application security. #SVGClickjacking #CrossOriginLeaks…
AI-driven threat emulation can significantly reduce the time security teams need to validate emerging cyber threats. Picus’s innovative agentic, multi-agent platform enhances accuracy and safety by mapping threat intelligence to pre-validated safe components, transforming threat detection and response. #FIN8 #PicusSecurity

Cybersecurity experts have uncovered new Android malware families FvncBot and SeedSnatcher, as well as an upgraded ClayRat version with enhanced capabilities. These threats target banking, cryptocurrency, and personal data, demonstrating evolving tactics in Android malware. #FvncBot #SeedSnatcher #ClayRat…
The holiday shopping season increases the risk of cyber attacks like credential stuffing and account takeover, especially during peak times. Implementing layered security controls, adaptive MFA, and rigorous third-party access management can mitigate these threats. #TargetDataBreach #CredentialStuffing #HolidayFraud…
Large language models face a persistent threat from prompt injection, which manipulates AI systems into ignoring their original instructions. Experts warn that unlike traditional vulnerabilities like SQL injection, prompt injection may never be fully eliminated and requires careful risk management. #PromptInjection #AIThreats…

Russian authorities dismantled a criminal group responsible for stealing over $2.6 million from bank customers using NFCGate-based malware. The group targeted victims across Russia by distributing fraudulent banking apps via messaging platforms and tricking users into revealing their PINs. #NFCGate #FakeBankApps…
This article discusses the discovery of critical vulnerabilities in Microsoft’s SharePoint software exploited by multiple Chinese hacking groups, leading to widespread cyberattacks. It highlights the importance of patching and the suspicious cooperation between state-linked groups and cybercriminals, raising concerns about escalation and motives behind these operations. #ToolShell #SharePointVulnerabilities…

The recent data breach at Tri-Century Eye Care affected around 200,000 individuals, exposing sensitive personal and health information. The Pear ransomware group claimed responsibility, stolen data was made public, and the organization refused to pay the ransom. #PearRansomware #TriCenturyEyeCare…
Resemble AI has raised $13 million to enhance its AI detection platform that identifies deepfakes and prevents fraud across various media types and languages. Its solutions are trusted by Fortune 500 companies and government agencies to combat AI-based threats like voice cloning and social engineering. #DeepfakeDetection #VoiceCloningProtection…