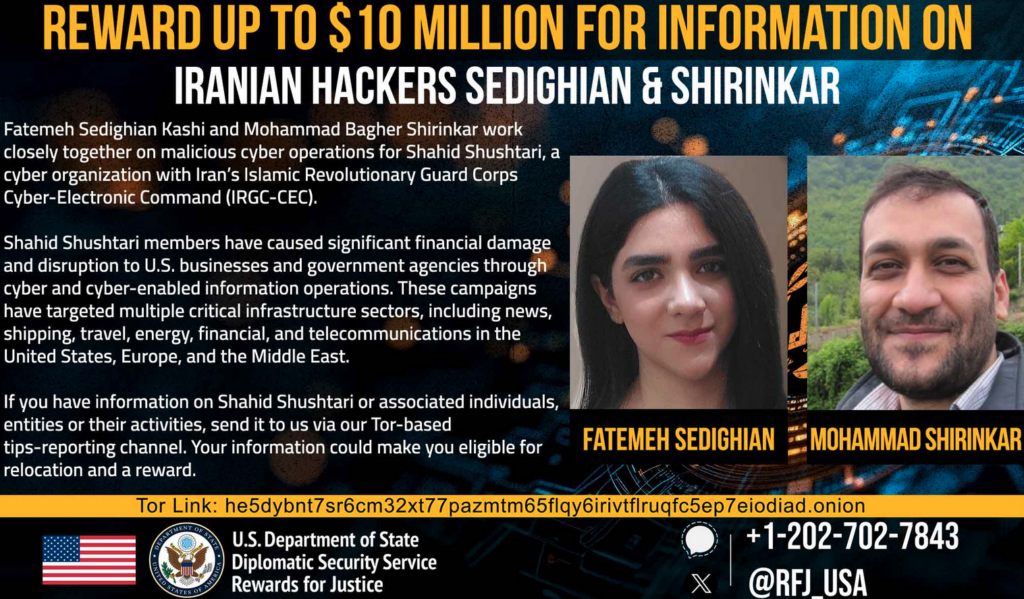
The US government has announced a $10 million reward for information on the Iranian hacking group Shahid Shushtari, linked to Iran’s IRGC-CEC. The group has conducted cyberattacks against critical infrastructure and influence operations globally, including targeting the 2024 Olympics and US elections. #ShahidShushtari #IRGC-CEC…
Category: Cyber Security News

The 6th NIS Investments report shows a shift in EU organizations’ cybersecurity spending from staffing to technology and outsourced services, driven by talent shortages and NIS2 compliance. The findings highlight ongoing challenges in patching, supply-chain risks, and resource allocation, informing future EU cybersecurity policies. #NIS2Directive #ENISA #CyberResilience #SupplyChainThreats…

The UK’s NCSC highlights the rising threat of prompt injection in generative AI systems, emphasizing its significant distinction from traditional SQL injection. They stress that organizations should adopt secure design principles and robust monitoring to mitigate risks in AI deployments. #PromptInjection #GenerativeAI…

A critical security vulnerability in the Apache Tika framework has been expanded to affect multiple modules, increasing the potential attack surface. While no active exploits are reported, timely updates and configuration adjustments are recommended to mitigate risks. #ApacheTika #CVEs2025-54988 #CVEs2025-66516…

Polish police detained three Ukrainian nationals found with advanced hacking and surveillance equipment, raising concerns over national security and cybercrime. The suspects, claiming to be IT specialists, face multiple charges including cyber fraud and possession of illegal devices. #FlipperTools #CyberCrime…
The FinCEN report highlights the rise and fall of ransomware incidents, with law enforcement actions impacting operations of gangs like ALPHV/BlackCat and LockBit. The report underscores the financial damage across industries, emphasizing the need for continued vigilance and reporting. #ALPHV #LockBit
Two malicious extensions on the Visual Studio Code Marketplace, Bitcoin Black and Codo AI, infect developer machines with malware capable of stealing credentials, screenshots, crypto wallets, and hijacking browser sessions. Developers should only install extensions from reputable sources to mitigate these security risks. #BitcoinBlack #CodoAI #VSCodeMarketplace
Multiple ransomware gangs utilize the Shanya packer-as-a-service platform to obfuscate malicious payloads and disable endpoint detection solutions. Sophos’s analysis reveals how Shanya compounds its effectiveness by encrypting payloads in memory and disrupting security tools in targeted regions. #Shanya #Medusa #Crytox #Akira #endpointdetection

The European Commission approved Meta’s new feature allowing Instagram and Facebook users in the EU to share less personal data and see fewer targeted ads. This move responds to an earlier €200 million fine and aims to enhance user privacy rights under the Digital Markets Act. #Meta #DigitalMarketsAct…
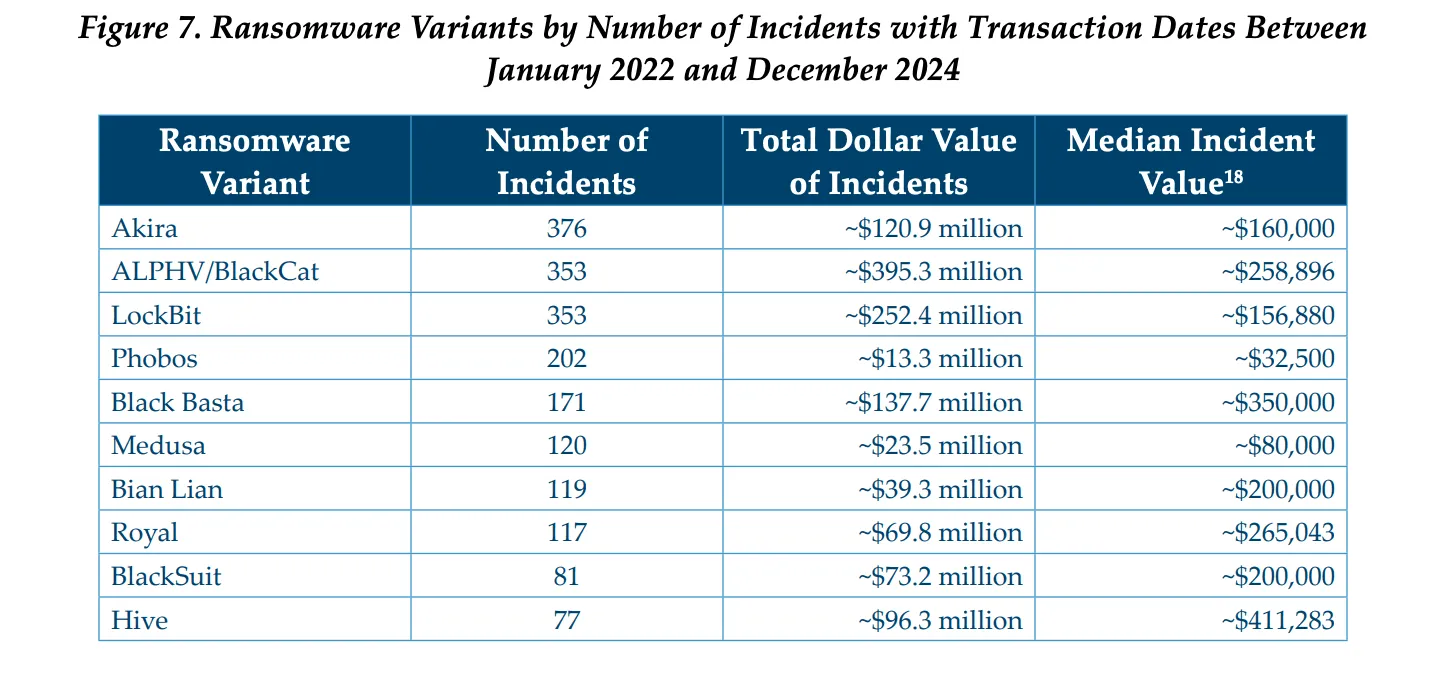
Companies paid over $2.1 billion to ransomware gangs between 2022 and 2024, with 2023 experiencing a peak payout of $1.1 billion. The report highlights the prominence of gangs like ALPHV/BlackCat and LockBit, and details targeted sectors such as finance, manufacturing, and healthcare. #ALPHV #LockBit #BlackBasta #RansomwarePayments #CyberThreats…

President Donald Trump plans to sign an executive order to create a unified rule for AI regulation across the United States, aiming to prevent states from enacting their own laws. The move is designed to streamline AI policy but faces opposition from privacy advocates and some lawmakers who argue states should…

A sophisticated cyber-espionage campaign targeting Chinese organizations uses SEO poisoning and Russian false flags to mislead investigators. The attackers employ malware like ValleyRAT to steal sensitive information and conduct financial theft. #SilverFox #ValleyRAT…
Google is enhancing Chrome’s security with layered protections for its new agentic capabilities, aiming to prevent indirect prompt injections and data leaks. These defenses include a specialized AI model called User Alignment Critic and expanded origin isolation policies. #Gemini #AgenticBrowsers…

U.S. companies paid over $2 billion in ransomware demands between 2022 and 2024, with a significant increase in incidents in 2023. Law enforcement actions against groups like ALPHV/BlackCat and LockBit have temporarily reduced total ransomware payments. #BlackCat #LockBit…

Gartner warns that AI browsers pose significant cybersecurity risks, including data leakage, rogue transactions, and credential abuse. They recommend blocking such browsers for most organizations and implementing strict controls during limited use cases. #PerplexityComet #OpenAIAtlas…