
The FBI Anchorage Office warns residents about the rise in government impersonation scams, primarily via phone calls. Victims are pressured to pay fake fines or provide personal information, with scammers using advanced AI tools for impersonation. #FBI #Alaska scams #governmentimpersonation…
Category: Cyber Security News

Cybersecurity Threat Research ‘Weekly’ Recap: A critical unauthenticated deserialization RCE in React Server Components (React2Shell, CVE-2025-55182) is being weaponized for mass scanning and arbitrary code execution, prompting patches and WAF/runtime protections while defenders hunt for indicators (MINOCAT, SNOWLIGHT, HISONIC, XMRig). A broad surge of activity across loaders, backdoors, info stealers, phishing, ransomware, and APTs—featuring EtherRAT, GhostPenguin, NANOREMOTE, CastleRAT, ValleyRAT, GrayBravo, AshTag, AshenLepus, Group123, APT31, Salt Typhoon, GOLD_SALEM, Warlock, Makop, 01flip, Storm-0249, and others—underscores supply-chain abuse, credential theft, and geopolitical intrusions.
#React2Shell #CVE-2025-55182 #MINOCAT #SNOWLIGHT #HISONIC #XMRig #EtherRAT #GhostPenguin #NANOREMOTE #CastleRAT #ValleyRAT #GrayBravo #AshTag #AshenLepus #Group123 #APT31 #SaltTyphoon #GOLD_SALEM #Warlock #Makop #01flip #Storm_0249 #FrostBeacon #Shai_Hulud_2_0 #NexusRoute #RTO_Challan #DroidLock #PhantomStealer #AMOSStealer #Banshee #LummaStealer #JSCEAL #NoteGPT #MoneyMount #VSCodeExtensions

CyberVolk, a pro-Russian hacktivist group, has relaunched its VolkLocker ransomware-as-a-service, targeting Windows and Linux systems with notable design flaws that allow victims to decrypt files without paying. The group continues expanding its malicious offerings, including remote access tools, while leveraging Telegram for operations. #CyberVolk #VolkLocker #Telegram #RaaS…

Asahi Group Holdings is considering establishing a dedicated cybersecurity unit following a ransomware attack that caused extensive operational and financial disruptions. The incident prompted a shift towards a zero-trust security model and highlights the importance of advanced cybersecurity measures in protecting corporate assets. #AsahiGroup #Ransomware #ZeroTrustSecurity…
CyberVolk’s VolkLocker ransomware was found to have significant cryptographic flaws that could allow victims to decrypt files for free. The group, known for pro-Russia hacktivism, has been disrupted multiple times but continues to launch attacks using its RaaS platform. #CyberVolk #VolkLocker #Telegram #AES256
This article reveals how scammers are exploiting PayPal’s billing features to send legitimate-looking phishing emails containing fake purchase notifications. These messages aim to trick recipients into calling scam numbers or installing malware, despite passing security checks. #PayPal #PhishingEmails

A Hamas-affiliated group, Ashen Lepus, continues its persistent cyber-espionage activities amidst ongoing conflict, significantly upgrading its malware capabilities with the new AshTag suite. The group’s evolving tactics include sophisticated evasion techniques and expanded targeting across Arabic-speaking nations, emphasizing the strategic importance of their digital operations. #AshenLepus #AshTag…

A threat group impersonated Trend Micro to launch a targeted spear-phishing campaign against critical infrastructure, leveraging the vendor’s branding to deceive victims. This operation appears to be linked to the cybercriminal group Void Rabisu, showcasing a mix of old and new attack techniques. #SHADOWVOID042 #VoidRabisu…

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a critical vulnerability in Sierra Wireless AirLink ALEOS routers to its Known Exploited Vulnerabilities list due to active exploitation. This flaw, CVE-2018-4063, allows remote code execution through malicious HTTP requests, posing a significant threat to impacted systems. #CISA #CVE2018-4063…

Daily Recap, the security landscape today spans zero-day exploits patched in Apple WebKit and active Gogs exploitation affecting hundreds of self-hosted instances, along with critical flaws in Varex Imaging, GDCM, and Johnson Controls iSTAR Ultra impacting medical and industrial systems. The report also highlights Lazarus Group and Ashen Lepus espionage campaigns, major data breaches at Coupang and Pierce County Library, and a surge of malware kits and phishing tools including PyStoreRAT, Agent Tesla, BlackForce, GhostFrame, InboxPrime AI, and DroidLock. #LazarusGroup #AshenLepus #Coupang #PierceCountyLibrary #PyStoreRAT #AgentTesla #BlackForce #GhostFrame #InboxPrimeAI #DroidLock #AppleWebKit #Gogs #VarexImaging #GDCM #JohnsonControls #AshTag
Daily Recap, active exploitation of GeoServer CVE-2025-58360 enables file reads, SSRF, and DoS alongside multiple React Server Component flaws (CVE-2025-55182 / React2Shell) that trigger RCE and prompt emergency patching by federal agencies. The round-up also notes a RasMan zero-day with unofficial 0Patch fixes, plus incidents such as Gladinet RCE, Notepad++ update-flaw, malicious VSCode extensions, Fieldtex data breach, ICO fines for LastPass, CodeRED outage, and other breaches and takedowns like MKVCinemas. #GeoServer #RasMan
Apple has issued emergency patches for two critical WebKit zero-day vulnerabilities exploited in targeted, highly sophisticated attacks on specific individuals. These vulnerabilities, tracked as CVE-2025-43529 and CVE-2025-14174, affected various Apple devices and were also addressed by Google Chrome in coordination with Apple. #WebKitVulnerabilities #TargetedAttacks

Apple has released security updates for multiple platforms to fix two critical vulnerabilities in WebKit that have been exploited in the wild, including one previously patched by Google Chrome. These flaws are believed to have been used in targeted spyware attacks, affecting a wide range of Apple devices and browsers. #WebKitVulnerabilities…
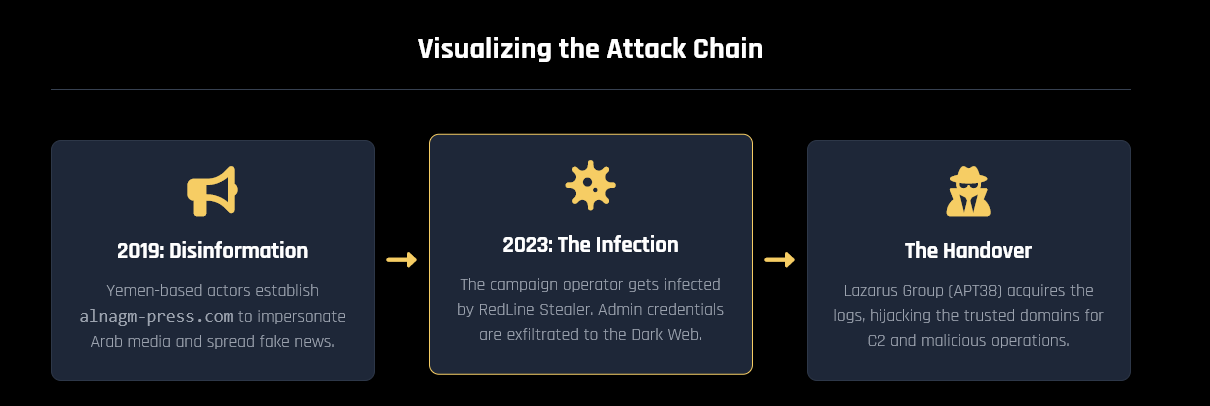
This article reveals how a Yemen-based disinformation campaign was linked to North Korea’s Lazarus Group through a single infected computer in 2020. The compromise enabled the threat actors to hijack trusted news domains for cyber-espionage and malicious campaigns. #LazarusGroup #RedLineStealer
Organizations often rely on spreadsheets for collaborative work, but shadow spreadsheets pose significant security risks due to oversharing and version sprawl. Grist offers a structured, secure alternative that combines spreadsheet familiarity with relational database controls. #Grist #ShadowSpreadsheets