A cyber campaign named ‘GhostPoster’ is hiding malicious JavaScript code within popular Firefox extension logos to monitor activity and plant backdoors. This stealthy attack enables persistent access, affiliate hijacking, and ad fraud, posing a significant threat to user privacy. #GhostPoster #FirefoxExtensions
Category: Cyber Security News
A new Android malware-as-a-service called Cellik is offered on underground forums, enabling attackers to embed malicious code into apps from Google Play Store. Its advanced features include screen streaming, notification interception, and app injection, which can help evade detection and bypass Google Play Protect. #Cellik #AndroidMalware #GooglePlayStore #TrojanApps

Amazon’s threat intelligence has revealed a prolonged Russian state-sponsored campaign targeting Western critical infrastructure from 2021 to 2025. The campaign primarily exploited misconfigured network edge devices and leveraged vulnerabilities to harvest credentials and gain persistent access, with connections to GRU-linked groups like APT44 and Sandworm. #GRU #APT44…

Cybersecurity researchers uncovered a malicious NuGet package that impersonates a legitimate .NET tracing library to steal cryptocurrency wallet data. The stealthy package has been active for nearly six years, exfiltrating sensitive wallet information to a Russian infrastructure. #NuGetTyposquatting #CryptocurrencyTheft…

An ongoing cyberattack targets AWS customers by exploiting compromised IAM credentials to deploy cryptocurrency mining operations, utilizing sophisticated persistence techniques. Amazon warns users to enhance their security measures to prevent further damage and unauthorized resource consumption. #IAMCredentials #CryptoMining…

Andrew Garbarino discusses the importance of renewing key cybersecurity legislation and emphasizes the need for offensive cyber capabilities in national strategy. He also highlights ongoing investigations into Chinese hacking groups and the emerging threats from artificial intelligence. #CybersecurityInformationSharingAct #SaltTyphoon #VoltTyphoon #Anthropic #CyberThreats…

A recent cyberattack on Venezuela’s state oil company PDVSA has disrupted its operations and caused its website to go offline, amid heightened tensions with the U.S. government. The Venezuelan authorities blame the U.S. for the attack, but cybersecurity experts have not found direct evidence linking it to U.S. actors. #PDVSA #VenezuelanCyberattack…
Russian government hackers, specifically the group APT44, are increasingly targeting Western energy sectors by exploiting misconfigured network edge devices rather than vulnerabilities in software. These attacks demonstrate a strategic shift towards passive data collection and credential harvesting, emphasizing the importance of proper device configuration in cybersecurity defenses. #APT44 #Sandworm #RussianCyberThreats #CriticalInfrastructure…
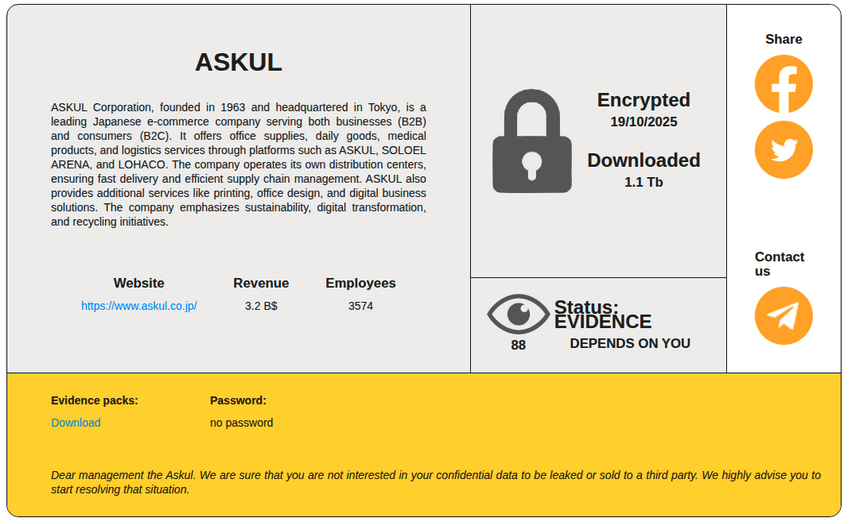
A ransomware attack on Japanese company Askul resulted in the theft of over 700,000 records, disrupting orders and logistics. The RansomHouse group claimed responsibility, leaking stolen data after the company refused to pay the ransom. #RansomHouse #Askul #DataBreach…

CISO communities have grown rapidly, providing a trusted and secure environment for cybersecurity executives to share insights, support, and collaborate in real-time. These peer groups help strengthen defenses, share threat intelligence, and address mental health challenges in the cybersecurity industry. #CISOCommunities #ThreatSharing…
This article discusses the increasing vulnerabilities in software supply chains, especially due to rapid development practices and emerging threats like slopsquatting. It highlights the importance of proactive visibility and security measures such as SBOMs, SAST, DAST, and human reviews to mitigate these risks. #SolarWinds #Log4J #Slopsquatting #SupplyChainRisks…
The Texas Attorney General has filed lawsuits against major television manufacturers for secretly collecting user data via Automated Content Recognition (ACR) technology. These companies, including Sony, Samsung, LG, Hisense, and TCL, are accused of invasive monitoring practices that may also expose U.S. data to foreign governments, especially Chinese firms. #ACRtechnology #ChineseCompanies
PornHub’s user data was targeted and stolen through a Mixpanel breach, leading to extortion by the ShinyHunters gang. The breach exposed sensitive user activity data, including search and watch histories, but not payment or financial information. #ShinyHunters #Mixpanel #PornHub…

Google is discontinuing its dark web report tool by February 2026, citing a need for more actionable security features. The move aims to improve user privacy and security management, ending Google’s initiative to monitor personal data on the dark web. #DarkWebReport #GoogleSecurityTools…

React2Shell is a security vulnerability being exploited by threat actors to deploy sophisticated malware like KSwapDoor and ZnDoor, leading to widespread cyber attacks globally. The exploitation involves remote code execution, credential theft, lateral movement, and infrastructure compromise. #React2Shell #KSwapDoor #ZnDoor #CVE-2025-55182…