
A cybercriminal campaign dubbed GhostPoster has exploited Mozilla Firefox add-ons to embed malicious JavaScript code that hijacks affiliate links, injects tracking, and conducts ad fraud. Security researchers warn that these extensions, though now removed, delivered a complex malware payload capable of monitoring browsing activity, stripping browser security, and opening backdoors for…
Category: Cyber Security News
Jewelbug, also known as Ink Dragon, is a highly sophisticated threat group targeting government entities across Europe, Asia, and Africa since March 2023. They utilize advanced malware tools like FINALDRAFT and ShadowPad to conduct stealthy intrusions, lateral movements, and data exfiltration, forming a resilient, multi-layered infrastructure. #Jewelbug #InkDragon #FINALDRAFT #ShadowPad #CobaltStrike…

Modern security teams need to shift from reactive firefighting to proactive threat detection by using contextual threat intelligence. Implementing tools like ANY.RUN’s Threat Intelligence Lookup enables SOCs to understand, prioritize, and respond to cyber threats tailored to their industry and geography. #Tycoon2FA #LummaStealer…

France’s Interior Ministry is investigating a cyber intrusion that compromised multiple email accounts and confidential documents, raising concerns about internal security. The attack is under judicial and technical scrutiny, with increased cybersecurity measures being implemented to prevent further breaches. #FrenchInteriorMinistry #ANSSI…
Cybersecurity in 2026 will revolve around the shift from network-based defenses to identity-focused security, with AI playing a critical role for both attackers and defenders. As deepfakes and AI-driven attacks increase, organizations must rethink trust, verification, and security strategies to stay resilient. #Deepfakes #AIThreats…
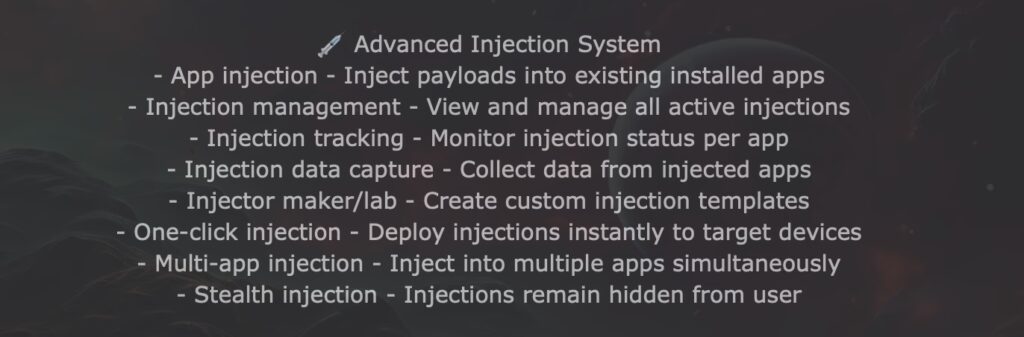
A new Android remote access trojan called Cellik offers extensive surveillance and control features, including real-time screen streaming, keylogging, and data theft. It is sold on the dark web for $150 per month, enabling cybercriminals to bundle malicious payloads into legitimate apps and conduct advanced attacks. #Cellik #AndroidRAT #DarkWebThreats…
Alex Hall’s journey highlights how personal trauma and neurodiversity can influence an individual to become a successful fraudster before turning to cybersecurity to combat cybercrime. His insights reveal the evolving tactics of fraudsters and the importance of advanced detection methods. #AccountTakeover #TrustAndSafetyArchitects…
Dux, an exposure management startup, has launched with $9 million in seed funding to help enterprises identify and mitigate vulnerabilities using AI-powered agents. Its innovative approach focuses on analyzing real exploitability to reduce attack surfaces and enhance cybersecurity defenses. #Dux #AgenticExposureManagement…
A cyberattack on PDVSA’s administrative systems caused significant disruptions to Venezuela’s oil export logistics, though official statements claimed operations were unaffected. The incident occurs amid escalating U.S.-Venezuela tensions, with accusations of U.S.-sponsored cyber and military actions targeting Venezuela’s oil resources. #PDVSA #VenezuelanOil #Cyberattack #U.S.VenezuelaTensions…
The DPDP rules enhance enterprise data governance by establishing clear consent and provenance requirements, making it harder for deceptive synthetic identities to infiltrate systems. While they do not eliminate deepfakes, these regulations help reduce the attack surface and improve fraud detection through better data quality and operational discipline. #DPDP #SyntheticIdentity #Deepfakes…
A major cyberattack on South Korea’s KT telecom operator appears to involve state-level espionage targeting femtocells to gather large-scale data. Experts suggest the breach indicates systemic failures and potential negligence in management, raising global concerns. #KT #femtocell #cyberespionage…

Daily Recap, Fortinet flaws are being actively exploited to bypass SAML/SSO and steal configurations, while the critical React2Shell (CVE-2025-55182) is used to deploy backdoors like KSwapDoor and ZnDoor in campaigns linked to China, and patched FreePBX vulnerabilities require urgent updates. The threat landscape also features SantaStealer and PyStoreRAT campaigns, massive data breaches affecting Prosper, 700Credit, SoundCloud, PornHub, Jaguar LandRover, and Askul, plus state-backed espionage by Sandworm (APT44) and Salt Typhoon, alongside privacy/regulation concerns and AI-enabled phishing and scams. #Fortinet #FortiGate #React2Shell #KSwapDoor #ZnDoor #FreePBX #SantaStealer #PyStoreRAT #Prosper #700Credit #SoundCloud #PornHub #JaguarLandRover #Askul #SaltTyphoon #Sandworm #MI6 #UrbanVPNProxy #GoogleDarkweb #Texas #Soverli #WSL
A recent report highlights a strategic shift in Russian state-sponsored cyber operations from exploiting software vulnerabilities to targeting misconfigured network edge devices. This tactic allows persistent access to critical infrastructure sectors such as energy and telecommunications. #Sandworm #GRU…
Hackers are exploiting two critical vulnerabilities (CVE-2025-59718 and CVE-2025-59719) in Fortinet products to gain unauthorized admin access and steal configuration files. The exploits target FortiCloud SSO authentication bypass, especially when enabled, posing significant security risks. #FortiCloudSSO #CVE202559718 #CVE202559719 #FortinetVulnerabilities
Amazon’s Threat Intelligence team has identified and disrupted operations linked to Russian GRU hackers targeting cloud infrastructure, especially in Western critical sectors like energy. The threat actors shifted from exploiting vulnerabilities to focusing on misconfigured devices, aiming for persistent access and credential theft. #GRU #Sandworm #AWSecurity #Cyberespionage