The Clop ransomware gang is actively targeting exposed Gladinet CentreStack file servers, compensating their data theft with extortion tactics. This campaign follows previous attacks exploiting vulnerabilities in various file-sharing platforms, including Oracle EBS. #Clop #GladinetCentreStack
Category: Cyber Security News
Hackers accessed and stole personal information from the University of Sydney’s online coding repository, affecting over 27,000 individuals. The university responded swiftly by shutting down the breach, notifying authorities, and supporting impacted community members. #UniversityofSydney #Cyberattack #DataBreach

This report highlights the prevalence of phishing attacks in November 2025, emphasizing the use of HTML scripts and hyperlinking techniques to steal user credentials. It also discusses the distribution of phishing emails in Korean and analyzes malware cases involving XLoader and compressed EXE files. #PhishingEmails #XLoader #FakePage #C2Server…

A new China-linked threat group called LongNosedGoblin has been targeting government agencies in Southeast Asia and Japan for cyber espionage since September 2023. The group employs advanced tools and techniques, including Group Policy, cloud services, and custom malware, to infiltrate and spy on victims. #LongNosedGoblin #CyberEspionage…

Chinese hackers have exploited a critical vulnerability in Cisco email management tools affecting appliances running AsyncOS Software. The threat group, linked to Chinese cyber espionage efforts, has used various tools to maintain access, prompting urgent mitigations from Cisco and the U.S. government. #CiscoVulnerability #UAT9686…

North Korean hackers stole over $2 billion in 2025, focusing on large-scale, targeted crypto thefts and sophisticated money laundering techniques. Their operations significantly contributed to the overall rise in crypto thefts, highlighting their strategic shift towards high-value attacks. #NorthKoreanHackers #CryptoTheft2025…

A new China-aligned hacker group called LongNosedGoblin has been targeting Southeast Asian and Japanese government institutions since September 2023, using sophisticated tactics like abusing Group Policy. Their malware arsenal includes NosyHistorian, NosyDoor, and other tools designed for data theft, lateral movement, and targeted attacks. #LongNosedGoblin #NosyHistorian #NosyDoor #GroupPolicy…
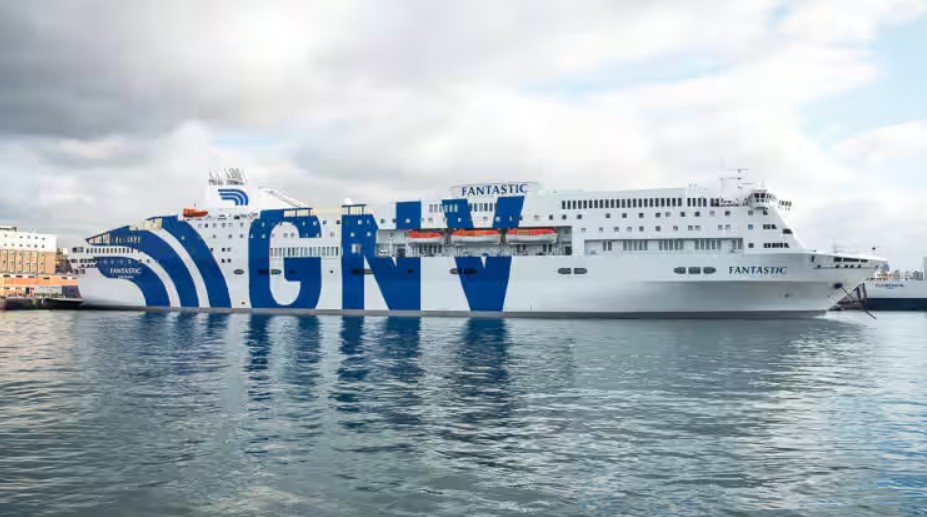
France is investigating a remote access trojan malware found on a passenger ferry, raising fears of foreign interference, possibly by a hostile nation. The incident, along with a recent cyberattack on the French Interior Ministry, underscores the increasing threat of cyber operations targeting critical infrastructure and government systems. #FerryMalware #FranceCyberAttack…
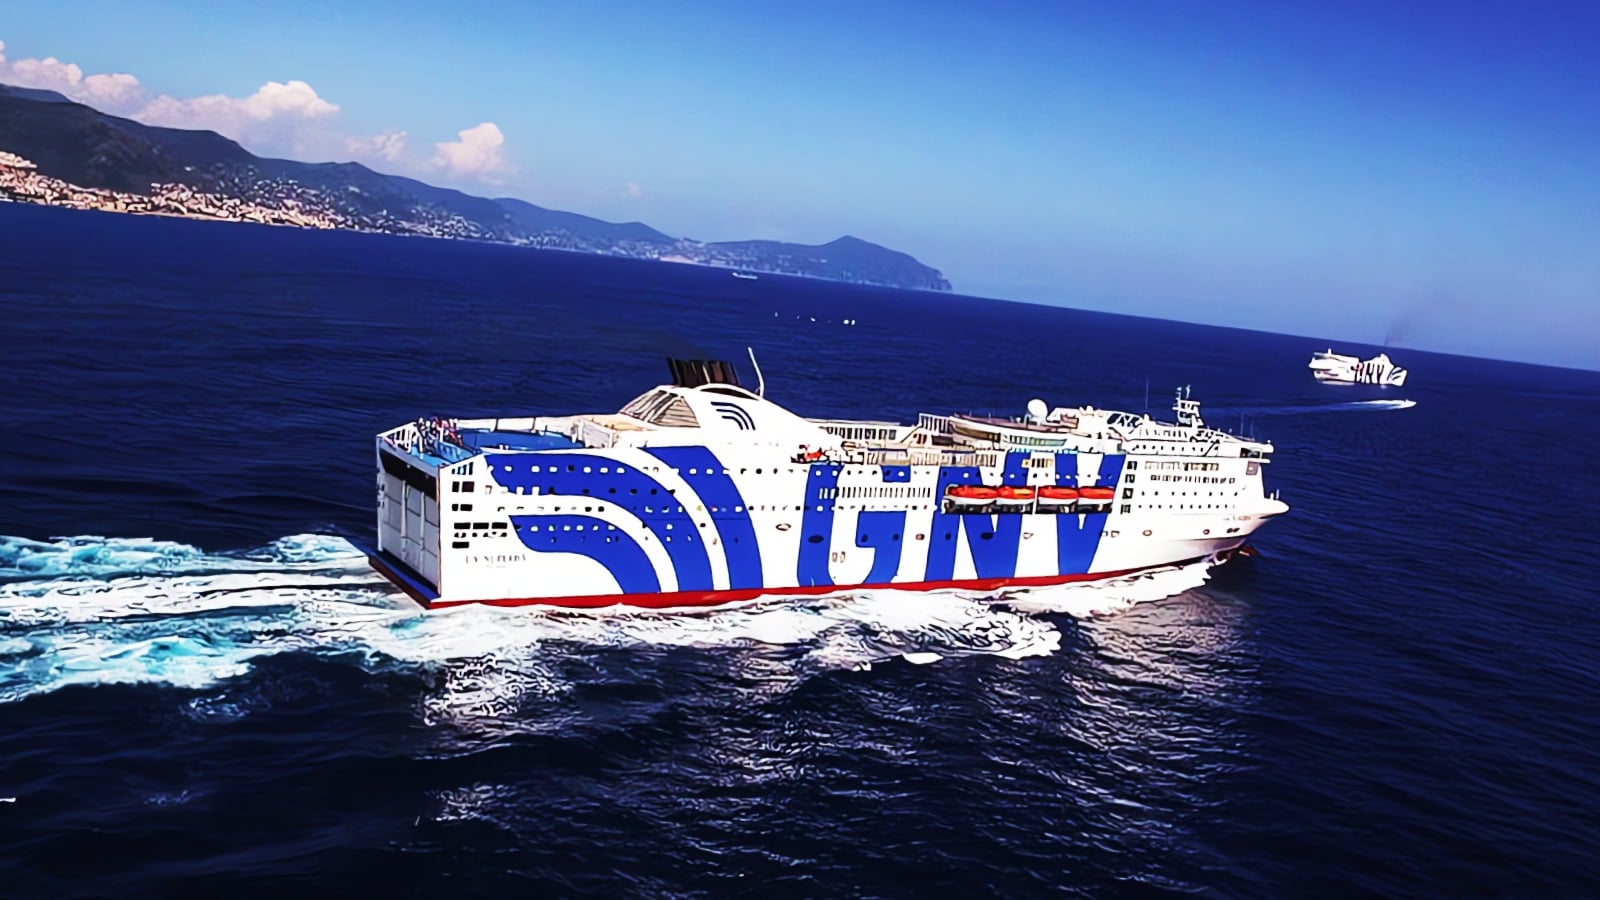
French authorities detained crew members of an Italian ferry suspected of malware infection that could enable remote control of the vessel. The investigation points to potential foreign interference involving cyber espionage and sabotage efforts in European maritime security. #FantasticFerry #DGSI
The EU’s NIS2 Directive emphasizes the importance of robust cybersecurity and strict access management for organizations in critical sectors. Implementing strong password policies, MFA, and continuous monitoring are essential steps for compliance and security. #NIS2 #AccessManagement
Law enforcement agencies worldwide have seized servers, domains, and mobile apps associated with the E-Note cryptocurrency exchange, which was used by cybercriminal groups to launder over $70 million. The operation targeted illicit funds from ransomware and account takeover attacks, leading to charges against its alleged operator, Mykhalio Petrovich Chudnovets. #E-Note #MykhalioPetrovichChudnovets

Threat actors linked to North Korea caused a record-breaking $2.02 billion in cryptocurrency thefts in 2025, primarily through high-profile attacks like the Bybit hack. Their operations include sophisticated money laundering schemes and infiltration of IT workers globally to fund North Korea’s regime. #LazarusGroup #BybitHack…

This week’s ThreatsDay Bulletin highlights how cyber attackers continuously adapt by modifying familiar tools and tactics, making the threat landscape more dynamic. Key incidents include a large international scam ring, emerging modular info stealers, and increased exploitation of vulnerabilities like React2Shell. #Eurojust #SantaStealer #React2Shell…

HPE has fixed a critical security vulnerability in OneView Software (CVE-2025-37164) that could allow remote code execution. Users are advised to apply the available hotfixes promptly to secure their systems. #HPEOneView #CVE202537164…

DXS International, a key NHS software provider, experienced a cybersecurity breach affecting its internal systems but claimed clinical services remained operational. UK health tech supply chain attacks highlight ongoing risks, with investigations ongoing and no confirmed patient data compromise yet. #DXSInternational #NHS #CyberAttack #HealthTech #ICO…