
The University of Sydney experienced a significant cybersecurity breach exposing personal data of thousands of staff, students, alumni, and supporters. Authorities and the university’s cybersecurity partners are investigating the incident, which involved unauthorized access to an internal code library. #UniversityOfSydney #DataBreach…
Category: Cyber Security News

SonicWall has released a patch for a critical privilege escalation flaw (CVE-2025-40602) affecting its SMA 1000 appliances, which has been actively exploited. The vulnerability, combined with CVE-2025-23006, allows attackers to execute commands with root privileges, emphasizing the need for urgent updates. #CVE202540602 #CVE202523006 #SonicWall #SMA1000…

North Korean scammers are using fake identities and AI tools to infiltrate US and European companies, including Amazon, for remote employment to fund their regime. Despite advanced detection methods, identifying these fraudulent applications remains increasingly challenging. #North Korea #FakeWorkerScam…
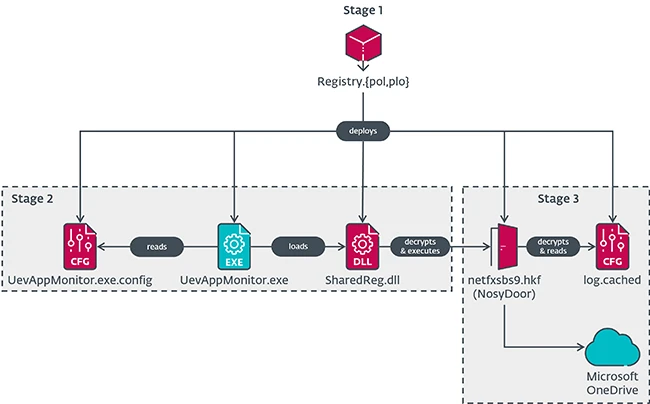
ESET Research uncovered a new China-aligned threat group, LongNosedGoblin, exploiting Windows Group Policy for malware deployment and lateral movement in government networks. The group uses cloud services like OneDrive and Google Drive for command and control, deploying sophisticated surveillance tools to conduct long-term espionage. #LongNosedGoblin #GroupPolicy #EspionageTools…

Federal authorities have dismantled an online money-laundering operation linked to ransomware proceeds and arrested the creator of E-Note, a cryptocurrency payment platform. The investigation uncovered over $70 million in illicit funds laundered through the platform, impacting sectors like healthcare and critical infrastructure. #E-Note #MykhalioChudnovets…

A security vulnerability in the Motors WordPress theme allows users with minimal privileges to upload and activate malicious plugins, risking full site control. The flaw has been fixed in version 5.6.82, emphasizing the importance of proper permission checks and updates. #MotorsTheme #WordPressVulnerability…

A security vulnerability affects certain motherboard models from vendors like ASRock, ASUS, GIGABYTE, and MSI, allowing DMA attacks during the early boot phase due to a failure in configuring IOMMU properly. Patch updates are crucial to fix these issues and prevent potential memory access breaches by malicious peripherals. #ASRock #ASUS #GIGABYTE…

Authorities in Nigeria successfully arrested three suspects linked to a major phishing operation involving the RaccoonO365 PhaaS scheme. The operation targeted Microsoft 365 users worldwide, leading to significant data breaches and financial losses. #RaccoonO365 #PhishingScheme…
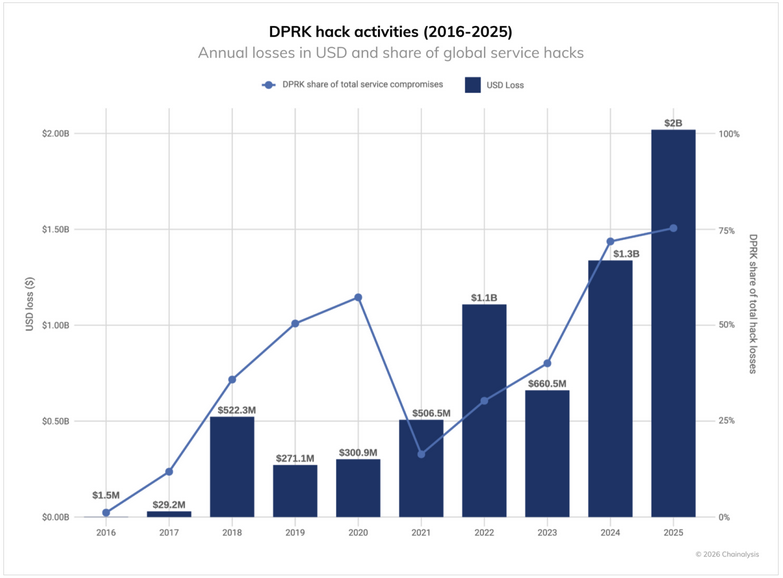
North Korea has increased its digital operations significantly, stealing over $2 billion in cryptocurrency in 2025 and deploying sophisticated fake IT worker schemes. These efforts are part of a broader strategy to fund the regime and avoid sanctions, with many cyberattacks linked to North Korean threat actors. #NorthKoreaCyberattacks #Chainalysis #BybitHeist #AmazonITWorkers…
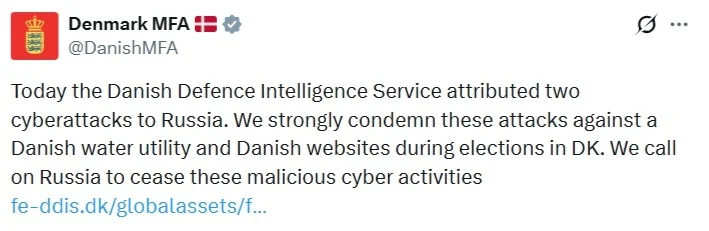
Denmark has accused Russia of orchestrating cyberattacks on critical infrastructure and election systems, escalating diplomatic tensions. These attacks highlight Russia’s broader hybrid warfare tactics aimed at destabilizing European support for Ukraine. #RussiaCyberattacks #HybridWarfare…

Daily Recap, Forum Troll APT hijacks scholars’ systems using fake plagiarism reports to deliver malware and gain access to academic networks, while a Russian APT conducts high‑pressure phishing campaigns targeting Transnistria and NATO personnel to harvest credentials and access. The report also highlights critical vulnerabilities and exploits—ASUS Live Update, AsyncOS, and React2Shell—as well as a ZeroDay Cloud event, breached platforms like PornHub and SoundCloud, and privacy concerns involving TikTok and Grindr, with FBI and France taking enforcement actions.
#ForumTrollAPT #AcademicAmbush #BlurredDeception #Transnistria #NATO #InkDragon #ASUSLiveUpdate #AsyncOS #React2Shell #ZeroDayCloud #PornHub #SoundCloud #TikTok #Grindr #FBI #France
The recent Windows 10 security update caused issues with Message Queuing (MSMQ), mainly affecting enterprise environments. Microsoft has responded with an out-of-band update (KB5074976) to fix the problem, which is available via Update Catalog. #Windows10 #MSMQ #KB5074976

The Austrian Supreme Court ruled that Meta’s personalized advertising model violates GDPR and is illegal within the EU. This decision establishes a legal precedent requiring Meta to provide users with access to their personal data and obtain explicit consent for data processing. #Meta #GDPR…
The implementation of the Digital Personal Data Protection (DPDP) Act has transformed cybersecurity risk management for Indian organizations, emphasizing the importance of regulatory compliance and cyber insurance. Cases ranging from cloud misconfigurations to AI-enabled social engineering attacks highlight the increased financial and legal implications, especially for vulnerable SMEs. #DPDPAct #CyberInsurance #DataBreaches…
An automated campaign is targeting VPN platforms like Palo Alto Networks GlobalProtect and Cisco SSL VPN with credential-based attacks, involving millions of login attempts from thousands of IPs worldwide. These attacks aim to identify weak credentials rather than exploiting specific vulnerabilities, highlighting ongoing pressure on enterprise VPN security. #GlobalProtect #CiscoSSLVPN #CredentialAttacks