
A persistent Iranian threat actor known as Infy, also called Prince of Persia, has resumed significant activity after nearly five years. New malware variants, sophisticated command and control infrastructure, and targeted attacks across multiple regions highlight the group’s ongoing danger. #PrinceOfPersia #Foudre #Tonnerre #APT35…
Category: Cyber Security News
RansomHouse RaaS has upgraded its encryptor to a more complex, multi-layered system called ‘Mario,’ enhancing encryption strength and evasion. These developments indicate a concerning trend in ransomware evolution, targeting virtual machines and complicating recovery efforts. #RansomHouse #MarioEncryptor

The U.S. Department of Justice has charged 54 individuals involved in a large ATM jackpotting scheme using malware called Ploutus, linked to the Venezuelan gang Tren de Aragua. The scheme has resulted in over $40 million in losses, allegedly funding terrorist activities and criminal enterprises. #Ploutus #TrendeAragua…

Daily Recap, major breaches impacted 27,000 University of Sydney records and about 113,000 VA patients, while UK NHS‑linked providers and other government intrusions highlighted a broad cross‑sector threat landscape. The roundup also notes ransomware takedowns like E‑Note, critical exploits from WatchGuard and Cisco AsyncOS, and campaigns such as Kimsuky’s DocSwap Android malware and North Korea–linked crypto theft, plus policy and industry responses shaping defenses. #Kimsuky #DocSwap #NKCryptoTheft #ENote #WatchGuard #CiscoAsyncOS
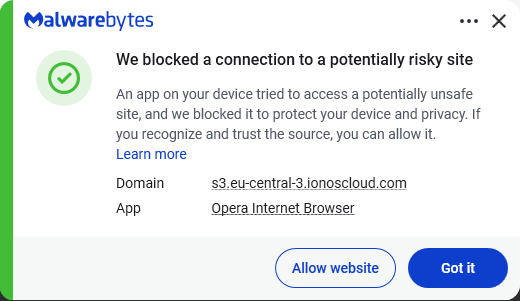
This article details a phishing attack involving a malicious PDF that leads to a fake login page designed to steal business credentials. It emphasizes the importance of vigilance and proper cybersecurity tools to prevent such intrusions. #Ionoscloud #Phishing #TelegramHack…
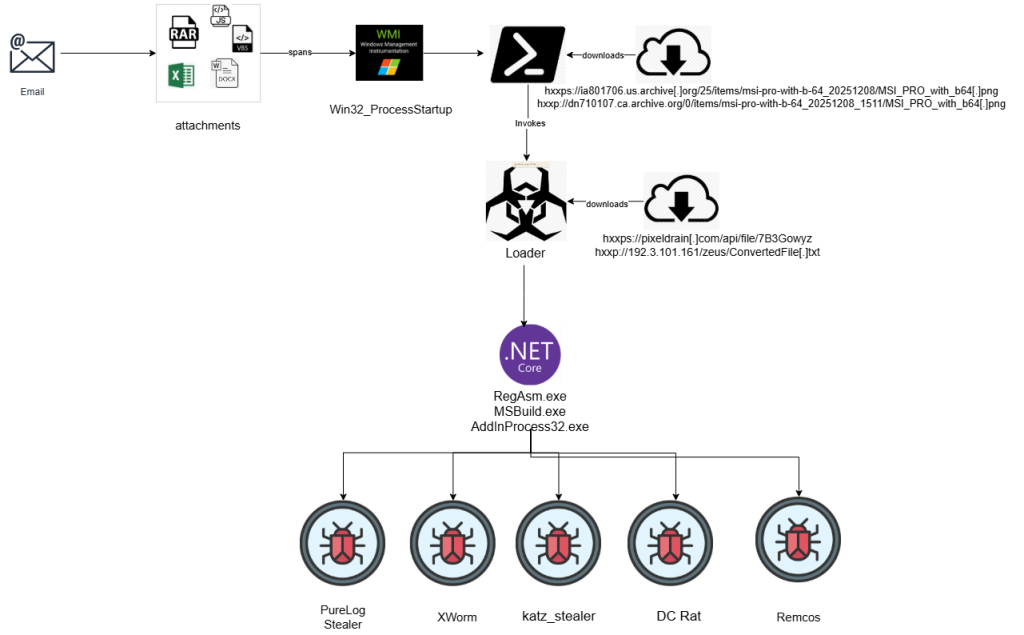
Cyble researchers have uncovered a sophisticated cyberattack campaign targeting critical sectors in Europe and the Middle East, utilizing advanced obfuscation, UAC bypass, and stealth techniques to deploy malware. The campaign employs a shared loader framework used by multiple threat actors to exfiltrate industrial data and steal high-value credentials. #Remcos #KatzStealer…
Shadowserver highlights over 25,000 Fortinet devices exposed online due to enabled FortiCloud SSO, which is exploited through a serious authentication bypass vulnerability. Cybercriminals are actively abusing this flaw to hijack admin accounts and access sensitive system configurations. #FortiCloudSSO #CVE2025-59718 #CVE2025-59719 #Shadowserver #Fortinet
This article discusses a UEFI firmware vulnerability in motherboards from ASUS, Gigabyte, MSI, and ASRock that allows DMA attacks, potentially exposing system memory. The issue impacts security protections during early boot and affects systems running certain games like Valorant, with updates from vendors and Riot Games addressing the problem. #UEFIvulnerability #DMAattack #Valorant #Vanguard
Multiple threat actors are exploiting OAuth device code authentication to compromise Microsoft 365 accounts through sophisticated phishing attacks. These campaigns involve tricking users into authorizing malicious applications without stealing passwords or bypassing MFA, with attacks increasing since September. #TA2723 #Graphish
Three individuals linked to a Microsoft 365 phishing scheme using the Raccoon0365 platform have been arrested in Nigeria, disrupting a global operation. The scheme led to widespread business email compromises, data breaches, and financial damages, with police actions supported by Microsoft and FBI intelligence. #Raccoon0365 #Microsoft365 #CybercrimeNigeria
Microsoft Teams is experiencing widespread messaging delays and service issues affecting users globally, including in the US and Europe. Microsoft is actively investigating the outage and working to identify the cause and restore normal functionality. #MicrosoftTeams #Outage

Cybersecurity researchers have uncovered a sophisticated campaign using cracked software sites to distribute CountLoader, a modular loader capable of deploying multiple malware families. The campaign demonstrates advanced persistence, propagation, and anti-detection techniques, highlighting the evolving threat landscape. #CountLoader #GachiLoader…

A Russia-aligned threat group, UNK_AcademicFlare, has been conducting a phishing campaign targeting Microsoft 365 credentials to facilitate account takeovers. The campaigns exploit device code authentication workflows and involve compromised emails from government and military sources. #UNK_AcademicFlare #DeviceCodePhishing…

A key developer linked to the RaccoonO365 phishing kit was arrested in Nigeria following coordinated efforts by Nigerian authorities, Microsoft, FBI, and U.S. Secret Service. The phishing platform was used to steal thousands of Microsoft credentials and execute business email compromises, with significant international cybercriminal activity detected. #RaccoonO365 #Microsoft #CybercrimeNigeria…

The University of Sydney experienced a data breach exposing personal information of thousands of staff, students, and alumni after hackers accessed an internal code repository. The incident is under active investigation, and the university is monitoring for any misuse of the data, which so far remains unconfirmed for publication or misuse….