The MacSync Stealer malware has recently upgraded its delivery method, removing the need for user interaction and employing more sophisticated stealth techniques. This malware, a rebranded version of Mac.c, now uses signed and notarized applications to evade detection and infect macOS devices more effectively. #MacSyncStealer #macOSMalware…
Category: Cyber Security News
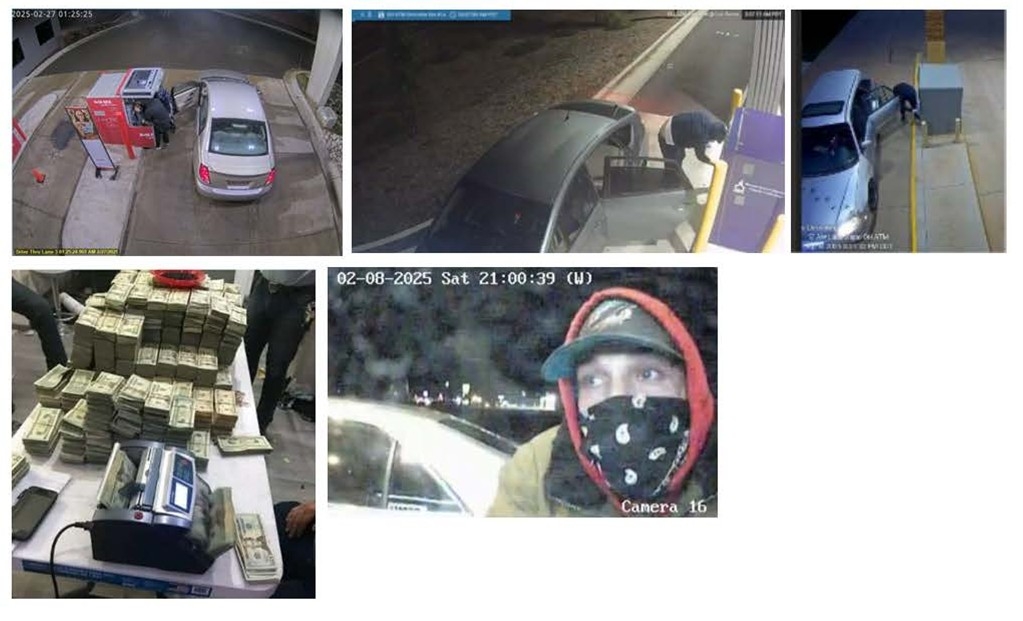
The US Department of Justice has charged 54 individuals involved in a large-scale ATM jackpotting scheme using Ploutus malware linked to the Venezuelan Tren de Aragua syndicate. The operations resulted in the theft of millions of dollars, highlighting ongoing threats from malware like Ploutus in ATM security breaches. #Ploutus #TrendeAragua…
Over 1,000 Docker Hardened Images (DHI) are now freely available as open-source, secure, minimal, and production-ready container images, aiming to reduce attack surfaces and supply-chain risks. Docker ensures timely vulnerability patches, maintaining high security standards, while making DHIs accessible to all developers without licensing restrictions. #DockerHardenedImages #ContainerSecurity
Over 115,000 WatchGuard Firebox devices exposed online remain unpatched against a critical RCE vulnerability being actively exploited. Security experts warn of the risks posed by this flaw, especially for Firebox firewalls configured with IKEv2 VPN. #CVE-2025-14733 #WatchGuardFirebox
A Ukrainian man pleaded guilty to conducting Nefilim ransomware attacks targeting high-revenue businesses worldwide. The case highlights the international scope of ransomware operations and the involvement of multiple threat actors. #Nefilim #RansomwareOperations

Cybercriminals are increasingly using disguised dropper apps to deliver sophisticated Android malware like Wonderland targeting users in Uzbekistan, enabling real-time command-and-control and data theft. These threats employ advanced obfuscation, dynamic infrastructure, and social engineering tactics to evade detection and facilitate financial fraud. #Wonderland #TrickyWonders…
The British government is investigating a cyber incident involving suspected Chinese-linked hackers accessing sensitive documents. Despite concerns, officials believe the risk to personal data remains low, amid ongoing diplomatic tensions with China. #Storm1849 #ChineseHacking…
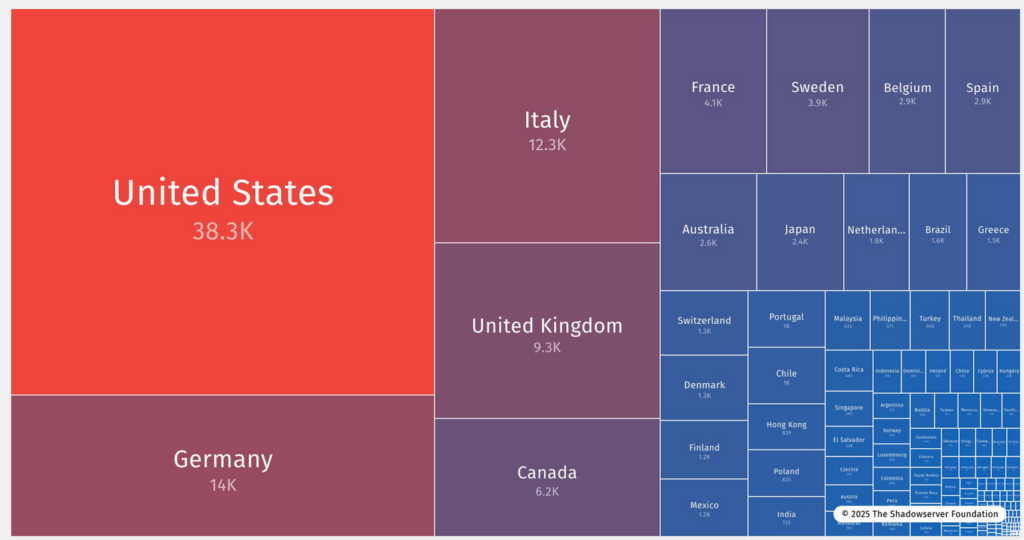
WatchGuard has issued patches for a critical vulnerability (CVE-2025-14733) in Firebox firewalls, which is actively exploited in the wild. The flaw allows remote attackers to execute arbitrary code, impacting Fireware OS versions 11.x, 12.x, and 2025.x, with significant implications for organizations using VPN configurations. #WatchGuard #FireboxVulnerability…
A new security vulnerability in Somalia’s electronic visa platform exposes sensitive personal data of thousands of travelers, adding to previous breaches. This ongoing issue highlights serious security flaws and the potential misuse of personal information across multiple countries. #SomaliaEvisa #DataBreach…
A controversy involving the acting CISA director’s alleged polygraph failure has sparked an internal investigation within DHS, leading to the administrative leave of several staff members. The incident raises concerns about leadership, accountability, and national security at CISA, which is already experiencing staffing turmoil. #MadhuGottumukkala #CISAHQ #DHSinvestigation…

AI-driven cyberattacks are becoming faster, more widespread, and more targeted, forcing organizations to rethink their cybersecurity strategies. In 2026, real-time data protection and quantum-safe encryption will be critical to safeguarding sensitive information amidst evolving threats. #AIpoweredattacks #quantumcomputing #dataprotection…

A cyber-espionage campaign by Russia’s BlueDelta group targets Ukrainian webmail users using legitimate web services to avoid detection. The campaign focuses on stealing credentials through sophisticated redirect chains and malware-laden attachments, reflecting ongoing digital conflict in Ukraine. #BlueDelta #GRU #UKR.NET #CyberEspionage…

A joint investigation by Hunt.io and Acronis reveals the complex infrastructure behind North Korea’s cyber operations, highlighting shared resources among threat groups like Lazarus, Kimsuky, and Bluenoroff. The study provides new insights into their operational habits, infrastructure, and interconnected assets, helping defenders better anticipate future attacks. #Lazarus #Kimsuky #Bluenoroff #NorthKoreaCyber #ThreatInfrastructure…

Cybersecurity Threat Research ‘Weekly’ Recap: State-aligned APTs, phishing campaigns, loader developments, and ransomware trends continue to reshape threats across government and enterprise targets. Key highlights span SideWinder and Cloud Atlas espionage, LongNosedGoblin, Ink Dragon, ForumTroll, APT35 leak, Phantom Enigma, DPRK campaigns, supply-chain and OSS tampering, OAuth device-code phishing, NexusRoute Android phishing, and ransomware trends including RansomHouse and Gentlemen.
#SideWinder #RansomHouse

Daily Recap, China-aligned APT groups abused Windows Group Policy to deploy espionage malware against governments in Southeast Asia and Japan. Other highlights include Russia accused by Denmark of destructive attacks amid Europe’s hybrid threats and North Korea-linked cybercrime with more than $3.4 billion stolen in crypto, alongside widespread vulnerability disclosures and credential-theft campaigns. #ChinaAPT #NKSurge