Microsoft Teams will soon let administrators customize the file extensions blocked by Weaponizable File Protection, giving organizations more control over which attachments are treated as high-risk. Microsoft is also adding several other Teams security features to help defend against phishing, fraud, external bots, and social engineering attacks. #MicrosoftTeams #WeaponizableFileProtection #Defender #phishing #guestinvitations
Category: Cyber Security News
Cloud collaboration in Microsoft 365 makes sharing easy, but that convenience also creates major visibility and governance gaps for sensitive data. Dedicated Identity & Access Governance tools like tenfold help close those gaps by centralizing reporting and streamlining access reviews across Teams, OneDrive, and SharePoint. #Microsoft365 #SharePoint #OneDrive #Teams #tenfold
Helpfeel says hackers breached Gyazo servers through a vulnerability in its image upload server on September 11 and accessed a database containing about 23.6 million user records. The incident also exposed roughly 490 million image metadata records and a list of private images, though payment card information was not compromised. #Helpfeel…
Hacktron used Claude to develop an exploit for a libheif flaw in Discourse, then chained it with an OpenAI sign-in token issue to take over employee ChatGPT and Codex accounts. The researchers briefly reached internal GitHub resources before stopping, and OpenAI later narrowed Community sign-in token permissions and revoked affected sessions….

SecurityWeek’s weekly roundup covers major cybersecurity developments, including new AI agent risks, active exploitation of software flaws, and law enforcement actions against cybercrime networks. It also highlights urgent fixes for SAP, WordPress, TP-Link, and AI coding tools, along with research on cloud token theft and plugin takeover techniques. #Raindrop #Mandiant #PhantomRaven…
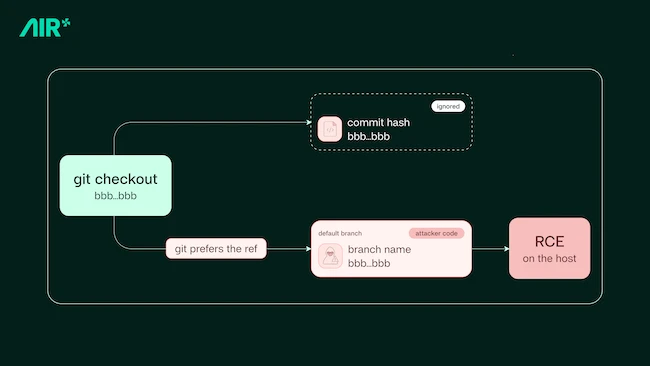
AIR uncovered Plugin4Shell, a zero-click RCE affecting Claude Code, Codex, GitHub Copilot, and Gemini CLI through a shared plugin SHA-pinning bypass. The flaw lets attackers swap in malicious code during background updates, with vendor responses ranging from patches to deprecation and no fix yet for GitHub Copilot. #Plugin4Shell #ClaudeCode #Codex #GitHubCopilot #GeminiCLI #AIR #Anthropic #OpenAI #Microsoft #Google #Antigravity

Arcjet has introduced agent runtime security to help engineering teams secure AI agents in production while giving security teams the observability, enforcement, and audit evidence they need. The product tracks agent workflows across sessions, applies deterministic controls to risky actions, and preserves execution context for reviews and compliance. #Arcjet #OpenTelemetry #Rego #OpenPolicyAgent #ClaudeAgentsSDK #OpenAIAgentsSDK #LangChain #LangFuse #Strands #Mastra #MicrosoftsAgentFramework
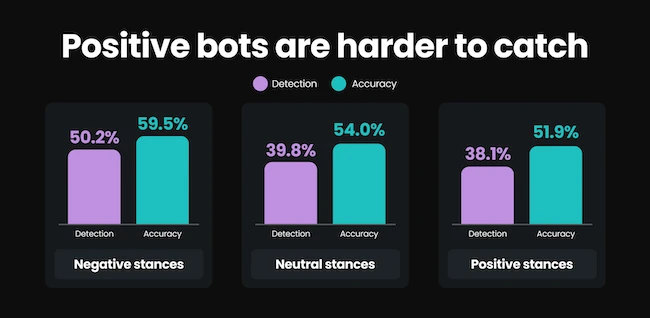
A Surfshark study found that most people struggle to tell bots from humans online, correctly identifying only 40% of AI-generated comments in a social media test. Polite, friendly, and logical-sounding bots were the hardest to detect, making them a greater concern for manipulation and privacy than hostile accounts. #Surfshark
Microsoft has fixed a known issue in KB5002914 that caused silent copy-and-paste, autofill, and formula dragging failures in Excel for some users. The released workaround update KB5002665 only addresses Microsoft Installer-based Office 2016, while affected users of other Excel versions are advised to use Paste Special or temporarily uninstall KB5002914. #Microsoft #KB5002914 #KB5002665 #Excel2016
Check Point Software has issued security updates for CVE-2026-91843, a critical stack-based buffer overflow flaw that can allow unauthenticated attackers to achieve root remote code execution on Security Management Server and Log Server systems. The company has also shared mitigation steps and detection guidance, while noting that its recently patched CVE-2026-85102 and CVE-2026-85103 vulnerabilities are considered likely to face exploitation attempts soon. #CheckPoint #CVE-2026-91843 #CVE-2026-85102 #CVE-2026-85103 #NCSC-NL #Qilin
Brevo suffered a supply chain attack after a compromised Cloudflare API key was used to inject malicious scripts into Brevo assets and customer-embedded JavaScript, impacting more than 100,000 websites. The attack followed an earlier SAML SSO abuse that exposed 138 accounts, including Trezor, and used fake Cloudflare verification pages to trick…
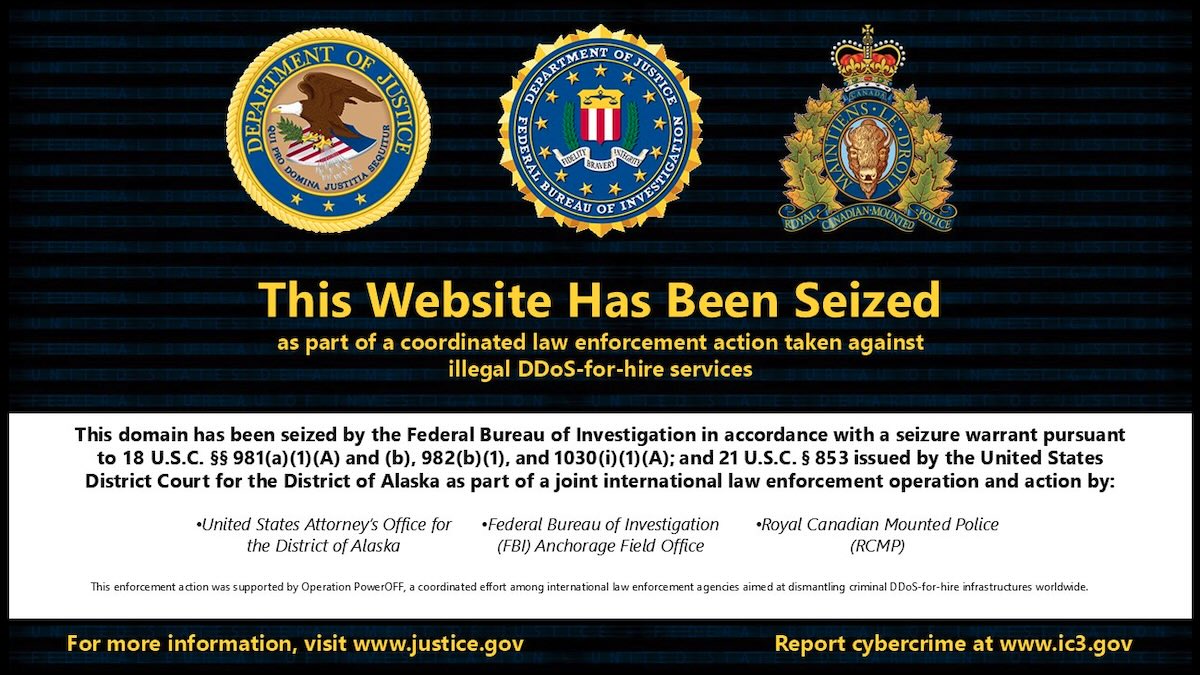
The FBI has seized the domains of NightmareStresser, a long-running DDoS-for-hire service that was used to launch hundreds of thousands of attacks worldwide. The takedown was part of Operation PowerOFF, a global effort to disrupt booters and stressers and hold their operators accountable. #NightmareStresser #OperationPowerOFF #FBI #USDepartmentofJustice…
Microsoft released patches for 18 vulnerabilities across Azure services and Copilot-branded AI products, with most issues involving elevation of privilege and several information disclosure flaws. The company said none of the bugs are known to be exploited, and all Azure and Copilot fixes were handled server-side, while Windows users must update…
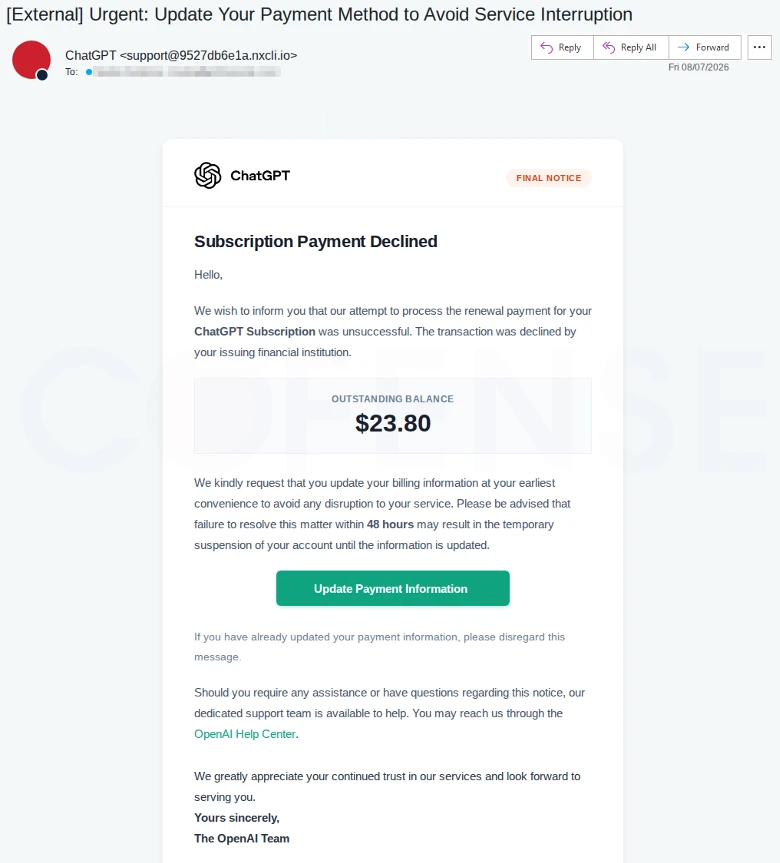
A fake ChatGPT billing email is luring users to a counterfeit OpenAI login page that steals any username and password entered. Cofense traced the attack through a Google redirect and identified indicators tied to the nxcli[.]io host, while urging users to verify the address bar shows auth.openai.com before signing in. #ChatGPT #OpenAI #Cofense #nxcliio

Cisco disclosed CVE-2026-76460, a maximum-severity zero-day in Cisco Identity Services Engine (ISE) that was actively exploited before patching. The flaw lets a remote attacker bypass authentication, take full control of the device, and potentially move laterally across networks managed by ISE. #Cisco #CiscoISE #CVE-2026-76460