Gopass is a free, open-source command-line password manager designed as a drop-in replacement for pass, using GPG encryption and git-backed storage to manage secrets across devices. It also supports alternative storage and encryption options, works on Linux, macOS, Windows, and the BSDs, and can operate offline or on air-gapped machines. #Gopass #pass #GPG #age #fossil
Category: Cyber Security News
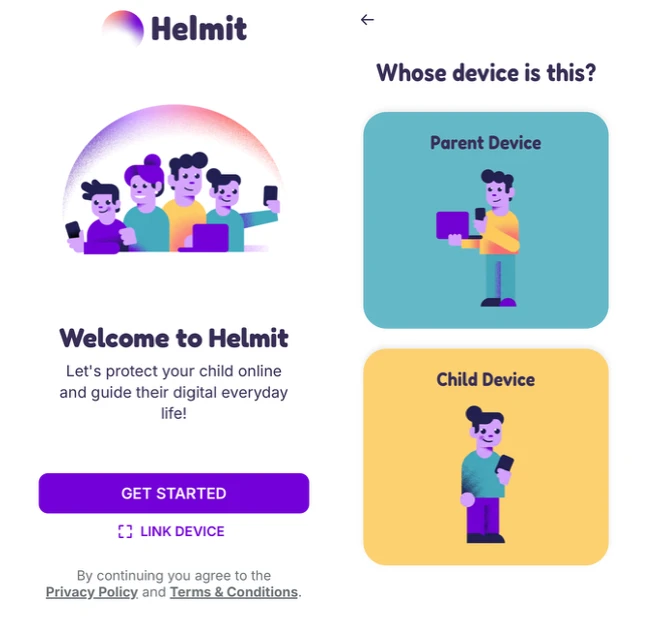
Helmit is a parental control app that combines AI-powered social media monitoring, screen time limits, web filtering, location tracking, and safety alerts to help parents identify online risks. It supports multiple devices and services, including WhatsApp, Instagram, Telegram, Discord, Signal, YouTube, Gmail, and Outlook, while showing only the messages tied to alerts rather than full chat histories. #Helmit #WhatsApp #Instagram #Telegram #Discord #Signal #YouTube #Gmail #Outlook #EUKidsAct
Large companies may choose to stay on ECC past the 2027 deadline and pay SAP for extended support until 2030, often because the real concern is disruption rather than budget. A Central American migration showed that even when every quality gate is met, poor sizing, thin testing coverage, and limited client bandwidth can still make go-live difficult. #SAP #ECC #MIGNOW #CentralAmerica

Cybersecurity Threat Research ‘Weekly’ Recap. The roundup covers credential theft, phishing, and session abuse using device-code kit GhostCode, rogue Entra MFA provider TrustSink, and Fast Flux phishing infrastructure, alongside regional lures like Falso Bonus Vacanze and banking malware KREMLIN and RatHat. It also highlights cloud/identity and APT activity (including TraderTraitor, NightEagle, FamousSparrow/SparroWocky/SquawkDoor, and Operation RapidRust) plus crimeware and supply-chain/underground operations such as XMRig, MovieReaper, Evooo1Bot, PhantomRaven, and Tajin Group.

Last week’s security news highlighted major breaches, active exploits, and AI-related risks, including incidents at Revolut, CenterPoint Energy, HBO Max, and the first data breach blamed on an autonomous AI agent in Spain. It also covered critical vulnerabilities in Cisco Secure Email Gateway, Cisco ISE, Acronis, Parallels Desktop, and AI coding agents, alongside new guidance and tools from CISA, ENISA, NIST, Google, and Microsoft. #Revolut #CenterPointEnergy #HBOMax #CiscoSecureEmailGateway #CiscoISE #Acronis #ParallelsDesktop #ENISA #CISA #NIST #Google #Microsoft
Researchers uncovered two sandbox escapes in OpenAI Codex, including Heapjack and Overpatch, that could let attacker-controlled code run commands outside Codex’s intended restrictions. OpenAI patched both issues quickly, and users are advised to update to Codex Desktop build 26.818.21641 or Codex CLI 0.149.0 and later. #OpenAICodex #Heapjack #Overpatch #CodexDesktop #CodexCLI
The indexed-btree npm campaign hides malicious code in normal runtime behavior to bypass new GitHub and npm supply chain defenses, while impersonating the legitimate sorted-btree library. Checkmarx found the package and nine related npm packages, which exposed victims to data theft, C2 activity through Slack, Telegram, and an Ethereum smart contract, and possible trace removal by the attackers. #indexed-btree #sorted-btree #Checkmarx #GitHub #npm #Sepolia

North Korean hackers tied to the WaterPlum campaign stole more than $10.5 million by posing as AI and blockchain recruiters to target job seekers and infect their devices. The operation overlapped with North Korean IT worker schemes and used malware such as BeaverTail, InvisibleFerret, OtterCookie, OtterCandy, and StoatWaffle to steal cryptocurrency…

Daily Recap, TigerByte Cyber emerged from stealth with $3 million in funding, while multiple nation-state and AI-driven advances underscored how fast attackers are operationalizing new techniques. North Korea’s WaterPlum campaign reportedly infected 30,000 devices and used fake job-seeker lures, and research showed AI-assisted exploitation could chain weaknesses to gain access to OpenAI staff accounts. #TigerByteCyber #WaterPlum #TransparentTribe #RustBackdoor #SolarWinds #ARMHardCodedKey #WordPressClick2Shell #Gyazo #Click2Shell #ClaudeOpus5 #Rapuncel #LastPassAuthenticator #ScatteredSpider #AhmedElbadawy #OpenAI
NightEagle, also known as APT-Q-95, has expanded its cyberespionage operations from China to Russian companies, using stolen VPN credentials, Microsoft Exchange abuse, and the GhostContainer backdoor to infiltrate networks. The group also relied on GitHub for tool storage and exploited Active Directory to deepen access, steal credentials, and attempt control of…
Multiple countries have taken legal and sanctions actions after a UN-linked report exposed North Korea’s illicit IT worker scheme and the network of local facilitators supporting it. The MSMT said the program has spread across dozens of countries, generated hundreds of millions of dollars, and is now facing tighter scrutiny in…

Identity visibility gives security teams a continuous view of every identity, its real permissions, and how those permissions are used across cloud, SaaS, and on-prem environments. The article explains why hidden identities, machine accounts, and cross-cloud trust relationships create blind spots that traditional IAM reporting often misses, and how identity visibility…
Tilly Norwood’s viral Piers Morgan appearance drew fresh attention after the AI actress glitched and began speaking Chinese, sparking questions about whether the moment was accidental or a publicity stunt. The accompanying “Talking Tilly” service also revealed strict biometric age checks, emotion monitoring, recorded calls, and short-lived paid access tied to Xicoia’s rollout and UK online safety rules. #TillyNorwood #TalkingTilly #Xicoia #PiersMorgan #Misaligned
ShinyHunters breached Clop’s data leak site, defaced its Tor page, and claimed to steal server data, logs, source code, and the private keys for Clop’s onion service. The incident appears tied to an escalating feud between the two groups over earlier Oracle E-Business Suite attacks and alleged threats. #ShinyHunters #Clop #OracleEBusinessSuite #CVE202561882
Security researcher Gal Weizman of Forever Security revealed BragJack, a new attack technique that can hijack AI assistants inside popular browsers through a single malicious extension. The findings affected Google Chrome’s Gemini Live, Perplexity Comet, Microsoft Edge, Opera Neon, and Claude in Chrome, and led to two CVEs and bug bounty rewards from multiple vendors. #BragJack #GalWeizman #ForeverSecurity #GoogleChrome #GeminiLive #PerplexityComet #MicrosoftEdge #OperaNeon #ClaudeinChrome #CVE-2026-0628 #CVE-2026-55945