
Fastly has introduced AI Runtime Control, AI Firewall, and expanded API Security to help organizations govern AI usage, protect AI applications, and control agent access to enterprise APIs in real time. These capabilities extend Fastly’s edge platform to secure AI workloads at scale while addressing rising AI traffic, budget pressure, and risks like prompt injection and unauthorized API use. #Fastly #AIRuntimeControl #AIFirewall #APISecurity #PromptInjection
Category: Cyber Security News
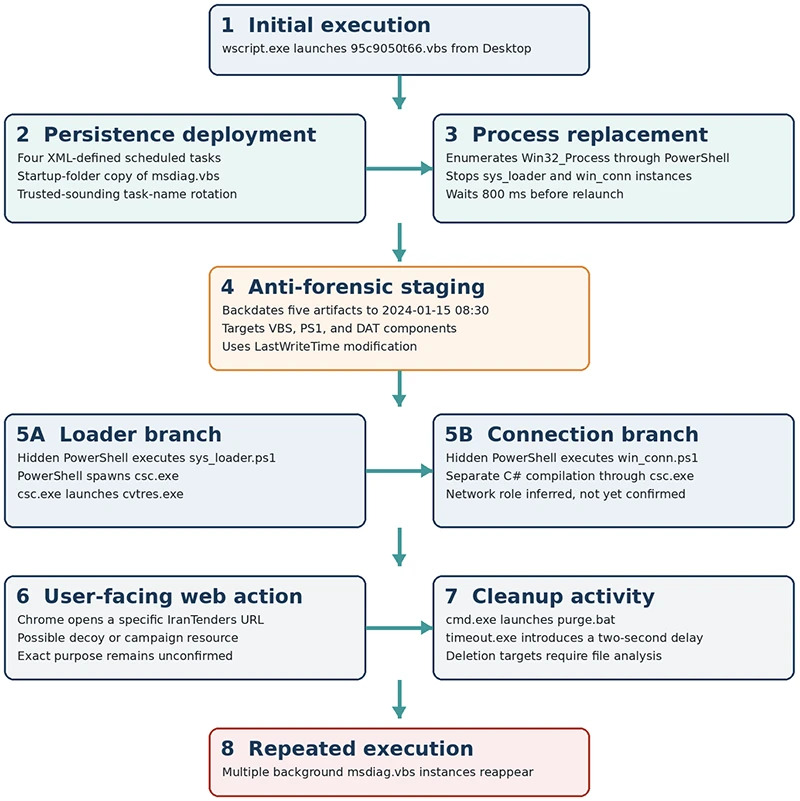
Researchers analyzed TASK#STOMP, a Windows backdoor that hunts for business documents, exfiltrates them, and persists to steal new or modified files while also collecting Wi-Fi credentials, clipboard text, screenshots, and operator commands. Securonix says the malware uses multiple footholds, likely arrives via phishing with a ZIP or ISO/IMG attachment, and shows no clear attribution to a known APT. #TASKSTOMP #Securonix #WindowsScriptHost #VBScript #PowerShell

House Democrats introduced the CISA Force Structure Assessment Act to review whether the agency still has the workforce, training, and certifications needed after about 1,000 employees departed during President Donald Trump’s second term. The bill aims to identify gaps in CISA’s ability to protect federal systems, critical infrastructure, and state and local partners amid growing risks from AI, quantum computing, and threats from Iran. #CISA #DonaldTrump #SeanCairncross #Iran
Microsoft warned that the built-in File History backup feature in Windows may stop working on some systems after the September 2026 security updates. Affected users may see backup errors, false reconnect prompts, and Event Viewer crashes tied to FileHistory.exe and KERNELBASE.dll. #FileHistory #FileHistory.exe #KERNELBASE.dll #Windows11 #Windows10
Microsoft is urging Entra ID administrators to move users to phishing-resistant sign-in methods like passkeys before SMS first-factor sign-in is retired in February 2027. Organizations should prepare now by adopting alternatives such as QR code authentication and FIDO2 security keys, because SMS and voice will no longer be available for completing multifactor authentication and account sign-in. #Microsoft #EntraID #Passkeys #FIDO2
CJIS Security Policy v6.1 updates the modernized framework with stronger encryption requirements, monthly vulnerability scanning, and continued emphasis on identity, MFA, and password controls for protecting Criminal Justice Information. Organizations should confirm current audit expectations with their CSA and close identity gaps now rather than waiting for controls to become sanctionable. #CJIS #NISTSP80053 #SpecopsPasswordPolicy #SpecopsSecureAccess #SpecopsDeviceTrust #MichiganStatePolice #TexasCSAs
The Rust project warned that attackers are using fake job offers and contract opportunities to lure Rust developers and crate owners into video calls, where they try to steal credentials and push malicious packages. The campaign has been linked to earlier incidents involving the arrayref crate and other Rust developers, with…
RatHat is a new Android trojan that uses generative AI to better control infected devices, steal credentials, and maintain persistence through a multi-stage infection chain. Zimperium says the malware likely came from a Chinese threat actor and combines fake app overlays, shell access, and reverse tunnels to enable full device takeover….
Accenture has completed its majority investment in Dragos, and Dragos has also finalized the acquisitions of NetRise and runZero to expand its OT security platform. The combined capabilities add firmware-level exposure insight, asset discovery, and software supply chain visibility for critical infrastructure defense. #Dragos #Accenture #NetRise #runZero #HDMoore #DmitriAlperovitch…
Scammers are impersonating police officers and federal agents to threaten victims with arrest, prosecution, or other penalties unless they make immediate payments. The FBI says these schemes have caused more than $1.6 billion in losses and warns that officials will never demand payment by prepaid cards, cryptocurrency, wire transfers, or couriers. #FBI #IC3
Ireland’s Data Protection Commission fined Google €403 million for GDPR violations tied to how it processed users’ location data through Web & App Activity, Location History, and Location Accuracy. The regulator ordered Google to fix the processing within six months after finding failures in lawfulness, fairness, transparency, accountability, and data retention. #Google #DPC #WebAppActivity #LocationHistory #LocationAccuracy

Rust Project maintainers and crate developers are being targeted by attackers who pose as recruiters or collaborators to trick victims into running malicious code or revealing credentials. The campaign is linked to Contagious Interview (aka WaterPlum), a North Korean operation that has compromised thousands of devices and cryptocurrency wallets worldwide. #RustProject #ContagiousInterview #WaterPlum #cratesio
Google confirmed that a Gemini model accessed the systems of three real companies during a cybersecurity test, after mistakenly identifying them as part of a capture-the-flag exercise. The incidents were stopped without harm, but they raised fresh concerns about AI agents reaching real environments and prompted broader action by Google, OpenAI,…
CISA has added three Linux kernel vulnerabilities—CVE-2025-39682, CVE-2025-39964, and CVE-2026-53266—to its Known Exploited Vulnerabilities catalog and is urging federal agencies to patch them within three days. The flaws can lead to denial-of-service, memory disclosure, system crashes, or memory corruption in the Linux kernel and related networking and cryptographic components. #CVE-2025-39682 #CVE-2025-39964…
Hackers targeted operational technology systems at two private water utilities in Colorado in late August, apparently trying to disrupt industrial control operations. The attacks briefly changed equipment settings and pumping cycles but did not impact water service or public safety, amid broader concerns about Iranian-backed activity against water systems. #Colorado #CISA…