
A new variation of a fake recruiter campaign attributed to North Korea’s Lazarus group targets JavaScript and Python developers with cryptocurrency-related coding tasks that trick applicants into running malicious repositories. Researchers uncovered 192 malicious npm and PyPI packages dubbed “Graphalgo” that deliver a modular RAT capable of MetaMask theft, token‑protected C2, remote command execution, and data exfiltration; impacted developers should rotate credentials and reinstall their OS. #Graphalgo #Lazarus
Category: Cyber Security News
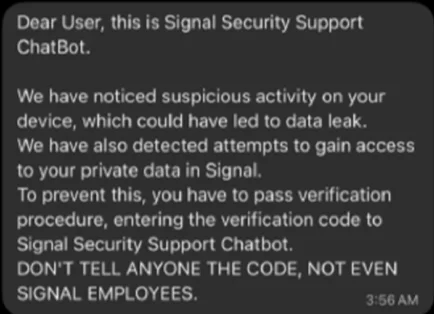
German security authorities warn that a likely state-backed hacking group is using Signal to phish senior politicians, military officials, diplomats, and investigative journalists across Germany and Europe. The alert describes two attack variants—fake Signal support requests for PINs or codes and QR-code prompts that link an attacker’s device—and urges users to…
Flickr suffered a data breach on February 5 that stemmed from a compromise of a third-party email service provider, and the company shut down access to the affected system, removed vulnerable links, and notified its email provider and data protection authorities. Potentially exposed information includes names, email addresses, usernames, account types,…
Attackers harvest organization-specific language from public-facing content to build targeted wordlists using tools like CeWL, then mutate those words into high-probability password guesses tested with tools such as Hashcat. Defenders must block context-derived and known-compromised passwords, enforce long passphrases, and use MFA alongside solutions like Specops Password Policy to reduce the effectiveness of CeWL-style attacks. #CeWL #ActiveDirectory
SmarterTools confirmed that the Warlock group breached its network by exploiting an unpatched SmarterMail VM (CVE-2026-23760), allowing lateral movement via Active Directory and deployment of tools like Velociraptor and SimpleHelp. SentinelOne prevented final encryption, affected systems were isolated and restored from backups, and administrators are advised to upgrade SmarterMail to Build 9511 or later. #SmarterMail #Storm2603
China appears to have used a secret cyber range called Expedition Cloud to rehearse attacks on replicas of neighboring countries’ critical infrastructure, according to a cache of leaked development and training files. The materials, linked to developer files from CyberPeace and obtained via an exposed FTP server, show staged reconnaissance and…
Senegal’s Directorate of File Automation (DAF) suspended operations after a cyberattack that a ransomware gang calling itself Green Blood Group claims included the theft of 139 GB of citizen data, including biometric records, passports, and ID card personalization files. IRIS Corporation Berhad and Malaysian cybersecurity teams have been engaged to investigate…
Coveware’s report concludes that pure data-exfiltration extortion is no longer widely profitable, prompting many ransomware groups to return to encryption or seek other ways to monetize network access. Despite low overall payment rates after breaches like MOVEit and Cleo, average ransom settlements rose due to isolated high-impact incidents, and attackers such…

Lema AI, a startup founded in 2023 by Eddie Dovzhik, Omer Yehudai, and Tomer Roizman, emerged from stealth with $24 million in seed and Series A funding to commercialize an agentic AI platform for continuous third-party supply chain risk management. Its autonomous system continuously analyzes vendor access, data flows, and permission…
The European Commission’s central mobile device management infrastructure was hit by a cyberattack on January 30 that may have exposed staff names and mobile numbers, but the system was contained and cleaned within nine hours with no compromise of mobile devices detected. Observers suspect a link to a Dutch campaign exploiting…
The European Commission is investigating a breach after detecting traces of a cyberattack on its mobile device management platform that may have exposed some staff names and phone numbers, though no mobile devices have been found to be compromised. The incident appears linked to zero-day code-injection flaws in Ivanti Endpoint Manager Mobile (EPMM) that have also affected Dutch authorities and Finland’s Valtori, and the Commission says the system was contained and cleaned within nine hours. #IvantiEPMM #EuropeanCommission
Microsoft is investigating an ongoing Exchange Online issue that began on February 5, where a new URL rule is incorrectly flagging legitimate emails as phishing and quarantining them, blocking some users from sending or receiving messages. The company is reviewing and releasing quarantined messages while working to unblock affected URLs and confirm full remediation. #Microsoft #ExchangeOnline
Two Connecticut men were indicted for allegedly using stolen personally identifying information from about 3,000 victims to create thousands of fraudulent accounts on gambling sites and steal roughly $3 million through promotional bonuses. Authorities say they purchased PII from darknet markets and Telegram, used services like TruthFinder and BeenVerified to pass verification, converted winnings to virtual stored-value cards, and face multiple federal charges including wire fraud, identity theft, and money laundering. #FanDuel #AmitojKapoor
BeyondTrust warned of a critical pre-authentication remote code execution vulnerability (CVE-2026-1731) in Remote Support and Privileged Remote Access that allows unauthenticated attackers to execute OS commands via crafted client requests. The vendor has secured cloud instances and urged on‑premises customers to upgrade to Remote Support 25.3.2 and Privileged Remote Access 25.1.1 to mitigate exposure affecting roughly 11,000 internet-facing instances. #CVE-2026-1731 #BeyondTrust
A wave of cyberattacks exploiting two critical code-injection vulnerabilities in Ivanti Endpoint Manager Mobile (tracked as CVE-2026-1281 and CVE-2026-1340) has prompted emergency warnings from national security agencies worldwide. Ivanti released patches and urged customers to treat exposed systems as potentially compromised after confirmed and suspected breaches affected Dutch government bodies and…