
Ireland’s Data Protection Commission has opened a large-scale GDPR investigation into Elon Musk’s X Internet Unlimited Company over its Grok AI generating nonconsensual sexually explicit deepfake images, including images reportedly involving children. The probe — running alongside separate EU and UK inquiries under the Digital Services Act — could result in…
Category: Cyber Security News
The NCSC warns SMEs that assuming they are too small to be targeted is dangerous and urges urgent action through the UK government-backed Cyber Essentials baseline. Richard Horne stresses closing the awareness–action gap by implementing simple controls and using NCSC-assured support to reduce exposure to opportunistic automated attacks. #CyberEssentials #NCSC…

Daily Recap, researchers report a live ClawdBot infection that exfiltrates OpenClaw configurations (including private keys) enabling AI‑agent impersonation, while CTM360 warns of a global campaign distributing Lumma Stealer and a trojanized Ninja Browser via Google Groups and weaponized ad fraud. Patch alerts follow, with BeyondTrust CVE-2026-1731 requiring patching within 3 days, Google Chrome’s high‑severity zero‑day CVE-2026-2441 being fixed across platforms, Windows 11 boot issues addressed by KB5077181, Lotus Blossom hijacking Notepad++ updates to deploy Chrysalis and Cobalt Strike in high‑value targets, and VoidLink campaigns affecting technology and financial sectors alongside ShinyHunters’ Canada Goose data leak. #ClawdBot #OpenClaw #LummaStealer #NinjaBrowser #ModeloRAT #NotepadPlusPlus #Chrysalis #CobaltStrike #LotusBlossom #VoidLink #ShinyHunters #CanadaGoose #BeyondTrust #ChromeZeroDay

A targeted cyberespionage campaign called Operation MacroMaze, attributed to Russian state-sponsored APT28, has been active since late September 2025 and targets government entities in Western and Central Europe using decoy Spanish government documents. The operation uses simple “living off the land” techniques—malicious macros, VBScript and headless Microsoft Edge—to track document openings…
Researchers at ETH Zurich analyzed popular cloud-based password managers under a malicious-server (zero-knowledge) threat model and found multiple ways attackers could compromise users’ vaults. They demonstrated full vault compromise for Bitwarden and LastPass, shared-vault compromise for Dashlane, and attacks targeting account recovery, SSO, sharing, and vault integrity, while vendors have issued…

The Federal Government filed a three-count criminal charge against former Kaduna State governor Nasir El-Rufai, accusing him of unlawfully intercepting National Security Adviser Nuhu Ribadu’s communications and failing to report related offenses. The case, brought by the DSS under provisions of the Cybercrimes (Amendment) Act 2024 and the Nigerian Communications Act…

A January breach of Eurail’s customer database has escalated into a large-scale identity theft crisis after attackers began offering millions of travelers’ sensitive records for sale on criminal marketplaces and publishing a sample on Telegram. The compromised information—names, passport numbers, ID numbers, IBANs, health data and contact details—puts DiscoverEU participants at…
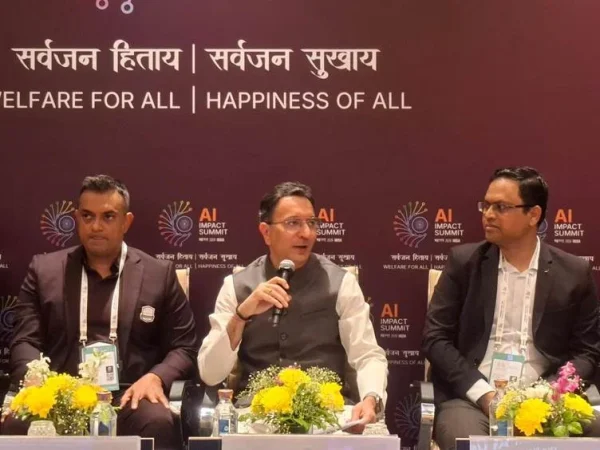
The India AI Impact Summit 2026 convened global leaders, ministers, researchers and industry in New Delhi to position the Global South as a co-creator of AI governance and to translate policy into scalable implementation across People, Planet and Progress. Key themes included aligning AI adoption with mass employability, digital sovereignty, open-source…
CISA will remain operational during the DHS shutdown but at reduced capacity, requiring 888 of its 2,341 staff to work in excepted areas without pay while many projects and new work are curtailed. The KEV Catalog will remain online and can be updated for actively exploited vulnerabilities, but regulatory work like…
Google released the first Android 17 beta with a range of privacy, security, and developer-focused improvements across performance, media, camera, and connectivity. Major security changes include deprecation of the usesCleartextTraffic attribute (blocking cleartext by default without a network security config), a public SPI for HPKE hybrid cryptography, certificate transparency enabled by…
South Korea’s PIPC fined Louis Vuitton, Dior, and Tiffany a combined 36 billion won after a hacker campaign exposed millions of customer records through a SaaS intrusion tied to attacks on Salesforce customers. The Scattered LAPSUS$ Hunters extortion group gained access via social engineering, including voice phishing and malware on employee…
An actively exploited use-after-free flaw in Google Chrome’s CSS engine, tracked as CVE-2026-2441, enables remote code execution and prompted an out-of-band emergency update. Users should update Chrome Stable on Windows, macOS, and Linux to versions 145.0.7632.75/76 or 144.0.7559.75 (or extended 144.0.7559.177) immediately to mitigate the risk #CVE-2026-2441 #GoogleChrome…
OpenClaw configuration and memory files containing API keys, authentication tokens, private keys, and agent memories were exfiltrated in the first reported in-the-wild infostealer compromise, likely a Vidar variant, enabling potential full compromise of a user’s AI agent identity. Researchers warn infostealers will increasingly target agent frameworks as they become widespread, and Tenable also disclosed a separate max-severity remote flaw in Nanobot (CVE-2026-2577) that was patched. #OpenClaw #Vidar #HudsonRock #Nanobot #CVE-2026-2577
Dutch police arrested a 40-year-old man after he downloaded confidential documents that were mistakenly shared by an officer and then refused to delete them unless he received “something in return.” Authorities detained the suspect in Ridderkerk, seized data storage devices during a home search, and said knowingly downloading misdirected files after being told not to may amount to computer trespass under Dutch law. #DataBreachesNet #DutchPolice
Eurail B.V. confirmed that customer data stolen in a breach earlier this year is being offered for sale on the dark web and a sample of the data was published on Telegram. The company is investigating which records and how many customers were affected, has notified data protection authorities under the GDPR, and advises customers to change Rail Planner passwords, reset reused credentials, and monitor bank accounts. #Eurail #Telegram #GDPR #RailPlanner #DiscoverEU