Notepad++ has rolled out a “double-lock” update verification in version 8.9.2 that checks both the GitHub-signed installer and an XMLDSig-signed XML from notepad-plus-plus.org to prevent supply-chain tampering. The change follows a six-month compromise attributed to the Lotus Blossom group that used the Chrysalis backdoor, and users are urged to upgrade to 8.9.2 and download installers only from the official domain. #NotepadPlusPlus #LotusBlossom
Category: Cyber Security News
A suspected Chinese state-backed group, UNC6201, has been exploiting a hardcoded-credential zero-day (CVE-2026-22769) in Dell RecoverPoint for Virtual Machines since mid-2024 to gain unauthenticated access and root persistence. The intruders deployed a new C# backdoor called Grimbolt (replacing Brickstorm) and used stealthy Ghost NICs on VMware ESXi to move laterally; Dell urges immediate remediation. #UNC6201 #Grimbolt
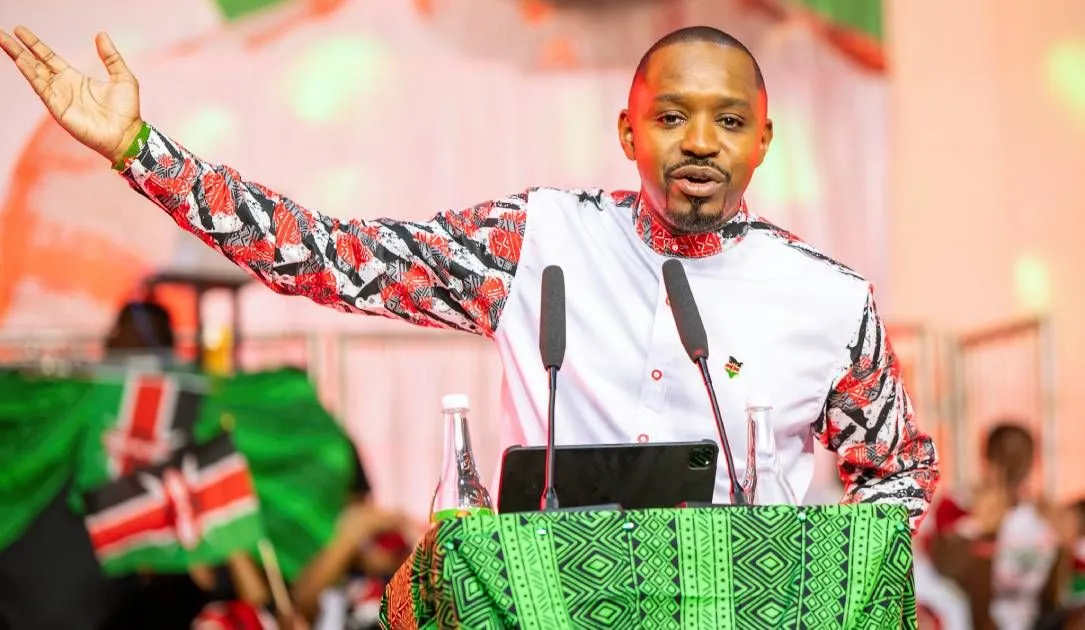
Citizen Lab found traces of Cellebrite’s commercial data-extraction technology on Kenyan activist Boniface Mwangi’s phone after his arrest, suggesting his private communications and photos were accessed. The discovery adds to allegations of Cellebrite being used against activists in multiple countries and has sparked calls for the company to publish its sales…
Canada Goose said a recently published dataset claimed by the ShinyHunters group appears to be a historical customer transactions file and not the result of a breach of its systems. The company is reviewing the data and reports no evidence of unmasked financial information, while ShinyHunters has continued high-profile campaigns using…

Polish police arrested a 47-year-old man in Małopolska for alleged involvement with the Phobos ransomware operation after finding encrypted communications during raids coordinated in Katowice and Kielce, and he now faces up to five years in prison. International law enforcement actions under Operation Aether have disrupted Phobos and its spinoff 8Base—linked…
Eurail disclosed a mid-January breach in which attackers stole customer personal, order, reservation, passport, and sensitive DiscoverEU data and are now offering the stolen records for sale. The hackers claim to have exfiltrated roughly 1.3 TB from AWS S3, Zendesk, and GitLab and have posted samples on Telegram while threatening to…
Vulnerability intelligence company VulnCheck announced a $25 million Series B funding round led by Sorenson Capital to expand product development and scale growth. The platform tracks CVEs, exploit availability, proof-of-concept code, and weaponized payloads to help security teams prioritize truly exploitable vulnerabilities and accelerate patching efforts. #VulnCheck #CVEs…
Ireland’s Data Protection Commission has opened a formal GDPR investigation into X over its Grok AI allegedly generating non-consensual sexual images of real people, including children. The inquiry joins parallel probes by the ICO, the European Commission, California’s attorney general, Ofcom, and French prosecutors and could result in significant EU‑wide fines and criminal measures. #Grok #X
Polish police arrested a 47-year-old in the Małopolska region suspected of ties to the Phobos ransomware group and seized computers and phones containing stolen credentials, credit card numbers, and server access data. The arrest was part of Operation Aether, an international Europol-coordinated effort that has disrupted Phobos infrastructure, led to extraditions and server seizures, and warned hundreds of companies of imminent attacks. #Phobos #OperationAether
Keenadu is a newly discovered, highly sophisticated Android backdoor embedded in firmware across multiple device brands that can compromise every installed app and give attackers unrestricted control. Kaspersky reports multiple distribution methods — including compromised OTA firmware, system apps, modified APKs, and apps on Google Play — and has confirmed about 13,000 infected devices worldwide. #Keenadu #Kaspersky
Intruder scanned 5 million JavaScript bundles and uncovered more than 42,000 exposed tokens across 334 secret types, including active GitLab and GitHub repository tokens and a Linear API key. Traditional SAST, DAST, and infrastructure scanners often miss secrets baked into single-page application builds, so Intruder built automated SPA secrets detection to find them before attackers do. #GitLab #Linear

DavaIndia’s Next.js-based platform had an exposed admin subdomain that allowed unauthenticated access to super-admin APIs, which a security researcher exploited to create a super-admin account. The vulnerability exposed customer orders, personal data, inventory and drug-control functions, was reported on August 20, 2025, fixed within a month, and confirmed closed with CERT-In…
Industrial Control Systems (ICS) remain highly vulnerable because decades‑old hardware, outdated protocols, and operators’ inability to accept downtime prevent effective patching and replacement amid growing nation‑state pre‑positioning and ransomware pressure. To build long‑term resilience in 2026, experts recommend OT‑aware zero trust, identity‑centric controls, microsegmentation, continuous threat exposure management (CTEM), supply‑chain transparency,…
APIs remain a primary attacker-favored route — Wallarm found 17% of 2025 vulnerabilities were API-related and 43% of exploited CISA KEV entries in 2025 were tied to APIs, contributing to major breaches at 700Credit, Qantas, and Salesloft. The rapid growth of AI and the Model Context Protocol (MCP) is amplifying API…
A critical vulnerability in the CleanTalk Anti-Spam WordPress plugin (up to version 6.71) could put as many as 200,000 websites at risk. Tracked as CVE-2026-1490 with a CVSS score of 9.8, the flaw can allow unauthenticated attackers to install arbitrary plugins and potentially achieve remote code execution, and was disclosed by…