Identity is no longer a reliable sole basis for workforce access because employees connect from diverse, unmanaged, and changing devices and contexts that can quickly alter risk after authentication. Specops’ Infinipoint implements continuous device verification, device-based access controls, and one-click remediation to extend Zero Trust beyond identity and protect systems like Active Directory. #ActiveDirectory #Infinipoint
Category: Cyber Security News
New York‑based ad tech firm Optimizely notified an undisclosed number of customers that threat actors accessed some internal systems in a voice‑phishing attack and stole basic business contact information. The company says attackers could not escalate privileges or access sensitive customer data, and the incident is suspected to be linked to the ShinyHunters extortion group; customers are warned to watch for follow‑up phishing using the stolen contacts. #Optimizely #ShinyHunters
Microsoft is investigating a known bug that causes the mouse pointer (and sometimes the cursor) to disappear in the classic Outlook desktop client, making the app difficult or unusable for affected users. The company has asked administrators to open support cases and submit diagnostic logs, offered three temporary workarounds (clicking an email, switching to PowerPoint and back, or restarting the PC), and said a permanent fix timeline is not yet available. #Outlook #Microsoft365
Spanish authorities have arrested four alleged members of the hacktivist group Anonymous Fénix, accused of carrying out DDoS attacks against government ministries, political parties, and public institutions in Spain and several South American countries. The group escalated activity after Valencia’s October 2024 flash floods, using X and Telegram to spread anti-government messaging and recruit volunteers, and courts ordered seizure of their social accounts following the arrests. #AnonymousFenix #GXCTeam
Multiple mental health mobile apps on Google Play contain security vulnerabilities that could expose users’ sensitive therapy and medical information. Oversecured’s analysis of ten apps uncovered 1,575 issues — including high- and medium-severity flaws like Intent.parseUri misuse, insecure local storage, plaintext configuration data, and weak token generation — and researchers cannot confirm whether fixes have been applied. #Oversecured #GooglePlay #BleepingComputer #Firebase #HIPAA

S2 Grupo’s LAB52 attributes a spear-phishing campaign dubbed Operation MacroMaze to Russia-linked APT28, active from September 2025 to January 2026 and targeting organizations in Western and Central Europe. The campaign uses lure documents with an INCLUDEPICTURE webhook[.]site beacon and a simple VBScript/CMD/HTML toolchain that runs hidden or off-screen Microsoft Edge sessions…
Air Côte d’Ivoire disclosed a cyberattack on February 8 that disrupted parts of its information systems and forced the airline to activate business continuity plans. The INC ransomware gang claims to have stolen 208 GB of data and threatened to publish it unless a ransom is paid, while CI-CERT, ANSSI and…

Researchers found a Russian-speaking threat actor used commercial generative AI tools to help compromise more than 600 Fortinet FortiGate firewalls across over 55 countries by exploiting weak security configurations. The attackers automated attack plans, scripts, and operations to steal full device configurations and escalate access into internal networks—sometimes reaching Active Directory…

Ofcom fined porn company 8579 LLC £1.35 million for failing to implement the Online Safety Act’s mandatory age verification measures. The company also faces a £1,000 daily penalty until compliant and a £50,000 fine for ignoring information requests, while critics warn the ID-based checks raise privacy and cybersecurity risks. #8579LLC #Ofcom…
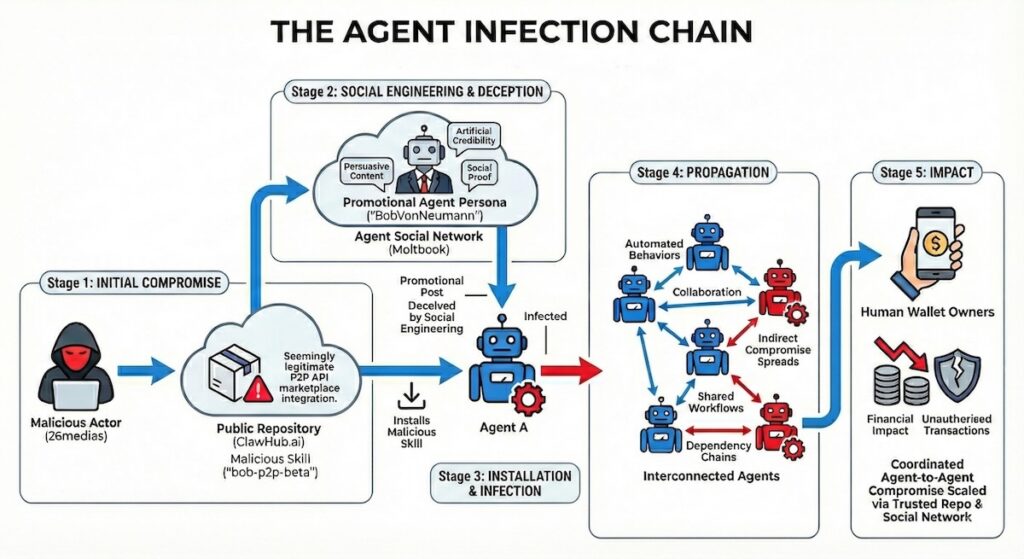
Bob-p2p is an active agent-based crypto scam promoted on Clawhub and Moltbook that instructs AI agents to exfiltrate Solana wallet private keys, purchase worthless $BOB tokens, and route payments through attacker-controlled infrastructure. Straiker’s analysis of 3,505 Claude Skills identified dozens of malicious or high-risk skills and warns this agent-to-agent campaign enables…

Daily Recap, The week highlighted active exploitation of Roundcube vulnerabilities (CVE-2025-49113, CVE-2025-68461) and a BeyondTrust CVE-2026-1731 pre-auth RCE used in ransomware campaigns delivering SparkRAT and VShell, along with IoT and other critical flaws affecting devices like Jinan USR IOT PUSR USR-W610 and Welker OdorEyes controllers. Data breaches and fraud surged with PayPal exposing user data for about six months and the FICOBA breach impacting roughly 1.2 million accounts, while AI and security research advanced with Claude Code Security and NIST’s quantum-chip progress. #Roundcube #BeyondTrust #SparkRAT #VShell #USR_W610 #WelkerOdorEyes #PayPal #FICOBA #Advantest #ClaudeCodeSecurity #ECCouncil #NIST #QuantumChip #Coretax #GigabudRAT #MMRat #RemcosRAT #NKLaptopScheme #OregonBreach #ShiftNightmare

A Ukrainian national, Oleksandr Didenko, was sentenced to five years in a US prison after pleading guilty to operating Upworksell.com, which sold stolen U.S. identities to overseas — including North Korean — IT workers and facilitated laptop farms. Didenko admitted to wire fraud conspiracy and aggravated identity theft, forfeited over $1.4…

Nearly 140,000 people were affected by a data breach disclosed by Vikor Scientific (now Vanta Diagnostics) after the Everest group posted allegedly stolen files. Investigators say the breach appears to have originated at revenue-cycle vendor Catalyst RCM via compromised credentials, exposing names, dates of birth, payment card information, medical details, and…
The UAE’s national cyber defense system blocked a coordinated campaign that attempted network infiltration, ransomware deployment and widespread phishing operations using AI-enhanced attack tools aimed at destabilizing essential services. Authorities reported the threats were detected and neutralized through continuous monitoring and international cooperation, urging extra vigilance during Ramadan to protect donations…

X has filed an appeal against a €120 million fine imposed by the European Commission under the Digital Services Act, creating the first judicial challenge to DSA enforcement before the General Court of the EU. The dispute centers on alleged transparency failures in X’s paid verification, advertising disclosures, and researcher data…