Peter Williams, former head of Trenchant at defense contractor L3Harris, was sentenced to 87 months in federal prison for stealing and selling at least eight zero-day exploit components to a Russian broker known as Operation Zero. The theft caused $35 million in losses, risked access to millions of devices, led to forfeiture of $1.3 million and other assets, and prompted U.S. sanctions against Operation Zero. #PeterWilliams #L3Harris #OperationZero #Trenchant
Category: Cyber Security News
The U.S. Treasury sanctioned Matrix LLC (Operation Zero), its owner Sergey Zelenyuk, and associated entities for buying stolen zero-day exploits sold by a former L3Harris cyber unit executive. The designations, the first under the Protecting American Intellectual Property Act (PAIPA), coincide with the sentencing of Peter Williams for stealing and selling eight Trenchant exploits to Operation Zero. #OperationZero #L3Harris
Zyxel released security updates for CVE-2025-13942, a critical UPnP command-injection flaw in multiple 4G/5G CPE, DSL/Ethernet CPE, fiber ONT, and wireless extender models that can allow unauthenticated remote OS command execution. Exploitation is constrained by the need for UPnP and WAN access to be enabled, but Zyxel also patched two high-severity post-authentication command-injection bugs and urged replacement of end-of-life routers as Shadowserver and CISA track widespread exposed devices and active exploitation. #CVE-2025-13942 #Zyxel
OpenClaw is an AI-powered automation framework with a plugin “skills” marketplace that creates a substantial supply-chain attack surface when user-installable modules run with broad system permissions. Flare’s analysis highlights confirmed issues such as CVE-2026-25253 and numerous poisoned skills enabling credential theft and remote code execution, while current underground discussion is driven more by research amplification and hype than by mass criminal operationalization. #OpenClaw #ClawHub

An Australian national, Peter Williams, was sentenced to 87 months in U.S. prison after stealing at least eight cyber exploits from his employer and selling them to the Russian broker Operation Zero. The theft caused $35 million in losses to the defense contractor L3Harris’s Trenchant division, impacted U.S. and allied government…
UFP Technologies disclosed a cybersecurity incident detected on February 14 that involved theft of files and disruption of IT systems, including billing and customer delivery label creation. The company says contingency plans and backups kept operations running while investigators work to determine what data was exfiltrated; the incident appears to involve…
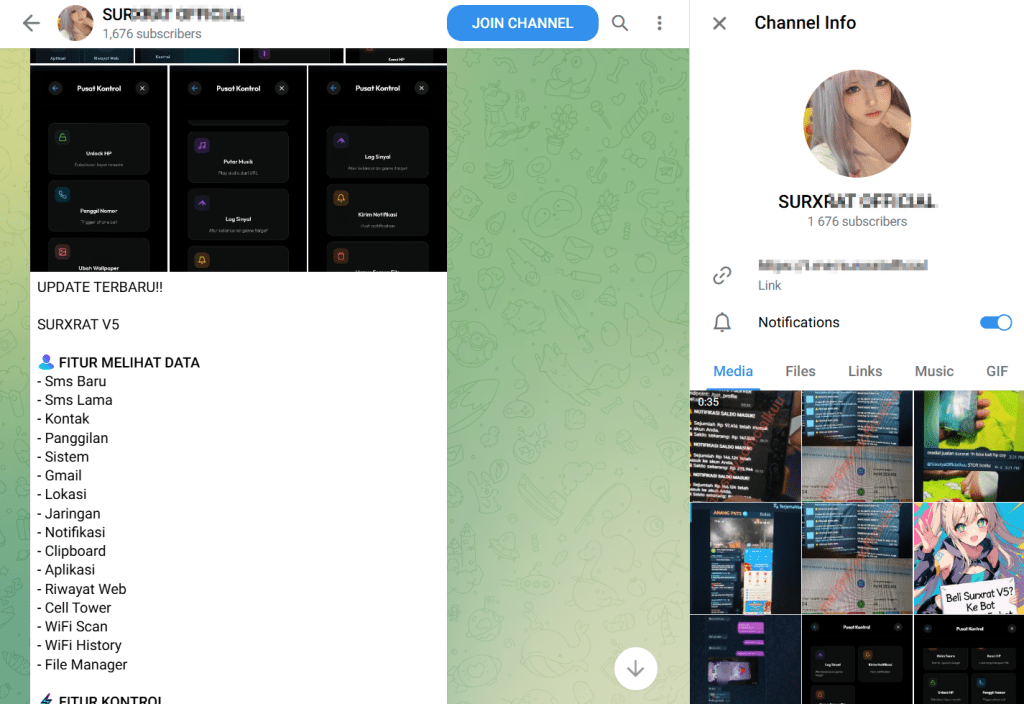
SURXRAT is an Android Remote Access Trojan sold as a commercial MaaS on Telegram with reseller and partner licensing that centralizes infrastructure while enabling affiliates to generate and distribute customized builds. Code links to ArsinkRAT and more than 180 identified samples show rapid evolution, and unusual features—like the conditional download of…
The United States has imposed sanctions on a Russia-linked cyber exploit brokerage called Operation Zero after investigators found it bought stolen zero-day exploits and tried to sell advanced cyber capabilities to foreign actors. The action targets individuals and entities tied to the network and signals a shift toward treating exploit marketplaces…
Marquis has sued SonicWall in the U.S. District Court for the Eastern District of Texas, alleging that a 2025 breach of SonicWall’s cloud backup service exposed firewall configuration backups and enabled a ransomware attack on Marquis’ network. The complaint says stolen emergency “scratch codes” and other configuration data allowed attackers to…

Daily Recap, CISA warns that two patched Roundcube Webmail flaws (CVE-2025-49113 and CVE-2025-68461) are actively exploited, prompting federal agencies to patch within three weeks and exposing tens of thousands of internet-facing instances tied to Winter Vivern (TA473) and APT28. Arkanix Stealer has emerged as a short-lived, AI-assisted info-stealer with modular Python and protected C++ builds that exfiltrated data from browsers, wallets, messengers, and games, while researchers published IoCs and a threat-research hub tracks a Weekly Recap for 22 Feb 2026. #WinterVivern #ArkanixStealer

The UK Information Commissioner’s Office has fined Reddit £14.47 million for collecting and using the personal information of children under 13 without adequate safeguards, finding that Reddit lacked a meaningful age-verification system until July 2025. The ICO said many underage accounts were processed without a lawful basis and exposed to potentially harmful content, criticized self-declaration age checks as insufficient, and the company intends to appeal; the penalty follows a similar fine for MediaLab over Imgur. #Reddit #ICO #MediaLab #Imgur
AI agents are now operators within enterprises, authenticating and acting like identities while often inheriting over-scoped privileges that create a major security blind spot for CISOs. The recommended approach is identity-first security combined with intent-based permissioning—assign unique, lifecycle-managed identities, document approved missions, and activate privileges only when identity, intent, and context align. #TokenSecurity #AIagents
Microsoft is expanding Purview data loss prevention controls so Microsoft 365 Copilot cannot process confidential Word, Excel, and PowerPoint documents regardless of where they are stored. The change will be deployed via the Augmentation Loop (AugLoop) between late March and late April 2026 and is being auto-enabled for organizations with DLP policies, following a Copilot Chat bug that briefly allowed summarization of confidential Sent Items and Drafts. #Microsoft365Copilot #MicrosoftPurviewDLP #AugLoop #CopilotChatBug
The ShinyHunters extortion group published a 6.1GB archive allegedly containing 12.4 million CarGurus records, exposing emails, IPs, full names, phone numbers, addresses, account IDs, and finance data. Have I Been Pwned added the dataset and noted about 3.7 million records are new, warning that the freely downloadable data could be used for phishing. #ShinyHunters #CarGurus

The U.K. Information Commissioner’s Office fined Reddit £14.47 million for failing to properly verify the ages of child users and for unlawfully processing personal data of users under 13. The ICO said Reddit relied on self-declaration, lacked a data protection impact assessment, and will continue enforcing the Age Appropriate Design Code…