Everyday third-party tools like PDF readers, office suites, email clients, browsers, and remote-access software form a large, often overlooked part of the enterprise attack surface. Because these tools are common and frequently out of date, vulnerabilities scale across organizations, and continuous third-party patching and visibility—offered by platforms like Action1—significantly reduce real-world risk. #Action1 #Outlook
Category: Cyber Security News

Daily Recap, Arkanix Stealer surfaced in October 2025 and disappeared by December 2025, packing infostealing capabilities and post-exploit tools like ChromElevator to harvest system, credentials, VPN, and crypto-wallet data. The rest of the recap covers a VMware Aria Operations patch for CVE-2026-22719, Copilot data controls via Purview DLP, a CarGurus breach claimed by ShinyHunters, Reddit’s ICO fine, FBI actions against Southeast Asia scam networks, and Tim Youngblood’s CISO‑in‑residence advisory work. #ArkanixStealer #ChromElevator #VMwareAriaOperations #CVE-2026-22719 #Microsoft365Copilot #PurviewDLP #AugLoop #CarGurus #ShinyHunters #Reddit #FBI #TimothyYoungblood
A coordinated campaign targets software developers by publishing malicious Bitbucket repositories disguised as legitimate Next.js projects and technical assessment materials, including coding tests. When developers clone and open these repos, embedded triggers (VS Code folderOpen tasks, npm dev assets, or backend startup code) execute JavaScript loaders that fetch in-memory backdoors enabling remote code execution, data exfiltration, and staged payload delivery. #Nextjs #Bitbucket
UFP Technologies disclosed a cybersecurity incident discovered on February 14 that compromised some IT systems, resulted in data theft, and caused destruction of certain company-related data. The company says the intruder has been removed, primary systems remain operational, and investigations continue to determine whether personal information was exfiltrated. #UFPTechnologies #BillingSystems
New York Attorney General Letitia James sued Valve Corporation, alleging its loot boxes on Steam amount to illegal gambling that has harmed children and fueled a multi‑billion‑dollar virtual‑item market. The complaint targets loot boxes in Counter‑Strike 2, Team Fortress 2, and Dota 2, seeks to ban the features in New York, recover profits, and highlights risks like account theft and youth gambling addiction. #Valve #Steam
Microsoft has expanded its first sign-in restore experience within Windows Backup for Organizations to let enterprise users restore personal settings and their Microsoft Store app lists when signing into a new or reimaged Windows 11 device. The update extends support beyond Microsoft Entra-joined devices to hybrid-managed environments, multi-user devices, and Windows 365 Cloud PCs and will be available with Windows updates released February 24, 2026 or later. #MicrosoftEntra #WindowsBackupForOrganizations
Ransomware victim payment rates dropped to an all-time low of 28% in 2025 despite a roughly 50% increase in claimed attacks and on-chain payments totaling about $820 million (likely to approach or exceed $900 million). The median ransom surged 368% to $59,556 as the ecosystem fragmented into 85 active extortion groups and high-impact breaches like Jaguar Land Rover and Marks & Spencer highlighted growing scale and sophistication. #Chainalysis #ScatteredSpider

Darktrace detected more than 32 million high-confidence phishing emails in 2025, revealing a sharp surge in automated, identity-driven attacks that increasingly bypass traditional defenses. Identity compromise—particularly Microsoft 365 and SaaS account takeovers—has overtaken vulnerability exploitation as the primary entry vector, highlighting the need for real-time identity-centric security. #Darktrace #Microsoft365…
Tel Aviv-based Gambit Security emerged from stealth with $61 million in combined seed and Series A funding to build an AI-powered resilience platform that maps organizations’ environments, security products, and backup tools to uncover gaps and validate recovery paths in real time. The company also reported a threat actor abusing Anthropic’s…
Check Point researchers found critical vulnerabilities in Anthropic’s Claude Code configuration files that could allow attackers to execute arbitrary commands on developers’ machines. Anthropic implemented patches and added warnings and confirmations after researchers showed that malicious repositories or manipulated settings could exfiltrate API keys and bypass user consent. #ClaudeCode #Anthropic…
Hazeldenes, a major Victoria-based poultry processor, is restoring operations after a cyberattack that disrupted production across its network. The company has begun a phased return to production while engaging external cybersecurity experts and working with authorities as the investigation continues. #Hazeldenes #BGHCapital…
Cisco Talos disclosed that a sophisticated threat actor exploited a critical authentication bypass in Cisco Catalyst SD-WAN for at least three years, allowing unauthenticated attackers to gain administrative privileges and add rogue peers to enterprise networks. The campaign, attributed to UAT-8616 and tracked as CVE-2026-20127, included a downgrade-exploit-restore escalation leveraging CVE-2022-20775…
Samsung SDS warns that cybersecurity threats in 2026 will be driven by AI-based attacks, evolving ransomware tactics, cloud misconfigurations, phishing and account takeovers, and data security weaknesses. Its report recommends enforcing least privilege for AI agents, deploying AI Guardrails and CNAPP monitoring, securing backups and incident response, and applying MFA and…
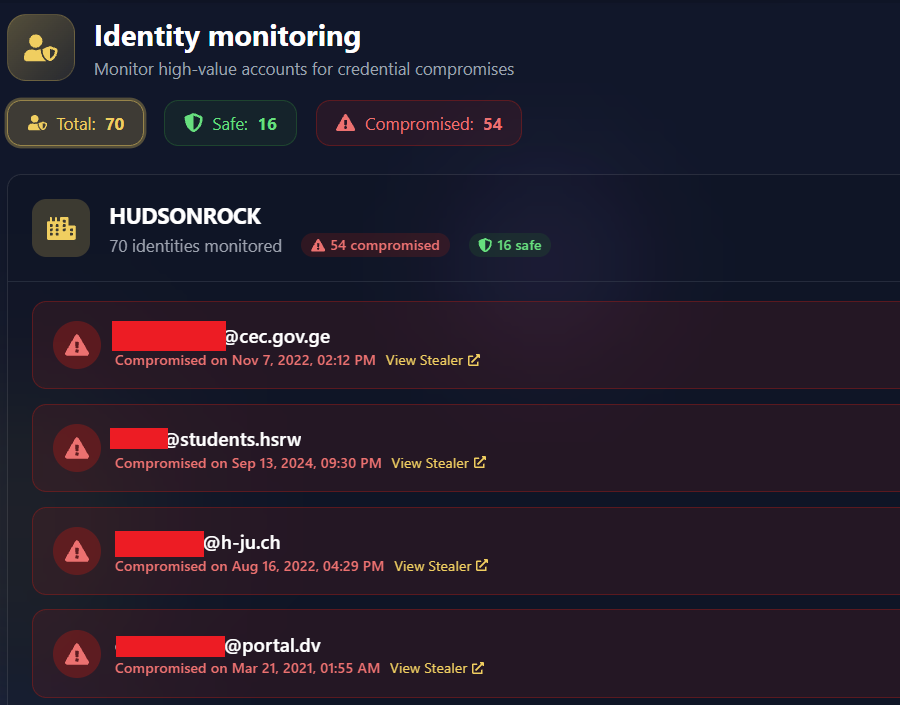
A large credential stuffing campaign targeted F5 BIG-IP devices using credentials harvested from Infostealer infections rather than from direct F5 breaches. Attackers bought or scraped Infostealer logs, then stuffed ADFS/STS SSO credentials against edge devices—often via compromised Fortinet appliances—to bypass MFA and gain network access. #Infostealer #F5_BIG_IP
Microsoft released KB5077241, an optional February 2026 preview update for Windows 11 that delivers 29 non‑security quality improvements including BitLocker reliability fixes, a built‑in network speed test, and native Sysmon functionality. The update also adds usability and management features such as Shift/middle‑click File Explorer instances, RSAT on Arm64, and automatic Quick Machine Recovery for certain Windows 11 Pro devices, and can be installed via Windows Update or the Microsoft Update Catalog. #KB5077241 #Sysmon