A flaw in the OpenClaw AI assistant’s local gateway allowed attackers to hijack agents by luring developers to malicious websites without installing extensions or requiring further user interaction. Because the WebSocket gateway bound to localhost exempted loopback from rate limiting and allowed cross-origin connections, browser JavaScript could brute-force passwords and gain…
Category: Cyber Security News

A vulnerability in Chrome’s Gemini Live side panel could have allowed malicious extensions to inject JavaScript, hijack the AI assistant, and spy on users or exfiltrate data. Palo Alto Networks reported CVE-2026-0628 and Google patched the issue in Chrome 143 to block extensions from abusing declarativeNetRequests access to the Gemini panel….
The University of Hawaii’s Cancer Center suffered a 2025 ransomware attack that encrypted and potentially exfiltrated historical research files, exposing Social Security numbers, driver’s license numbers, and voter registration data. The breach impacted research tied to the Multiethnic Cohort Study, prompted system shutdowns and engagement with the threat actors to obtain…
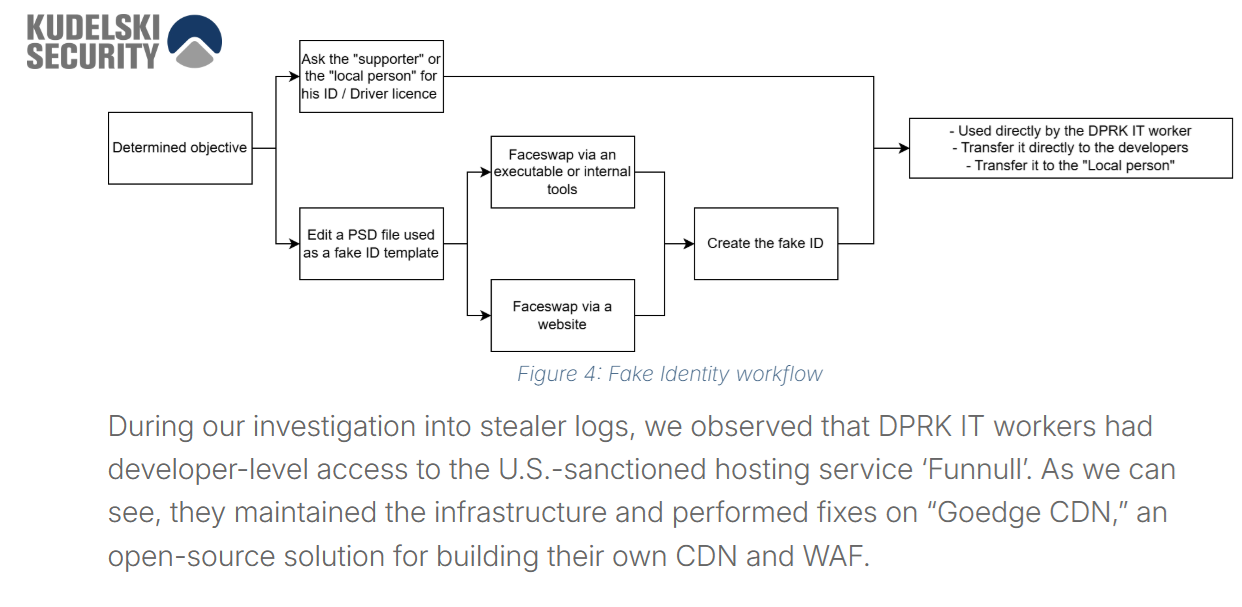
Researchers analyzing Hudson Rock cybercrime telemetry found a suspected DPRK IT worker’s machine infected with the LummaC2 infostealer, and its exfiltrated logs revealed an undocumented Indonesian proxy node tied to a broad “Vueyi” fraud operation. The case exposed synthetic identities, deepfake tooling, CDN infrastructure laundering via Funnull, large-scale crypto scams, and a catastrophic OPSEC failure when a local facilitator downloaded game hacks that delivered the infostealer. #LummaC2 #DPRK

Daily Recap, North Korea actors published 26 steganographic npm packages (StegaBin) that pull Vercel-hosted C2s from Pastebin to deploy credential stealers and a RAT, while APT37 expanded tooling with LNKs and implants (Restleaf, ThumbSBD, VirusTask, FootWine) to bridge air-gapped systems via USB and Zoho WorkDrive C2s. CISA warns RESURGE remains dormant on Ivanti Connect Secure devices (CVE-2025-0282) with ECC encryption, forged TLS certs, SSH tunnels and traffic fingerprinting for covert persistence — a malicious campaign delivers a RAT via trojanized gaming utilities (Xeno.exe, RobloxPlayerBeta.exe) connecting to C2 79.110.49.15 for data theft and follow-up payloads, and ClawJacked fixes tighten WebSocket checks to block localhost brute-force abuse. #StegaBin #APT37 #RESURGE #IvantiConnectSecure #CVE20250282 #XenoExe #RobloxPlayerBetaExe #ClawJacked #OpenClaw #VAL4K

Researchers disclosed a new iteration of the Contagious Interview campaign — tracked as StegaBin and attributed to the North Korean Famous Chollima cluster — that published 26 malicious npm packages masquerading as developer tools to deliver a developer-targeted credential stealer and remote access trojan. The packages use install.js to run a…

A recently patched high-severity MSHTML vulnerability (CVE-2026-21513) may have been exploited by the Russia-linked threat actor APT28, according to Akamai’s findings. The flaw allows crafted HTML or LNK files to bypass browser protections and invoke ShellExecuteExW to execute code outside the browser sandbox, with artifacts tied to the wellnesscaremed[.]com infrastructure. #APT28…

Most SaaS teams misread sudden traffic growth as organic success while bots inflate sign-ups, scrape APIs, and drive up server costs. SafeLine is a self‑hosted WAF and reverse proxy that uses semantic request analysis, anti‑bot challenges, rate limiting, and access controls to stop business‑logic attacks while keeping logs and control on…
Russia’s internet regulator Roskomnadzor and the Russian Defense Ministry experienced a large, brief multi-vector DDoS attack that disrupted access to their websites and related infrastructure, including the Main Radio Frequency Center (GRFC). Roskomnadzor said the attack originated from servers and botnets in Russia as well as the United States, China, the…

APT37 (aka ScarCruft/Ruby Sleet/Velvet Chollima) deployed five new tools in the Ruby Jumper campaign to compromise air-gapped systems using LNK-triggered PowerShell and a decoy Arabic document. The attack chain uses RestLeaf with Zoho WorkDrive for C2 to fetch shellcode that loads SnakeDropper, which installs a backdoored Ruby runtime and drops ThumbsBD…

Microsoft Defender researchers uncovered a campaign that tricks users into running trojanized gaming utilities (Xeno.exe and RobloxPlayerBeta.exe) distributed through browsers and chat platforms, leading to the deployment of a remote access trojan. A malicious downloader used a portable Java runtime, PowerShell and LOLBins like cmstp.exe to run a harmful JAR, evade…
A North Korea–linked group, APT37, has deployed a new “Ruby Jumper” campaign that uses malicious LNK files and a suite of implants to infect systems and bridge air-gapped networks via removable USB media. The operation leverages newly documented tools — including Restleaf, SnakeDropper, ThumbSBD, VirusTask and FootWine — with Restleaf using…
AWS has launched Security Hub Extended to unify its own tools like Inspector and GuardDuty with a curated set of third-party vendors under a single-pane mini-SOC. The service uses the Open Cybersecurity Schema Framework (OCSF) for pre-normalized findings, offers AWS as the seller of record with consolidated billing and flexible pricing,…
Nick Andersen has been appointed acting director of the United States’ Cybersecurity and Infrastructure Security Agency (CISA), replacing Madhu Gottumukkala who is leaving for a senior role at the Department of Homeland Security. Gottumukkala’s departure follows reports he failed a polygraph and uploaded sensitive government information to a public ChatGPT, and…
A Chilean national, Alex Rodrigo Valenzuela Monje (aka VAL4K), was extradited to the United States and arraigned on charges alleging he ran Telegram-based carding channels that sold tens of thousands of stolen payment cards. Court documents claim his channels MacacoCC Collective and Novato Carding distributed over 26,000 compromised cards containing account…