
A new analysis found 54 EDR killers abusing 34 vulnerable drivers via the bring your own vulnerable driver (BYOVD) technique to gain kernel privileges and disable endpoint protections before encryption. These tools are developed by closed ransomware groups, proof-of-concept forkers, and marketplace sellers and include examples such as DemoKiller, EDRSilencer, and…
Category: Cyber Security News

Speagle hijacks the functionality and infrastructure of the legitimate Cobra DocGuard document protection software to stealthily harvest and exfiltrate sensitive information from infected systems. The campaign, tracked as Runningcrab and linked to prior supply-chain abuses of Cobra DocGuard, uses compromised servers and legitimate client drivers for C2 and cleanup, suggesting deliberate…
A newly disclosed vulnerability called “PolyShell” affects all Magento Open Source and Adobe Commerce 2 installations, allowing unauthenticated attackers to upload polyglot files that can enable remote code execution or stored XSS leading to account takeover. Adobe’s fix is currently only available in the 2.4.9 second alpha while Sansec warns the exploit method is already circulating and urges immediate mitigations like restricting access to pub/media/custom_options and scanning for shells. #PolyShell #Magento
Navia Benefit Solutions notified nearly 2.7 million individuals that an unauthorized actor accessed its systems between December 22, 2025 and January 15, 2026, potentially exposing names, Social Security numbers, dates of birth, contact details, and benefits enrollment data (HRA, FSA, COBRA). The company launched an investigation, notified federal law enforcement, is offering 12 months of identity protection and credit monitoring through Kroll, and says no ransomware group has claimed the breach. #NaviaBenefitSolutions #HRA
Federal cybersecurity agencies urged organizations to harden Microsoft Intune deployments after an alleged Iran-linked cyberattack wiped more than 200,000 devices at medical device firm Stryker. CISA and the FBI advised using role-based access, multi-factor authentication, Microsoft Entra ID, and dual-admin approval policies while federal authorities disrupted the Handala group’s infrastructure. #Stryker…
Bitrefill says a March breach was likely carried out by North Korea-linked Bluenoroff (Lazarus/APT38), with investigators citing similar tactics, malware, reused IPs/emails, and on-chain tracing as indicators. Attackers used a compromised employee laptop and stolen legacy credentials to access production secrets, drain some hot wallets, and expose about 18,500 purchase records (including 1,000 names), while Bitrefill reports minimal losses and is strengthening security. #Bitrefill #Bluenoroff
Researchers have discovered a new Android trojan called Perseus that hides inside IPTV streaming apps to steal passwords, banking data, and spy on users’ personal notes. Perseus, active in Turkey and Italy, uses overlays, keylogging, and note-extraction—targeting apps like Google Keep and Evernote—and builds on leaked Cerberus code. #Perseus #Cerberus…
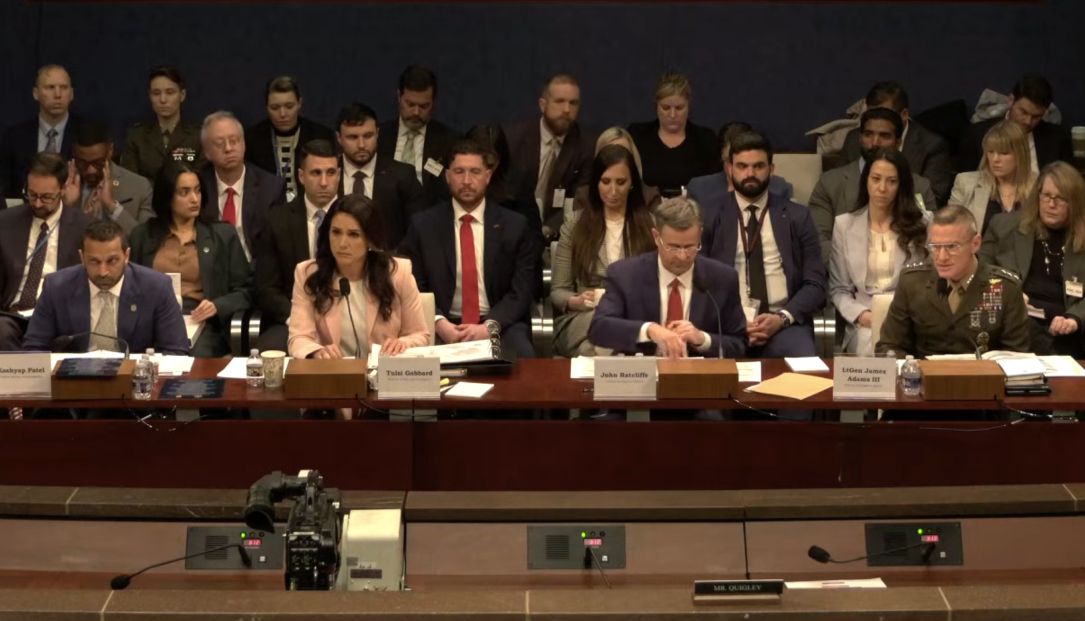
U.S. intelligence leaders publicly urged Congress to approve an 18-month “clean” extension of Section 702 of the Foreign Intelligence Surveillance Act, saying the authority is vital for actionable intelligence. Opponents including hardline Republicans, progressive Democrats, and civil liberties groups argue for added privacy safeguards and warn that AI-driven capabilities make unchecked…
ConnectWise has released a security update for ScreenConnect that encrypts machine keys to prevent server compromise. The patch addresses CVE-2026-3564, a critical vulnerability exposing ASP.NET machine key material used for session authentication, and users are urged to update to ScreenConnect 26.1 and tighten access controls. #ScreenConnect #ConnectWise #CVE-2026-3564 #ASP.NET…
Endpoint security startup 1stProtect emerged from stealth with $20 million in funding and has built an OS-level platform that enforces runtime policies to block malicious behavior without relying on cloud decision-making. The platform includes nearly two dozen protection modules and an on-device AI investigator for local forensic analysis and remediation, even…

Oasis Security raised $120 million in a Series B led by Craft Ventures, bringing its total funding to $195 million to accelerate its non-human identity and agentic access governance platform. The company will use the capital to deepen R&D, expand across AI agent frameworks, and scale go-to-market efforts while delivering just-in-time…
Password reset workflows are often less protected than primary logins, creating a clear attack surface that adversaries exploit to escalate privileges and move laterally. Strengthening resets with phishing-resistant MFA, device posture checks, strict password policies, auditing, least-privilege controls, and replacing knowledge-based checks can close these gaps without adding undue friction. #ActiveDirectory #SpecopsPasswordPolicy

State-sponsored APT28 actors exploited a high-severity Zimbra Collaboration Suite XSS flaw (CVE-2025-66376) to achieve remote code execution and compromise Ukrainian government email servers. CISA added the bug to its catalog of vulnerabilities exploited in the wild and ordered federal agencies to patch within two weeks after researchers linked Operation GhostMail to obfuscated JavaScript attacks that harvested credentials, tokens, backup 2FA codes, and mailbox data. #APT28 #CVE-2025-66376
The FBI has seized two websites used by the Iranian-linked Handala hacktivist group after a destructive attack on medical technology firm Stryker that wiped approximately 80,000 devices. The seizure notice states the domains were used to support malicious cyber activities tied to a foreign state actor, while Handala acknowledged the seizures and said it is rebuilding its infrastructure. #Handala #Stryker
Amazon Integrated Security researchers reported that the Interlock ransomware gang exploited a zero-day in Cisco Secure Firewall Management Center (CVE-2026-20131) as early as January 26, before the vulnerability was publicly disclosed. The report links Interlock to disruptive attacks on local governments, healthcare, and education, and details the gang’s use of custom…