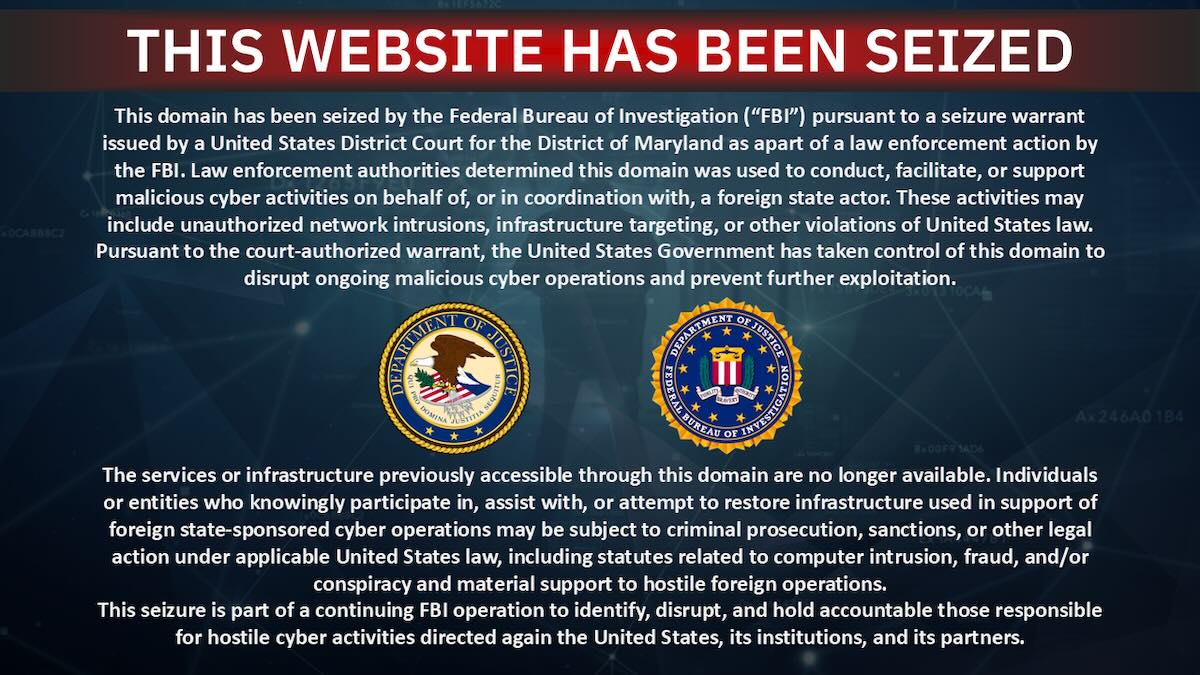
The United States has officially linked the Handala hacker group to Iran’s Ministry of Intelligence and Security (MOIS) and seized four domains used in the group’s psychological operations. Handala, widely viewed as a cover for the state-sponsored actor Void Manticore, has carried out destructive campaigns including wiping thousands of Stryker systems…
Category: Cyber Security News

Eclypsium raised $25 million in a strategic funding round led by PEAK6 Strategic Capital, bringing its total funding to $110 million. The Portland-based firm will use the investment to expand its device supply chain security platform to cover GPU-based AI servers and broader AI infrastructure after joining the NVIDIA Inception Program….
A cyberattack attributed to the Handala group has disrupted Stryker’s manufacturing, shipping, and order processing while CISA investigates and customer products remain unaffected. The roundup also highlights rising AI governance and legal risks, increased nation-state activity led by China, and intensifying cyber warfare in the Middle East. #Stryker #Handala…

Handala Hack Team went back online hours after the FBI announced the seizure of clearnet domains tied to Iran-linked operators accused of issuing threats and conducting “name and shame” campaigns. The group announced a new domain on Telegram while Stryker confirmed a contained attack on its Microsoft environment with restoration efforts…
Write 2 sentences summarizing the content. At the end, add hashtags for specific keywords mentioned in the article—such as names of malware, threat actors, or affected organizations/systems. Avoid general terms like #malware, #ransomware, or #cybersecurity. Use this format: #Keyword1 #Keyword2…
A mass defacement campaign has hit over 7,500 Magento sites, placing plaintext defacement files across more than 15,000 hostnames and briefly affecting major brands, government services, universities, and some Trump Organization domains. Netcraft links the incidents to an unauthenticated file-upload vulnerability in Magento/Adobe Commerce while Sansec disclosed a REST API flaw…

Navia Benefit Solutions has disclosed a data breach that likely exposed personal and health plan information for approximately 2,697,540 individuals after attackers accessed its systems from December 22, 2025 to January 15, 2026. The company discovered the incident on January 23, notified affected individuals, and is offering 12 months of free…
The U.S. Justice Department seized four domains tied to Iran’s Ministry of Intelligence and Security (MOIS), disrupting a state-backed campaign that combined cyberattacks, data leaks, and online intimidation. The operation used fake hacktivist fronts to publish stolen data and directly threaten journalists, dissidents, and individuals linked to Israel, signaling a shift…
CERT-In has reported a coordinated Android malware campaign targeting Indian users that uses fake eChallan and RTO Challan SMS alerts to trick victims into downloading malicious APKs. The multi-stage dropper installs hidden payloads that request sensitive permissions, can establish VPNs to intercept traffic, and lead to financial theft via fake RTO…
Microsoft says the March Windows 11 cumulative update KB5079473 causes Microsoft account sign-ins to fail across multiple apps, including Teams, OneDrive, Edge, Excel, Word, and Microsoft 365 Copilot. Microsoft is working on a fix, recommends restarting devices while connected to the internet as a temporary workaround, and has issued out‑of‑band updates and additional guidance for related Windows 11 issues. #Windows11 #KB5079473

U.S., German, and Canadian authorities dismantled command-and-control infrastructure used by the Aisuru, KimWolf, JackSkid, and Mossad botnets that had infected millions of IoT devices and launched hundreds of thousands of DDoS attacks. The takedown targeted virtual servers, domains, and other resources after record-setting assaults — including Aisuru’s 31.4 Tbps, 200 million RPS attack — to prevent further infections and attacks on victims such as the Department of Defense Information Network. #Aisuru #DoDIN
Michael Smith pleaded guilty to using AI-generated songs and automated bot accounts to fraudulently collect over $10 million in streaming royalties from platforms including Spotify, Apple Music, Amazon Music, and YouTube Music. He and co-conspirators used VPNs and thousands of bot accounts to generate billions of fake streams; Smith agreed to forfeit $8,091,843.64 and faces up to five years in prison. #MichaelSmith #Spotify
A North Carolina contractor, 27-year-old Cameron Curry, was found guilty of extorting Brightly Software (formerly SchoolDude) by stealing payroll and corporate data and threatening to leak employees’ PII unless paid $2.5 million. Brightly paid $7,540 in Bitcoin, reported the incident leading to an FBI search and Curry’s indictment, and the company had previously disclosed an unrelated April 2023 breach that affected nearly 3 million SchoolDude users. #BrightlySoftware #CameronCurry

Daily Recap, active exploits include Microsoft SharePoint deserialization RCE (CVE-2026-20963) being exploited in the wild against unpatched SharePoint Server 2016/2019/Subscription, and Interlock ransomware leveraging a Cisco Secure FMC zero-day (CVE-2026-20131) before patching. It also notes CISA directives to patch Zimbra XSS (CVE-2025-66376) and patches across WebKit (CVE-2026-20643) and UniFi (CVE-2026-22557), ongoing Marquis and Aura breaches, and policy moves involving China, DPRK, and Volt Typhoon. #SharePointFlaw #InterlockRansomware #CiscoFMC #ZimbraXSS #WebKitPatch #UniFiFlaw #TelnetdRCE #ScreenConnectPatch #MarquisBreach #AuraBreach #DarkSwordKit #PerseusMalware #Stryker #Handala #China #DPRK #VoltTyphoon

This week’s ThreatsDay Bulletin highlights a steady stream of low‑noise but high‑impact operations — from a nascent RaaS exploiting FortiGate devices to stealthy loaders, advanced evasion tricks, and refined phishing campaigns. Multiple attack chains show real‑world utility and growing background noise around supply‑chain, secrets sprawl, and mass exploitation trends. #TheGentlemen #FortiGate…