
A threat actor mounted a supply chain attack against the Strapi ecosystem by publishing 36 malicious NPM packages that deliver payloads enabling Redis code execution, Docker container escape, credential harvesting, reverse shells, and persistent implants. SafeDep reports the campaign specifically targets Guardarian and Strapi configurations and advises affected users to remove…
Category: Cyber Security News
Google DeepMind researchers show that malicious web content can manipulate autonomous AI agents by embedding “AI Agent Traps” that inject harmful context and trigger unexpected behavior. They categorize six attack classes—content injection, semantic manipulation, cognitive state, behavioral control, systemic, and human-in-the-loop—and propose defenses including model hardening, runtime protections, content governance, and…
Write 2 sentences summarizing the content. At the end, add hashtags for specific keywords mentioned in the article—such as names of malware, threat actors, or affected organizations/systems. Avoid general terms like #malware, #ransomware, or #cybersecurity. Use this format: #Keyword1 #Keyword2
CISA ordered federal agencies to secure FortiClient Enterprise Management Server (EMS) instances by April 9 after Defused disclosed CVE-2026-35616, a pre-authentication API access bypass being actively exploited. Fortinet released emergency hotfixes for affected EMS versions and urged customers to apply fixes or upgrade while Shadowserver reports nearly 2,000 EMS instances exposed online. #CVE-2026-35616 #FortiClientEMS
A cyberattack in northern Massachusetts temporarily disrupted the Patriot Regional Emergency Communications Center, compromising town and public safety computer systems and taking non-emergency and business phone lines offline while 9-1-1 service remains operational. Officials are working with IT vendors to restore systems, using CodeRED notifications and mutual aid to maintain emergency…

This is not an April Fools joke: a $285 million exploit on April 1 drained over half of Drift Protocol’s roughly $550 million in total value locked on Solana by abusing durable nonces and a fake CarbonVote Token to seize multisig administrative control and rapidly empty vaults. Investigators attribute the six‑month,…
Phishing emails now initiate more than 75% of cyberattacks, with attackers sending an estimated 3.4 billion phishing messages globally each day to steal credentials, distribute malware, and harvest personal data. The UAE Cyber Security Council warns users to verify messages, enable multi-factor authentication, apply updates, and report suspicious emails promptly to…

Germany’s Federal Criminal Police Office (BKA) identified the REvil affiliate known as “UNKN” as 31-year-old Daniil Maksimovich Shchukin and added alleged developer Anatoly Sergeevitsch Kravchuk to its wanted list, linking them to a string of high-impact ransomware attacks. The BKA said the suspects are tied to 130 attacks in Germany causing…

The FCC has proposed a $4.5 million fine against Voxbeam after finding the company routed tens of thousands of robocalls from an unregistered Czech provider into U.S. networks, many impersonating bank fraud and customer service numbers. Investigators found the calls came from a dormant account reactivated since 2018 and say Voxbeam…

The Education Authority’s C2K network was hit by a cyberattack that left thousands of pupils and staff across Northern Ireland unable to access coursework, communication tools, and exam resources. Recovery is underway with phased restorations and a compulsory full password reset while investigators and authorities assess whether personal data was compromised….
The European Commission cloud breach began when a compromised Trivy update and a single AWS credential allowed an attacker to access cloud resources and move laterally without triggering obvious outages. Approximately 91.7 GB of compressed data was exfiltrated and published by ShinyHunters, affecting dozens of europa.eu clients and prompting rapid remediation…

Cybersecurity Threat Research ‘Weekly’ Recap. The weekly roundup highlights supply-chain compromises (Mar 2026), Yurei operator toolkit exposure, multi‑stage TeamPCP attacks, RAT ecosystems such as CrystalX/NetSupport/Resoker/Xloader, DPRK modular malware with TA416 and Kimsuky campaigns, BRICKSTORM in virtualization, EvilTokens phishing, Tycoon 2FA infrastructure, and AI‑platform leaks (Claude Code, ChatGPT/Codex), along with detection and defense updates from Elastic, Microsoft and Validin. #TeamPCP #Yurei #CrystalX #NetSupport #Resoker #Xloader #TA416 #Kimsuky #DPRK #BRICKSTORM #EvilTokens #CocaCola #Ferrari #Tycoon #ClaudeCode #ChatGPT #Codex #BPFDoor #MythicLikho
Fortinet released an emergency hotfix for a critical pre-authentication access control vulnerability in FortiClient Enterprise Management Server (EMS), tracked as CVE-2026-35616, which is being actively exploited in the wild. Customers running FortiClient EMS 7.4.5 and 7.4.6 are urged to install the provided hotfixes or upgrade to 7.4.7 to mitigate the risk, after Defused reported the zero-day and Shadowserver identified over 2,000 exposed instances. #FortiClientEMS #CVE-2026-35616
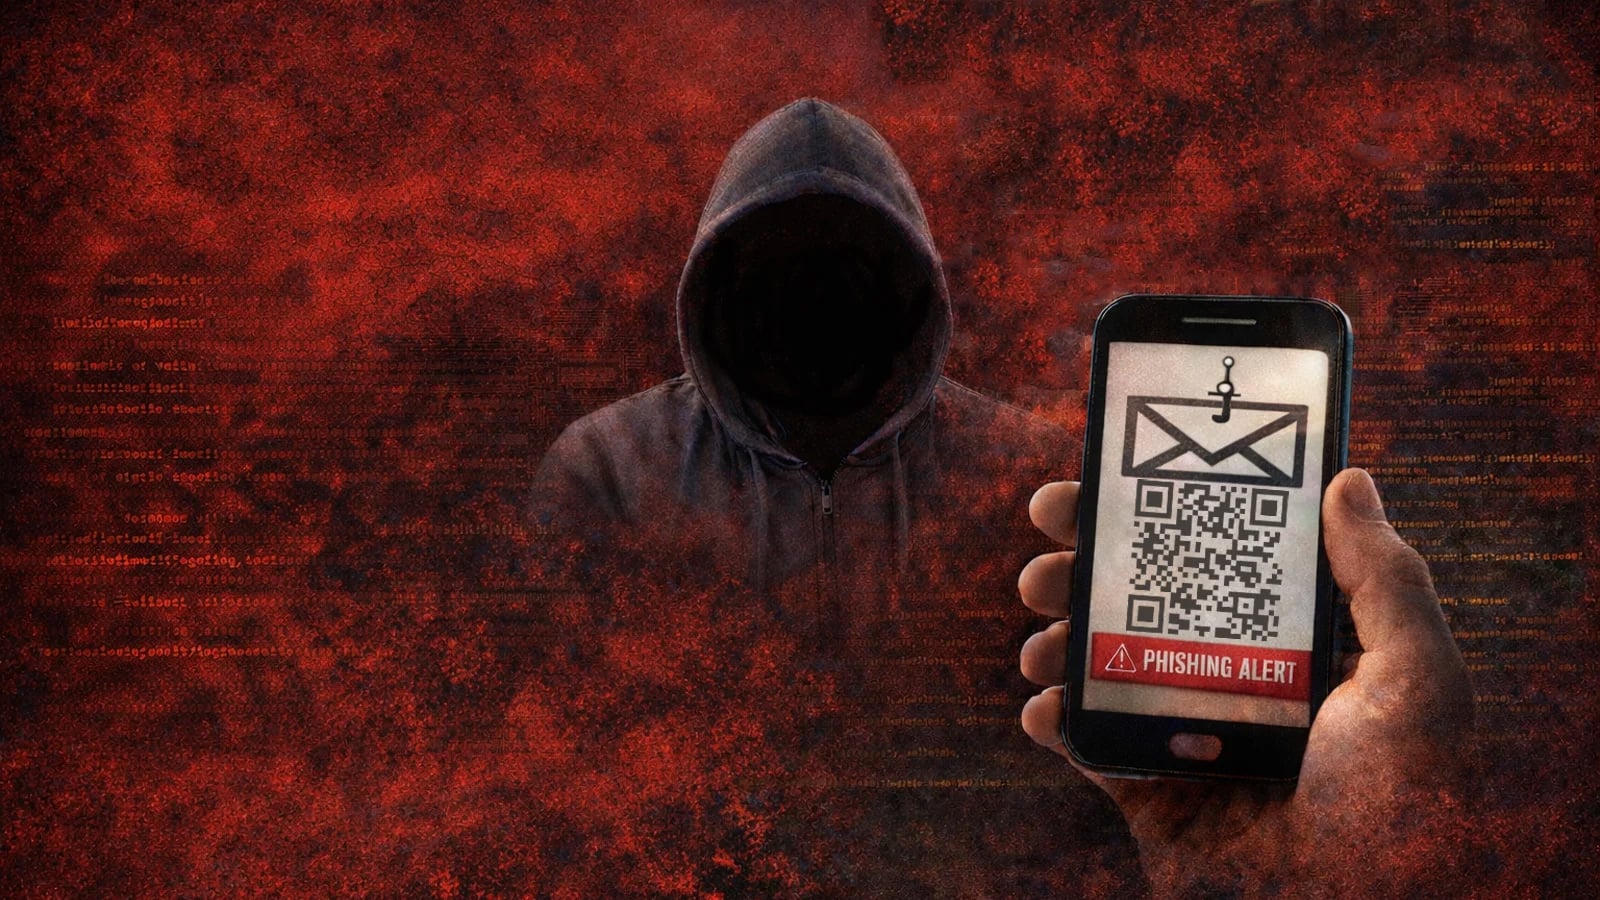
Scammers are sending fake “Notice of Default” texts impersonating state courts that include an image with a QR code leading to a phishing site demanding a $6.99 payment while harvesting personal and financial information. The campaign targets residents across multiple states and uses intermediary sites and CAPTCHAs to evade detection; state agencies say they do not request payments or personal data via text. #NewYorkDMV #CriminalCourtNY

Drift says the April 1, 2026 theft of $285 million was the culmination of a months-long, targeted social engineering operation by DPRK-linked actors who built trust through in-person meetings, Telegram groups, and a fake trading firm. The campaign deployed supply-chain tactics (a malicious VS Code project and a fraudulent TestFlight wallet),…