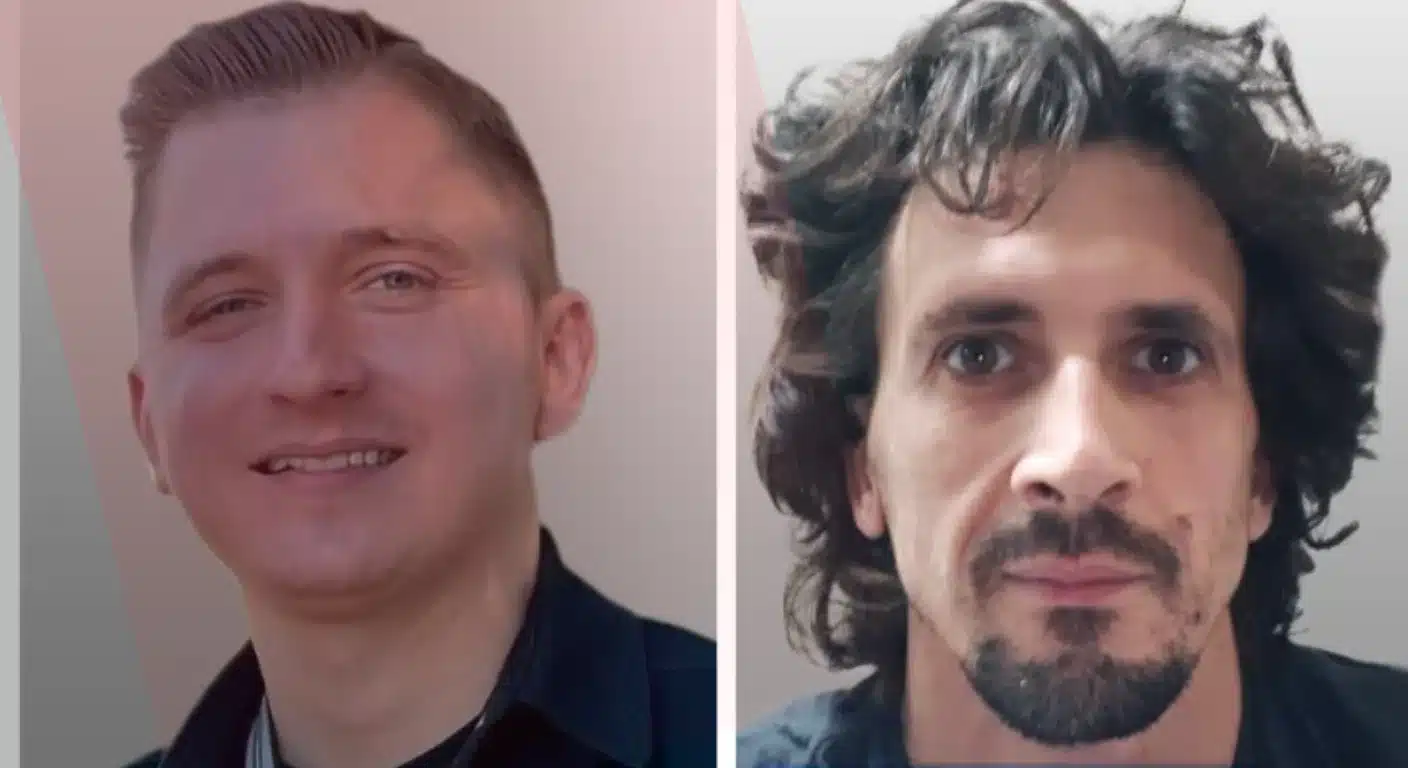
German authorities have linked 31-year-old Daniil Maksimovich Shchukin to the aliases “UNKN”/”UNKNOWN” and identified him as a leader of the GandCrab and REvil operations tied to at least 130 attacks in Germany between 2019 and 2021. The case highlights how GandCrab’s affiliate model evolved into REvil’s industrialized “big-game hunting” and double-extortion…
Category: Cyber Security News
A surge in Child Sexual Abuse Material (CSAM) across online platforms has alarmed EU authorities and child protection groups as digital communication expands. The expiry on April 3, 2026 of a temporary ePrivacy derogation that allowed providers to scan private messages has left hash-matching detection used by firms such as Google,…
Microsoft has deprecated and removed the Support and Recovery Assistant (SaRA) command-line utility from all in-support Windows updates as of March 10 and urges IT admins to migrate to the Get Help command-line tool (GetHelpCmd.exe). Get Help offers similar scriptable diagnostics with enhanced security for troubleshooting Microsoft 365 apps like Outlook and Teams, while Microsoft continues to retire other apps and features such as Microsoft Authenticator autofill, Publisher, and Microsoft Lens. #SaRA #GetHelp #Microsoft365 #Outlook #MicrosoftAuthenticator #MicrosoftPublisher #MicrosoftLens

Threat actors likely linked to the DPRK used obfuscated Windows LNK files delivered via phishing to drop decoy PDFs and PowerShell scripts, initiating multi-stage attacks against South Korean organizations. The PowerShell payload performs anti-analysis checks, establishes persistence via scheduled tasks, exfiltrates host profiles to a GitHub repository (motoralis) using a hard-coded…

An Iran‑nexus threat actor is suspected of running a three‑wave password‑spraying campaign in March 2026 against Microsoft 365 cloud environments in Israel and the U.A.E., impacting more than 300 organizations in Israel and over 25 in the U.A.E., with limited targeting observed in Europe, the U.S., the U.K., and Saudi Arabia….
The European Union law permitting tech companies to scan private communications for child sexual abuse material (CSAM) expired, yet major firms have vowed to continue scanning despite legal uncertainty. European officials say the scans now lack a legal basis while companies and child-safety groups argue stopping scans will weaken protections and…
Write 2 sentences summarizing the content. At the end, add hashtags for specific keywords mentioned in the article—such as names of malware, threat actors, or affected organizations/systems. Avoid general terms like #malware, #ransomware, or #cybersecurity. Use this format: #Keyword1 #Keyword2…
Cyber-enabled fraud dominated IC3 reports in 2025, accounting for 85% of reported losses and $17.6 billion stolen, with investment fraud, BEC, and tech support scams among the largest contributors. The FBI also warned of a growing ransomware ecosystem—63 new variants identified and investigations into over 200 variants—while AI-enabled scams and cryptocurrency-facilitated…
Germany’s Federal Police (BKA) have identified Daniil Maksimovich Shchukin and Anatoly Sergeevitsch Kravchuk as the leaders of the GandCrab and REvil ransomware operations from early 2019 until at least July 2021. BKA says the pair were linked to at least 130 extortion cases in Germany that caused over $40 million in damage and at least $2.2 million in ransom payments, and authorities have released images and details to help locate them. #GandCrab #REvil
GPUBreach is a new Rowhammer-based attack that induces bit flips in GPU GDDR6 memory to corrupt GPU page tables and grant an unprivileged CUDA kernel arbitrary GPU memory read/write. The University of Toronto team demonstrated that this capability can be chained via memory-safety bugs in the NVIDIA driver into CPU-side privilege escalation and full system compromise even with IOMMU enabled; full details will be presented at IEEE S&P on April 13. #GPUBreach #NVIDIA
Microsoft has implemented a server-side fix for an issue that prevented some Classic Outlook users from sending emails via Outlook.com and generated NDRs with error code 0x80070005-0x0004dc-0x000524. Affected users are advised to use the New Outlook or Outlook.com on the web or apply temporary workarounds while Microsoft continues investigating related Classic Outlook and Exchange Online issues. #ClassicOutlook #Outlookcom
Exploit code was released for an unpatched Windows local privilege escalation flaw dubbed BlueHammer that can grant SYSTEM or elevated administrator permissions. The proof-of-concept was published by a researcher using the aliases Chaotic Eclipse and Nightmare-Eclipse after a disclosure dispute with Microsoft, and researchers confirm it can access the SAM database and enable full system compromise despite bugs and no official patch. #BlueHammer #ChaoticEclipse

Bryan Fleming, founder of pcTattletale, pleaded guilty to manufacturing and distributing devices that intercept communications and was sentenced to a $5,000 fine with no additional prison time beyond one day already served. His conviction, stemming from a long Homeland Security Investigations probe into more than 100 stalkerware companies, highlights pcTattletale’s brazen…
Check Point Research tracked an Iran-linked, three-stage password-spraying campaign against Microsoft 365 tenants that peaked on March 3, 13, and 23, 2026 and primarily targeted municipalities in Israel and the UAE. Attackers scanned via rotating Tor exit nodes, used Windscribe and NordVPN endpoints geolocated in Israel to bypass geo-fencing, and leveraged…

North Korean threat actor UNC1069 ran a targeted social engineering campaign against multiple high-profile Node.js maintainers that resulted in two malicious package versions being briefly published to the NPM registry and likely installed by millions. Attackers used staged Slack and Teams meetings, built convincing infrastructure, and delivered a RAT via a…