The U.S. Defense Department is developing a new cyber strategy to align with the Trump administration’s National Cyber Strategy and to more aggressively counter digital adversaries. The plan, led by Katie Sutton, prioritizes integrating cyber across all warfare domains, gaining strategic advantage below the level of armed conflict, and reorganizing forces through initiatives like Cyber Command 2.0 while leveraging private-sector innovation. #NationalCyberStrategy #CyberCommand2_0
Category: Cyber Security News

Britain is now handling about four nationally significant cyber incidents every week, with the majority traced back to hostile nation-states rather than criminal gangs. The government announced a £90 million package and a Cyber Resilience Pledge as it warns of sophisticated operations from China, Russia (including GRU router compromises) and Iran and the accelerating offensive potential of frontier AI like Anthropic’s Mythos Preview. #GRU #MythosPreview

China has likely reached parity with the United States in offensive cyber capabilities, and the Netherlands’ MIVD warns that only a limited proportion of Chinese operations against Dutch interests are detected and mitigated. The report links the rise to PLA cyber restructuring and names campaigns and tools such as Salt Typhoon, RedMike and COATHANGER that have targeted routers, ISPs and FortiGate devices. #SaltTyphoon #COATHANGER
Many security leaders still rely on static frameworks—audits, closed vulnerabilities, and compliance—that were designed for a more predictable threat landscape and no longer reflect real-time risk. CISOs must shift to runtime visibility, comprehensive identity inventory, least-privilege enforcement, AI-driven alert triage, and realistic incident rehearsals to close the widening gap between measured and actual risk. #Anthropic #ClaudeMythosPreview #Mythos #UpwindSecurity #RinkiSethi

The head of the U.K.’s National Cyber Security Centre warned that the most serious cyberattacks now come from hostile states such as Russia, Iran and China, and that British businesses must prepare to defend against attacks that could occur at scale. European incidents targeting power, water and industrial systems — alongside…
Mastodon, the decentralized social network, suffered a major distributed denial-of-service (DDoS) attack that disrupted its flagship server Mastodon.social. The attack began on April 20 and was largely mitigated the same day with full operations confirmed normal by April 21, occurring days after a similar disruption of Bluesky. #Mastodon #Bluesky…
Microsoft will roll out an Efficiency Mode for Microsoft Teams in May 2026 that optimizes performance on CPU- and memory-constrained Windows and Mac devices by dynamically adjusting video resolution and app behavior. The update is enabled by default on eligible devices and is accompanied by new messaging security tools for reporting suspicious external users and a Security Detection Report for admins. #MicrosoftTeams #EfficiencyMode
A new supply chain attack targeting the npm ecosystem has compromised multiple Namastex Labs packages to steal developer credentials and secrets while attempting to self-propagate. Researchers from Socket and StepSecurity observed credential theft, data exfiltration, and worm-like republishing behavior similar to TeamPCP’s CanisterWorm, impacting packages such as pgserve and allowing cross-ecosystem spread to PyPI. #NamastexLabs #npm #CanisterWorm #pgserve #PyPI
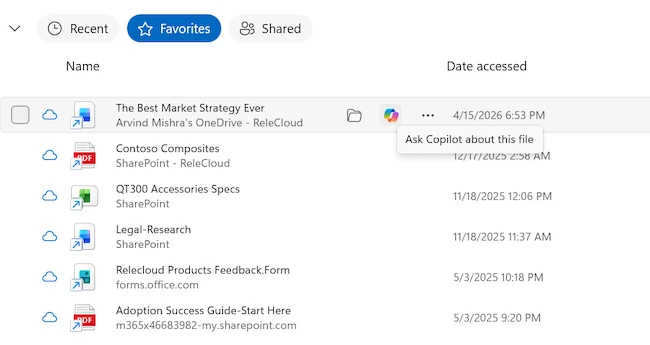
Microsoft’s OneDrive updates expand Copilot-driven intelligence to summarize files, generate new documents from stored content, and surface key insights via Ask Copilot in File Explorer and semantic search. The release also improves accessibility and governance with mobile OCR, Markdown support, OneDrive Sync public preview for up to 1 million items, file-level archiving, and enhanced sharing and admin controls. #OneDrive #Copilot
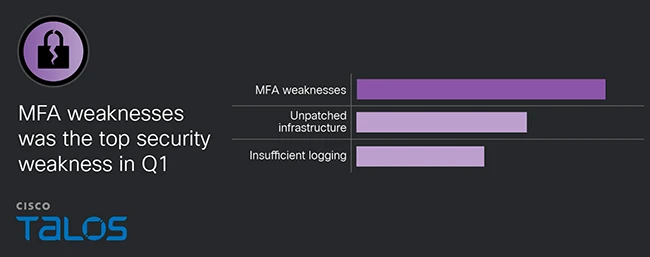
Phishing returned to the top initial-access method in Q1 2026, accounting for over a third of engagements where initial access could be determined, according to Cisco Talos. Talos also documented novel abuse of the AI web-builder Softr to host Exchange/OWA credential-harvesting pages, a decline in ToolShell SharePoint exploitation, the first Talos sighting of Crimson Collective using exposed GitHub tokens to access Azure via Microsoft Graph, and persistent MFA and logging gaps enabling attacks. #Softr #CrimsonCollective

Tencent has opened an international beta of QClaw, an AI agent app for Windows and MacOS available to 20,000 users in Canada, Japan, Singapore, South Korea, and the United States, with additional markets planned. Built on the open-source OpenClaw, QClaw integrates leading LLMs and messaging platforms like WhatsApp and Telegram, offers three pre-configured agent sets for daily and work tasks, processes data on-device, and uses a Claw Gateway security layer; it first launched as a public beta in Mainland China with over 80 feature iterations. #QClaw #OpenClaw #Tencent #ClawGateway #WhatsApp #Telegram
Over 1,300 Microsoft SharePoint servers exposed online remain unpatched for a zero-day spoofing vulnerability (CVE-2026-32201) that Microsoft fixed in April 2026 but continues to be exploited in active attacks. Shadowserver reports fewer than 200 systems have been patched, and CISA has added the flaw to its KEV catalog and ordered federal agencies to remediate under BOD 22-01. #CVE-2026-32201 #MicrosoftSharePoint #Shadowserver #CISA
Microsoft released out-of-band security updates to fix a critical privilege escalation bug in the ASP.NET Core Data Protection APIs that allowed forged authentication cookies to grant SYSTEM privileges. Customers are urged to update Microsoft.AspNetCore.DataProtection to 10.0.7, redeploy, and rotate DataProtection keys to invalidate any forged tokens #CVE-2026-40372 #ASPNetCore
Symantec researchers found a Linux variant of the GoGra backdoor that uses hardcoded Azure AD credentials and the Microsoft Graph API to stealthily pull commands from an Outlook mailbox. Developed by the state-linked Harvester group, the backdoor persists via systemd and an XDG autostart entry, decrypts AES-CBC/base64 commands from a “Zomato Pizza” folder (subject “Input”), executes them, returns AES-encrypted results (subject “Output”), and deletes the original command emails. #GoGra #Harvester
Microsoft has attributed an ongoing Universal Print sharing issue—causing intermittent “Sharing Print Failed” errors when creating printer shares—to a Microsoft Graph API code change that increased Entra ID directory replication latency and exposed a pre-existing race condition. The company has tagged the problem as incident UP1287359, is deploying a corrective code change, and provided a 13-step mitigation that avoids selecting organization-wide access and adds members manually until the fix is applied. #UniversalPrint #MicrosoftGraphAPI