
France Titres (ANTS) disclosed a data breach that may have exposed user login IDs, names, email addresses, dates of birth, and other personal information from its online portal. The agency has notified affected users, reported the incident to CNIL and the Paris public prosecutor, informed ANSSI, and implemented extra security measures while urging caution against phishing. #FranceTitres #ANTS
Category: Cyber Security News
Expel investigators, led by Marcus Hutchins, revealed a North Korean-linked campaign dubbed HexagonalRodent that stole up to $12 million from web developers by infecting personal devices and siphoning crypto from thousands of wallets. The group used malware strains such as BeaverTail, OtterCookie and InvisibleFerret, lured targets with fake LinkedIn job offers and generative-AI-created companies, and operated infrastructure to exfiltrate credentials and drain funds #HexagonalRodent #BeaverTail

Researchers warn malicious images were pushed to the official checkmarx/kics Docker Hub repository after attackers overwrote existing tags and added a fake v2.1.21 release. Analysis shows the poisoned KICS binary collected, encrypted, and exfiltrated scan reports, and related Checkmarx tooling (including some Visual Studio Code extensions) delivered remote-add-on malware via the…
A new Kyber ransomware operation has been observed targeting Windows systems and VMware ESXi endpoints, with Rapid7 analyzing two distinct variants deployed on the same network in March 2026. One variant targets VMware ESXi datastores, encrypts VM files and defaces management interfaces while using ChaCha8 and RSA-4096 despite ‘post-quantum’ claims, and the Windows Rust variant implements Kyber1024 for key encapsulation, disables recovery mechanisms, and includes an experimental Hyper-V shutdown feature; #Kyber #VMwareESXi
A Mirai-based botnet campaign is actively exploiting CVE-2025-29635 in D-Link DIR-823X routers to execute commands via a POST to /goform/set_prohibiting and enlist devices. Akamai SIRT observed the activity in March 2026 and found attackers download and run a multi-architecture Mirai variant called “tuxnokill,” while affected models reached end-of-life in November 2024, making vendor fixes unlikely. #CVE-2025-29635 #tuxnokill
Apple released out‑of‑band security updates for iPhone and iPad to fix a Notification Services flaw (CVE-2026-28950) that could allow notifications marked for deletion to remain stored on the device. The fixes—iOS 26.4.2, iPadOS 26.4.2, iOS 18.7.8 and iPadOS 18.7.8—use improved data redaction but Apple disclosed no technical details or whether the flaw was exploited, while reporting indicates retained notification data may have allowed recovery of Signal messages; users should install updates and consider changing Signal notification content to “Name Only” or “No Name or Content”. #CVE-2026-28950 #Signal
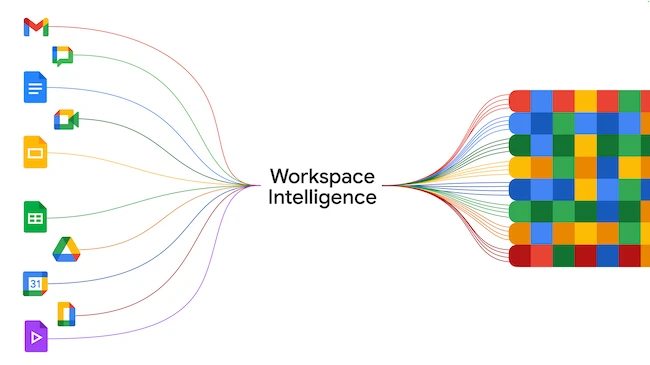
Google’s new Workspace Intelligence brings generative AI into Workspace apps, using content from Gmail, Drive, Calendar, Chat, Docs, and Slides to provide context-aware suggestions and task automation via features like Ask Gemini. Google says these capabilities run on Workspace’s secure, compliant infrastructure with per-user permissions, admin controls, DLP integration, regional data residency, and optional client-side encryption to ensure data governance and that customer data isn’t used to train external models or for advertising. #WorkspaceIntelligence #GoogleWorkspace
French authorities have arrested a 20-year-old suspected hacker known online as HexDex in connection with roughly 100 website breaches affecting public institutions, sports federations, and private organizations across France. Prosecutors say the suspect admitted to posting stolen data on forums like BreachForum and Darkforum and is linked to a major breach of the Ministry of National Education’s Compas system that exposed personal information of about 243,000 employees. #HexDex #Compas
Researchers found a previously unknown destructive wiper, dubbed Lotus Wiper, was deployed against Venezuela’s energy and utilities sector in an attack designed to destroy systems. The wiper erases data across physical drives and was compiled in September 2025, with indicators suggesting months of preparation and targeting of older Windows machines. #LotusWiper #PDVSA
The Supreme Court will hear Chatrie v. The United States to decide whether geofence warrants that collect bulk location data from companies with a single warrant violate the Fourth Amendment. The case could redefine privacy protections for remotely stored digital records like Google Location History and determine how courts apply the good-faith exception. #Chatrie #GeofenceWarrant
Fraudulent phone calls have evolved into a professionalized “Caller-as-a-Service” ecosystem that uses specialized roles, real-time supervision, and structured incentives to scale vishing attacks powered by stolen data. Flare monitors underground forums, Telegram channels, and marketplaces to surface leaked credentials and victim lists so organizations can proactively respond and reduce harm. #CallerAsAService #Flare
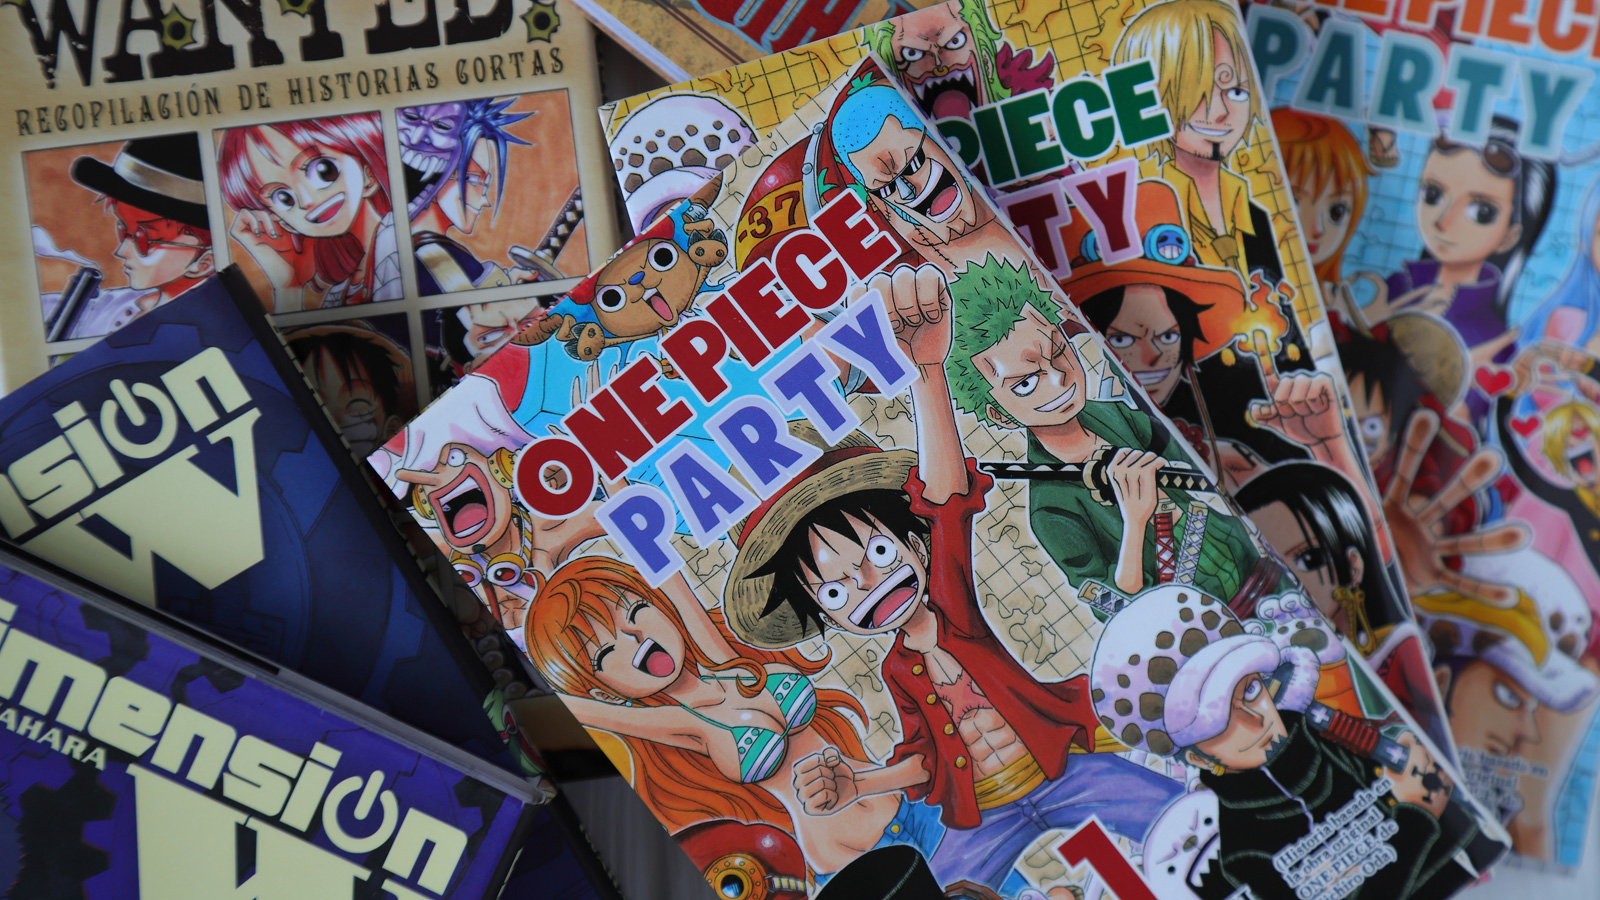
Spanish police dismantled what they say is the largest Spanish-language manga piracy platform, active since 2014 and serving millions of monthly users worldwide. Authorities seized hidden cold wallets holding over $470,000, made several arrests after a raid in Almería, and said the site—widely linked to Tu Manga Online—generated more than $4.7 million from aggressive pop-up advertising, much of it pornographic. #TuMangaOnline #PoliciaNacional

Harvester has deployed a new Linux variant of its GoGra backdoor that leverages the Microsoft Graph API and Outlook mailboxes as a covert C2 channel. Symantec and Carbon Black tied artifacts to India and Afghanistan and noted the implant polls an Outlook folder named “Zomato Pizza” for Base64-encoded commands before executing…

Researchers have flagged a supply-chain worm dubbed CanisterSprawl that uses compromised npm packages and stolen developer npm tokens to push poisoned releases and self-propagate via malicious postinstall hooks. The campaign exfiltrates extensive developer secrets to an HTTPS webhook and an ICP canister, includes PyPI propagation logic, and sits alongside other attacks…
Kaspersky warns that a new wiper, Lotus Wiper, was used in targeted attacks against the energy and utilities sector in Venezuela. The campaign relied on two batch scripts to disable defenses, trigger network-based execution, and deploy a wiper that overwrites drives and removes recovery mechanisms, with no extortion demands suggesting sabotage….