UNSW Sydney researchers found that AI models trained to sound drunk became easier to jailbreak and more likely to reveal private information shared in confidence. Their tests across GPT-3.5, GPT-4, Llama 2, Llama 3.1 and Mistral showed higher rates of privacy breaches and harmful request compliance after prompt-based drunkenness and fine-tuning on drunk text. #UNSWSydney #GPT4 #Llama2 #Llama31 #Mistral #ConfAIde #JailbreakBench
Category: Cyber Security News
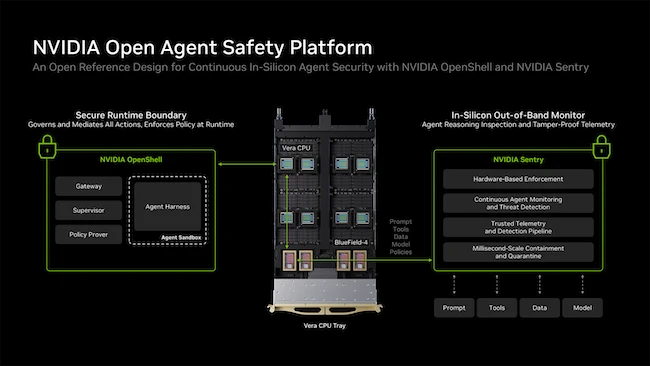
NVIDIA has launched the Open Agent Safety Platform to help organizations keep AI agents within approved boundaries using software controls and hardware-based monitoring. The platform combines OpenShell and Sentry to isolate agents, enforce access policies, and independently stop agents that try to exceed their permissions. #NVIDIA #OpenAgentSafetyPlatform #OpenShell #Sentry #BlueField4 #VeraRubinPOD
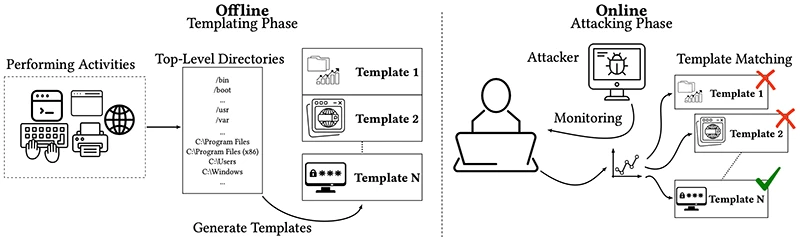
Researchers at Graz University of Technology showed that file-notification systems in Windows, Linux, macOS, and Android can leak sensitive user activity across accounts, including browsing history, keystroke timing, and device events. The paper also describes partial mitigations and reports that the attacks still work on default or lightly protected systems in several cases. #GrazUniversityofTechnology #Windows #Linux #macOS #Android #CVE-2025-68788 #CVE-2025-27738 #CVE-2025-21197
A New Mexico jury found Meta liable for deceiving users about Facebook privacy protections, citing more than 43 million violations of state consumer protection law. The case centers on the Cambridge Analytica data scandal, and the judge will later decide whether Meta must pay massive civil penalties. #Meta #Facebook #CambridgeAnalytica #MarkZuckerberg…
Mandiant and Google Threat Intelligence Group warned that ShinyHunters, tracked as UNC6240, has launched a new mass-exploitation campaign against Oracle PeopleSoft customers by modifying its exploit to bypass WAF rules. The group has deployed web shells, SideEye, Neo-reGeorg, and MeshCentral across multiple sectors while preparing for data theft extortion. #ShinyHunters #UNC6240…
The District of Columbia Department of Health Care Finance said nearly 400,000 Medicaid and DC Healthcare Alliance beneficiaries may have had personal information exposed through two website reports that contained hidden data. DHCF removed the reports, completed internal checks, and said it has no evidence the information was misused, though affected…
CISA has ordered U.S. federal agencies to secure vulnerable Citrix NetScaler systems after active exploitation of two critical flaws, CVE-2026-88771 and CVE-2026-88772. Citrix confirmed zero-day attacks, urged immediate patching, and warned organizations to check for compromise before updating. #Citrix #NetScaler #CVE-2026-88771 #CVE-2026-88772 #CISA #Shadowserver #CERT-EU
A former U.S. Army soldier, Cameron John Wagenius, was sentenced to 70 months in prison for hacking and extorting at least 10 U.S. technology and telecommunications companies, including AT&T and Verizon. His case was tied to stolen credentials, Telegram-based coordination, and broader data-theft schemes connected to the Snowflake attack campaign. #CameronJohnWagenius #AT&T #Verizon #Snowflake #BreachForums #XSSis
Bitget has resumed Bitcoin withdrawals after a suspected North Korean hacking group breached its systems and stole hundreds of millions of dollars from hot and warm wallets. The exchange said the vulnerability has been addressed, funds remain unaffected, and it will gradually restore withdrawals across other assets and networks while launching a Recovery Bounty Program. #Bitget #NorthKorea #GracyChen #Bybit #Elliptic
AI agents are pushing enterprises to redesign security governance so human accountability, privacy, and oversight are built into systems from the start. AWS’s Reimagine 2026 warns that weak approval workflows, shadow AI, and inconsistent controls can drive data leakage, unreliable outcomes, and uneven adoption across organizations. #AWS #Reimagine2026 #shadowAI
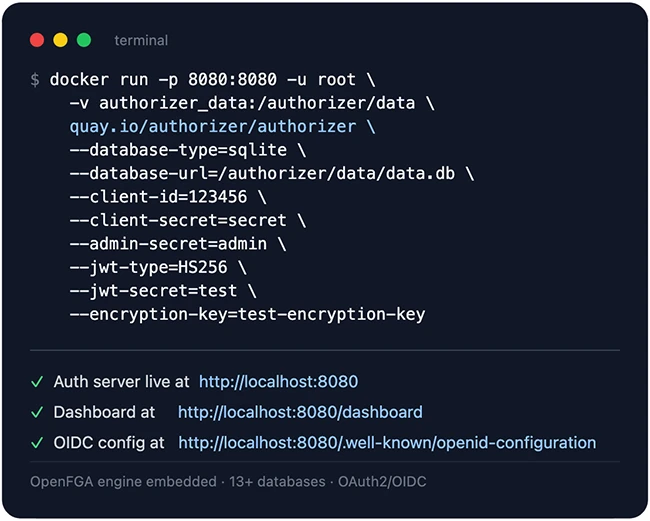
Authorizer is an open-source sign-in and access control server that adds AI-aware permission checks so assistants can verify whether a user may access a document before retrieval. It supports many login methods, multiple databases, and embeds OpenFGA plus a local MCP server to enforce fine-grained access control for teams using AI with company files. #Authorizer #OpenFGA #MCP
Chris Latimer of Vectorize warns that AI agent memory can quietly collect API keys, credentials, and sensitive documents in plain text across developer machines and cloud services. He also explains how poisoned memories can be introduced through plugins, skills, and MCP integrations, and says CISOs should audit agent memory now to uncover unvetted tools and exposed secrets. #Vectorize #ChrisLatimer #OWASP #MemoryGuard

Cybersecurity Threat Research ‘Weekly’ Recap. The report highlights frequent ransomware and identity-focused intrusion chains, including PAYLOAD’s abuse of Active Directory GPO/SYSVOL, Qilin’s continued cross-sector activity in ANZ, and multiple OAuth/session and phishing techniques such as TeamFiltration, CSuite, and token theft even in MFA-protected environments. It also covers software supply-chain and platform abuse (MemTensor, OpenCode, CI/CD hardening, and AWS IAM key protection), plus notable loader/infostealer malware (ShinyHunters/UNC6240, Kothamine, AvisLoader, Vidar, MacSync, SilentXMRMiner) and exploitation work like pfSense stored XSS to root RCE and MagicINFO leading to miner deployment.
#PAYLOAD #ActiveDirectory #Qilin #TeamFiltration #CSuite #OAuth #AppX #WWAHost #MemTensor #OpenCode #ShinyHunters #UNC6240 #Kothamine #AvisLoader #Vidar #MacSync #SilentXMRMiner #pfSense #MagicINFO #VolzTyphoon #SaltTyphoon #UNC6293 #UNC7005 #UNC5976
Cloudflare fixed a Containers and Sandboxes flaw that could let Workers Paid customers recover leftover data from other tenants’ containers on the same physical host. The issue affected reused storage blocks and could expose files, databases, Chromium profiles, and credential data, but Cloudflare found no evidence of real customer data exposure. #Cloudflare #WorkersPaid #Containers #Sandboxes
Citrix has confirmed that two critical NetScaler remote code execution flaws, CVE-2026-88771 and CVE-2026-88772, are being actively exploited as zero-days and has released security updates to address them. Organizations using affected NetScaler ADC and NetScaler Gateway appliances should patch immediately or reduce Internet exposure until upgrades can be completed. #Citrix #NetScaler #CVE-2026-88771 #CVE-2026-88772