Keio Corporation confirmed a ransomware attack on its servers that disrupted some business and hospitality systems, while train operations were not affected. Tokyo Metro also disclosed a separate cyber incident that exposed 59,000 member email addresses, and it is unclear whether the two events are connected. #KeioCorporation #TokyoMetro
Category: Cyber Security News

Apple has released security updates for older versions of iOS, iPadOS, and macOS to fix CVE-2026-86950, an out-of-bounds write in CoreGraphics that could enable arbitrary code execution. The company said the flaw may have been exploited in highly targeted attacks against specific individuals, and it was discovered and reported by Meta…

NVIDIA has launched the Open Agent Safety Platform to improve the security of AI agents through stronger sandboxes, monitoring, and hardware-backed policy enforcement. The platform has support from more than 100 organizations, including Anthropic, Microsoft, and JPMorgan Chase, as the industry pushes to make agentic AI safer in real-world environments. #NVIDIA #OpenAgentSafetyPlatform #Anthropic #Microsoft #JPMorganChase #Bluefield4 #OpenShell
Researchers found more than 16,000 misconfigured Supabase databases exposing readable tables with sensitive data such as PII, passwords, authentication tokens, and in some cases credit card information. UpGuard linked the exposure to weak configuration practices in AI-assisted app development and advised users to review Supabase security controls to reduce risk. #Supabase #UpGuard #AIcodingagents
Dutch police confirmed the arrest of a 24-year-old Amsterdam man in an investigation tied to the ShinyHunters hacking group, with authorities expected to provide more details at his court appearance in Rotterdam. The suspect, identified by reporters as Pepijn van der Stap, has previously been convicted of hacking and blackmail, while ShinyHunters denied any connection to him. #ShinyHunters #PepijnvanderStap #PolitieLandelijkeOpsporingenInterventies
Times Car has confirmed that a cyberattack exposed data belonging to about 6.6 million current and former members, including personal, driver’s license, and account information. The company says credit card data was not affected, no stolen data has been found online, and it is warning customers to watch for suspicious messages and fraud attempts. #TimesCar #Park24 #TimesMobility
Modulate has secured an additional $25 million to expand its audio-native AI platform, Velma, which detects emotion, intent, synthetic speech, and conversational behavior in real time. The company is using its proprietary Ensemble Listening Model to help organizations counter deepfake attacks, harassment, and other harmful voice misuse. #Modulate #Velma #FutureVentures #Hyperplane…
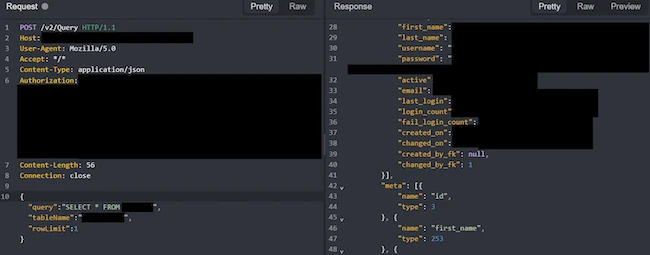
A 16-year-old researcher named Faav found that Microsoft’s Titan analytics service failed to verify login token signatures, allowing administrator access and SQL queries across 17 connected databases. The issue exposed employee records and Bing search analytics, and Microsoft later locked down the endpoint after coordinated disclosure. #Titan #Microsoft #Faav #MSRC #Antares #Entra #Bing

ShinyHunters claims responsibility for a breach of FBI job applicant portals and related systems, allegedly exposing personal, medical, and sensitive staff information. Google Cloud / Mandiant says the group is again exploiting Oracle PeopleSoft vulnerability CVE-2026-35273 by bypassing WAF rules and targeting organizations that failed to patch. #ShinyHunters #FBI #OraclePeopleSoft #CVE-2026-35273
ShinyHunters claims it stole sensitive FBI data that may expose agents’ personal contact details, family information, assignments, and specialties, raising serious safety and counterintelligence concerns. Researchers say the alleged extortion appears to be a personal retaliation against the FBI, with the stolen data already spreading beyond the group’s control. #ShinyHunters #FBI
SOCRadar’s AI Identity Exposure Report shows how infostealer logs are exposing employee logins to AI platforms, with ChatGPT dominating the findings across 482 major enterprises. The report explains why stolen AI sessions are more dangerous than stolen passwords and urges organizations to treat AI platforms as critical identity assets. #Anthropic #Claude #ChatGPT #HuggingFace #Replit #Zapier #Notion #ElevenLabs #SOCRadar
JadePuffer is a new AI-driven ransomware operator targeting Azure tenants with automated reconnaissance, credential theft, lateral movement, and destructive actions against cloud resources. Microsoft linked the activity to Storm-3168, which used compromised service principals to delete storage accounts, weaken recovery protections, and expand attacks to AI assets such as training data and vector databases. #JadePuffer #Storm3168 #Azure #EncForge #Microsoft

This week’s roundup highlights active exploitation of Citrix NetScaler flaws, a major Bitget breach, and multiple campaigns abusing weak identities, phishing kits, and old vulnerabilities. It also shows how forgotten placeholder domains, exposed service accounts, and leaked GitHub App keys continue to create real attack paths for threat actors. #Citrix #NetScaler…
Former US Army soldier Cameron John Wagenius was sentenced to 70 months in prison for hacking AT&T and Verizon systems, leaking a government official’s call detail records, and participating in extortion schemes. He and his accomplices used stolen credentials to target at least 10 organizations, including involvement in the broader Snowflake…
SecurityWeek has opened the Call for Presentations for its 2026 CISO Forum Virtual Summit, inviting original, vendor-neutral talks from cybersecurity leaders and practitioners. The event will focus on practical guidance across topics such as AI threats, ransomware, supply-chain risk, Zero Trust, incident response, and executive communication. #SecurityWeek #CISOForum #ZeroTrust #Ransomware #AI…