A 23-year-old Taiwanese university student was arrested after allegedly using software-defined radio and handheld radios to transmit a forged high-priority “General Alarm” on the TETRA network, stopping four Taiwan High Speed Rail (THSR) trains for 48 minutes. Authorities say the attacker decoded and reused long-standing TETRA parameters with help from an accomplice, bypassed multiple verification layers, and now faces charges under Article 184 while police seized SDR equipment and radios. #TETRA #THSR
Category: Cyber Security News
Attackers trojanized digitally signed DAEMON Tools installers (versions 12.5.0.2421–12.5.0.2434), embedding a first-stage info-stealer that establishes persistence and a backdoor on startup when executed. The supply-chain compromise infected thousands across more than 100 countries since April 8, while only about a dozen high-value targets—including organizations in Russia, Belarus, and Thailand—received second-stage payloads such as a lightweight backdoor and QUIC RAT. #DAEMONTools #QUICRAT
A hacker claiming to be the ShinyHunters extortion gang says they stole 280 million records tied to students and staff from 8,809 colleges, school districts, and online education platforms using Instructure’s Canvas export features. Instructure is investigating while universities issue statements, the attacker published institution-level record counts and BleepingComputer and others seek independent verification. #ShinyHunters #Instructure
A Latvian affiliate, Deniss Zolotarjovs, was sentenced to over eight years in U.S. prison after pleading guilty to money laundering and wire fraud for acting as a ransomware negotiator and extortion specialist for groups including Karakurt, Conti, and Akira. Prosecutors say he helped extort more than 53 companies, causing at least…
The Federal Trade Commission reached a proposed settlement with data broker Kochava and its subsidiary Collective Data Solutions that bars them from selling, sharing, or disclosing sensitive location data without consumers’ explicit consent. The FTC’s complaint alleged Kochava illegally sold precise geolocation (within 10 meters), yearly incomes, mobile device IDs and…

Cisco Talos attributes a China-nexus APT tracked as UAT-8302 to attacks on South American governments since late 2024 and southeastern European agencies in 2025, with post-exploitation marked by deployment of custom malware. The group uses tools such as the .NET backdoor NetDraft (NosyDoor), CloudSorcerer, VShell and SNOWRUST, and appears to share…

A federal judge sentenced Latvian national Deniss Zolotarjovs to 102 months in prison for his role pressuring victims and facilitating ransomware extortions tied to former Conti leaders between 2021 and 2023. The crew, operating under multiple names including Conti, Karakurt and Royal, extorted nearly $16 million in confirmed ransoms, leaked sensitive data—including pediatric health records—and caused extensive financial and personal harm to victims worldwide. #DenissZolotarjovs #Conti
CISA officials say AI automation has delivered the biggest gains in the agency’s security operations unit, enabling analysts to triage threats faster, perform real-time checks, and support tasks like data migration and customer response in its Technology Operations Center. Leaders caution that adoption faces hurdles from legacy workflows, spreadsheet reliance, unclear data structures, and the need for transparent AI governance as the agency explores generative and agentic AI. #CISA #TechnologyOperationsCenter

A supply chain attack has trojanized DAEMON Tools installers (versions 12.5.0.2421–12.5.0.2434) distributed from the official site and signed with legitimate developer certificates, activating an implant when DTHelper.exe, DiscSoftBusServiceLite.exe, or DTShellHlp.exe run. The implant contacts env-check.daemontools[.]cc to fetch commands that download and execute payloads including envchk.exe, a shellcode loader (cdg.exe/cdg.tmp), and a…

The Apache Software Foundation released security updates addressing multiple flaws in Apache HTTP Server, including a severe HTTP/2 double-free bug that can lead to denial-of-service and potential remote code execution. The issue, tracked as CVE-2026-23918 and affecting httpd 2.4.66, was reported by Bartlomiej Dmitruk and Stanislaw Strzalkowski and is fixed in…
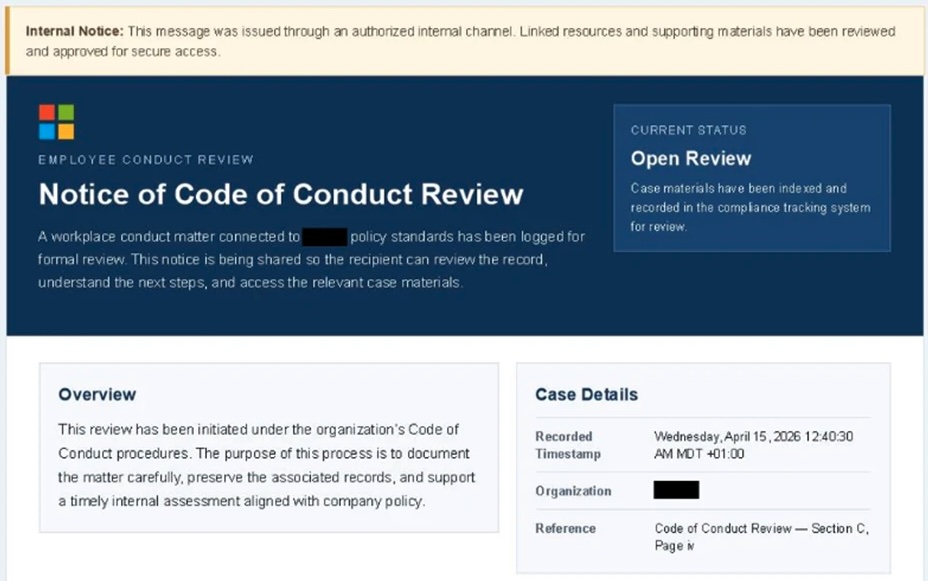
Microsoft warned that a sophisticated phishing campaign used a “code of conduct review” theme to lure victims to malicious sites, generating over 35,000 attempts targeting roughly 13,000 organizations between April 14–16. The attack used PDF attachments and Cloudflare CAPTCHAs to funnel victims into an adversary-in-the-middle (AitM) flow that captures authentication tokens…

Daily Recap, Copy Fail, a Linux kernel vulnerability (CVE-2026-31431), is now being actively exploited to gain root on major distributions, with a public PoC and a mandatory patch deadline of May 15, alongside MOVEit Automation CVE-2026-4670 that enables remote, unauthenticated access and a privilege-escalation fix (CVE-2026-5174) as more than 1,400 instances remain exposed. DigiCert revoked 60 certificates after a support-portal breach exposed EV code-signing certificates used by the Zhong Stealer family, Instructure confirmed a breach claimed by ShinyHunters, and broader themes include AI-driven security and data-center risk with Pentagon AI deals and MSP-focused defense of backups. #CopyFail #MOVEitAutomation #ZhongStealer #ShinyHunters #DigiCert #Instructure #MSPs #Pentagon
Google has restructured its Android and Chrome vulnerability reward programs to prioritize the highest-impact, hardest-to-achieve exploits while reducing payouts for flaws that AI has made easier to find. Top prizes include up to $1.5 million for zero-click Pixel Titan M2 full-chain exploits with persistence and up to $250,000 (plus a $250,128 MiraclePtr bonus) for full-chain Chrome process exploits. #PixelTitanM2 #MiraclePtr
ShinyHunters stole personal information for more than 119,200 people after abusing Anodot authentication to access Vimeo and later posted a 106GB archive when extortion attempts failed. Vimeo says no video content, valid user login credentials, or payment card data were exposed, and it disabled Anodot access, engaged third-party security experts, and notified law enforcement. #ShinyHunters #Vimeo
Write 2 sentences summarizing the content. At the end, add hashtags for specific keywords mentioned in the article—such as names of malware, threat actors, or affected organizations/systems. Avoid general terms like #malware, #ransomware, or #cybersecurity. Use this format: #Keyword1 #Keyword2