PCPJack is a new malware framework that steals credentials from exposed cloud systems while removing TeamPCP artifacts and access from compromised environments. It targets services and applications such as Docker, Kubernetes, Redis, MongoDB, RayML, and vulnerable web apps, and may be linked to a former TeamPCP affiliate. #PCPJack #TeamPCP #Trivy #LiteLMM #Telnyx #SAP
Category: Cyber Security News
TCLBanker is a new banking trojan that targets 59 banking, fintech, and cryptocurrency platforms using a trojanized MSI installer for Logitech AI Prompt Builder to infect systems. It also includes self-spreading worm modules for WhatsApp and Outlook, and Elastic Security Labs says it may represent a major evolution of the Maverick/Sorvepotel family. #TCLBanker #ElasticSecurityLabs #Maverick #Sorvepotel #Logitech
ShinyHunters has reportedly exploited a vulnerability in Instructure to deface Canvas login portals for about 330 schools and universities, using the takeover to threaten the release of stolen data. Instructure has taken Canvas offline while investigating the attack, which follows claims that 280 million student and staff records were stolen from its learning management system. #ShinyHunters #Instructure #Canvas #UniversityofTexasatSanAntonio
Autonomous offensive security firm XBOW announced a $35 million extension to its Series C, bringing total funding to more than $270 million after an earlier $120 million round that valued the company at over $1 billion. XBOW’s AI-driven platform autonomously executes adversarial workflows to find and validate exploitable vulnerabilities, and the…

Daily Recap, today’s cybersecurity headlines cover regulatory actions against Kochava over location data, and privacy settlements tied to Forbes, while data-exposure incidents affected Vimeo and Canvas. The report also flags critical vulnerabilities, such as Bleeding Llama (CVE-2026-7482) in Ollama and MOVEit flaws, plus active phishing and threat campaigns like VENOMOUS#HELPER and BirdCall, along with the Karakurt extortion group. #Kochava #Forbes #Vimeo #Canvas #ShinyHunters #BirdCall #Karakurt #Conti #BlackCat #Trellix #AstrixSecurity #ShaiWorm #VENOMOUS_HELPER #BleedingLlama #Ollama #MOVEit #PixelTitanM2
Most network incidents escalate not because alerts are missing but because response breaks down during triage, enrichment, and routing. On June 02, 2026 at 12:00 PM ET BleepingComputer will host a webinar with Edgar Ortiz of Tines demonstrating how intelligent workflows, automation, and AI can enrich alerts, prioritize and route incidents, and enable coordinated containment. #BleepingComputer #Tines
MuddyWater disguised a state-sponsored cyber-espionage operation as a Chaos ransomware attack, using Microsoft Teams social engineering to steal credentials, bypass MFA, and establish remote persistence. Rapid7 attributes the incident to MuddyWater based on infrastructure overlap, a unique code-signing certificate, and operational tradecraft, suggesting the ransomware was a cover for espionage rather than financial gain. #MuddyWater #Chaos #MicrosoftTeams #Game.exe #Qilin #MOIS

CISA warns that nation-state actors have embedded themselves in US critical infrastructure and telecommunications, positioning to disrupt operational technology beyond traditional espionage. The agency launched CI Fortify to help operators develop isolation and recovery capabilities so public health, national defense, and economic systems can continue operating during prolonged or degraded cyber…
A Romanian national, 53-year-old Gavril Sandu, was extradited to the United States in April 2026 to face charges related to a vishing-based bank fraud scheme carried out between May 2009 and October 2010. Authorities say Sandu hacked small businesses’ VoIP systems to steal customer credentials, cloned payment cards and acted as…
Oracle is adding monthly Critical Security Patch Updates (CSPUs) to supplement its quarterly Critical Patch Update program, with the first CSPU on May 28 followed by releases on June 16 and August 18. The company says frontier AI models have accelerated vulnerability discovery and remediation, enabling customers—especially those in customer-managed environments—to…
Palo Alto Networks is preparing patches for a critical PAN-OS zero-day, CVE-2026-0300, a buffer overflow in the User-ID Authentication Portal that can allow unauthenticated attackers to execute code as root on affected PA and VM series firewalls. The vendor reported limited targeted exploitation of internet-exposed portals, plans a first-round fix on…
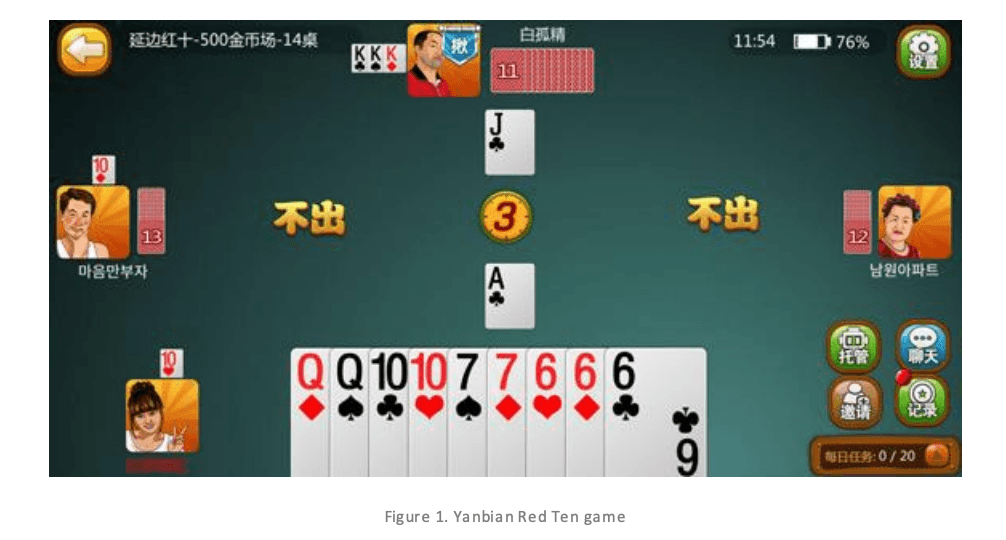
A North Korean threat actor, APT37, delivered a backdoor called BirdCall embedded in popular Android card games from Sqgame to target ethnic Koreans in the Yanbian region, enabling screenshots, call recording, and broad data theft. ESET discovered seven Android versions of BirdCall and traced the infection to a compromised update package…
Quasar Linux (QLNX) is a previously undocumented Linux implant targeting developers’ systems and DevOps environments with a blend of rootkit, backdoor, and credential-stealing capabilities. Trend Micro analysis shows QLNX compiles rootkit components on the host, runs fileless and in-memory for stealth, and uses multiple persistence mechanisms across npm, PyPI, GitHub, AWS, Docker, and Kubernetes. #QuasarLinux #TrendMicro

CISA is urging critical infrastructure operators to plan to deliver essential services for weeks to months under emergency isolation and is launching the CI Fortify initiative to assess and harden operational technology against attacks entering through IT or third-party vendors. The agency warns that state-sponsored groups Salt Typhoon and Volt Typhoon continue to threaten sectors like electricity, water, and internet, and CISA will pilot targeted assessments and isolation/recovery plans to maintain service delivery while disconnected. #SaltTyphoon #VoltTyphoon
Open source end-of-life (EOL) packages are frequently omitted from CVE investigations and vulnerability feeds, leaving millions of versions unflagged and enterprises exposed. Industry research from HeroDevs and Sonatype shows 5.4M EOL package versions across major registries and finds that AI-driven discovery like Project Glasswing may increase uncovered vulnerabilities in unmaintained code. #SpringSecurity #ProjectGlasswing