SecurityWeek will host the 2026 Artificial Intelligence (AI) Risk Summit on August 11-12, 2026, at the Ritz-Carlton in Half Moon Bay, CA, bringing together security leaders, researchers, policymakers, and enterprise risk professionals. The event will focus on AI security challenges such as adversarial attacks, deepfakes, governance, compliance, and protecting sensitive data…
Category: Cyber Security News
Microsoft has released the optional KB5089573 preview cumulative update for Windows 11 25H2 and 24H2, bringing 30 non-security changes focused on performance, reliability, and Windows Hello improvements. The update also adds shared audio, better battery and sensor behavior, and phased Secure Boot certificate rollout while Microsoft notes a separate known issue on Windows Server 2016 after KB5087537. #Microsoft #KB5089573 #Windows11 #WindowsHello #SecureBoot #WindowsServer2016
Dutch National Police arrested a 35-year-old man from Buren on suspicion of repeatedly hacking AFC Ajax’s computer systems and exploiting vulnerabilities that exposed fan data and ticketing controls. The incident affected hundreds of individuals and enabled access to more than 300,000 accounts, while Ajax has since patched the flaws and notified authorities. #AFCAjax #DutchNationalPolice #Buren
CISA has ordered U.S. federal agencies to patch an actively exploited critical privilege escalation flaw in the LiteSpeed cPanel user-end plugin by Friday, May 29. The vulnerability, tracked as CVE-2026-48172, can let unauthenticated attackers run arbitrary scripts with root privileges, and users are urged to update immediately or block suspicious IPs. #CVE-2026-48172 #LiteSpeed #cPanel #WHM #CISA
CISA has urged federal agencies to urgently patch CVE-2026-48172, a critical privilege escalation flaw in the LiteSpeed user-end plugin for cPanel that has been actively exploited in the wild. The issue affects user-end plugin versions v2.3 through v2.4.4 and can enable attackers to run arbitrary scripts with root privileges, with fixes…
Silent Ransom Group (SRG) is using impersonation of IT support to target law firms, tricking employees into granting remote access or allowing in-person device insertion. The group then quickly steals data, avoids deploying ransomware, and extorts victims by threatening to leak the stolen information online. #SilentRansomGroup #SRG #WinSCP #Rclone #FBI…

The cyberattack against LA Metro has been linked to the Iranian government through investigations connecting the claimed attacker, Ababil of Minab, to Iran-linked infrastructure and activity. The incident caused internal disruptions and involved data theft and destructive actions, including access to systems used to monitor trains. #LAMetro #AbabilofMinab #BlackShadow…

Daily Recap, AI security and governance advancements stood out as AppOmni launched Marlin AI for autonomous SaaS security investigations and Varonis Atlas added the Claude Compliance API to strengthen AI governance and compliance controls. In threat and patching coverage, an Iranian APT targeted aviation and software firms with updated tools, CISA ordered federal agencies to patch an actively exploited Drupal flaw, and 7-Eleven disclosed a breach impacting about 185,000 people. #AppOmni #Marlin AI #Varonis Atlas #Claude Compliance API #Iranian APT #Drupal #CISA #7-Eleven #Microsoft Defender
Charter Communications confirmed a data breach after ShinyHunters threatened to leak stolen information, while the company says no sensitive personal information or CPNI was exfiltrated. The attackers claim they used vishing to compromise an employee’s Microsoft Entra account and steal millions of customer records from a Salesforce instance. #CharterCommunications #ShinyHunters #MicrosoftEntra #Salesforce
Mandiant reported that attackers exploited CVE-2026-5426 in KnowledgeDeliver LMS servers as a zero-day to deploy the Godzilla web shell and gain remote code execution through ViewState deserialization. The intrusion relied on reused ASP.NET machine keys, led to fake software installation prompts and Cobalt Strike infection, and was tailored to the targeted organization. #CVE-2026-5426 #KnowledgeDeliver #Godzilla #CobaltStrike #Mandiant #ViewState

Russian President Vladimir Putin has appointed Andrei Kozlov, a former Rostec cybersecurity executive, as an aide to Security Council Secretary Sergei Shoigu. Leaked data alleged Kozlov held a classified clearance under Military Unit 26165, the GRU-linked unit associated with Fancy Bear, APT28, BlueDelta and Forest Blizzard. #AndreiKozlov #SergeiShoigu #MilitaryUnit26165 #FancyBear #APT28…
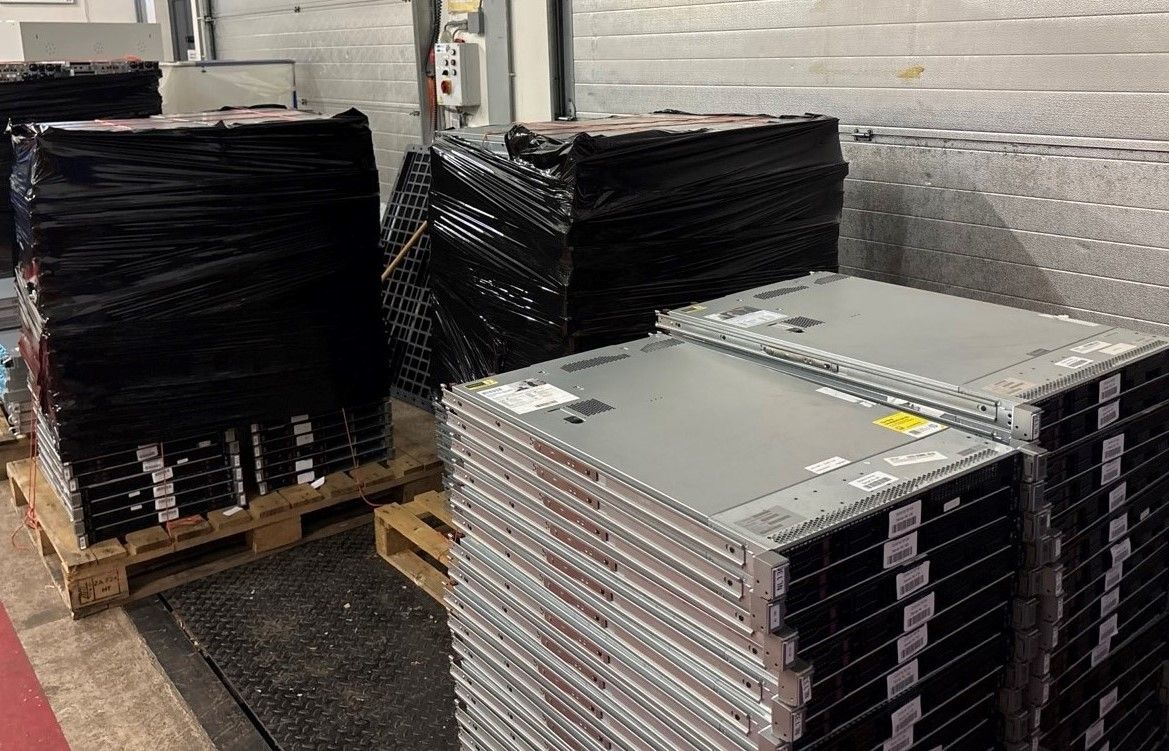
Dutch authorities arrested two IT entrepreneurs over alleged violations of European sanctions tied to hosting infrastructure used in pro-Russian cyberattacks and disinformation campaigns. Investigators say the network involved Stark Industries, MIRhosting, WorkTitans, the Doppelgänger-linked Reliable Recent News network, and NoName057(16). #StarkIndustries #MIRhosting #WorkTitans #ReliableRecentNews #Doppelgänger #NoName05716…

Lithuanian prosecutors are investigating a breach of the Centre of Registers that exposed more than 600,000 records from the country’s state registry systems, including personal and property-related data. Authorities say the attack used misused login credentials and may have originated from abroad, while no hacking group has claimed responsibility. #CentreofRegisters #Lithuania…
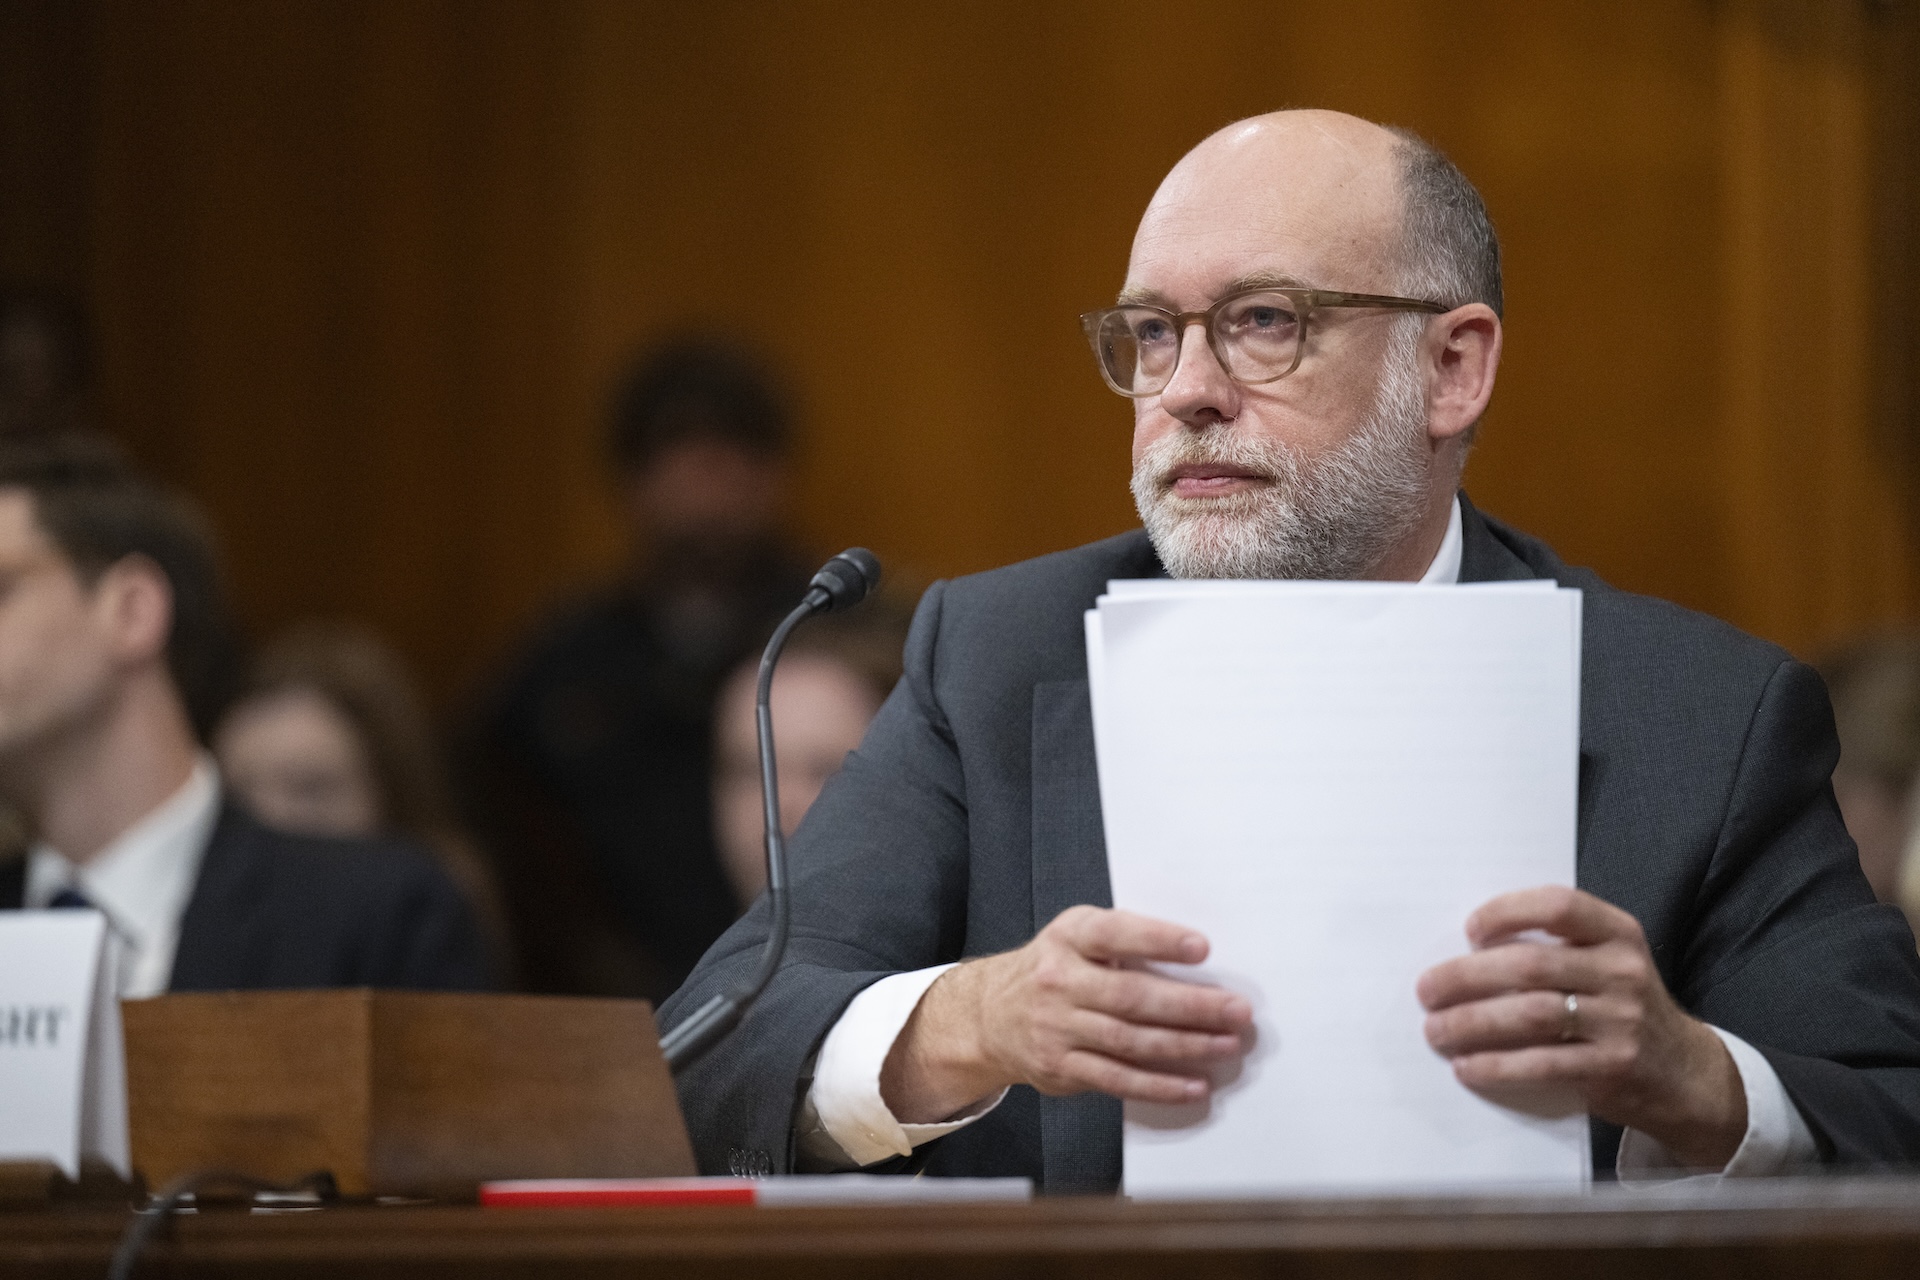
The White House has revised federal logging rules with a risk-based approach that aims to improve threat detection, investigations, and recovery while reducing unnecessary data collection. The update replaces the 2021 guidance and directs CISA to publish a logging reference architecture within 90 days, though some experts worry the transition could create a temporary gap in agency prioritization. #WhiteHouse #CISA #M-21-31 #M-26-14
Apple has released quantum-resistant cryptographic code and the formal verification tools used to prove its correctness, making them publicly available for independent review and broader industry use. The release covers ML-KEM and ML-DSA in corecrypto, and Apple says its hybrid verification approach uncovered a bug that conventional testing could have missed. #Apple #corecrypto #ML-KEM #ML-DSA #Isabelle #Cryptol