
Army Gen. Joshua Rudd has launched external and internal studies to review how U.S. Cyber Command can modernize, with MITRE tasked to examine acquisition and other structural issues. The reviews come as the command pushes CYBERCOM 2.0, a strategy meant to improve agility, industry ties, and operational capability. #CyberCommand #MITRE #CYBERCOM2.0…
Category: Cyber Security News
A Romanian national, Catalin Dragomir, was sentenced to 56 months in prison for hacking into Oregon’s Office of Emergency Management and other U.S. targets. He used the alias “inthematrixl” to sell stolen access and credentials on the dark web, including sensitive employee data from the Oregon office. #CatalinDragomir #inthematrixl #OregonOfficeofEmergencyManagement…

A malicious npm package named “mouse5212-super-formatter” was found stealing files from Anthropic’s Claude AI workspace by uploading them to a threat actor-controlled GitHub account. The package, dubbed Malware-Slop, disguises its activity as a sync utility, and it even leaked the attacker’s GitHub token while remaining available on npm. #mouse5212-super-formatter #Malware-Slop #Anthropic…

WatchGuard and ESET found two active banking trojan campaigns targeting Windows and Android users across Latin America and Europe, including Grandoreiro attacks against banks in Portugal and BTMOB infections spread through fake app sites. Both families use phishing, legitimate-service abuse, and anti-analysis techniques to steal credentials and expand their reach. #Grandoreiro…
Researchers at Novee Security disclosed CVE-2026-41241, a high-severity stored XSS vulnerability in Pretalx that could let any registered speaker execute malicious JavaScript in an organizer’s browser when they search for a submission. The issue affected a widely used conference CFP and scheduling platform, was patched in Pretalx 2026.1.0, and could be…
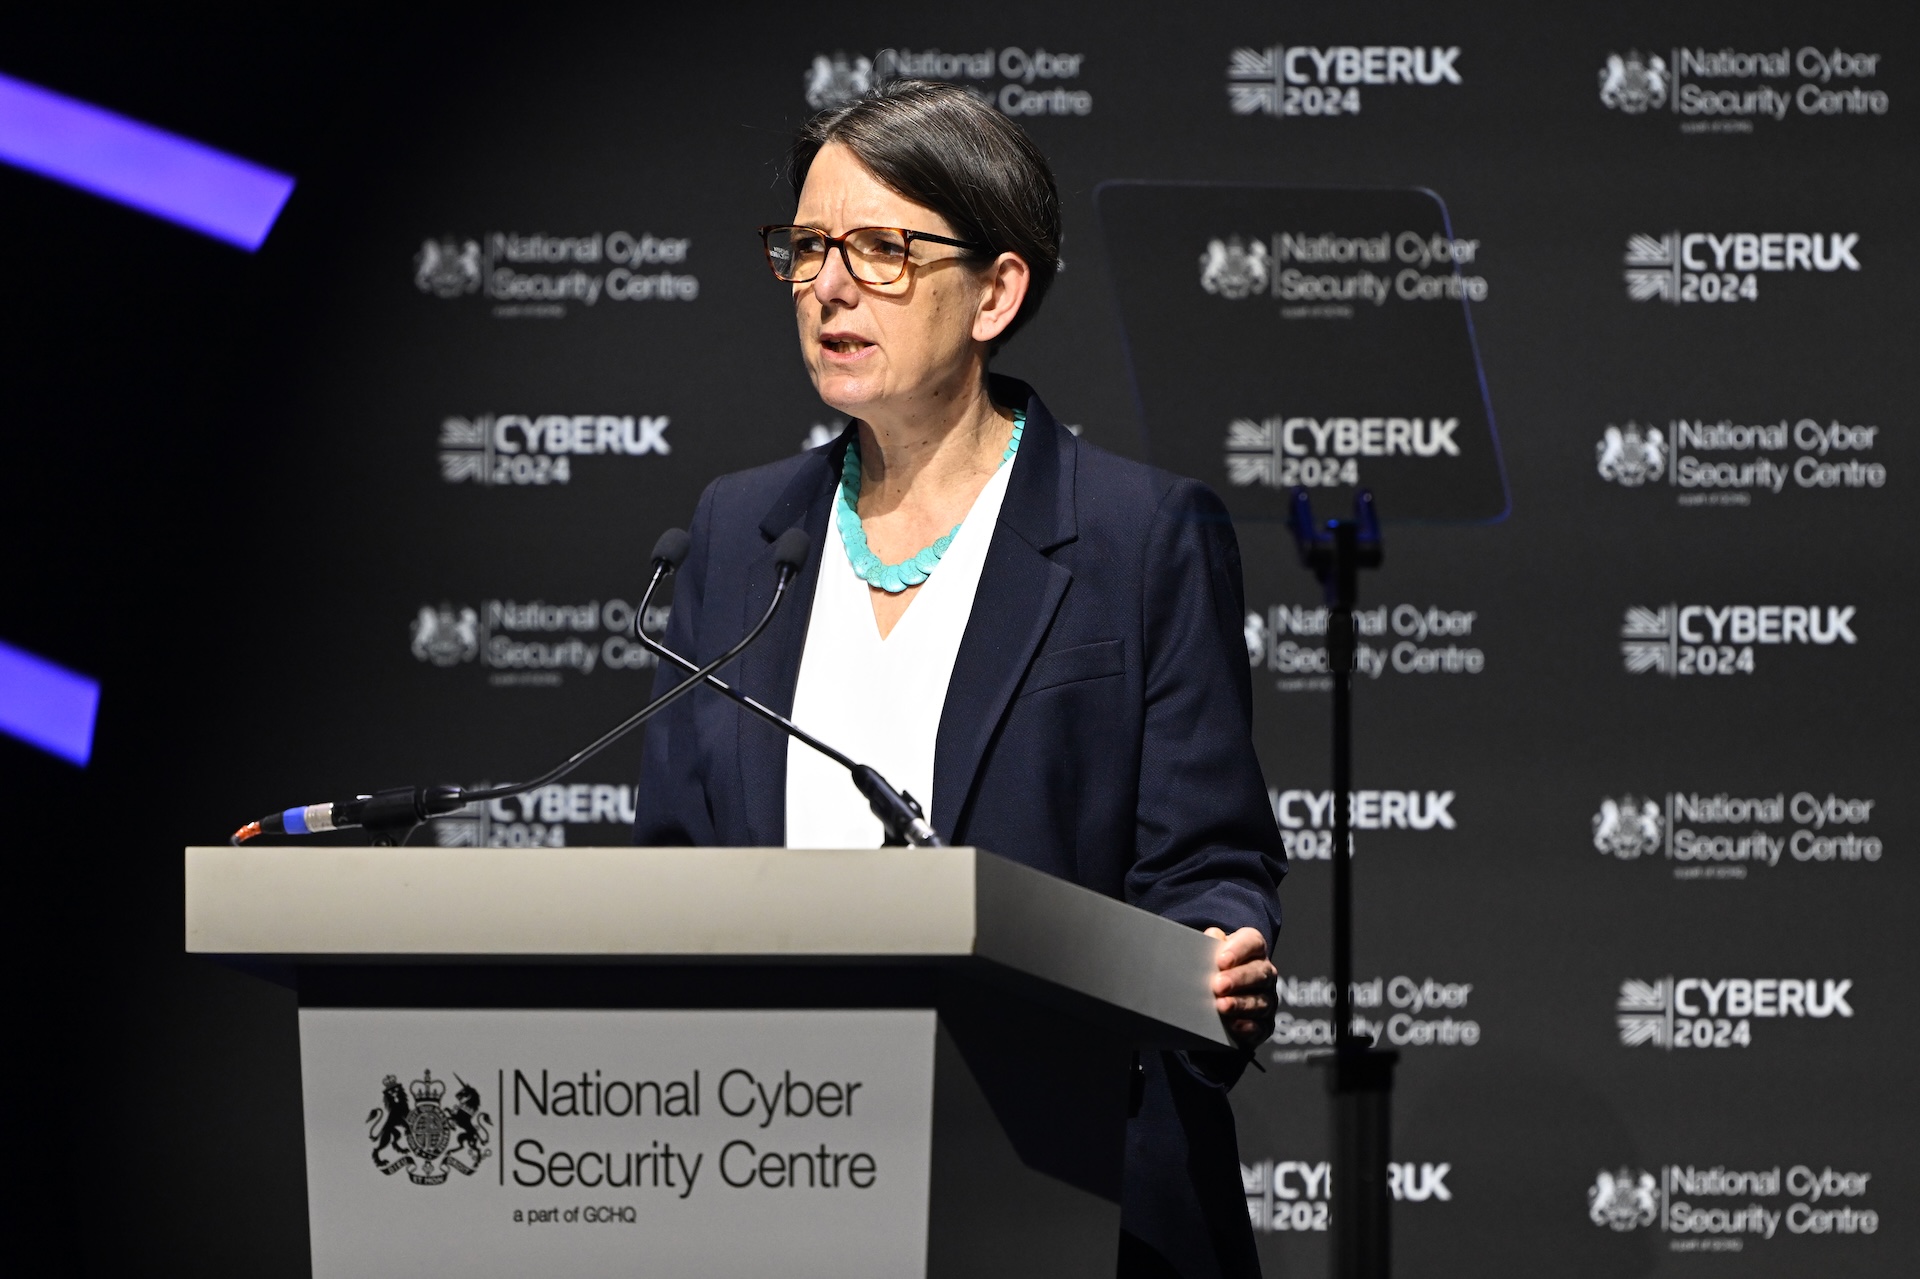
Artificial intelligence is rapidly changing both cyber offense and defense, with GCHQ chief Anne Keast-Butler warning that it can be weaponized below the threshold of traditional warfare. She also highlighted growing risks from China and Russia as AI, data, and automation reshape conflicts and cybersecurity. #GCHQ #AnneKeastButler #China #Russia #Ukraine
The Silent Ransom Group is targeting U.S. law firms with fake IT support calls, phishing, and even in-person visits to steal data, according to the FBI. Researchers say the group, also known as Chatty Spider, UNC3753, and Storm-0252, has carried out more than 100 attacks and is unusually focused on legal organizations. #SilentRansomGroup #ChattySpider #UNC3753 #Storm0252
OpenAI outlined a five-part plan to support election security for the 2026 midterms, focusing on reliable voting information, cybersecurity help, deepfake watermarking, and blocking election interference. The company also announced tools for election officials and a new partnership with the Associated Press to share election data. #OpenAI #SynthID #AssociatedPress #CodexSecurity #TrustedAccessForCyber

Threat actors are running an SEO poisoning campaign that pushes malicious download pages for popular utilities to compromise high-performance Windows systems and install cryptomining payloads. Microsoft also found that some users were steered to attacker-controlled links by AI chatbots, with the campaign using ScreenConnect, process hollowing, and GPU miners like gminer, lolMiner, and SRBMiner-MULTI. #ScreenConnect #CrystalDiskInfo #HWMonitor #FurMark #KLiteCodecPack #PDFgear #gminer #lolMiner #SRBMinerMULTI #Microsoft
Britain’s GCHQ chief Anne Keast-Butler warned that AI is being weaponized in a “space between peace and war,” while Russia intensifies daily hybrid activity against the West. She said the U.K. must urgently strengthen cybersecurity, protect critical infrastructure, and deepen cooperation with allies such as the United States. #GCHQ #AnneKeastButler #Russia…
The FBI warned that the Silent Ransom Group (SRG) is targeting U.S. law firms with in-person data theft by posing as IT support to gain access to victim computers. The gang, also known as Luna Moth, Chatty Spider, and UNC3753, uses stolen data for extortion and has a history of targeting legal and financial organizations. #SilentRansomGroup #SRG #LunaMoth #ChattySpider #UNC3753
CrowdStrike, Google, and The Shadowserver Foundation disrupted the Glassworm botnet by cutting off four coordinated command-and-control channels tied to Solana blockchain transactions, BitTorrent DHT, Google Calendar, and direct VPS connections. The botnet had been used since October 2025 in supply-chain attacks against developers through malicious OpenVSX, VS Code, GitHub, and npm artifacts that stole wallets and credentials. #Glassworm #CrowdStrike #Google #ShadowserverFoundation #OpenVSX #VSCode #GitHub #npm #Solana #BitTorrent
Strong Active Directory password security depends on balancing enforcement with usability, and the article recommends passphrases, breached-password blocking, and smarter expiration policies to reduce weak choices and user workarounds. It also highlights tools like Specops Password Policy, Specops Password Auditor, password managers, self-service resets, and clear notifications to improve both protection and the user experience. #SpecopsPasswordPolicy #SpecopsPasswordAuditor #ActiveDirectory

A Romanian national, Catalin Dragomir, was sentenced in the United States after admitting he sold access to an Oregon state government network and other compromised systems. Prosecutors said his activity caused more than $250,000 in losses and involved at least 10 other organizations, with the Oregon access reportedly sold for $3,000…

RevEng.AI has raised $15 million in a Series A round led by NATO Innovation Fund, bringing its total funding to $19.5 million. The London-based startup uses its BinNet AI model to analyze software at the binary level without source code, helping detect vulnerabilities, backdoors, and hidden functionality in executables, firmware, and…