Tina Peters remained defiant in her first public interview after having her prison sentence commuted, repeating election-conspiracy claims and saying she will keep fighting to clear her criminal record. The interview drew renewed attention to her felony conviction for breaching Mesa County election facilities, while Governor Jared Polis continued to defend the commutation despite criticism from Democrats and election officials. #TinaPeters #JaredPolis #MesaCounty
Category: Cyber Security News
Researchers are responding to CVE-2026-0257, an authentication-bypass flaw in Palo Alto Networks firewalls that was rapidly upgraded from medium to critical after active exploitation was confirmed. Attackers are using it to bypass security controls and establish VPN access, prompting urgent patching guidance from Palo Alto Networks and inclusion in CISA’s KEV catalog. #CVE-2026-0257 #PaloAltoNetworks #CISA #Rapid7
Spanish National Police arrested a suspect for leaking sensitive personal data tied to key Spanish state institutions, including INCIBE, the National Police, the Civil Guard, and the National Security Council. The data was allegedly compiled from older breaches and open-source intelligence, and was linked to the doxing operation reported by Police-ESP-Doxed. #INCIBE #SpanishNationalPolice #Police-ESP-Doxed #BreachForum #Doxbin
More than 30 npm packages in Red Hat’s @redhat-cloud-services namespace were compromised in a supply-chain attack that deployed the new Shai-Hulud variant “Miasma” to steal developer credentials and cloud secrets. Red Hat says the affected packages were limited to internal development tooling, but researchers report the campaign has already compromised 309 GitHub repositories and is linked to similarities with Mini Shai-Hulud. #RedHat #Miasma #ShaiHulud #MiniShaiHulud
DriveSurge is running large-scale malware distribution campaigns through compromised websites using ClickFix and FakeUpdates lures, with visitors redirected by the zTDS traffic distribution system. The campaign delivers fake browser update prompts and malicious commands, affecting both Windows and macOS users while leveraging thousands of hijacked sites. #DriveSurge #SilentPush #zTDS #ClickFix #FakeUpdates
Nearly 2,000 WordPress websites were infected with malware that hides command-and-control data inside Steam Community profile comments using invisible Unicode characters. GoDaddy researchers found the campaign on about 1,980 sites and traced it to a payload that downloads malicious JavaScript, installs a backdoor, and evades detection through stealthy encoding and obfuscation. #SteamCommunity #WordPress #GoDaddy #hello-mywordlinfo
Dashlane said some user accounts were automatically suspended after brute-force attacks attempted logins from unfamiliar devices and distant locations. The company later confirmed the accounts were unsuspended and stated there was no evidence that Dashlane’s systems were compromised. #Dashlane #BleepingComputer
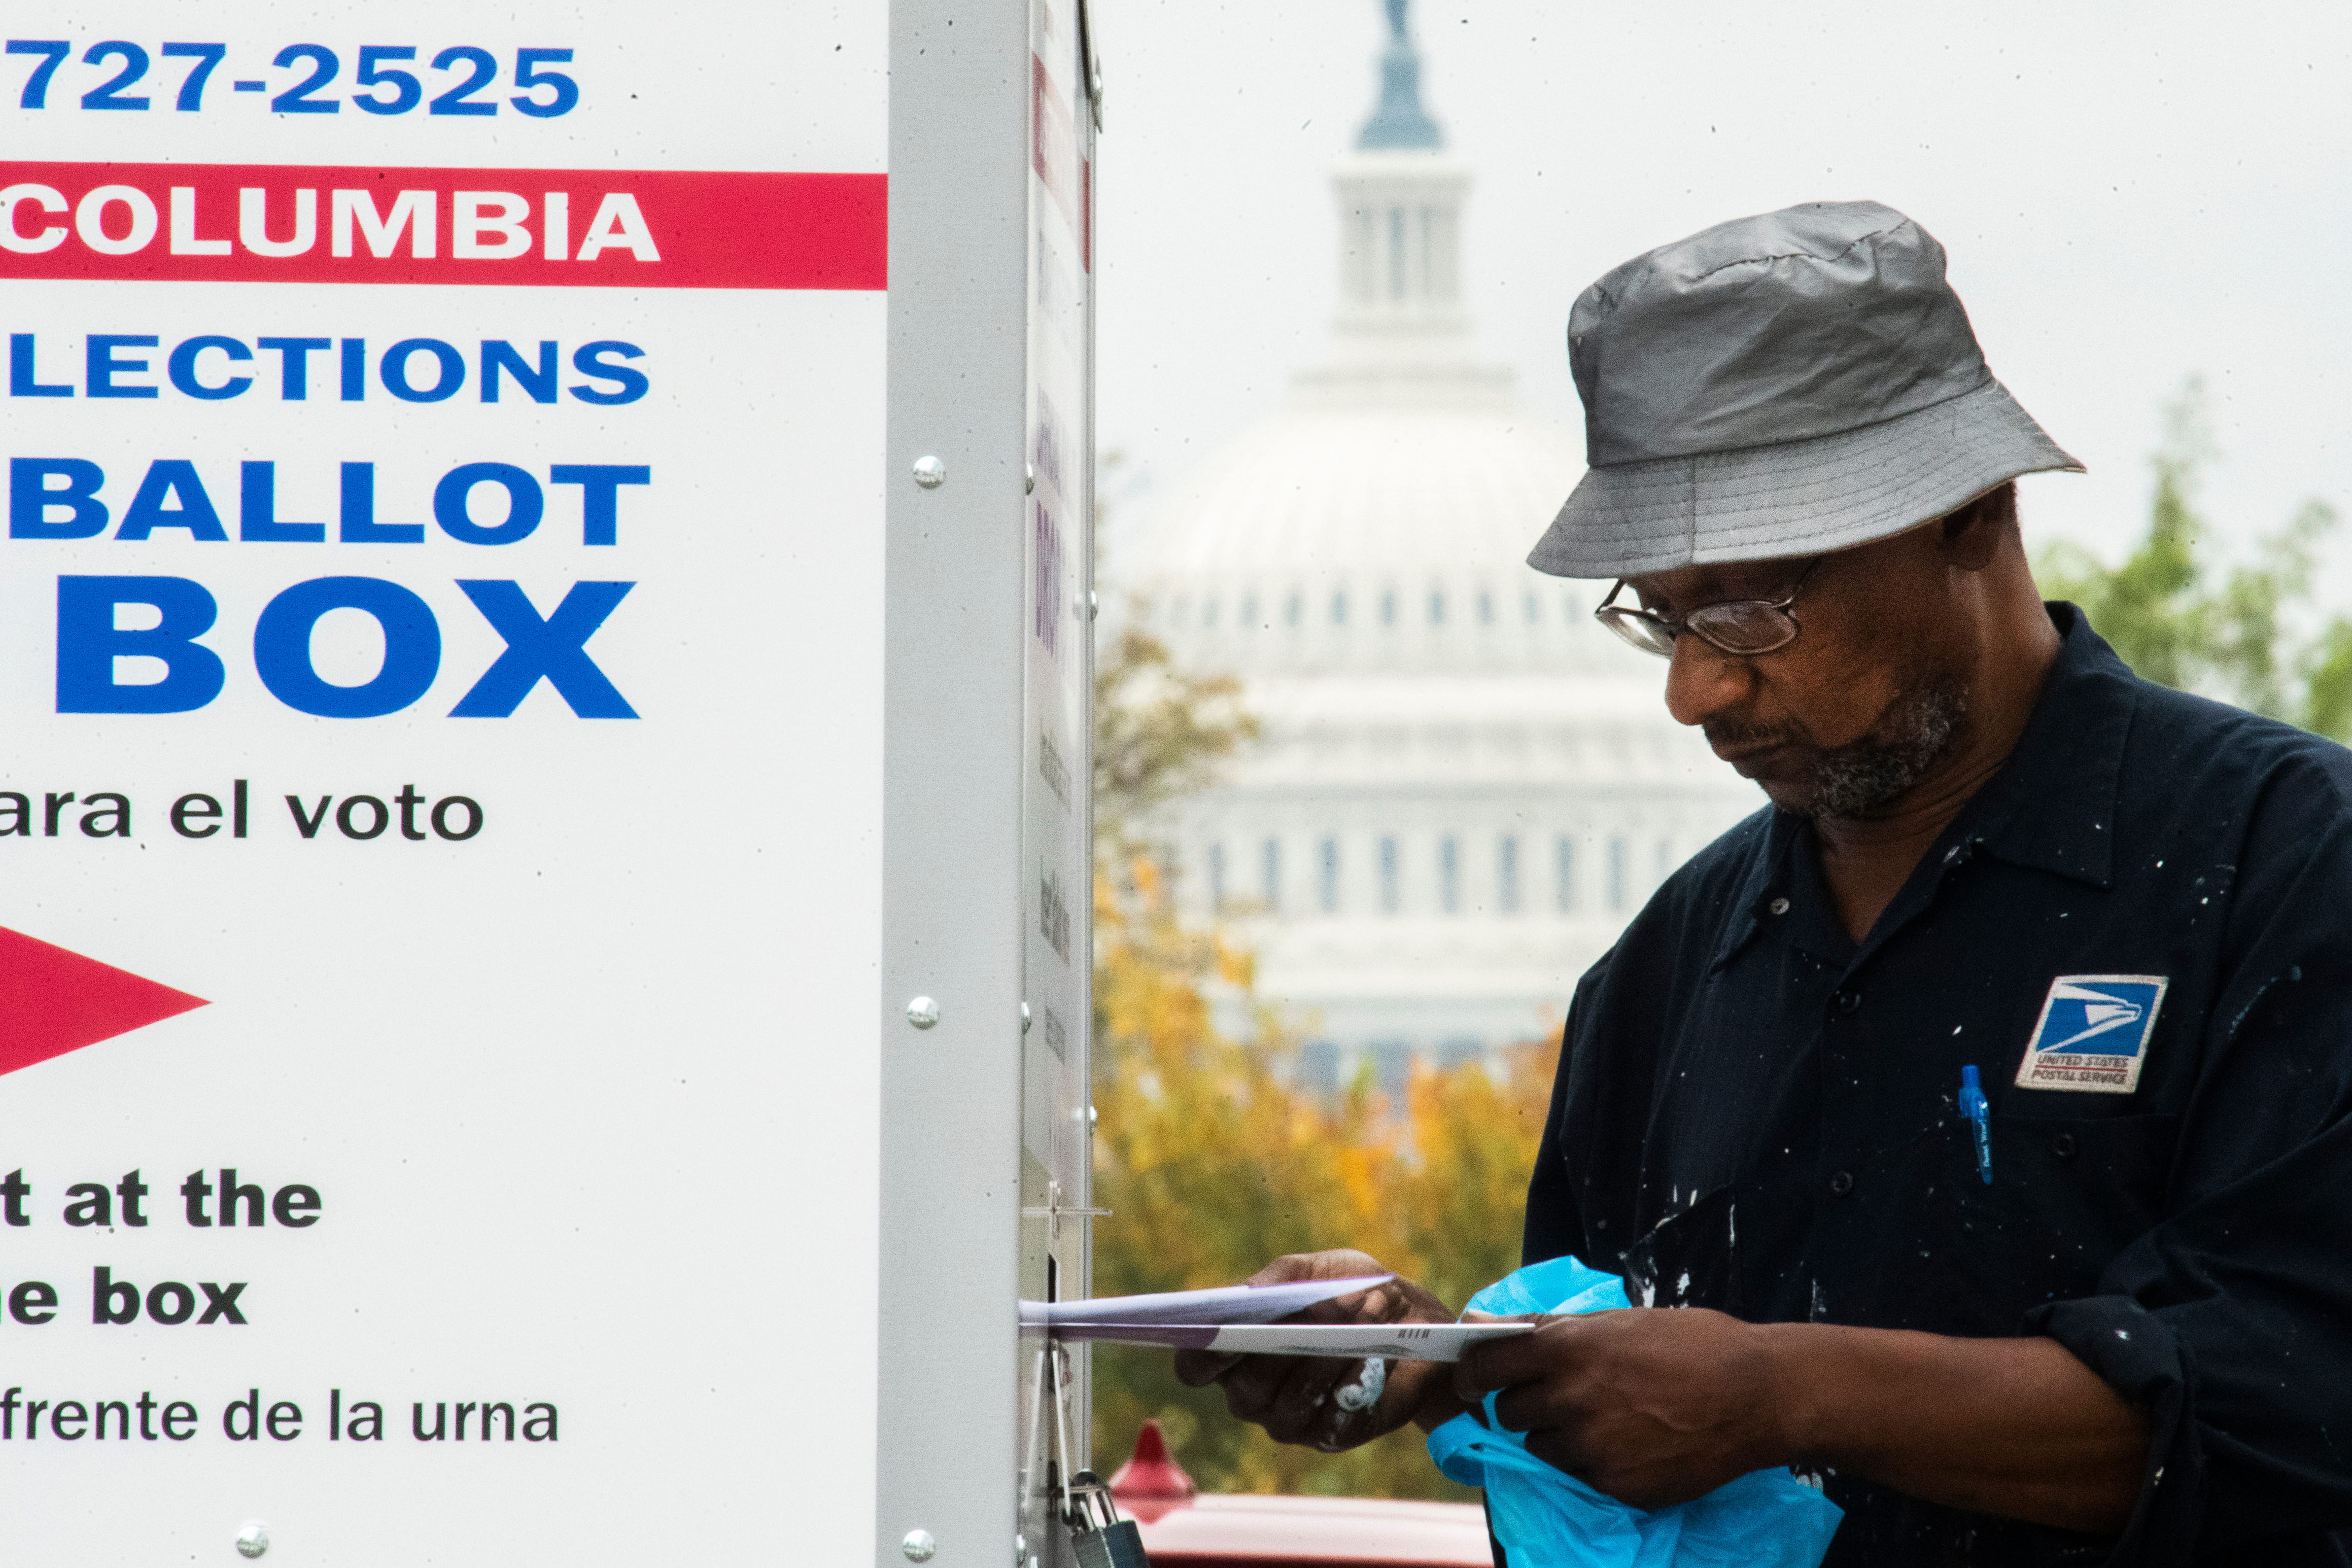
The U.S. Postal Service is moving ahead with new rules for mail-in and absentee ballots after a court declined to immediately block President Donald Trump’s executive order. The proposed changes would add barcodes, tracking, and verification steps that critics say could let the federal government monitor or interfere with ballot delivery. #USPS #DonaldTrump #ProtectDemocracy

Threat actors are actively exploiting a critical Windows Netlogon vulnerability, tracked as CVE-2026-41089, to gain remote code execution on domain controllers. Centre for Cybersecurity Belgium urges immediate patching as the flaw can let unauthenticated attackers run code with System privileges on affected Windows servers. #CVE-2026-41089 #WindowsNetlogon #CentreforCybersecurityBelgium #Microsoft…
Dutch police say they disrupted a botnet of 17 million infected devices, with 200 control servers identified and multiple servers seized in the Netherlands. The operation is linked in local reports to Asocks, while the takedown comes amid other recent actions against botnets such as Aisuru and Kimwolf. #Asocks #Aisuru #Kimwolf…
Threat actors are exploiting CVE-2026-8732 in the WP Maps Pro WordPress plugin to create administrator accounts and fully take over vulnerable websites. Defiant says the flaw was patched in WP Maps Pro 6.1.1, while more than 1,700 attacks were blocked in the past 24 hours. #WPMapsPro #CVE-2026-8732 #Defiant…
A critical RCE vulnerability in a widely used VPN application shows how quickly attackers can exploit newly disclosed flaws, often before organizations even receive an alert. The article argues that immediate, software-specific vulnerability intelligence is essential to reduce exposure and prevent breaches, highlighting SecAlerts as a faster alternative to delayed sources like NVD. #SecAlerts #NVD #CVE
Microsoft is investigating an ongoing incident that is preventing some users from opening files in Microsoft Teams and Office for the web, including Excel and PowerPoint. The company says the outage appears to be a cross-service issue and is working to restore access as soon as possible. #MicrosoftTeams #Officefortheweb #Excel #PowerPoint

Cybersecurity Threat Research ‘Weekly’ Recap. The roundup covers supply-chain and developer tooling abuse (including malicious packages, RAT installers, and backdoored developer ecosystems) alongside ongoing phishing, AiTM, and social engineering campaigns targeting 2FA and payment data. It also highlights actively exploited vulnerabilities and long-running access via RATs, cloud/Kubernetes secret theft, blockchain-based C2, and increasing use of AI tools to automate attacks and phishing workflows.
#SicoobSDK #NuGet #Sentry #axios #LaravelLang #RVTools #DenoRAT #DinDoor #Tycoon2FA #PhaaS #PhaaSEcosystem #CVE-2026-0257 #GlobalProtect #CVE-2026-31431 #CopyFail #Gogs #KnowledgeDeliver #NimbusRAT #DriveSurge #OperationDragonWeave #SapphireSleet #OverlayPhantom #AtlasCross #Kimsuky #AhnLab #QuasarLinux #QLNX #P2Pinfect #ClearFake #SectopRAT #ACRStealer #WormGPT #Promptflux #SilentPushContextGraph #SectopRAT
Dragos has acquired Phosphorus to expand its xIoT capabilities and improve visibility, intelligence, and remediation for connected devices across critical infrastructure and operational networks. The companies said existing customers will continue to be supported while they phase in integration, with Sonu Shankar remaining to lead Phosphorus inside Dragos. #Dragos #Phosphorus #RobertMLee…