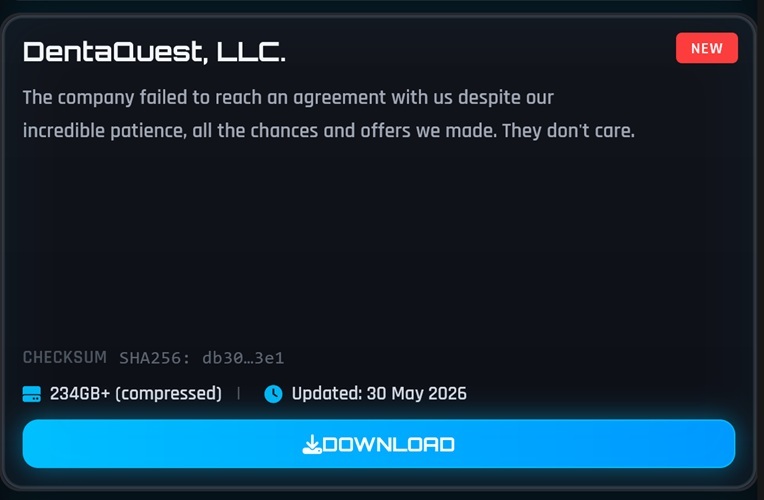
ShinyHunters claims to have stolen and leaked 234 GB of data from DentaQuest, affecting roughly 2.6 million accounts. The exposed information may include names, addresses, email addresses, phone numbers, dates of birth, government-issued IDs, and health insurance details. #ShinyHunters #DentaQuest #HaveIBeenPwned…
Category: Cyber Security News

This week’s roundup covers attackers abusing AI chatbot and SEO recommendations to spread fake utilities, deploy ScreenConnect, and run GPU-focused cryptocurrency miners, alongside a new Grandoreiro banking trojan campaign and The Gentlemen ransomware’s self-propagating Go encryptor. It also highlights exposed Automatic Tank Gauge systems, a Hola Browser supply-chain miner, Ultrahuman’s data…
Cisco warned that CVE-2026-20245 is an actively exploited zero-day in Cisco Catalyst SD-WAN Manager that can let low-privileged attackers escalate to root by uploading a crafted file. The flaw affects multiple deployment types, and Cisco recommends checking logs for suspicious tenant upload activity while waiting for a patch. #CVE-2026-20245 #CiscoCatalystSDWANManager #Mandiant #CiscoPSIRT #vManage
Cisco warned customers about CVE-2026-20245, an unpatched Cisco Catalyst SD-WAN Manager vulnerability that is being exploited in the wild and can let an authenticated attacker run commands as root. The flaw requires netadmin privileges and has been linked to a series of Cisco SD-WAN exploits in 2026, including attacks previously associated…
RCI Hospitality Holdings said a data breach tied to an IDOR flaw in an IIS web server affects more than 40,000 people, exposing sensitive personal information including names, contact details, dates of birth, Social Security numbers, and driver’s license numbers. The company has notified the FBI and is cooperating with the…
Chinese military intelligence officers are posing as recruiters on professional networking and job platforms to target government, military, and other sensitive personnel for privileged information. The Five Eyes warn that these campaigns use fake job offers, encrypted messaging, and paid reports to build long-term access to classified or strategically useful data….
Russia is moving to classify Belarusian Cyber Partisans and Silent Crow as extremist organizations, following their claims of attacks on Russian and Belarusian government and critical infrastructure targets. The proposal comes after their alleged role in the July 2025 Aeroflot breach, which disrupted more than 100 flights and exposed sensitive airline…

The FTC is considering whether to modify or set aside its 2022 settlement order against Twitter, now X, over allegations that account security data was used to target advertising. X argues the order is outdated and burdensome, while the FTC is seeking public comment before deciding by July 2. #Twitter #X…

The Trump administration is reportedly considering Palantir CTO Shyam Sankar to lead CISA, though the White House later disputed that the selection was accurate. The possible nomination comes as CISA remains without a Senate-confirmed director and as the administration pushes forward on new AI policy and cybersecurity priorities. #ShyamSankar #Palantir #CISA…

Frontier and agentic AI are rapidly entering defense and intelligence environments, but the Claude Mythos technical preview incident shows how quickly unauthorized access or misuse can undermine trust. The article argues that secure infrastructure, governed access, and cross-domain protection are essential for deploying AI safely at mission scale. #ClaudeMythos #Everfox #DaveWajsgras…

A security researcher found a flaw in Anthropic’s Claude Code GitHub Action that could let an attacker take over vulnerable public repositories with a single opened GitHub issue, and even potentially poison Anthropic’s own action repository. Anthropic fixed the issue in claude-code-action v1.0.94 after RyotaK of GMO Flatt Security reported it,…
The United Nations’ World Food Programme disclosed that its Gaza self-registration application was breached, exposing personal data for beneficiaries including names, ID numbers, phone numbers, and location details. The WFP temporarily suspended the platform and warned beneficiaries to watch for phishing attempts while it investigates the incident and strengthens security measures. #WorldFoodProgramme #Gaza #Palestine
DentaQuest, a major dental benefits administrator and Sun Life subsidiary, suffered a breach that reportedly exposed sensitive data tied to 2.6 million accounts. ShinyHunters claimed responsibility for stealing more than 234 GB of data, later leaking it after negotiations reportedly failed. #DentaQuest #ShinyHunters #SunLife
A new Magecart campaign is abusing Google Tag Manager and Stripe’s API infrastructure to host a credit card skimmer and hide stolen checkout data from defenses. Sansec says the attack targets Magento/Adobe Commerce stores, with variants also using Google Firestore to blend in with legitimate payment traffic. #Magecart #Sansec #GoogleTagManager #Stripe #AdobeCommerce #GoogleFirestore
The Windows version of Hola Browser was compromised in a supply chain attack that installed an undeclared executable identified as a Monero cryptocurrency miner. Researchers found the malicious file during AppEsteem certification checks, and Hola later confirmed the breach while saying only a small fraction of users were affected. #HolaBrowser #AppEsteem #Monero #Hola #Sygnia