Toshiba and Muji warned visitors about suspicious sign-in screens on their websites that could capture credentials, with the prompts linked to the external service polyfill[.]io. The issue also affected other Japanese organizations and appears tied to remnants of the 2024 polyfill[.]io incident, which had previously delivered malicious scripts to many websites. #Toshiba #Muji #polyfillio
Category: Cyber Security News

Apple reportedly removed the state-backed Russian messaging app Max from its App Store, prompting anger from Russian officials who called the move unfriendly and said it blocked access for millions of users. The app remains available on Android and RuStore, while critics warn its deep ties to government services and lack…
The European Commission has proposed new laws and strategies to reduce the EU’s dependence on foreign technology across semiconductors, cloud computing, AI, and open-source software, framing technological sovereignty as a security priority. The package includes Chips Act 2.0, the Cloud and AI Development Act, and open-source funding aimed at strengthening EU…

Multiple supply chain attacks have compromised dozens of npm packages to spread IronWorm and a new Miasma worm variant, both designed to steal secrets and self-propagate through developer and CI/CD environments. The campaigns abuse npm lifecycle hooks, GitHub commits, and trusted publishing to infect repositories, exfiltrate credentials, and keep republishing poisoned…
Darren Hughes, a San Jose man, was sentenced to more than 26 years in federal prison for trafficking methamphetamine and fentanyl through Nemesis Market, a major dark web marketplace. He sold drugs to an undercover agent for cryptocurrency and was later arrested with methamphetamine and a loaded ghost gun, while Nemesis Market itself had already been dismantled by German and American authorities. #NemesisMarket #DarrenHughes #RedwoodCityPoliceDepartment #FBI #DEA #IRS-CI
UNC5221, also tracked as VerdantBamboo, compromised Microsoft 365 environments using the Brickstorm backdoor along with newly identified malware Plenet and AgentPSD. The group maintained access for at least 18 months, also hit the victim’s MSP, and used a mix of stolen credentials, proxying, and custom backdoors to evade detection. #UNC5221 #VerdantBamboo #Brickstorm #Plenet #AgentPSD #Microsoft365 #Egnyte #Synology #pfSense #VMwarevSphere
CISA says attackers are actively exploiting the newly patched SolarWinds Serv-U flaw CVE-2026-28318 to crash exposed servers, and the issue affects the company’s Managed File Transfer and FTP software. SolarWinds has released a hotfix and urged admins to restrict access or block certain POST requests while CISA pushed federal agencies to patch by June 19. #SolarWinds #Serv-U #CVE-2026-28318 #CISA
Microsoft’s dispute with security researcher Nightmare Eclipse over the public disclosure of zero-day vulnerabilities has reignited debate about coordinated vulnerability disclosure and the trust gap between vendors and researchers. The controversy also highlights how delayed patching, public threats, and escalating tensions can increase risk for customers and weaken the security community’s willingness to report flaws. #Microsoft #NightmareEclipse #RedSun #UnDefend #BlueHammer #YellowKey #GreenPlasma #MiniPlasma #VSCode

Cybersecurity researchers uncovered OP-512, a previously unreported threat cluster linked with moderate to high confidence to China, which targeted Microsoft IIS servers to deploy a custom web shell framework. The group used multiple evasive techniques, including timestomping and automated self-reporting, to maintain stealth and support espionage operations on legacy, internet-facing systems….

ESET identified a new Android spyware campaign called Asin that targets Arabic-speaking users through fake apps disguised as government news, PDF tools, and war-update services. The activity remains unattributed, but the lures suggest possible targeting of Arabic-speaking journalists and OSINT researchers using malicious apps that require manual installation and permissions. #Asin…
CVE Lite CLI is an open-source, OSV-powered dependency scanner from Sonu Kapoor that checks npm, pnpm, and Yarn lockfiles locally and quickly identifies vulnerable JavaScript and TypeScript dependencies. It also recommends safe replacement commands, helping developers fix issues during coding instead of waiting for slow CI scans and repeated trial-and-error loops….
The Verizon 2026 DBIR and Keep Aware telemetry both show that Shadow AI, credential abuse, browser extensions, and ClickFix are becoming major enterprise risks that often evade traditional security controls. The report highlights that many attacks now begin and execute inside the browser, making browser-level visibility essential for detecting threats that network and endpoint tools miss. #VerizonDBIR #KeepAware #ClickFix #ChatGPT #Gemini
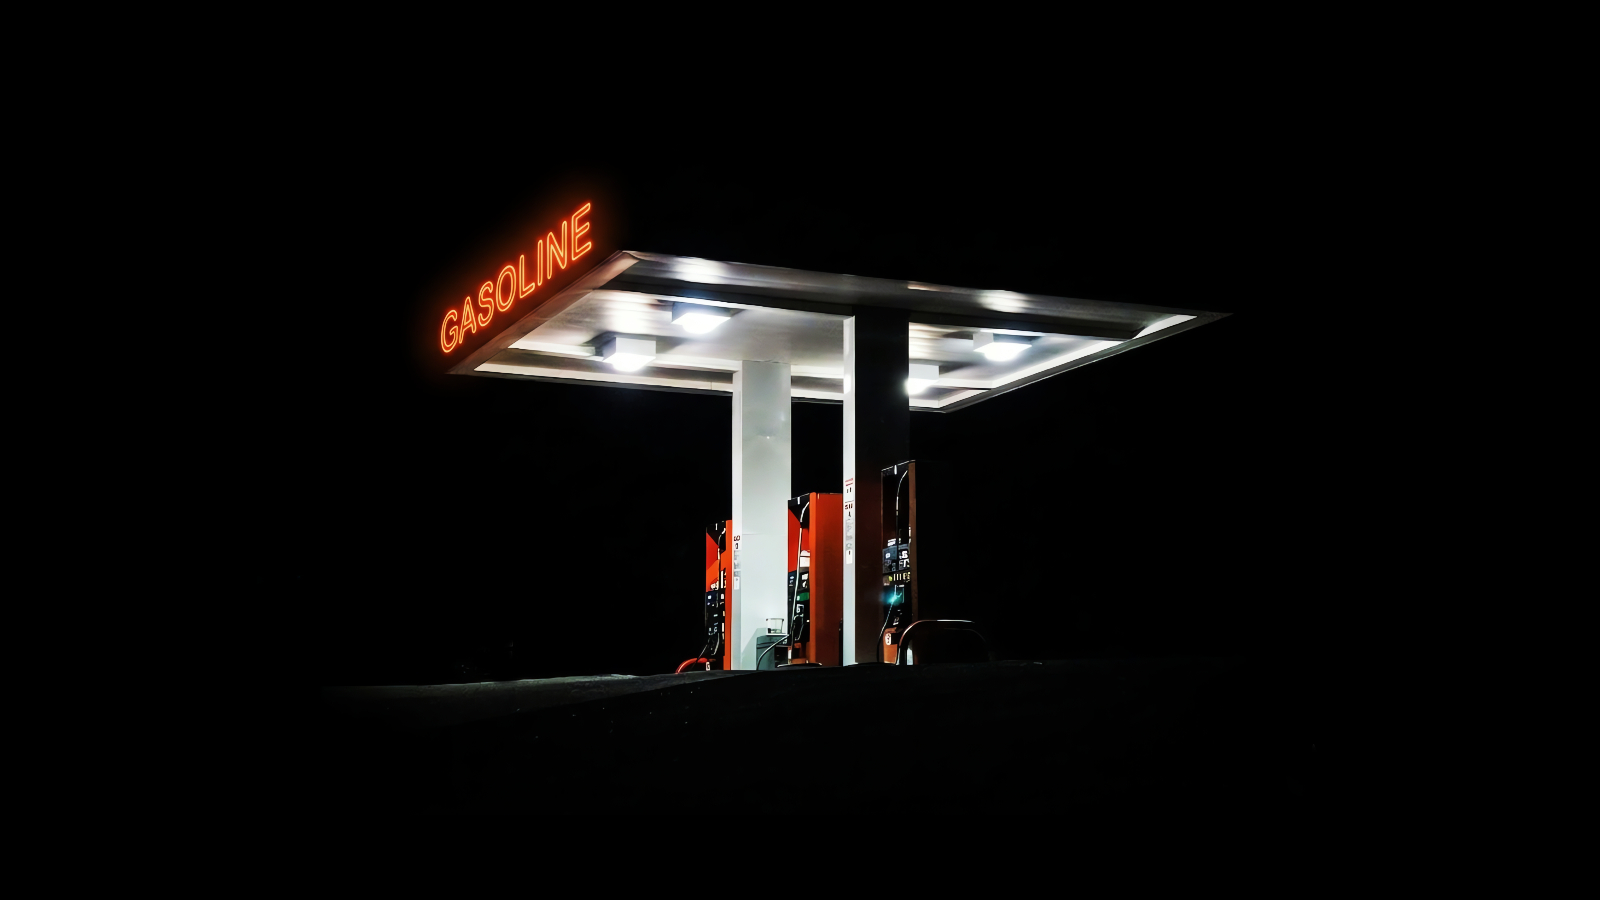
Over 900 automatic tank gauge (ATG) systems in the United States are exposed online and vulnerable to attacks that can alter settings, disable alerts, and disrupt fuel or chemical storage monitoring. U.S. agencies including CISA, the FBI, and the NSA warn organizations to secure these systems after reports linked some incidents to Iranian hackers targeting internet-facing industrial controls. #CISA #FBI #NSA #Shadowserver #IranianHackers #AutomaticTankGauge

Daily Recap, CISA and vendors warned of active exploitation and available proof-of-concept code tied to multiple high-risk issues, including Magento, Cisco Unified CM, and VS Code token theft, plus Android/Linux bugs, while a new HTTP/2 Bomb DoS technique can crash servers in under a minute. The day also covered rapid China-linked criminal activity using Atlas RAT, malspam abusing Google DoubleClick to deliver DesckVB RAT, Gemini prompt-injection risk via WhatsApp/Slack notifications, and further enforcement and policy updates involving Nobitex, fuel-tank monitoring targeting warnings, and CISA staffing planning.
#CISA #Magento #CiscoUnifiedCM #Vscode #GoogleDoubleClick #AtlasRAT #DesckVBRAT #WhatsApp #Slack #GoogleGemini #HTTP2Bomb #Nobitex

Google released Chrome 149 to the stable channel with fixes for 429 vulnerabilities, including several critical flaws in ANGLE and Network that could enable sandbox escape and code execution. The update also highlights a surge in Chrome bug discoveries, with Google paying large bug bounty rewards to external researchers and adjusting…