The French government said a breach of the Tchap encrypted messaging platform affected accounts tied to more than 73,000 public sector employees after an attacker used a compromised account. While private chats remained encrypted, the attacker accessed data from public chat rooms and reportedly claimed to have stolen messages, documents, and metadata from the platform. #Tchap #DINUM #CNIL #ANSSI
Category: Cyber Security News
CISA ordered U.S. federal agencies to patch the actively exploited Ivanti Sentry flaw CVE-2026-10520 within three days after it was added to the KEV Catalog under BOD 26-04. Shadowserver reported widespread exploitation attempts and likely compromise of unpatched Internet-exposed Ivanti Sentry gateways. #CVE-2026-10520 #IvantiSentry #CISA #Shadowserver #BOD26-04

European authorities have disrupted AudiA6, a large cryptocurrency laundering service that helped ransomware gangs and cybercriminals wash more than €336 million in illicit proceeds. The operation led to arrests, seizures, domain takedowns, and U.S. charges against the alleged administrators, while also exposing links to Dark2Web and major cases such as the…
Google confirmed that ShinyHunters exploited a critical PeopleSoft zero-day, CVE-2026-35273, to steal data from organizations before Oracle had patches available. The campaign primarily targeted higher education institutions, including the University of Nottingham, and involved compromised environments, custom tooling, and subsequent data leaks. #ShinyHunters #UNC6240 #CVE-2026-35273 #PeopleSoft #UniversityofNottingham…

Anthropic disputed claims that Claude Fable 5 was jailbroken, saying the alleged bypass did not defeat its independent classifier safeguards or produce dangerous assistance. The company said red-teaming, fallback controls to Claude Opus 4.8, and recent usage reviews showed no evidence of successful circumvention. #Anthropic #ClaudeFable5 #ClaudeOpus48 #PlinytheLiberator…
CISA has issued Binding Operational Directive 26-04 to force federal agencies to prioritize patching the most dangerous vulnerabilities, especially those in the Known Exploited Vulnerabilities catalog and on publicly accessible assets. The directive introduces tighter remediation timelines, expanded policy requirements, and a stronger focus on risk-based vulnerability management across federal networks….
Alert fatigue is overwhelming SOC teams because security tools generate too many low-context alerts, making it hard to distinguish real threats from noise. The article argues that the best path forward is better correlation, enrichment, and AI-assisted automation that adds context rather than simply reducing alerts. #Lanxit #SentinelOne #ArcticWolf #Darktrace #Presidio…
Oracle issued an out-of-band advisory for CVE-2026-35273, a critical PeopleSoft vulnerability that could allow unauthenticated remote code execution in PeopleSoft Enterprise PeopleTools 8.61 and 8.62. Reports also link the issue to ShinyHunters activity targeting hundreds of PeopleSoft instances across more than 100 organizations, with organizations such as the University of Nottingham…
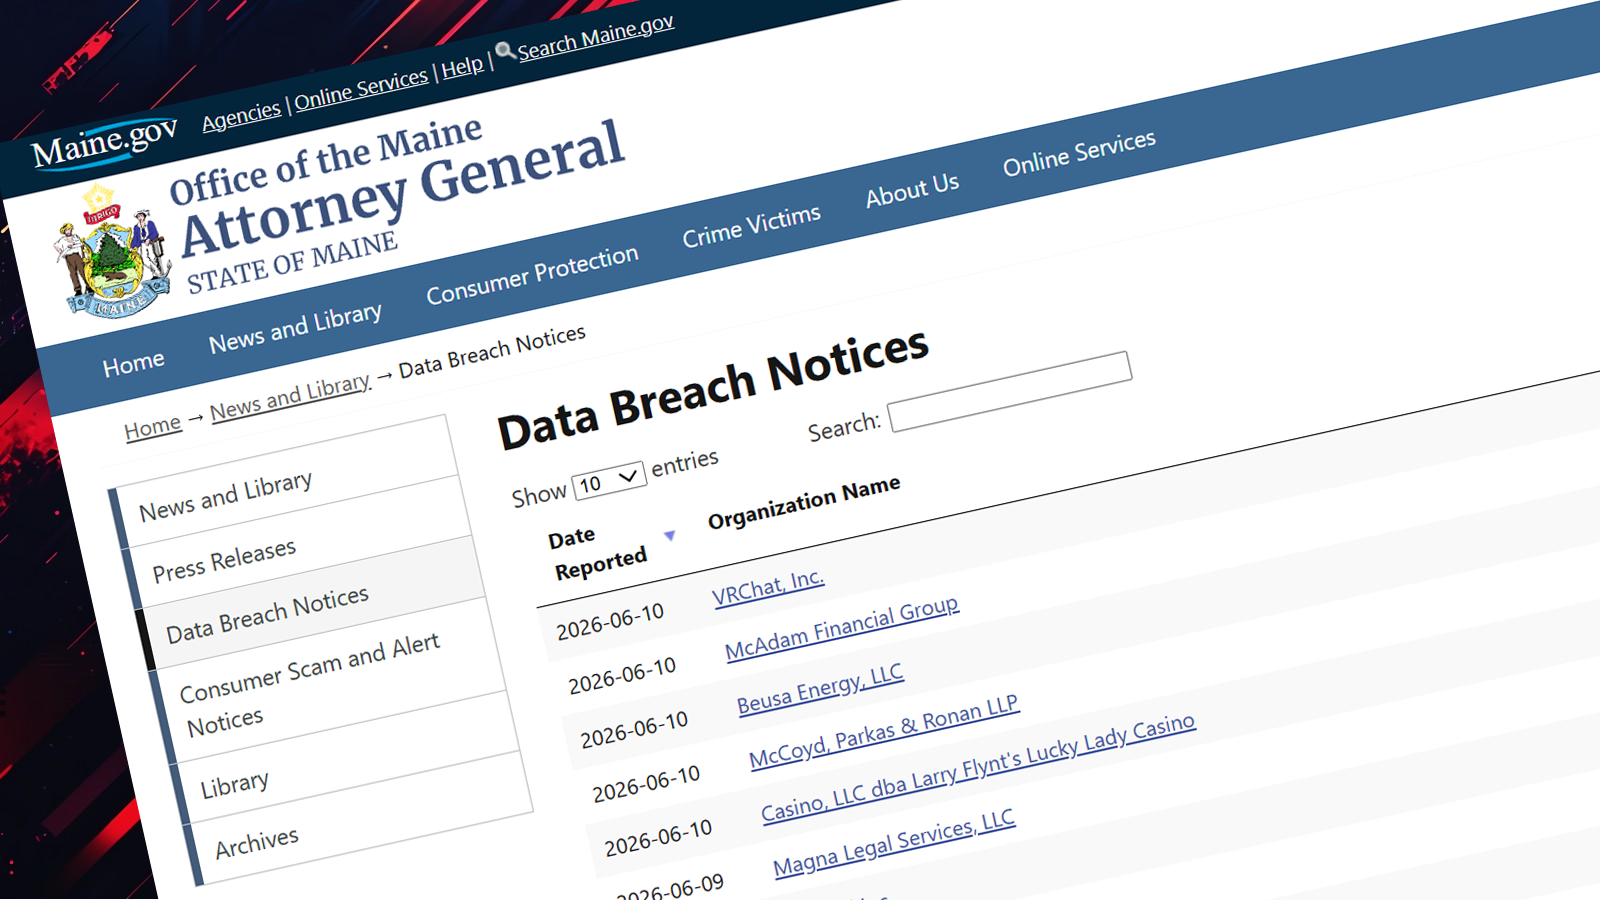
Fraudulent breach notices were posted to Maine’s official portal claiming major incidents at VRChat and Discord, but both companies denied the disclosures and said the filings were false. The cases show how unverified submissions can spread misinformation and damage reputations before anyone confirms a real breach. #VRChat #Discord #MaineAttorneyGeneral
Kyushu Electric Power Co., Inc. disclosed a physical security incident in which a missing external drive may have exposed private data for up to 10.9 million customer accounts. The drive contained customer names, service location addresses, electricity usage data, and phone numbers, and the company has notified authorities while investigating the loss. #KyushuElectricPower #JapanPersonalInformationProtectionCommission
Oracle is warning about a critical zero-day in PeopleSoft PeopleTools, tracked as CVE-2026-35273, which allows unauthenticated remote code execution and affects versions 8.61 and 8.62. The flaw has been used in ShinyHunters data theft attacks against more than 100 organizations, with Mandiant confirming active exploitation and Oracle releasing emergency mitigations. #Oracle #PeopleSoft #PeopleSoftPeopleTools #CVE-2026-35273 #ShinyHunters #Mandiant

Federal prosecutors have charged Russian national Denis Nikolayevich Obrezko with conspiracy to commit unauthorized computer access in connection with a cyber-espionage campaign linked to Void Blizzard, also known as Laundry Bear. Investigators say the group targeted U.S. and European organizations, using stolen session tokens, proxy services, and typosquatted Microsoft domains to steal data and conceal its activity. #VoidBlizzard #LaundryBear #DenisNikolayevichObrezko #MicrosoftEntraID

Daily Recap, Microsoft issued its June 2026 Patch Tuesday updates with a record 206 fixes and addressed multiple zero-days including YellowKey, GreenPlasma, MiniPlasma, and RoguePlanet, while also flagging potential issues installing some monthly updates on upgraded PCs. ServiceNow patched an already-exploited vulnerability and disclosed a customer data security incident, while Ivanti Sentry and Cisco SD-WAN faced high-risk flaws amid broader enterprise RCE and library vulnerability updates, including OpenSSL and Veeam Backup & Replication. #YellowKey #GreenPlasma #MiniPlasma #RoguePlanet #ServiceNow #Veeam #IvantiSentry #CiscoSDWAN #OpenSSL #Windows10 #Windows11

AI is accelerating cyberattacks by enabling faster phishing, automated reconnaissance, and quicker exploitation of account exposures, shrinking attacker timelines dramatically. For MSPs, fragmented security tools make it harder to respond, recover, and prove protection, while unified platforms like Kaseya 365 Endpoint offer a more efficient path forward. #Gartner #Verizon #Kaseya #Kaseya365Endpoint
Law enforcement has dismantled the AudiA6 cryptocurrency service, which allegedly laundered more than $380 million for ransomware actors and other cybercriminals. The operation was linked to more than 15 international investigations and led to arrests, seizures, and the exposure of a large money-mule network. #AudiA6 #Europol #Eurojust #Dark2Web #RuslanIgorevichTkachuk #AlexanderVladimirovichLedenev