
Google has filed a lawsuit against a Chinese cybercrime network accused of using Gemini to generate phishing pages and power large-scale smishing campaigns through the Outsider phishing-as-a-service kit. The operation allegedly impersonated trusted brands, victimized more than 100,000 people, and relied on Telegram-coordinated groups to steal financial and personal information. #Google…
Category: Cyber Security News

Attackers compromised more than 400 Arch User Repository packages and altered their build scripts to deliver the Atomic Arch credential stealer during package builds. The campaign also used the malicious npm package atomic-lockfile and a second wave involving js-digest, with some payloads able to install an optional eBPF rootkit and persistence…

SecurityWeek’s weekly roundup covers major cybersecurity developments, including allegations that IBM and AT&T covered up foreign government-linked hacks, a University of Oxford CareerConnect data breach, and new guidance from Microsoft for investigating incidents involving Microsoft 365 Copilot and Azure AI Services. It also highlights active exploitation of a LiteLLM flaw, a…
A 10-year-old authentication bypass in phpBB lets attackers log in as any user, including administrators, using a single HTTP request. phpBB fixed the issue in version 3.3.17, while 4.x users are still advised to upgrade immediately because no safe 4.x release is available yet. #phpBB #Aikido #HackerOne

Researchers say ShinyHunters exploited an Oracle PeopleSoft zero-day, CVE-2026-35273, to potentially breach more than 100 organizations, with higher education accounting for most of the exposed victims. Oracle has issued mitigation guidance but no patch yet, while victims such as the University of Nottingham have confirmed student data theft. #ShinyHunters #OraclePeopleSoft #CVE-2026-35273 #UniversityofNottingham
A former Conti member, Oleksii Oleksiyovych Lytvynenko, pleaded guilty in U.S. federal court to conspiracy to commit wire fraud for his role in ransomware attacks that targeted more than 1,000 victims worldwide. Prosecutors said he developed malware used by Conti, helped extort victims including entities in Tennessee, and faces up to 20 years in prison. #Conti #OleksiiOleksiyovychLytvynenko #CobaltStrike
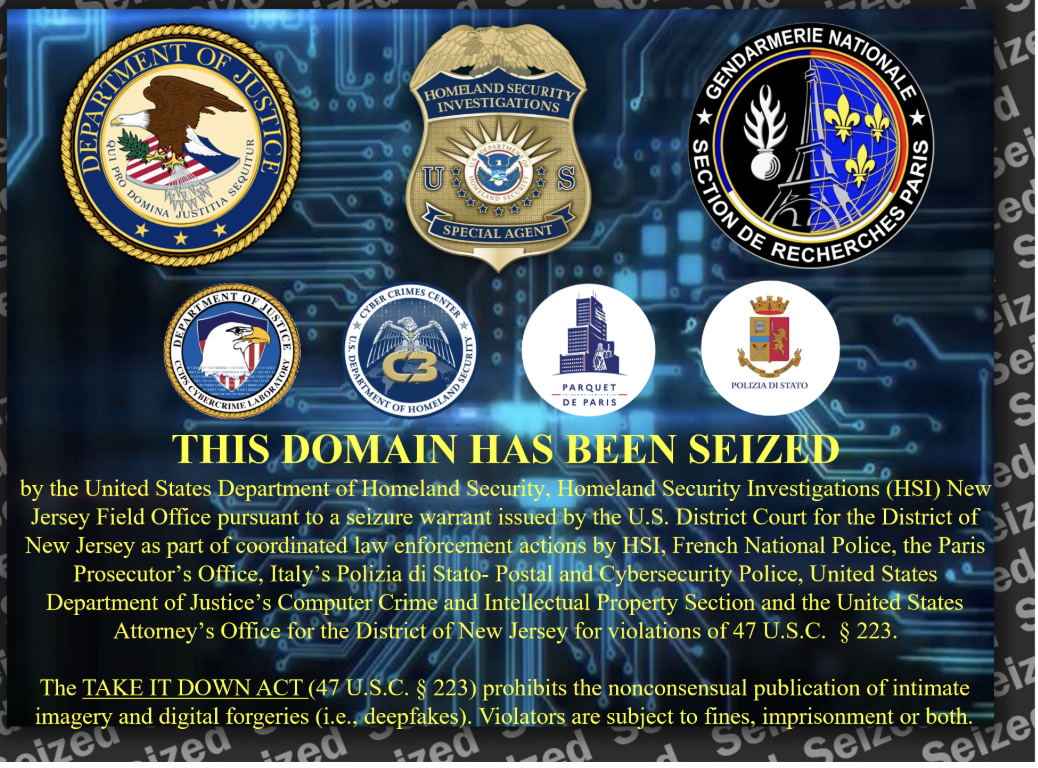
U.S. authorities seized CFAKE.com and SOCFAKE.com under the TAKE IT DOWN Act after accusing the sites of distributing thousands of AI-generated and digitally altered nude images and videos of women without consent. The operation involved coordination with law enforcement in France and Italy, where investigators arrested a suspected CFAKE administrator and linked the sites to large-scale deepfake porn activity. #CFAKE #SOCFAKE #TAKEITDOWNAct #PoliziaDiStato #ParisPublicProsecutorsOffice

Daily Recap, AI-driven attacks are straining MSP security stacks as tools like OnyxC2 Stealer promise “enterprise-grade” theft, while the Miasma worm source code was briefly leaked on GitHub. Separately, the China-linked JDY botnet expanded beyond 1,500 devices to conduct reconnaissance and target U.S. military networks, while OpenAI said a likely Chinese influence operation tried to use ChatGPT to stir debate on data centers. #OnyxC2 #OnyxC2Stealer #Miasma #GitHub #JDY #ChatGPT #OpenAI #U.S. military
Underground forum posts can reveal early signs of software supply-chain attacks long before a public incident, especially when they mention GitHub access, private repositories, source code, OAuth tokens, CI/CD data, or vendor-related leaks. Cases involving Vercel, Sportradar AG, TeamPCP, Mistral AI, Shai-Hulud, LiteLLM, and malicious VS Code extensions show how trusted developer tools, package ecosystems, and integrations can expose downstream systems and credentials. #Vercel #SportradarAG #TeamPCP #MistralAI #ShaiHulud #LiteLLM #VSCode
CyberCorps: Scholarship for Service has spent 25 years building a pipeline of nearly 5,000 cybersecurity professionals for the federal workforce, and it is now being updated to prepare students for AI-driven threats. Congress has stepped in to protect the program from proposed Trump administration budget cuts, while urging more AI training and additional scholarships to meet rising needs. #CyberCorps #ScholarshipforService #AI #NationalScienceFoundation

CISA has added CVE-2026-10520 in Ivanti Sentry to its Known Exploited Vulnerabilities catalog after reporting signs of exploitation, while Ivanti says the activity was only seen on honeypots. The flaw is a critical unauthenticated OS command injection issue that can lead to remote root code execution, and fixes are available in…

Handala, an Iran-linked threat actor, claimed it hacked California Water Service and leaked 5 gigabytes of data allegedly taken from the utility, including customer and administrative information. Dataminr says the intrusion likely began through Cal Water’s RTKBase GNSS platform before moving into the billing environment, and warns the exposed credentials should…
Anthropic has made Claude Fable 5 generally available, positioning it as a powerful Mythos-class AI model with built-in safeguards that downgrade risky cybersecurity and biology requests to Claude Opus 4.8. The release has sparked debate about tiered access, pricing, and whether models like Fable 5 and Mythos 5 will help defenders…
Novo Nordisk disclosed a data breach that exposed pseudonymized clinical trial patient information and personal details belonging to an undisclosed number of healthcare professionals. The company said the attackers copied non-public data from internal IT systems, but that the exposed trial data does not directly identify patients by name. #NovoNordisk
Microsoft fixed a known issue that caused Windows updates released since May 2025 to fail when installed through WUSA from a network share containing multiple .msu files. The problem affected Windows 11 24H2/25H2 and Windows Server 2025, and is now resolved in June 2026 cumulative updates for KB5079391 and KB5094125. #WUSA #KB5079391 #KB5094125