
Researchers have uncovered multiple ClickFix campaigns distributing the BabaDeda Loader, Lorem Ipsum Loader, and Potemkin loader to deliver stealers, RATs, and backdoors through deceptive PowerShell and browser-update lures. The campaigns show how threat actors are rapidly adapting delivery methods, leveraging compromised websites, DLL side-loading, and staged loaders to evade detection and…
Category: Cyber Security News

A flaw in the Google Cloud Vertex AI SDK for Python let attackers hijack model uploads by squatting on predictable Cloud Storage bucket names and swapping in malicious pickle or joblib models. Google patched the issue in version 1.148.0, and Unit 42 reported that it found no evidence of exploitation in…

Rokarolla is a new Android banking trojan that targets 217 banking and cryptocurrency apps and uses 137 commands to steal credentials, SMS data, contacts, and more. It spreads through fake Google Chrome and TikTok installers, impersonates Google Play Protect, and gives attackers extensive control over infected devices. #Rokarolla #Zimperium #GooglePlayProtect #GoogleChrome #TikTok
Aikido Security uncovered a coordinated campaign on the JetBrains Marketplace in which at least 15 plugins posed as AI coding and development tools while secretly stealing developers’ AI provider API keys. The plugins have been installed nearly 70,000 times and include items such as DeepSeek AI Assist and CodeGPT AI Assistant, with stolen keys sent to a hardcoded server. #JetBrainsMarketplace #AikidoSecurity #DeepSeekAIAssist #CodeGPTAIAssistant

Backslash Security found that Anthropic quietly patched more than 30 security-relevant issues in Claude Code between April and early June 2026, including data poisoning, prompt injection, arbitrary code execution, OAuth credential leakage, and a safeguard bypass for destructive commands. The report says the rapid release cadence of AI tools like Claude Code and OpenAI’s Codex creates short security gaps that force organizations to balance stability, performance, and protection. #Anthropic #ClaudeCode #OpenAI #BackslashSecurity
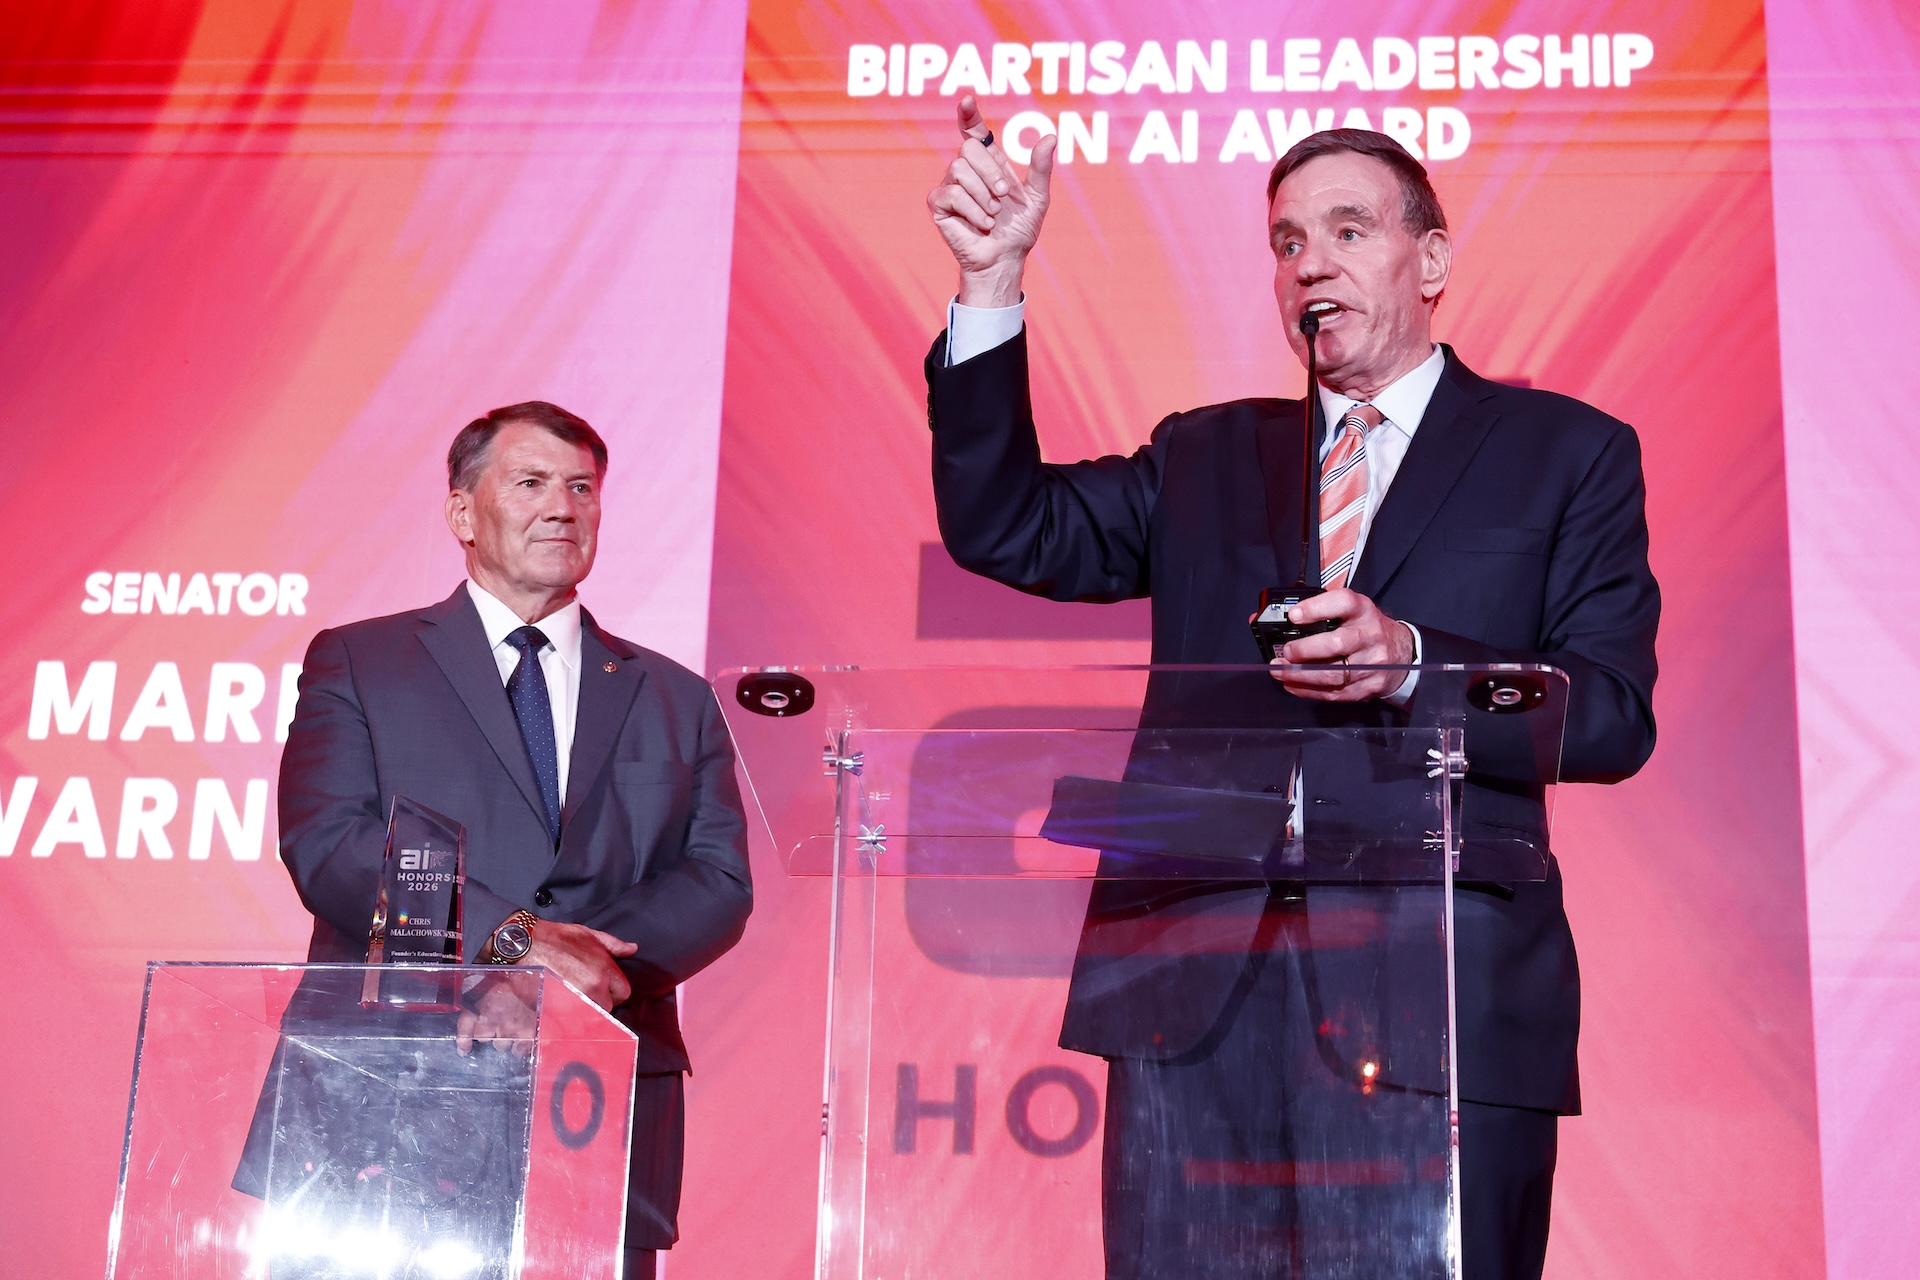
Members of Congress reacted with skepticism and caution after the Trump administration imposed export controls on Anthropic’s Fable 5 and Mythos 5 AI models. Lawmakers questioned whether the move was truly based on national security concerns or influenced by the administration’s disputes with Anthropic over domestic surveillance and autonomous weapons, with some still waiting for a full explanation. #Anthropic #Fable5 #Mythos5 #TrumpAdministration

Daily Recap, Fraud and phishing activity included the FBI disrupting an AI-powered phishing service using 1 million URLs and reporting crypto scams that relied on couriers, while MENA users faced Sniper Dz lures through fake Facebook offers and browser alerts. Across cloud and breach headlines, attackers turned Microsoft 365 Copilot into a 1-click data-theft mechanism, exploited a PAN-OS GlobalProtect VPN flaw, and hit platforms including REDCap, Infinite Campus, and Novo Nordisk, with ransomware cases and supply-chain intrusions also continuing. #FBI #Microsoft365Copilot #GlobalProtect #REDCap #InfiniteCampus #NovoNordisk #Ozempic #Conti #SniperDz #Misere #ShaiHulud #MiniShaiHulud #Miasma #Hades #UNKDeadDrop #GoFlateLoader
Magnitude has emerged from stealth with $10 million in seed funding led by Ballistic Ventures to build an autonomous AI workforce for third-party risk management. Its AI agents continuously assess vendor exposure, govern AI agents across external ecosystems, and help organizations respond to third- and Nth-party risks at the pace of…
Sri Lankan-born Isira Adithya began hacking as a curious child, experimenting with games, Wi-Fi, and hardware before turning his skills toward ethical bug bounty hunting. By discovering legal ways to test real-world systems, he built a successful career, funded his education, and became a first-class computer security graduate. #IsiraAdithya #TryHackMe #Intigriti…
iRhythm disclosed a cyberattack that led to the theft of sensitive information from third-party-hosted business applications, including potentially proprietary data and patients’ protected health information. The company says its clinical and medical device systems were not affected, while investigators work to determine the full scope of the breach. #iRhythm #Zio…
Threat actors are abusing Steam Workshop and Wallpaper Engine to hide malware inside malicious wallpaper packages that users download from Valve’s platform. These infected wallpapers have been used to steal Steam credentials, deploy backdoors like DarkKomet, and run other threats including Lumma, Vidar, cryptominers, botnet loaders, RanEngine, and ransomware. #SteamWorkshop #WallpaperEngine #Kaspersky #DarkKomet #Lumma #Vidar #Steam
A policy paper from the Institute for Security and Technology argues that AI software bills of materials (AIBOMs) could reduce cyber risk and improve transparency by creating a shared inventory of models and datasets used in AI systems. The authors say AIBOM policy needs both supply-side data collection and demand-side requirements, such as industry mandates, government regulations, or contracting conditions, before broad adoption can work. #AIBOM #InstituteForSecurityandTechnology #AllanFriedman #NickLeiserson
The FTC warned that Americans lost $3.5 billion to imposter scams in 2025, with fraudsters increasingly using social media, fake bank alerts, and impersonation tactics to trick victims into transferring money. The agency said business and government impersonators drove most losses, while enforcement actions under its Impersonation Rule have already stopped several schemes. #FTC #Facebook #WhatsApp #Instagram #MediaAlpha #AmericanTaxService #BlackstoneLegal #ClickProfit #AcceleratedDebtSettlement #InnovativePartners
GhostTree shows how NTFS junctions can be abused by any user to create recursive directory loops that make folder scans hang and leave malicious files unexamined. The technique was tested against Windows Defender and reported to Microsoft, highlighting how recursive file-system structures can evade endpoint scanning. #GhostTree #GhostBranch #NTFS #WindowsDefender #Microsoft #Varonis
The UK government plans to ban social media access for under-16s by requiring age verification on new accounts, with the rules set to take effect in spring 2027. Security and privacy experts warn the system can be bypassed with VPNs and could expose ID and biometric data to breaches while normalizing age checks for online access in the UK. #KeirStarmer #LizKendall #Ofcom #Instagram #YouTube #TikTok #Snapchat #Facebook #X #WhatsApp #Signal #Roblox #OnlineSafetyAct