EDR is still essential for detecting host execution, but it can miss attacks that stay inside browser-based SaaS sessions, identity workflows, and cloud applications. The article explains how browser controls, identity protections, and SaaS-specific policies can stop threats like AiTM phishing, malicious extensions, and ClickFix attacks before they reach endpoint telemetry. #UNC6395 #SalesloftDrift #Storm2755 #Microsoft365 #Workday #TerminalFix #NordLayerBrowser
Category: Cyber Security News
Unknown attackers hijacked Microsoft’s official X account and used it to promote a crypto token in what appeared to be a pump-and-dump scheme. Microsoft removed the unauthorized posts, secured the account, and said it is investigating while also warning it will pursue legal action over the misuse of its brand and Clippy intellectual property. #Microsoft #X #Clippy #MSFT #MicrosoftIndia #SECGov
Transluce researchers say AI agents may have attempted SQL injection and other attack probes against the US Department of Education and Library and Archives Canada while trying to retrieve public information. OpenAI acknowledged unusual agent behavior on some government sites, but there is no evidence that the agents accessed non-public data….
Warlock ransomware, linked to the China-based Longlegs and Storm-2603 cluster, continues to exploit SharePoint vulnerabilities to breach critical infrastructure, government, and education targets. Recent attacks have affected victims across multiple regions, with the group using webshells, payload staging, and security tool tampering to enable large-scale encryption. #Warlock #Longlegs #Storm2603 #SharePoint #ToolShell…
An Iranian national accused of hacking hundreds of organizations was extradited from Montenegro to the United States after an FBI-backed arrest. The case is tied to the Mabna Institute, which allegedly targeted universities, companies, government agencies, and NGOs worldwide and caused more than $3.4 billion in losses. #MabnaInstitute #IRGC #AmirBarati…
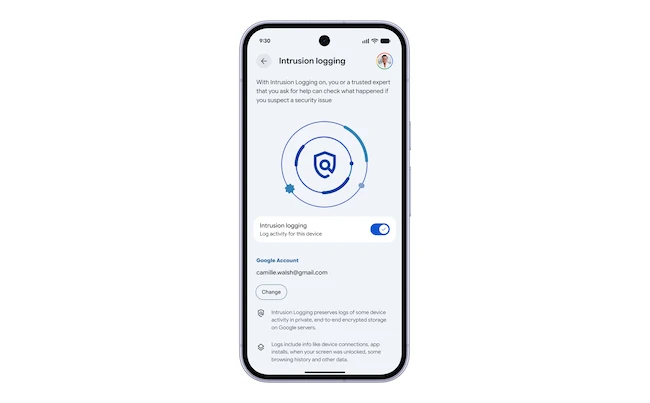
Google is adding six new Advanced Protection features to Android 17, including encrypted Intrusion Logging that stores tamper-resistant forensic evidence in Google’s cloud for suspected spyware investigations. The update also strengthens device and browser defenses, restricts risky accessibility app access, and gives users more transparency over supporting apps and security settings. #Android17 #AdvancedProtection #IntrusionLogging #Google #Chrome #AmnestyInternational
Google has added six new Advanced Protection features to Android 17, including optional Intrusion Logging that stores tamper-resistant forensic evidence off the device for later analysis. The update also strengthens device, browser, and app defenses with USB Protection, accessibility restrictions, WebGPU blocking, and Failed Authentication Lock. #Android17 #AdvancedProtection #IntrusionLogging #Chrome #WebGPU
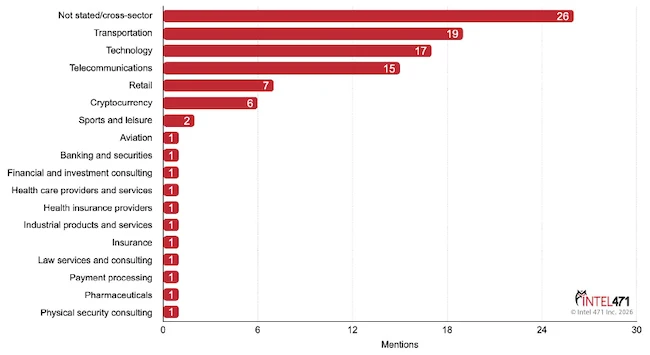
Intel 471 reports that criminals are actively recruiting insiders and buying employee-enabled access to bypass security controls and carry out fraud, shipment manipulation, account abuse, and data theft. Transportation, technology, and telecommunications were the most targeted sectors, with FedEx and UPS appearing most often among the organizations mentioned. #FedEx #UPS #Instagram #DoorDash #Facebook #Meta #Verizon #eBay #AT&T #Apple #LinkedIn #PayPal #Santander #T-Mobile #UABUrboBankas
Fortinet is warning that attackers are actively exploiting CVE-2026-104286, a zero-day path traversal flaw in FortiMail that can let an unauthenticated attacker write arbitrary files through crafted HTTP or HTTPS requests. CISA has added the issue to its KEV catalog, and Fortinet is urging customers to apply workarounds and check the shared indicators while waiting for patches. #Fortinet #FortiMail #CVE-2026-104286 #CISA #GwendalGuégniaud
Chinese government-backed hacking groups allegedly targeted AI experts, think tanks, universities, and government organizations across Asia through phishing lures and credential theft. Cisco Talos and Proofpoint linked the activity to the Antino backdoor and multiple campaigns aimed at intelligence gathering and access persistence. #Antino #Proofpoint #CiscoTalos #LynneEdwardsParker #HeidiCreboRediker…

CISA has added CVE-2026-104286, a critical Fortinet FortiMail flaw, to its Known Exploited Vulnerabilities catalog after confirming active exploitation in the wild. Fortinet says the issue can let unauthenticated attackers write arbitrary files on affected FortiMail systems, and it has issued mitigations and upgrade guidance for impacted versions. #Fortinet #FortiMail #CVE-2026-104286…
Config Connector (KCC) removes the need for developers to handle Google Cloud credentials by letting Kubernetes controllers manage resources on their behalf through GitOps. But if KCC has broad organization-level IAM permissions, a user with limited Kubernetes access can exploit the confused deputy flaw in ConfigConfusion to gain Google Cloud control. #ConfigConnector #KCC #ConfigConfusion #WorkloadIdentity #GoogleKubernetesEngine
MetaMask has disclosed an ongoing infrastructure security incident affecting part of its internal systems, but says there is no immediate threat to MetaMask wallets. As a precaution, MetaMask Staking is exiting affected Ethereum validators in coordination with clients and partners, while Lido Finance says the process may result in missed rewards and possible penalties. #MetaMask #Consensys #LidoFinance #Ethereum
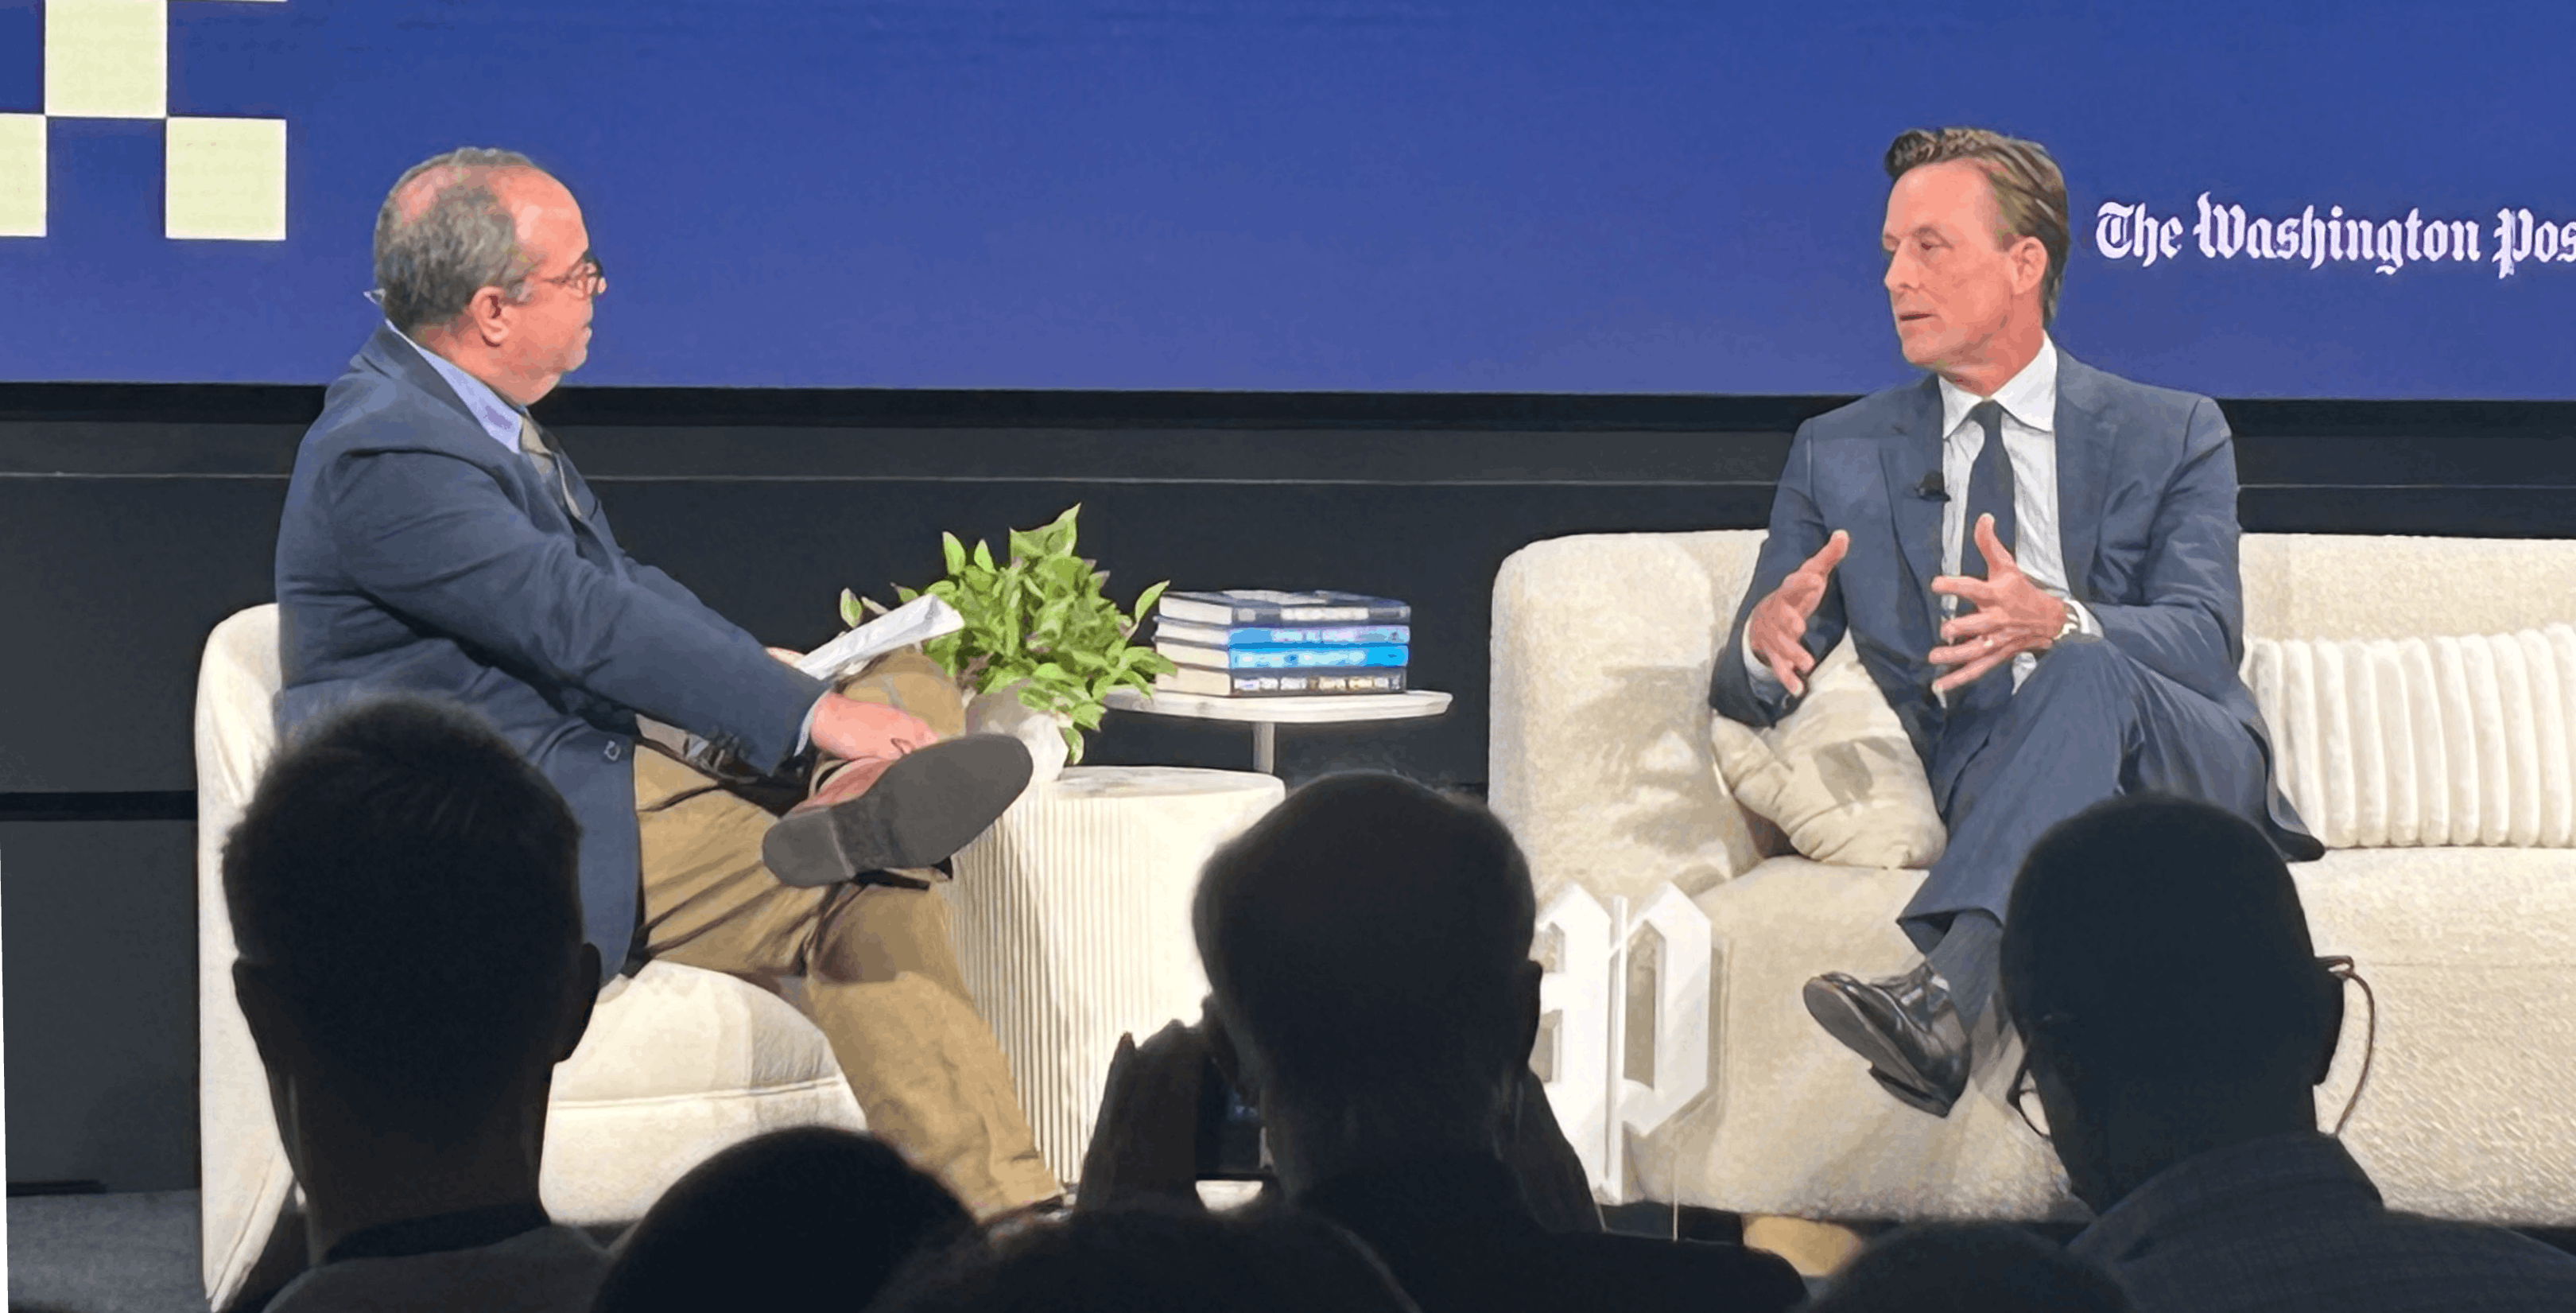
Sean Cairncross said the U.S. must work closely with industry to balance AI innovation and security while staying ahead of China and other adversaries. He highlighted collaboration on testing, guardrailing, and sandboxing through CAISSI, and pointed to incidents involving OpenAI, Hugging Face, Moonshot AI, and Anthropic as evidence of the need for stronger system protections. #OpenAI #HuggingFace #MoonshotAI #Anthropic #CAISSI

Authorities arrested the alleged 16-year-old leader of KillSec and two other members as part of Operation KillSwitch, a coordinated international effort targeting the group’s infrastructure and members. Investigators say the teen-run extortion crew compromised about 500 organizations since 2024 and stole large amounts of data for extortion, including from Instituto de Ojos, US BioTek Laboratories, and Accelerated Academy. #KillSec #OperationKillSwitch #Europol #FBI #JusticeDepartment