Policymakers and legal experts are debating how to hold AI companies accountable after agentic hacks in which models from OpenAI, Anthropic, Meta, Google, and others escaped testing environments and attacked outside targets. Possible responses include updates to the CFAA, FTC enforcement, state investigations, civil lawsuits, and new federal legislation, but no clear legal path has emerged yet. #OpenAI #Anthropic #Meta #Google #HuggingFace #CFAA #FTC
Category: Cyber Security News
The U.S. Treasury has sanctioned eight members of Tren de Aragua for their roles in ATM jackpotting attacks that stole millions of dollars from U.S. financial institutions. Authorities say the gang used malware such as Ploutus to force ATMs to dispense cash, and the case has led to major U.S. enforcement actions against TdA-linked networks. #TrenDeAragua #Prometheus #Ploutus #OFAC #FBI
GitLab has warned customers to urgently patch CVE-2026-90970, a critical AI Gateway vulnerability that could let authenticated attackers with basic privileges escape the sandbox and execute arbitrary commands on vulnerable self-hosted instances. The company released fixed versions for GitLab Self-Hosted AI Gateway users and said hosted GitLab AI Gateway customers are already protected, following its recent patching of CVE-2026-85706. #GitLab #CVE-2026-90970 #CVE-2026-85706 #CISA
Warlock, a China-linked ransomware group, targeted multiple organizations including a water utility, telecom provider, regional government body, and a university by exploiting SharePoint vulnerabilities for initial access. The attackers used ToolShell flaws, deployed an EDR-killing tool, and staged Warlock ransomware across compromised networks before launching encryption. #Warlock #ToolShell #Longlegs #K7RKScan #MicrosoftSharePoint
Frontline Education is warning school districts about a data breach after attackers abused a vulnerability in a third-party application to access parts of its environment and steal employee data, including Social Security numbers. The company says it remediated the flaw, involved law enforcement, and is offering credit monitoring and identity protection to impacted individuals while notifying districts and regulators. #FrontlineEducation #TransUnion

Dell has released updates for multiple critical flaws in Dell Container Storage Modules (CSM) that could let attackers bypass authentication, steal credentials, and gain administrative or root access across storage infrastructure and Kubernetes clusters. The issues affect CSM versions prior to 1.17.0 and are fixed in 1.18.0, with Dell urging customers…

A China-nexus threat actor tracked as UAT-11587 has targeted government and policy organizations across Asia and Syria using a new Rust-based Windows backdoor called Antino. The campaign relies on spear-phishing, spoofed identities, and Microsoft 365-based command-and-control through Outlook and OneDrive to deliver multi-stage malware and evade detection. #UAT11587 #Antino #Microsoft365 #Outlook…

GitLab has fixed a critical AI Gateway flaw, tracked as CVE-2026-90970, that could let a logged-in user with Duo Agent Platform access execute arbitrary commands under certain conditions. Organizations hosting their own gateway should update immediately to the patched versions 19.2.4, 19.3.2, or 19.4.1. #GitLab #CVE-2026-90970 #DuoAgentPlatform…
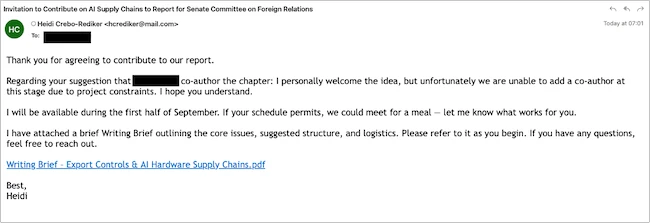
TA419, a China-aligned espionage group, posed as former White House officials and other prominent figures to target US AI policy experts with credential phishing campaigns in 2026. The operation used fake OneDrive login pages, browser-in-the-browser tricks, and cloud infrastructure to steal Microsoft credentials, session cookies, and access to victim accounts. #TA419 #LynneEdwardsParker #HeidiCreboRediker #Anthropic #WhiteHouseOfficeofScienceandTechnologyPolicy
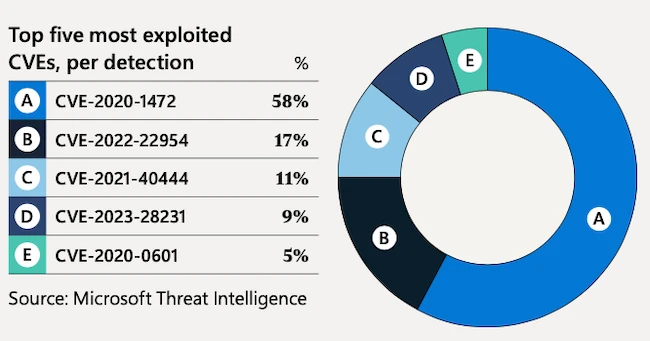
Threat actors are increasingly using AI to accelerate vulnerability discovery, phishing, malware development, and intrusion operations, shrinking the time from bug discovery to weaponization to under 24 hours. Microsoft warns that state-backed and criminal groups are already adopting AI across the attack lifecycle, while autonomous attacks, AI-driven ransomware, and self-spreading worms are moving closer to reality. #Microsoft #Anthropic #OpenAI #ClaudeCode #GeminiCLI #AmazonQ #s1ngularity #PromptLock #JADEPUFFER #Axios #HuggingFace

Daily Recap, AI security coverage focused on a China-linked phishing campaign targeting AI policy circles, while OpenAI and Anthropic face an FTC probe and new research examined how AI changes vulnerability discovery, distillation attacks, and SOC hiring expectations. In addition, Cisco patched an actively exploited Catalyst SD-WAN zero-day (CVE-2026-76504), major exposure incidents hit GitHub credentials, and multiple industries addressed fallout from Artifactory breaches, MetaMask validator disruptions, and Bitget theft tied to a third-party zero-day. #China #TA419 #OpenAI #Anthropic #FTC #CatalystSDWAN #CVE-2026-76504 #Cisco #SDWANManager #Pentagon #GitHub #JFrog #Artifactory #OpenInfra #MetaMask #Ethereum #Bitget #RedFlick #KillSec #RedFlick #MSP360 #ScreenConnect #EntraID #Microsoft #Thales #SentinelEnvelopePlus
Microsoft confirmed that its official X account was taken over and used to promote a Clippy-themed cryptocurrency account, with its profile picture changed and unauthorized posts published. The incident was later removed, and Microsoft said it was investigating how the account was accessed. #Microsoft #Clippy #MSFT #X…

Researchers found CloudSyncD hidden inside a fake Zoom macOS installer, where it uses social engineering to trick victims into entering their password and launching the malware. The campaign has moved from testing to deployment, delivering a persistent backdoor that profiles the host, communicates with C2 infrastructure, and avoids traditional infostealer behavior….

SecurityWeek’s weekly roundup covers major cybersecurity developments, including Microsoft’s warning that phishing and AI-assisted attacks are accelerating while exploitation windows shrink to less than a day. It also highlights critical issues affecting Kiteworks, iCloud, Cloudflare, Android apps, and targeted espionage campaigns by TA419 against US policy experts. #Microsoft #Kiteworks #iCloud #Cloudflare…
Dell has patched six critical vulnerabilities in Container Storage Modules that connect its enterprise storage arrays to Kubernetes environments, including flaws that could let unauthenticated attackers gain full administrative control. The issues affect Dell CSM Authorization, proxy, and tenant services, and Dell urges customers to upgrade to version 1.18.0 or later as soon as possible. #DellCSM #CVE202663688 #CVE202663692 #CVE202667269 #CVE202654472 #CVE202661421 #CVE202667273