Microsoft is blocking the KB5101650 Windows 11 security update on some Dell devices because it can trigger shutdowns, poor performance, excess heat, and battery drain. The problem stems from an incompatibility between the new Windows USB-C Connection Manager interface and the Intel Innovation Platform Framework Processor Participant driver, and Microsoft is working with Dell on a fix. #Dell #KB5101650 #KB5095093 #IntelInnovationPlatformFramework #Windows11
Category: Cyber Security News
CISA warned that attackers are actively exploiting three vulnerabilities in Internet-exposed on-premises Microsoft SharePoint Server instances to bypass authentication, execute code remotely, and steal IIS machine keys for persistence. The agency also highlighted additional SharePoint flaws that were patched by Microsoft, urging immediate patching, hardened configurations, and monitoring to protect affected servers. #CISA #MicrosoftSharePoint #SharePointServer #CVE-2026-32201 #CVE-2026-45659 #CVE-2026-56164
U.S. federal prosecutors have unsealed charges against three Russian nationals accused of running bulletproof hosting services that supported ransomware gangs and caused more than $62 million in damage worldwide. Media Land and ML.Cloud allegedly provided attack infrastructure to groups including LockBit, BlackSuit, and Play, while the U.S., U.K., EU, and Australia have also imposed sanctions and the State Department is offering a reward for information. #MediaLand #MLCloud #AleksandrVolosovik #YuliaPankova #KirillZatolokin #LockBit #BlackSuit #Play

Russian state-backed hackers are compromising internet-connected security cameras across Europe and Ukraine to collect intelligence on NATO military logistics and identify Ukrainian troops. Dutch intelligence agencies warned that the campaign uses exposed cameras and weak security to track military transport routes, weapons shipments, and troop movements, with some intelligence linked to…
SonicWall is urging customers to immediately patch SMA1000 secure remote access appliances after confirming active exploitation of two zero-day vulnerabilities, CVE-2026-15409 and CVE-2026-15410. The issues affect SMA1000 versions 6210, 7210, and 8200v, and organizations are advised to update to hotfix releases 12.4.3-03453 or 12.5.0-02835, with CISA also adding both flaws to…
Microsoft has released Windows 10 KB5099539, an extended security update that delivers the July 2026 Patch Tuesday fixes for 570 vulnerabilities, including two exploited zero-days and one publicly disclosed zero-day. The update also brings security hardening changes, bug fixes, and support for Windows 10 devices enrolled in ESU through October 12, 2027. #Windows10 #KB5099539 #PatchTuesday
A threat actor used hundreds of fake GitHub repositories impersonating legitimate software and security projects to spread an infostealer associated with BoryptGrab. The campaign targeted browser data, cryptocurrency wallets, messaging tokens, and other sensitive information while abusing trusted brands such as Arctic Wolf to lure victims. #GitHub #ArcticWolf #BoryptGrab
The Spanish Police dismantled a massive cybercrime and money-laundering network that generated €140 million through investment fraud and business email compromise attacks. The operation led to arrests in Spain, Portugal, and Panama, with Interpol and Europol helping to seize assets, freeze funds, and disrupt the scheme. #SpanishPolice #Interpol #Europol #BEC #CEOfraud #falseinvoicefraud
Finnish authorities have issued a wanted notice for Aleksanteri Kivimäki after the Supreme Court declined to hear his appeal, making his nearly seven-year conviction final in the Vastaamo extortion case. The case involved the theft and leak of sensitive psychotherapy records affecting about 33,000 patients and became Finland’s largest criminal case…
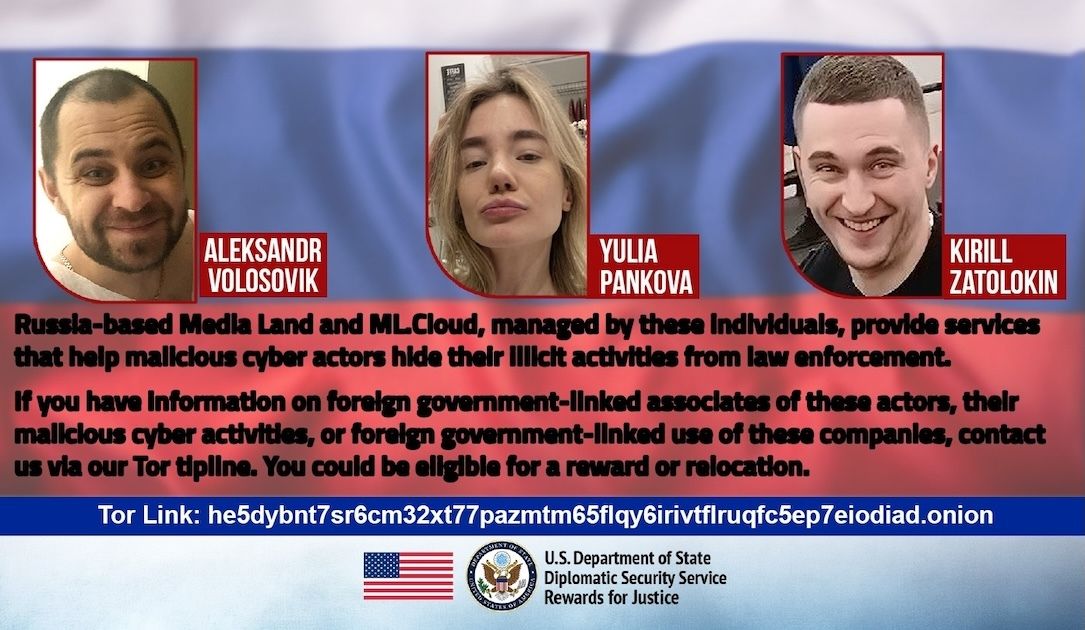
Federal prosecutors unsealed an indictment against three Russians tied to Media Land and ML Cloud, a sanctioned bulletproof hosting provider accused of supporting cybercriminal infrastructure and services. The case is linked to $62 million in losses, a $10 million reward, and criminal activity associated with LockBit, BlackSuit, Play, and stolen-card forums…

Claude for Chrome still contains two unresolved issues that let a script-capable browser extension trigger allowlisted tasks for Gmail, Google Docs, and Calendar through a forged click on claude.ai. Manifold Security says the current v1.0.80 build still accepts synthetic clicks and can enter skip-permissions mode from a URL, leaving users exposed…

The Trump administration has launched “Gold Eagle,” a new federal clearinghouse led by the Treasury Department to share AI cyber threat information between government and the private sector. The initiative is already collecting vulnerability intelligence and prioritizing patches, with support from CISA, DHS, the Department of Defense, and partners like Carnegie Mellon’s SEI. #GoldEagle #TreasuryDepartment #CISA #DHS #DepartmentOfDefense #CarnegieMellonUniversity #VINTS
The Spanish Police dismantled a money-laundering and fraud network that generated €140 million through investment scams and business email compromise attacks. The operation led to arrests in Spain, Portugal, and Panama, with investigators linking the group to large-scale “CEO fraud” and false-invoice fraud. #SpanishPolice #Interpol #Europol #BEC #CEOfraud
Researchers uncovered a ClickFix campaign on Artlist’s compromised subdomain new-blog.artlist[.]io, where attackers used a fake CAPTCHA to deliver a RAT through EtherHiding and a multi-stage malware chain. The intrusion began with an August 2023 infostealer infection on a freelance WordPress developer’s machine, which exposed privileged Artlist credentials that were later abused to inject malicious code.
#Artlist #new-blog.artlist.io #auth-code-check.info #EtherHiding #ClickFix #HudsonRock #Vidar #StealC

SAP’s July 2026 security updates fix multiple critical flaws, including CVE-2026-44747 in SAP NetWeaver Application Server ABAP, which could lead to memory corruption and unauthorized access. The patch set also addresses request smuggling in SAP Approuter and default-credential exposure in SAP Commerce Cloud tied to sample OAuth 2.0 client settings from…