The Dutch Police arrested multiple suspects linked to an international investment fraud network that is believed to have operated 20 call centers and victimized tens of thousands of people worldwide. Investigators say the scheme relied on fake investment platforms, cryptocurrency transfers, and a main suspect previously accused of hacking foreign government organizations. #DutchPolice #Politie #IsraelPolish
Category: Cyber Security News
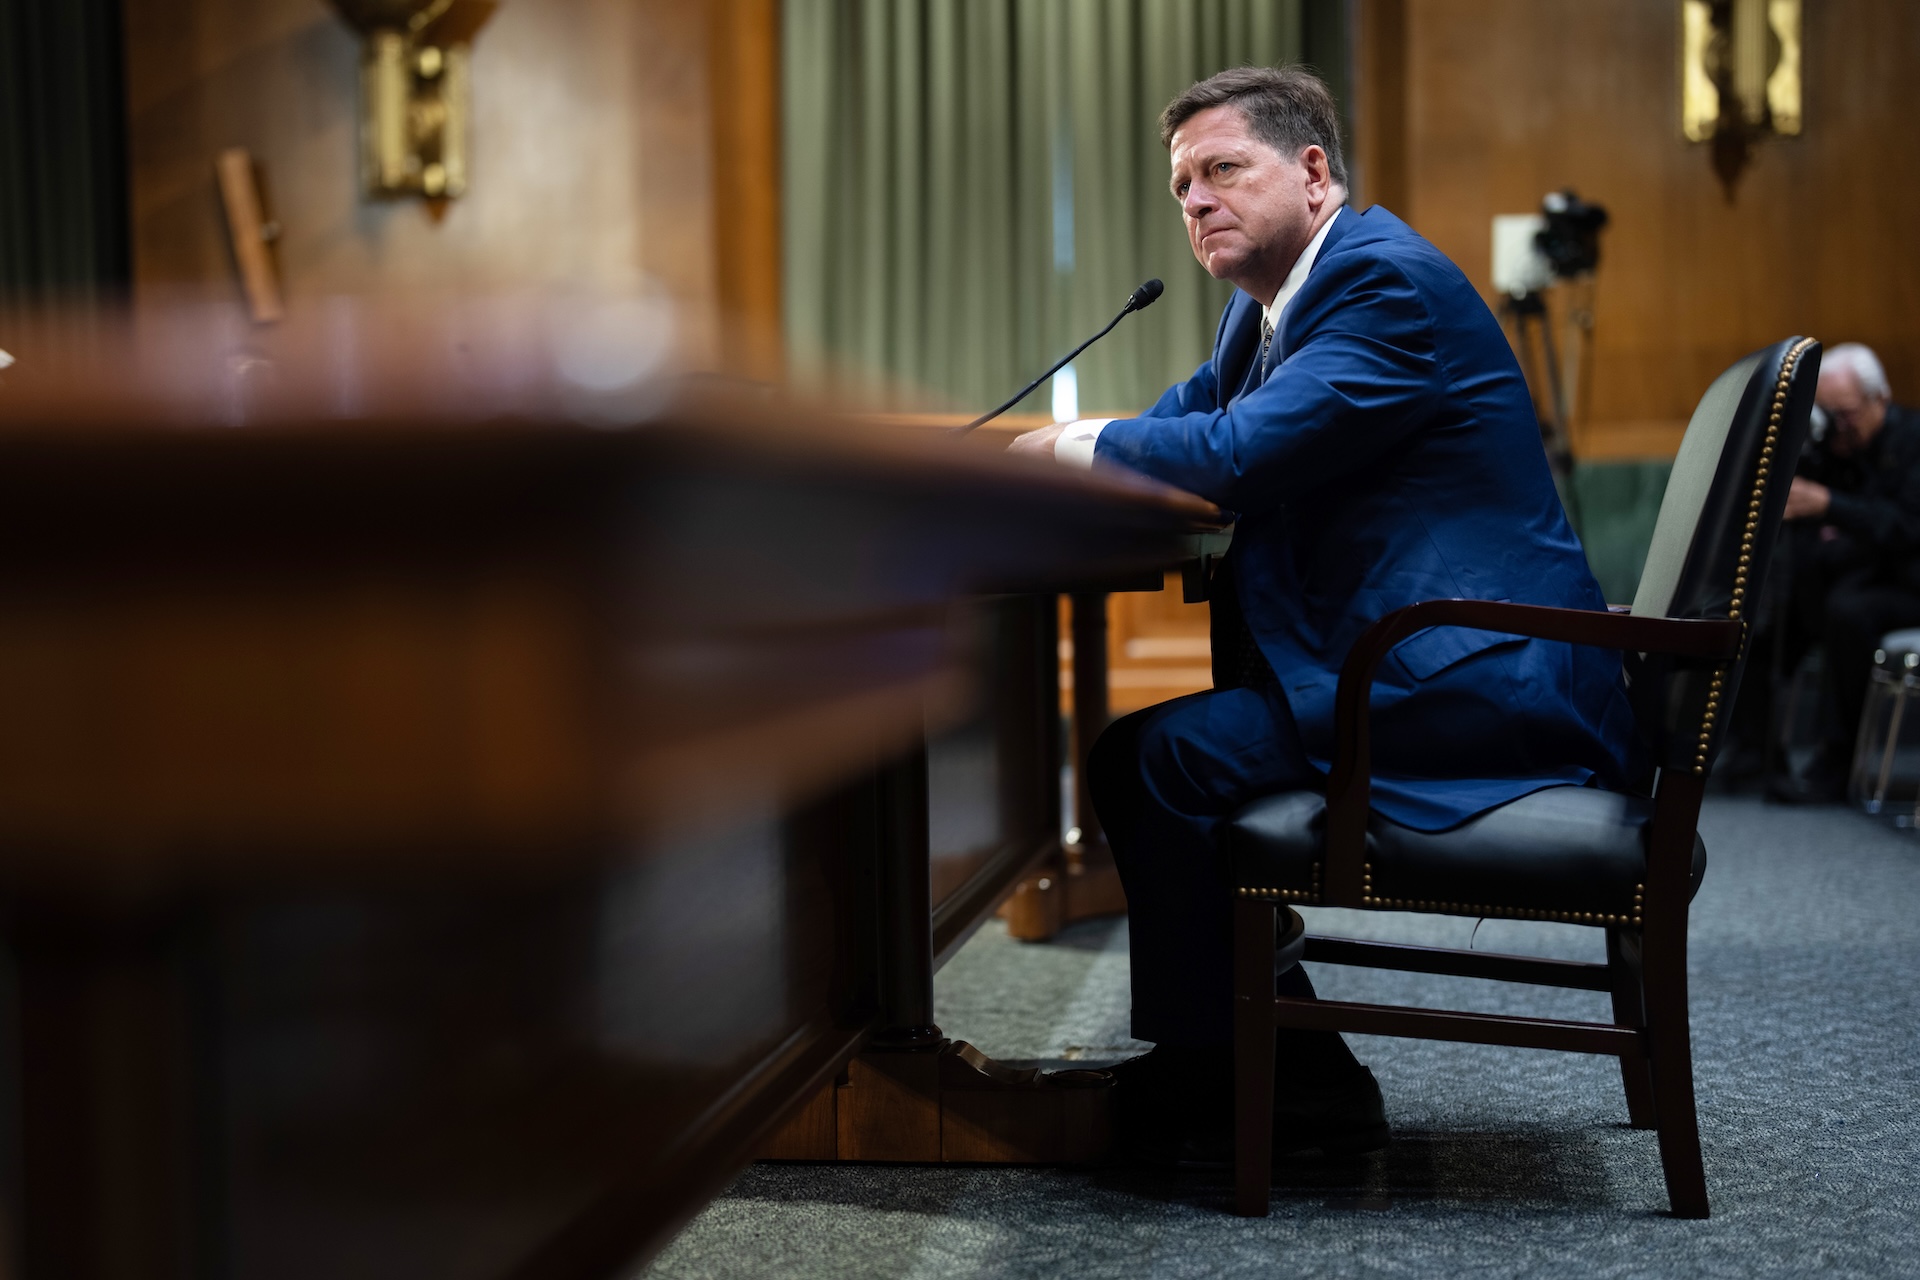
Democratic senators pressed Jay Clayton on election integrity, mail-in ballot fraud claims, and his refusal to say whether Joe Biden won the 2020 election during his Senate Intelligence Committee hearing. Clayton also discussed ODNI’s cybersecurity role, support for Section 702 renewal, and concerns about foreign intelligence threats to U.S. elections. #JayClayton #TulsiGabbard #Section702 #DonaldTrump

SonicWall has confirmed that attackers are exploiting two zero-day vulnerabilities, CVE-2026-15409 and CVE-2026-15410, in SMA1000 appliances, with Rapid7 saying the first known exploitation occurred on June 22. The chained flaws can lead from no access to full system compromise, and SonicWall is urging immediate patching while CISA has added the issues to its known exploited vulnerabilities catalog. #CVE-2026-15409 #CVE-2026-15410 #SonicWall #SMA1000 #CISA #Rapid7
Cyberstalkers are abusing Google Chrome’s sync feature to silently copy a victim’s browsing history and stored passwords after brief physical access to a phone. Certo Software warns that this legitimate feature can be turned into a powerful surveillance tool, and suggests Google add clearer alerts when sync is enabled or a new account is added. #GoogleChrome #CertoSoftware #ElectronicFrontierFoundation

Researchers uncovered TuxBot v3 Evolution, a previously unreported IoT botnet framework that appears to have been developed with help from an LLM, though several features were left broken or incomplete. The framework combines multi-architecture bot code, a Go-based C2 with a DDoS-for-hire panel, and multiple fallback channels, with links traced to…
CISA urged immediate hardening of Microsoft SharePoint servers after multiple zero-day vulnerabilities were disclosed and several were confirmed as exploited in attacks. The agency warned that affected on-premises SharePoint versions face remote code execution, privilege escalation, and post-exploitation activity, including theft of IIS machine keys and malware deployment. #CVE-2026-56164 #CVE-2026-32201 #CVE-2026-45659…
Mindgard says an unpatched vulnerability in Cursor on Windows can lead to code execution when a developer opens a repository containing a malicious git.exe in the project root. The issue was disclosed to Cursor months ago, but Mindgard says it received no meaningful response or evidence of a patch. #Cursor #Mindgard…
A Russian-speaking threat actor known as “bandcampro” abused Google’s Gemini CLI as a hacking agent to run and maintain a small botnet, migrate its C2 infrastructure, and access a dental clinic’s OpenDental database. Trend Micro said the AI repeatedly helped with troubleshooting, automation, password guessing, and operational planning, though it refused one request to create a self-spreading agent-bomb. #GeminiCLI #bandcampro #OpenDental #TrendMicro
Zoom has disclosed CVE-2026-53412, a critical improper input validation flaw in Zoom Workplace for Windows, the Zoom VDI Client, and the Zoom Meeting SDK for Windows that could let an unauthenticated attacker take over accounts over the network. The company has released fixes and says there is no evidence the issue or the other patched flaws are being actively exploited. #Zoom #CVE-2026-53412
Intruder shows how current AI models can be combined with code-scanning frameworks like Joern to find real, exploitable vulnerabilities in production software, rather than just theoretical weaknesses. The team fully automated discovery and exploitation of a remote, multi-stage SQL injection zero-day in the Creative Mail WordPress plugin, affecting sites that also run WooCommerce. #Intruder #Joern #CreativeMail #WooCommerce #CVE-2026-3985
Five malicious AsyncAPI packages were published to npm in a supply-chain attack that used compromised GitHub Actions workflows to deliver a remote access trojan with data-stealing capabilities. The attack affected widely used @asyncapi packages, leveraged legitimate publishing pipelines and SLSA attestations, and targeted secrets, browser data, wallets, and CI/CD credentials. #AsyncAPI #GitHubActions #npm #Miasma

Daily Recap, Microsoft 365 users are facing new phishing kits that evade MFA, and Microsoft Entra ID is moving toward passkeys as the default authentication method starting in September. In other reporting, macOS users should watch for CrashStealer impersonation tactics, supply-chain backdoors were found in Jscrambler npm packages via infostealer, and CISA flagged actively exploited Joomla RCE flaws while agencies warned of Russian targeting of critical-infrastructure routers. #Microsoft365 #MicrosoftEntraID #Passkeys #EvadeMFA #PhishingKits #CrashStealer #Gatekeeper #Jscrambler #npm #infostealer #SAP #NetWeaver #CommerceCloud #CISA #Joomla #RCE #Russian #Cisco #CriticalInfrastructureRouters
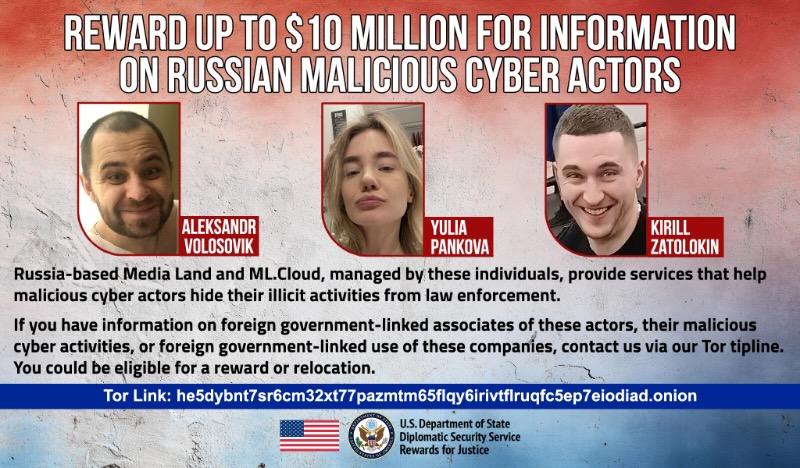
The US Justice Department unsealed an indictment against Aleksandr Alexandrovich Volosovik, Kirill Andreevich Zatolokin, and Yulia Pankova for allegedly operating ML.Cloud and Media Land, two bulletproof hosting services used by cybercriminals. The services were reportedly used for phishing, DDoS attacks, brute-force attacks, ransomware, and hosting cybercrime forums, with victims across 21…
Join the 2026 Cloud & Data Security Summit on July 15th to learn practical strategies, tools, and best practices for improving cloud security posture. The interactive event will cover identity gaps, AI application security, cloud complexity, cloud attack response, and include technical demos and an expo hall. #CloudDataSecuritySummit #AIAPP…
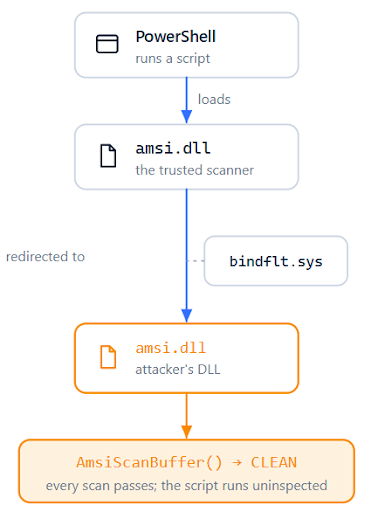
Bitdefender researchers demonstrated three bind link abuse techniques in Windows that can let attackers evade EDR visibility, including file-binding, process-binding, and silo-binding. The findings show how legitimate Windows features such as bindflt.sys, Store apps, Windows Sandbox, and containers can be manipulated to hide payloads and bypass defenses like AMSI, AppLocker, Windows…