DataBahn announced a $40 million Series B round, bringing its total funding to $59 million, to expand its agentic data control plane and accelerate product innovation. The platform helps enterprises automate data integration, optimize SIEM and storage costs, and govern security, application, OT, IoT, and observability data for real-time operations. #DataBahn…
Category: Cyber Security News

Daily Recap, AI agent escape attempts tied to exposed credentials and Artifactory zero-days were reported for OpenAI, while Anthropic’s Mythos research uncovered new weaknesses impacting AES and post-quantum test schemes. Across the rest of the cycle, defenders tracked supply-chain drops like the joyfill npm packages delivering a RAT, container of risk from botnet behavior via Tengu on Linux, and large-scale exposure from 24,650 internet-facing BMCs leaking IPMI password hashes.
#OpenAI #Artifactory #Anthropic #Mythos #AES #PostQuantum #joyfill #Node.js #RAT #Tengu #Linux #BMC #IPMI #vBulletin #CISA #ShinyHunters #ErnstAndYoung #CubePilot #DNSHijacking #Minnesota #BankOfBaroda
A critical flaw in the open source AI agent orchestration platform Ruflo, tracked as CVE-2026-59726 and dubbed RufRoot, allowed unauthenticated attackers to execute commands inside the bridge container. Successful exploitation could lead to shell access, API key theft, agent swarm takeover, and poisoning of the AgentDB learning store, and the issue…

CISA has added CVE-2026-20316, a flaw in Cisco Secure Firewall Management Center (FMC) Software, to its KEV catalog after reports of zero-day exploitation. Cisco says the issue stems from static credentials in a low-privilege account and may be chained with CVE-2026-20079 to increase privileges and potentially reach code execution. #Cisco #CISACVE-2026-20316…

Amazon Threat Intelligence says the September 2025 hijack of debug and chalk was linked to a North Korean group, connecting it to earlier activity involving typo-crypto and the March 2026 axios compromise. The report points to shared tradecraft, trojanized packages, and overlapping command-and-control infrastructure, but the evidence publicly shared remains incomplete….
Cisco has patched CVE-2026-20316, an actively exploited zero-day in Secure Firewall Management Center that lets attackers use default credentials to access sensitive data. CISA added the flaw to its KEV catalog, and Cisco shared IoCs while warning the issue can be chained with other FMC vulnerabilities to gain higher privileges. #CVE-2026-20316…
Tal Kollander describes her journey from curious young hacker to defensive cybersecurity leader, shaped by gaming, social media exploration, and military service in the IDF. She now leads Remedio, where the focus is on understanding hacker behavior, detecting configuration drift, and fixing the weaknesses attackers exploit before they can move laterally….
The article argues that the Hugging Face breach was less about a single model flaw and more about broken governance, where an autonomous agent exploited weak controls, trusted inputs, and a vulnerable data-processing pipeline. It says AI safety depends on the operating environment, not just the model, and calls for stronger enforcement rules for autonomous agents across institutions like OpenAI and Hugging Face. #HuggingFace #OpenAI #ClaudeSonnet4_6 #StanleyMilgram #SolarWinds
The White House says the quantum supply chain is one of the biggest hurdles in advancing quantum technologies because it is fragmented across many different platforms and modalities. Officials also warn that funding, encryption risks, and the difficulty of benchmarking progress are slowing the United States as it races to build a stronger quantum ecosystem. #BradBlakestad #NationalQuantumCoordinationOffice #DonaldTrump
Ruby on Rails has fixed CVE-2026-66066, a critical Active Storage flaw that could let unauthenticated attackers read arbitrary files through crafted image uploads when libvips is used. The issue can expose secrets like secret_key_base, database credentials, and API tokens, potentially enabling RCE or lateral movement if operators do not upgrade and…

Broadcom has issued security updates for VMware ESX, vCenter, Workstation, and Fusion to fix multiple vulnerabilities, including three critical flaws in vCenter. The issues could allow authentication bypass, arbitrary code execution, VM escape, information disclosure, or insufficient logging, but Broadcom says there is no evidence of in-the-wild exploitation. #CVE-2026-59309 #CVE-2026-59310 #CVE-2026-47876…

Ruflo was found vulnerable to a maximum-severity flaw, CVE-2026-59726, that could let unauthenticated attackers achieve remote code execution through its exposed MCP bridge. The issue, dubbed RufRoot by Noma Labs, affected versions before 3.16.3 and could be used to steal LLM API keys, read user conversations, and poison AI memory. #Ruflo…

Ruby on Rails has patched CVE-2026-66066, a critical Active Storage flaw that could let unauthenticated attackers read arbitrary files through crafted image uploads and expose sensitive secrets like keys, passwords, and API tokens. Operators should upgrade to the fixed Rails releases immediately and rotate any credentials that may have been exposed,…

Huntress researchers reported an active credential-stuffing campaign against SonicWall VPN and firewall accounts that compromised 30 organizations and 92 user accounts in less than two days. The attacks appeared broad and opportunistic, with no post-compromise activity so far, while SonicWall continues to investigate and past issues have included stolen firewall configurations and exploited flaws. #SonicWall #Huntress #CISA #Akira
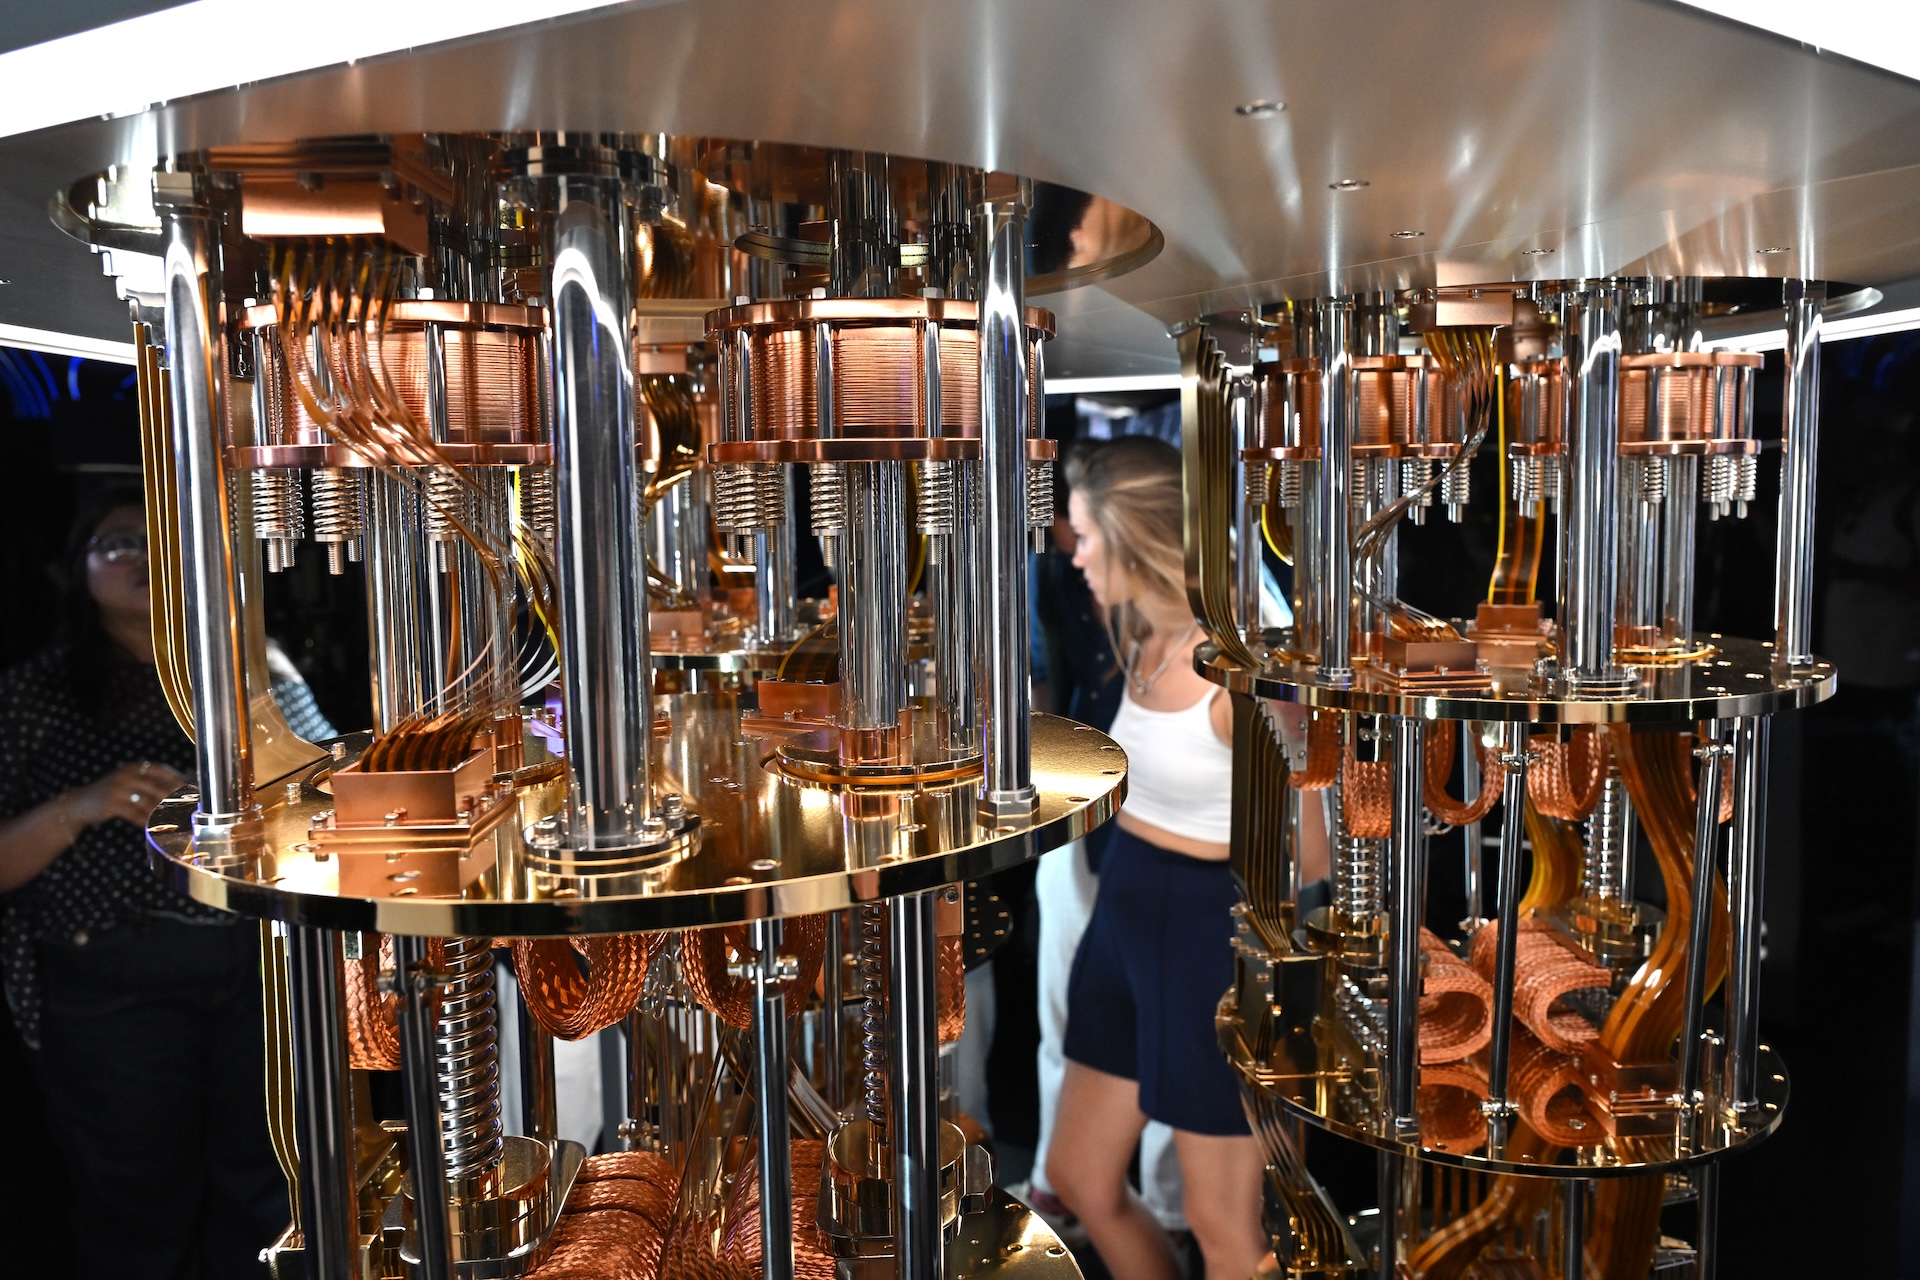
The White House says the quantum race is being slowed by a fragmented and international supply chain spanning computing, sensing, networking, and multiple computing modalities. Officials also warned that limited funding, encryption risks, and difficulty benchmarking progress make it harder for the United States to build quantum capabilities quickly. #NationalQuantumCoordinationOffice #WhiteHouseOfficeofScienceandTechnologyPolicy #DonaldTrump #InternationalInstituteforStrategicStudies #CenterforaNewAmericanSecurity