
Bank of America plans to acquire UK-based information security consultancy MDSec Consulting Limited, with the transaction expected to close in the fourth quarter of 2026 pending regulatory approvals. The deal will strengthen Bank of America’s presence in northern England and give it access to MDSec’s team of around 65 security professionals….
Category: Cyber Security News
CISA is warning water and wastewater system operators to secure internet-exposed PLCs after a surge in attacks on OT across the sector, including incidents that mirrored disruptions seen in Minnesota. The agency advises immediate steps such as removing exposed controllers from the internet, enforcing strong access controls, and reviewing activity linked…
Threat actors tracked as STAC4749 used Microsoft Teams calls to impersonate IT support staff and trick employees into granting remote access, leading to attacks on dozens of North American organizations. At least three intrusions resulted in Chaos ransomware deployment, with one case reaching file encryption in under 17 hours. #STAC4749 #MicrosoftTeams #ChaosRansomware

North Korea-linked threat actors launched a macOS malvertising campaign that uses a fake full-screen update page and ClickFix-style clipboard abuse to trick victims into running malicious Terminal commands. The campaign, tied to Contagious Interview and EtherHiding, delivers a Node.js backdoor, an info stealer, and a malicious Chrome extension targeting cryptocurrency wallets…
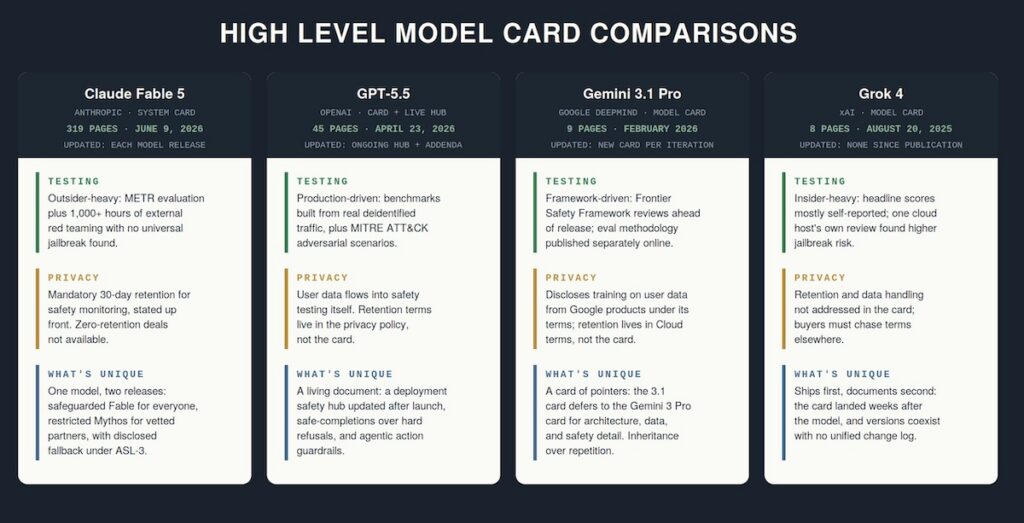
AI compliance should move away from bloated questionnaires and toward concise, evidence-based checklists that can be answered with logs, configs, eval reports, and other artifacts. The article argues that standardized model cards, risk-tiered assessments, and reusable controls can help organizations satisfy the EU AI Act, ISO/IEC 42001, and NIST AI RMF…
Okta has signed a definitive agreement to acquire Permiso Security, a cloud-native identity security platform focused on detecting threats across human, non-human, and agentic identities in multi-cloud environments. The acquisition will expand Okta’s identity security capabilities into ITDR and SOC operations, while integrating Permiso’s P0 Labs and threat research into Okta’s…
Brinks Home disclosed that attackers breached some of its systems and are threatening to leak stolen data, though its alarm monitoring and system functionality were not affected. ShinyHunters claimed responsibility for the intrusion and said it used a Microsoft Entra vishing attack to steal Salesforce and customer support data, while Brinks Home continues to investigate. #BrinksHome #ShinyHunters #MicrosoftEntra #Salesforce #Cresta
Broadcom has issued emergency patches for five VMware vulnerabilities affecting vCenter, ESX, Workstation, and Fusion, including three critical flaws that could let attackers bypass authentication, execute code, or escape a virtual machine to the host. Administrators of VMware Cloud Foundation, VMware vSphere Foundation, and VMware Telco Cloud products should update immediately, as Broadcom says there are no workarounds and no evidence of active exploitation yet. #Broadcom #VMware #vCenter #ESX #VMXNET3 #VMwareCloudFoundation #VMwarevSphereFoundation #VMwareTelcoCloudPlatform #VMwareTelcoCloudInfrastructure
Amazon linked a series of npm supply-chain compromises involving typo-crypto, debug, chalk, and axios to the North Korean Sapphire Sleet threat actor, also known as BlueNoroff and Stardust Chollima. The campaign used social engineering, malicious package updates, and evolving stealth techniques, while Amazon also backed community defenses and the Akrites initiative. #SapphireSleet #BlueNoroff #StardustChollima #npm #axios #debug #chalk #typo-crypto #OpenSSF #Akrites

A 41-year-old Ghanaian national, Derrick Van Yeboah, was sentenced to 85 months in prison for helping steal more than $10 million from vulnerable victims through romance scams. He was a high-ranking member of a Ghana-based criminal organization linked to over $100 million in losses and was extradited to the United States after his arrest in Ghana. #DerrickVanYeboah #JusticeDepartment #SouthernDistrictofNewYork
The article warns that U.S. troops remain exposed to telecom-based attacks because commercial cellular networks are still vulnerable to signaling abuse that can expose locations, intercept communications, and disrupt service. It calls on carriers, Congress, regulators, and the Pentagon to tighten oversight, improve defenses, and provide more secure mobile service for servicemembers. #Iran #Russia #China #SaltTyphoon #Spiral4
A Huntress investigation shows how an attacker used a SQL injection flaw to gain access, then spent time entrenching on the system by enabling Remote Desktop, creating admin users, disabling Windows Defender, and deploying BadIIS and XMRig. The case highlights that post-breach cleanup is not enough unless defenders also fix the original entry point and harden the environment against repeat access. #Huntress #BadIIS #XMRig
Analog Devices disclosed that an unauthorized party accessed some of its systems and exfiltrated certain files, with the incident detected on June 23 and immediately contained with help from external cybersecurity experts. The company says it has no evidence of stolen data being leaked online, while separately assessing a possible link to ExfilSquad and monitoring for further impact. #AnalogDevices #ExfilSquad
Discern Security raised $13 million in a Series A round led by Forgepoint Capital, bringing its total funding to $16 million. The company will use the new capital to expand its team and advance its AI-driven security platform that helps organizations identify control gaps and improve security posture. #DiscernSecurity #ForgepointCapital #ReyKirton…
Cantina has emerged from stealth with $8 million in new funding, bringing its total raised to $16.5 million, to advance its autonomous vulnerability management platform. The New York startup uses agentic security workers to map assets, prioritize risks, automate remediation, and verify fixes across an organization’s environment. #Cantina #FrameworkVentures #HariMulackal…