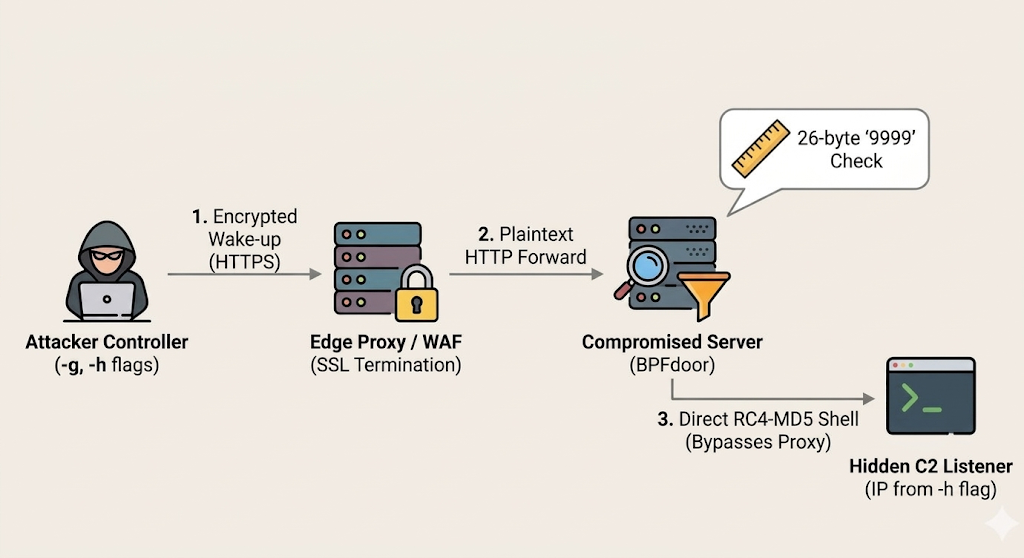
Rapid7 analyzed BPFDoor, BPF Rekoobe, and AVERAT samples that disguise themselves to match telecom and appliance environments, using port 25, BPF socket filters, and fileless staging to evade detection. The campaign affected South Korean, Taiwanese, and ShareTech/SpamSniper-related systems, including mail-security appliances, NAS devices, DVRs, and other edge infrastructure. #BPFDoor #BPFRekoobe #AVERAT #ShareTech #SpamSniper #ChunghwaTelecom
Keypoints
- Rapid7 tracked multiple Linux samples: a new BPFDoor variant, a BPF Rekoobe build, a dropper, and six AVERAT builds.
- The samples use regional and vendor-specific masquerading to blend into telecom and appliance environments, including SpamSniper and Oracle-like naming.
- The BPFDoor controller gained HTTPS POST tunneling through edge proxies, with padded requests to hide magic-packet delivery.
- The dropper writes a shell script to appliance storage, stages payloads in /sbin under fake names, and removes them after execution.
- AVERAT uses SMTP on port 25, STARTTLS, and custom encrypted handshakes to blend into legitimate mail traffic on relay appliances.
- Infrastructure included compromised Taiwanese devices and consumer/small-business edge equipment used as operational relays and VPN footholds.
- Defenders are advised to hunt for raw packet sockets, BPF filters, unlinked executables, hidden state files, and suspicious port-25 callbacks.
MITRE Techniques
- [T1584.008 ] Compromise Infrastructure: Network Devices – The operators used compromised NAS, DVR, and other edge devices as relays and footholds (‘consumer and small-business broadband CPE’).
- [T1133 ] External Remote Services – AVERAT relays exposed PPTP on 1723 and were used as inbound access paths (‘PPTP on 1723, present on all three’).
- [T1480 ] Execution Guardrails – The dropper executed only if /tmp/flag existed and the .php script was absent (‘Execution is gated on one precondition’).
- [T1059.004 ] Unix Shell – The dropper and implant used shell commands and scripts to stage and launch payloads (‘#!/bin/sh’, ‘sh -c’).
- [T1129 ] Shared Modules – AVERAT could load or unload shared-object modules to extend functionality (‘Load or unload a shared-object module’).
- [T1037 ] Boot or Logon Initialization Scripts – The dropper relied on package/startup behavior to relaunch on boot (‘package startup very likely relaunches it at boot’).
- [T1205 ] Traffic Signaling – BPFDoor used magic packets and HTTP-tunneled triggers for covert activation (‘magic packet’, ‘HTTPS POST tunneling mode’).
- [T1205.002 ] Traffic Signaling: Socket Filters – BPFDoor and Rekoobe used classic BPF filters to detect magic traffic (‘attaching a classic BPF filter’).
- [T1070.004 ] File Deletion – The dropper removed staged binaries and scripts after execution (‘rm -rf /sbin/ntpdate’).
- [T1070.003 ] Clear Command History – AVERAT suppressed bash/vim logging to hide operator activity (‘not logged to bash history nor to vim logs’).
- [T1070.006 ] Timestomp – BPFDoor-related behavior included misleading timing/cleanup patterns and deleted artifacts to obscure activity (‘delete each file ten seconds later’).
- [T1036.004 ] Masquerade Task or Service – BPFDoor spoofed service names and process identities (‘spoofs the identity of /usr/sbin/abrtd’).
- [T1036.005 ] Match Legitimate Name or Location – The samples used legitimate-looking names and paths such as ntpdate, udevds, and service paths (‘blend into the software and device conventions’).
- [T1564.001 ] Hidden Files and Directories – AVERAT used hidden state files such as /var/lib/.db and other dotfiles (‘persistent across restarts’).
- [T1027 ] Obfuscated Files or Information – BPFDoor and AVERAT hid strings and configuration with encoding, XOR, and encrypted blobs (‘Strings are hidden’, ‘encrypted blob’).
- [T1027.013 ] Encrypted/Encoded File – The dropper and AVERAT stored payload/configuration in AES- and RC4-protected blobs (‘AES-128-ECB blobs’, ‘276-byte encrypted blob’).
- [T1140 ] Deobfuscate/Decode Files or Information – The article describes decoding hidden strings and decrypting configuration to reveal paths, keys, and commands (‘Decoding reveals’).
- [T1562.004 ] Disable or Modify System Firewall – BPFDoor used NAT redirection and firewall-aware techniques to bypass inspection (‘iptables NAT-redirect staging/teardown logic’).
- [T1083 ] File and Directory Discovery – AVERAT enumerated directory contents and walked file trees (‘Enumerate directory contents’).
- [T1057 ] Process Discovery – AVERAT enumerated running processes with command lines (‘Enumerate running processes with command lines’).
- [T1082 ] System Information Discovery – AVERAT collected hostname, OS version, and other system details (‘report hostname, current user, OS version’).
- [T1033 ] System Owner/User Discovery – AVERAT reported the current user and logged-in users (‘current user’, ‘logged-in users’).
- [T1016 ] System Network Configuration Discovery – AVERAT collected network interfaces as part of beaconing (‘network interfaces’).
- [T1005 ] Data from Local System – The dropper staged local files and paths from the appliance filesystem (‘three paths and a script’).
- [T1041 ] Exfiltration Over C2 Channel – AVERAT sent collected host data back through its command channel (‘Each reports hostname…’).
- [T1030 ] Data Transfer Size Limits – AVERAT used chunked uploads and resumable downloads (‘Upload a file…in chunks’, ‘Download…with resume support’).
- [T1105 ] Ingress Tool Transfer – The dropper installed payloads by copying them from /addpkg into /sbin (‘copies AVERAT into /sbin/udevds’).
- [T1071.003 ] Application Layer Protocol: Mail Protocols – AVERAT communicated over SMTP and STARTTLS on port 25 (‘It connects outbound to port 25 and speaks SMTP’).
- [T1573.001 ] Encrypted Channel: Symmetric Cryptography – AVERAT and Rekoobe used TLS and application-layer encryption (‘HMAC-SHA1, AES-CBC’, ‘STARTTLS’).
- [T1090 ] Proxy – AVERAT included proxy and port-forward capabilities (‘Open a proxy or port-forward channel’).
- [T1008 ] Fallback Channels – BPFDoor and related samples used alternative trigger modes and networking paths (‘ICMP mode’, ‘UDP mode’, ‘HTTPS POST tunneling mode’).
- [T1529 ] System Shutdown/Reboot – AVERAT could reboot the appliance after syncing buffers (‘sync() before forcing a restart’).
- [T1489 ] Service Stop – The reboot and teardown behavior could stop services and flush state (‘forcing a restart through the kernel’).
Indicators of Compromise
- [SHA-256 ] Dropper and AVERAT samples – 2bedc26d4b29b435c21962beed7db21188a0219a0d28334bba8b4fb1656d7b15, bf8135f46ecedfe5bd06fcecbb2e721c2367ff765b18f4aa3f868e6597f49e47
- [SHA-256 ] Additional AVERAT and BPFDoor family samples – 4925bcca085ec504f51191645da278d8e96698d91f3c6df44146336c697b4de8, a4379e115d3c4420f5d4b92561022d6e0897990e7297be65c033d47de68e6a6a and 4 more hashes
- [SHA-256 ] SpamSniper BPFDoor and Rekoobe builds – a37ea9897221d4495b538de72b74f2aa1d2ff09b7b6dcedd395aee58931adbf3, 7e667ba5f9df912e02275d3cfe3809d16f822fe776f4035c84b118ebd925b1b5
- [Domain ] AVERAT C2 infrastructure – mx.zxopfds.com, spam.suwaccqi.com and mx1.wwstifsteel.com
- [IPv4 ] AVERAT C2 or relay hosts – 59.125.211.65, 122.116.138.33 and 1.34.200.85
- [File/Path ] Dropper and staging artifacts – /HDD/ms6x2xTo64/updIptable.php, /HDD/ms6x2xTo64/execProcEnd and /tmp/flag
- [File/Path ] Hidden AVERAT state files – /var/lib/.db, /var/lib/.sencha and /var/lib/.us
- [File/Path ] BPFDoor mutex and staged binaries – /var/run/spamsniper.pid, /sbin/ntpdate and /sbin/udevds
- [File/Path ] Dropper payload sources – /addpkg/sbin/update and /addpkg/sbin/agetty
- [Port ] Network communication and C2 – TCP/25, 1723 and other mail-related callbacks
- [Crypto/Protocol Constants ] AVERAT protocol and beacon material – 1571 / 0x0623, 5d 0c f9 47 e4 ea 7b 18 1b ed 5e b1 fb 5c 56 3f and 6b 6a 48 0e f8 ae 5f 1b 38 e6 c0 94 86 df e3 45
Read more: https://www.rapid7.com/blog/post/tr-smtp-is-the-key-bpfdoor-averat-hitting-the-network-edge