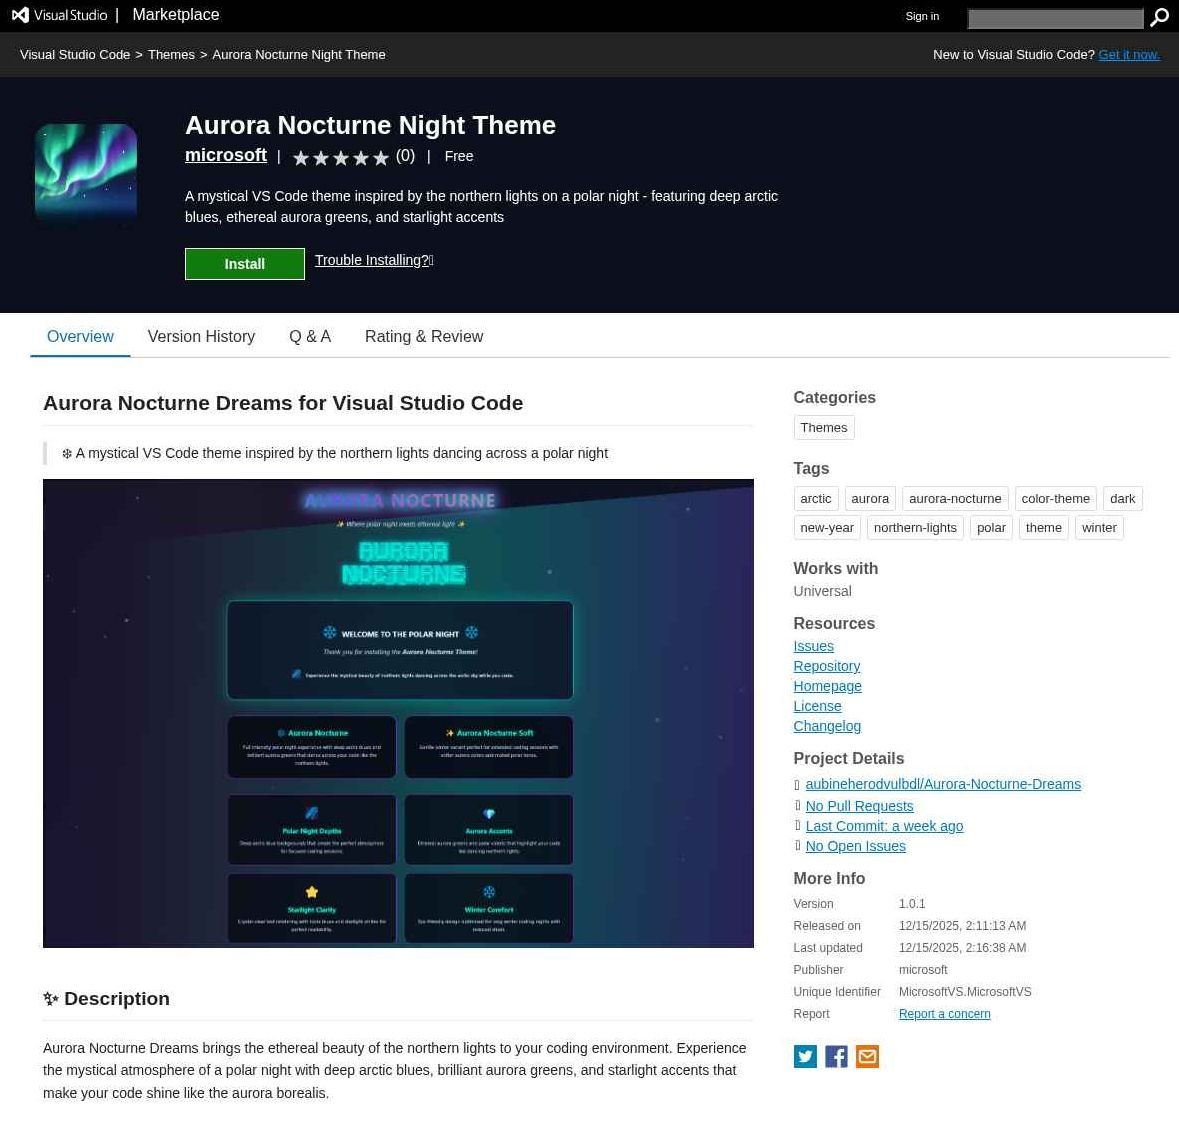
Socket uncovered a cluster of VS Code theme extensions spanning the Visual Studio Marketplace and Open VSX, including two confirmed malicious extensions and a high-confidence link to GlassWorm. The investigation found obfuscated JavaScript loaders, a Windows batch downloader, Solana transaction-memo dead drops, and shared Git history linking extensions such as Aurora Nocturne Night Theme, Coca-Cola Christmas, Aurora Borealis Studio Theme, and Cosmic Nebula Themes. #GlassWorm #AuroraNocturneNightTheme #CocaColaChristmas #AuroraBorealisStudioTheme #CosmicNebulaThemes
Keypoints
- Socket identified a theme cluster across four Visual Studio Marketplace extensions and six Open VSX extensions.
- Two extensions were confirmed malicious: Aurora Nocturne Night Theme and Cosmic Nebula Themes.
- Aurora Nocturne Night Theme downloaded a batch script from fingercakes4sale[.]store, saved it as %TEMP%temp_batch.cmd, and executed it with cmd.exe.
- Cosmic Nebula Themes used AES-256-CBC to decrypt embedded JavaScript, then executed it with eval() and later-stage in-memory execution.
- The Cosmic Nebula Themes loader used a Solana transaction memo as a dead drop to resolve follow-on infrastructure, matching prior GlassWorm activity.
- Git history, code similarity, and recurring Russian-language comments linked Coca-Cola Christmas, Aurora Borealis Studio Theme, and Aurora Nocturne Night Theme to the same development cluster.
- The cluster included brandjacking and name-squatting signals, plus high install/download counts, making even unweaponized extensions high-risk.
MITRE Techniques
- [T1195.002 ] Supply Chain Compromise – Threat actors abused theme extensions and publisher ecosystems to deliver malicious code through software distribution channels (‘compromise software supply chain’).
- [T1027 ] Obfuscated Files or Information – Aurora Nocturne Night Theme used heavily obfuscated JavaScript, runtime string reconstruction, zero-width Unicode encoding, and compressed single-line code (‘heavily obfuscated, roughly 59 KB JavaScript blob’).
- [T1140 ] Deobfuscate/Decode Files or Information – The extension decoded zero-width Unicode payloads and decrypted embedded stages before execution (‘decoded=zeroWidthDecode(encoded); eval(decoded);’, ‘decrypts embedded JavaScript stage with AES-256-CBC’).
- [T1105 ] Ingress Tool Transfer – Aurora Nocturne Night Theme downloaded a threat actor-controlled payload from fingercakes4sale[.]store and wrote it to a local batch file (‘Download threat actor-controlled content’).
- [T1102.001 ] Web Service: Dead Drop Resolver – Cosmic Nebula Themes queried a Solana transaction memo to dynamically resolve follow-on payload infrastructure (‘Use Solana transaction memos as a dead-drop to dynamically resolve follow-on payload infrastructure’).
- [T1059.007 ] Command and Scripting Interpreter: JavaScript – The malicious extensions executed recovered JavaScript using eval() and Node.js VM execution (‘executes it through eval()’, ‘execute decoded threat actor-controlled JavaScript’).
- [T1059.003 ] Command and Scripting Interpreter: Windows Command Shell – Aurora Nocturne Night Theme executed the downloaded batch script through cmd.exe (‘executes it through cmd.exe’, ‘cmd /c’).
- [T1614.001 ] System Location Discovery: System Language Discovery – Cosmic Nebula Themes checked for Russian-language systems and bypassed them (‘Exit on systems matching Russian locale/timezone conditions’).
Indicators of Compromise
- [Domain ] Aurora Nocturne Night Theme payload host – fingercakes4sale[.]store
- [URL ] Aurora Nocturne Night Theme download location – hxxps://fingercakes4sale[.]store/dsyuC
- [File path ] Dropped and executed batch script – %TEMP%temp_batch.cmd, temp_batch.cmd
- [File hash ] Aurora Nocturne Night Theme package and loader hashes – a276b76d3b00f302bb4dfb3690125c85ff472b16049c3c37476ac5e51096df07, 5e68ca8c2097caccdb74d2752b85b85595a4bf646b442b8431a2416e87dbf268
- [File hash ] Cosmic Nebula Themes hashes – 684c877a52d226d50584cb886ca8ec5bec6355d4de853f406734c79d5b387804, da2d950e50326171adbff9c2bfd6f28998e32623ea7c2c475b9159a45cfb86bb
- [Solana address ] GlassWorm dead-drop address – BjVeAjPrSKFiingBn4vZvghsGj9KCE8AJVtbc9S8o8SC
- [Encryption artifacts ] Cosmic Nebula Themes loader parameters – wDO6YyTm6DL0T0zJ0SXhUql5Mo0pdlSz, 4c4b9a3773e9dced6015a670855fd32b
- [Response headers ] Stage retrieval headers – ivbase64, secretkey
- [Repository ] Cosmic Nebula Themes source repository – vovanloc2234-sudo/Cosmic-Nebula-Themes
- [Extension IDs ] Cluster-linked extensions – holiday-themes.theme-coca-cola-christmas, lohsebhipolg2s.theme-aurora-borealis, aurora-them-creator.theme-aurora-nocturne, solidity-syntax.deep-focus, charcoal-mint-studio.theme-charcoal-mint, cosmic-themes.theme-cosmic-nebula