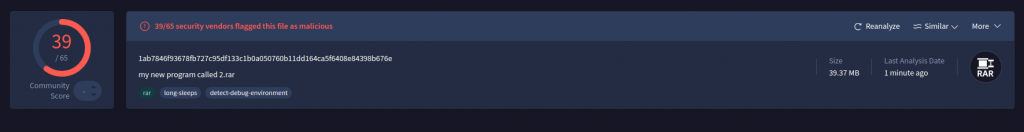
A nested archive named my new program called 2.rar ultimately revealed TokenGrabberBuilder.zip, which contained a Python-based builder and an embedded infostealer payload targeting Windows systems. The malware uses MaaS-style customization, anti-analysis checks, persistence, browser and Discord credential theft, Wi-Fi password harvesting, and webhook-based exfiltration to steal data. #TokenGrabberBuilder #stealer.py #Discord #Roblox
Keypoints
- Extraction of my new program called 2.rar led to a nested archive, TokenGrabberBuilder.zip, hiding suspicious files for further analysis.
- The sample contains two main components: a Python-based builder and an embedded infostealer payload.
- The builder follows a Malware-as-a-Service model, enabling customized Windows executables with Nuitka, PyInstaller, or raw script output.
- It automatically installs dependencies, stores webhook settings in webhook.txt, and XOR/Base64-encodes the webhook before injecting it into the payload.
- The payload uses anti-analysis checks, including debugger detection, process blacklisting, disk-size checks, and timing-based evasion.
- Persistence is established through a Run key and a scheduled task, both designed to run at logon while avoiding visible console windows.
- The stealer targets browser credentials, Firefox data, Wi-Fi passwords, Discord tokens, Roblox cookies, and system/geolocation information before exfiltrating it in a ZIP archive via webhook.
MITRE Techniques
- [T1057] Process Discovery – The malware enumerates running processes to detect virtualization and analysis artifacts, terminating if suspicious names are found (‘enumerates all running processes using psutil and terminates if any process name matches known virtualization artifacts’).
- [T1622] Debugger Evasion – It checks for attached debuggers via Windows API before continuing (‘calls the Windows IsDebuggerPresent() API through ctypes’).
- [T1497.001] Virtualization/Sandbox Evasion: System Checks – It uses disk-size and environment checks to avoid sandboxes (‘exits if it is less than 50 GB’ and checks for virtualization-related processes).
- [T1497.003] Virtualization/Sandbox Evasion: Time Based Evasion – A variable sleep derived from the process ID helps delay execution and outlast analysis (‘introduces timing unpredictability’).
- [T1547.001] Registry Run Keys / Startup Folder – The malware writes persistence into the Run key (‘writes itself to HKCUSoftwareMicrosoftWindowsCurrentVersionRun’).
- [T1053.005] Scheduled Task/Job: Scheduled Task – It creates a scheduled task to run at user logon (‘A scheduled task is created with the trigger ONLOGON’).
- [T1119] Automated Collection – The stealer automatically gathers browser data, Discord tokens, Wi-Fi profiles, and system details (‘collects different types of sensitive information’).
- [T1005] Data from Local System – It copies local browser databases and reads local profile files to extract data (‘copies locked database files to the system temp directory’ and reads local files like places.sqlite).
- [T1555.003] Credentials from Password Stores: Credentials from Web Browsers – It extracts saved credentials from Chromium browsers (‘Extracts the AES master key’ and decrypts Login Data entries).
- [T1555.004] Credentials from Password Stores: Windows Credential Manager – It uses Windows DPAPI/CryptUnprotectData to recover protected browser material (‘using Windows DPAPI (CryptUnprotectData)’).
- [T1021] Remote Services – The malware validates Discord tokens against the live Discord API before exfiltration (‘Tokens are validated against the live Discord API (/api/v9/users/@me)’).
- [T1041] Exfiltration Over C2 Channel – Stolen data is sent to an attacker-controlled webhook via HTTP POST (‘sent to an attacker-controlled webhook using an HTTP POST request’).
- [T1036] Masquerading – It disguises persistence under a legitimate-looking name (‘deceptive key name WindowsUpdate, mimicking a legitimate Windows component’).
- [T1027] Obfuscated Files or Information – Strings and the webhook URL are XOR/Base64-encoded to hinder analysis (‘stores as a Base64-encoded, XOR-encrypted blob’ and ‘XOR-encoded using the key 0x5A’).
Indicators of Compromise
- [File names ] Suspicious archive and payload artifacts – my new program called 2.rar, TokenGrabberBuilder.zip, stealer.py
- [Registry paths ] Persistence locations used by the malware – HKCUSoftwareMicrosoftWindowsCurrentVersionRun, HKCUSOFTWAREPythonPythonCore
- [File paths ] Browser and Firefox data locations targeted for theft – %LOCALAPPDATA%ProgramsPython, %APPDATA%MozillaFirefoxProfiles
- [File names ] Local databases and configuration files accessed for credential theft – Login Data, History, Web Data, Cookies, places.sqlite, cookies.sqlite, webhook.txt
- [URLs ] Exfiltration and validation endpoints – https://pastebin.com/api/api_post.php, /api/v9/users/@me
- [Hashes ] Reported IOC hashes – 610f0c65a3f8e88559f89ed90ea9ee5c, 429ed63ab3fbda8d22d0ac750ecfe8cc, and 1 more hash