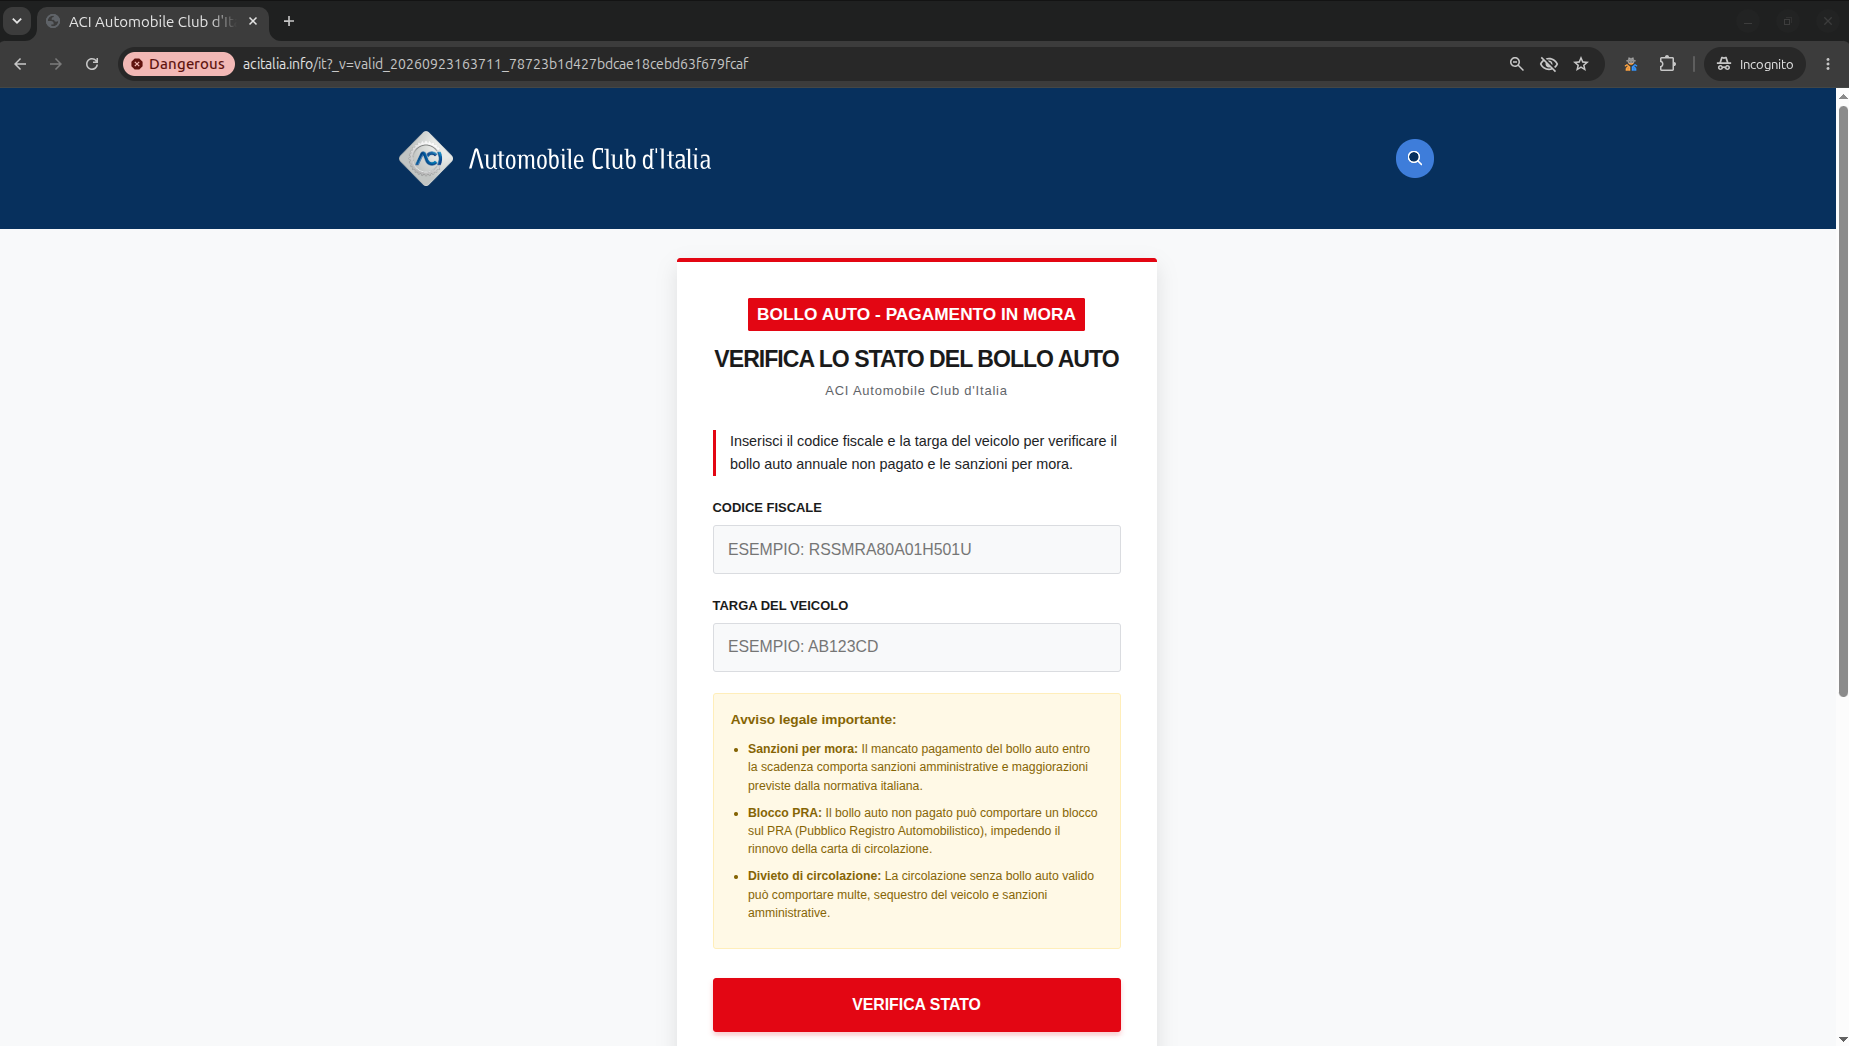
CERT-AGID identified a phishing campaign abusing the name, logo, and graphics of the Automobile Club d’Italia (ACI) to trick users into paying a fake annual vehicle tax debt. The fraudulent sites acitalia[.]info and acitalia[.]click collect personal data and card details while CERT-AGID has requested their takedown and shared the indicators with accredited organizations. #CERTAGID #AutomobileClubdItalia #ACI #acitaliainfo #acitaliaclick
Keypoints
- CERT-AGID detected a phishing campaign impersonating the Automobile Club d’Italia (ACI).
- The fake sites abuse ACI’s name, logo, and visual style to appear legitimate.
- The scam claims the victim has an unpaid annual vehicle tax and threatens sanctions and driving restrictions.
- The phishing flow first requests the fiscal code and vehicle license plate, then collects identity and contact details.
- The final stage simulates a payment page for a €15.87 penalty and asks for full payment card information.
- The fraudulent infrastructure is hosted on the domains acitalia[.]info and acitalia[.]click, which are outside ACI’s official channels.
- CERT-AGID requested domain takedown, informed ACI, and shared the IoCs with accredited recipient organizations.
MITRE Techniques
- [T1566.002 ] Spearphishing Link – Victims are driven to fraudulent websites that impersonate ACI and ask them to enter data (‘sfrutta indebitamente il nome, il logo e le grafiche dell’ACI’; ‘sito fraudolento’).
- [T1583.001 ] Acquire Infrastructure: Domains – The attackers used lookalike domains to host the fake portal (‘acitalia[.]info e acitalia[.]click’).
- [T1036 ] Masquerading – The site imitates the appearance and branding of a trusted organization to deceive users (‘riproduce una veste grafica riconducibile all’ente’).
- [T1005 ] Data from Local System – The page requests and captures sensitive local identity and vehicle information entered by the victim (‘codice fiscale e la targa del veicolo’).
- [T1110 ] Brute Force – Not mentioned in the article.
- [T1056.001 ] Keylogging – Not mentioned in the article.
- [T1556 ] Modify Authentication Process – Not mentioned in the article.
- [T1001 ] Data Obfuscation – Not mentioned in the article.
- [T1040 ] Network Sniffing – Not mentioned in the article.
- [T1539 ] Steal Web Session Cookie – Not mentioned in the article.
- [T1078 ] Valid Accounts – The article advises that official services require digital identity login, implying the fake site bypasses legitimate authentication (‘tramite i sistemi di autenticazione della Pubblica Amministrazione, come SPID o CIE’).
Indicators of Compromise
- [Domains ] Fraudulent phishing infrastructure impersonating ACI – acitalia[.]info, acitalia[.]click
- [Brand/Organization names ] Impersonated entity used in the scam – Automobile Club d’Italia (ACI), CERT-AGID
- [Payment amount ] Fake penalty amount shown on the payment page – € 15,87
Read more: https://cert-agid.gov.it/news/in-corso-un-phishing-a-tema-bollo-auto-ai-danni-di-aci/